
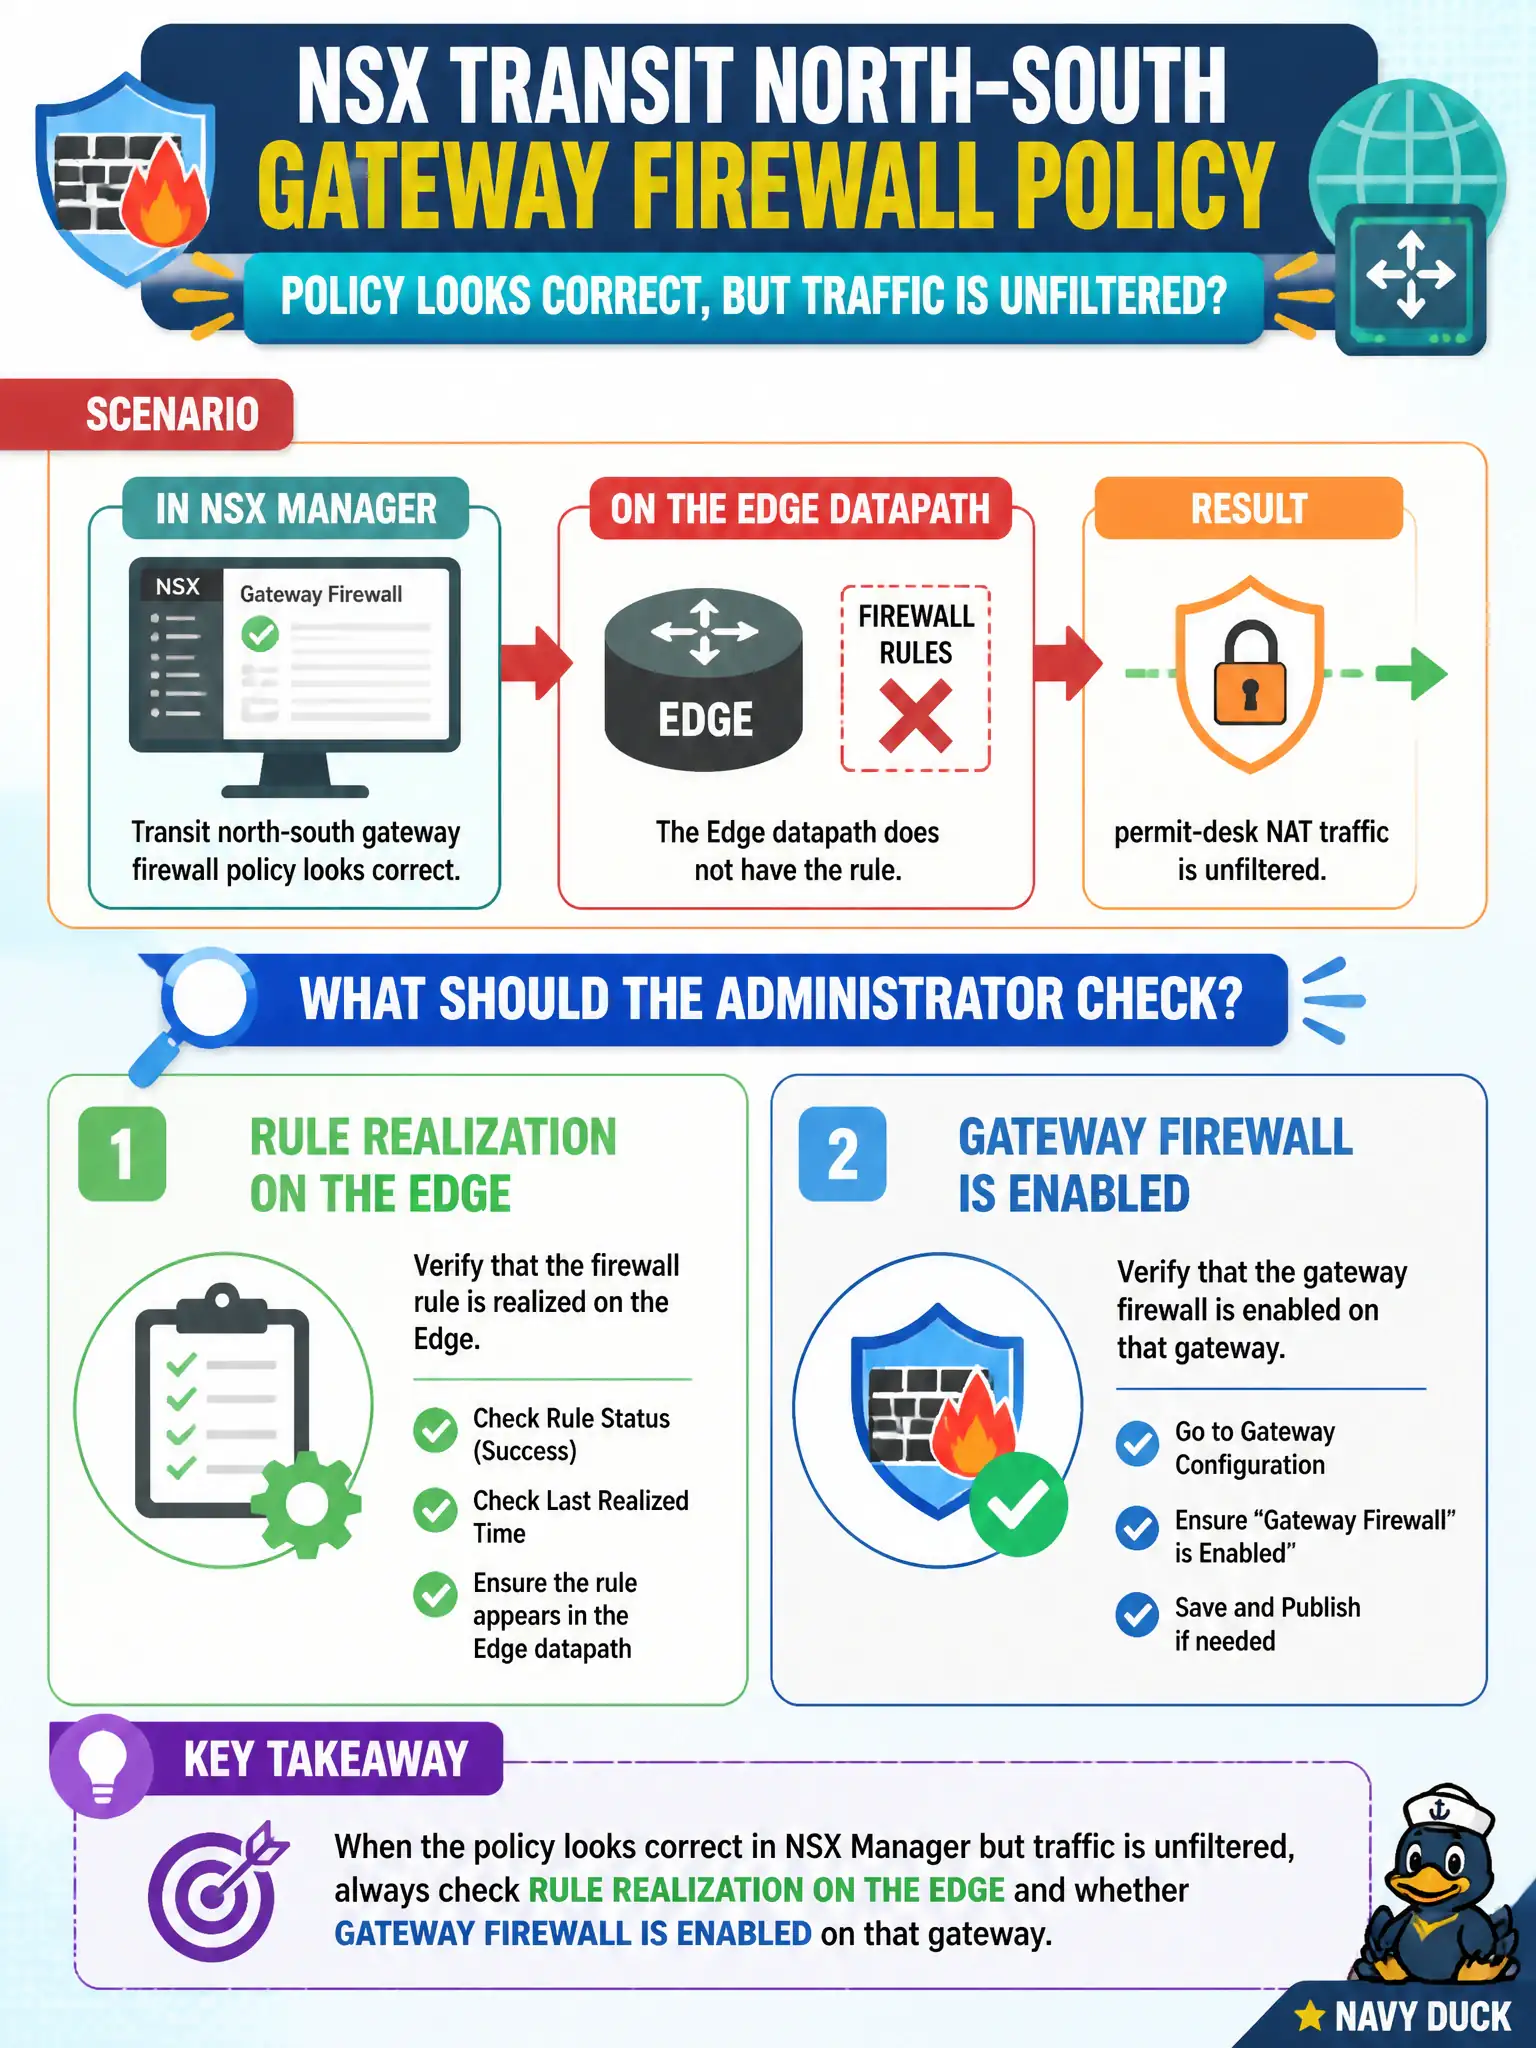
Transit north-south gateway firewall policy looks correct in NSX Manager, but the Edge datapath does not have the rule and permit-desk NAT traffic is unfiltered. What should the administrator check?
Select an answer to reveal the explanation.
Short Explanation
The picture in the UI is not the same as the Edge actually enforcing. Gateway firewall can be off per gateway, or realization can be stuck. Check the Edge datapath, not a UEM profile.
Full Explanation
When transit north-south gateway firewall policy looks correct in NSX Manager but the Edge datapath does not have the rule and permit-desk NAT traffic is unfiltered, check rule realization on the Edge and whether gateway firewall is enabled on that gateway. The UI picture is not the same as Edge enforcement; gateway firewall can be disabled per gateway or realization can be stuck, leaving NAT traffic unfiltered. Verifying Edge datapath and enablement restores civic north-south control. A Distributed Firewall exclusion list on the Edge management interface fails by concept because DFW exclusion on management is not the north-south gateway firewall realization path for NAT traffic. Workspace ONE UEM compliance of the Edge fails by concept because UEM compliance does not enable or realize NSX gateway firewall on the Edge. Carbon Black Cloud as the north-south engine fails by concept because CBC is endpoint prevention, not Edge gateway firewall for transit north-south flows. Exam caveat: Manager showing a gateway rule is insufficient—confirm gateway firewall enabled and realized on the Edge datapath. Operational check: verify gateway firewall is enabled on the gateway, check Edge realization for the rule, retest permit-desk NAT filtering, and file Edge datapath evidence in the transit security operations log for municipal north-south assurance.