
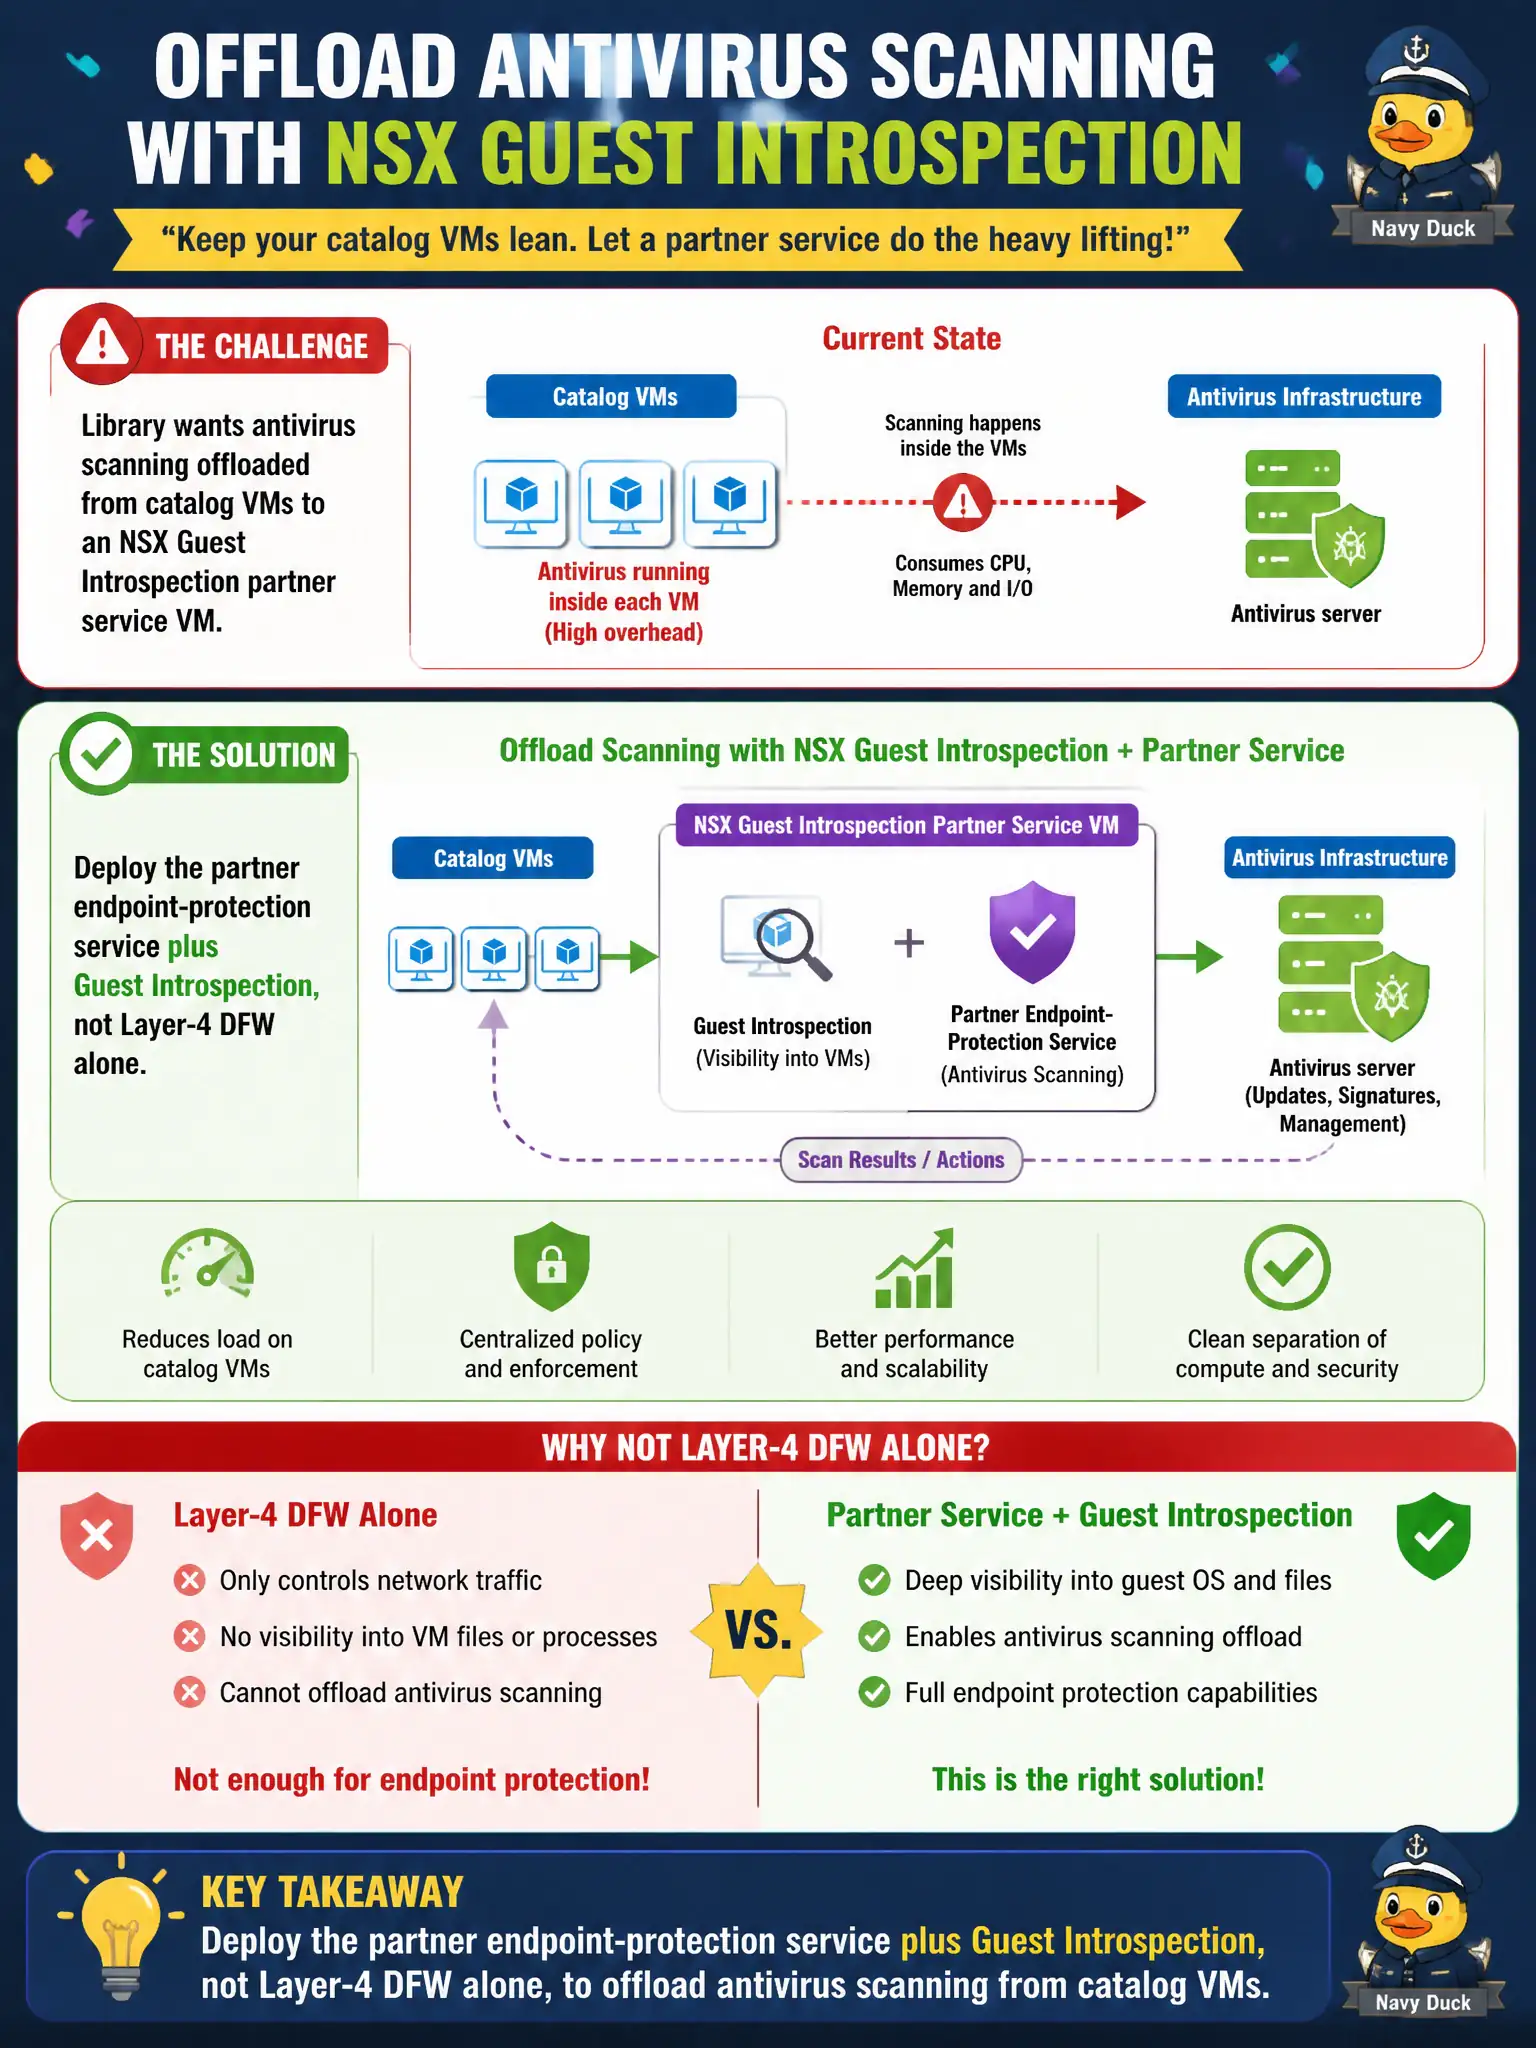
A library wants antivirus scanning offloaded from catalog VMs to an NSX Guest Introspection partner service VM. What should the administrator deploy?
Select an answer to reveal the explanation.
Short Explanation
L4 DFW can open or shut a port. It cannot open a file and ask a partner engine if it is malware. That offload needs Guest Introspection and the partner SVM.
Full Explanation
A library that wants antivirus scanning offloaded from catalog VMs to an NSX Guest Introspection partner needs the partner endpoint-protection service plus Guest Introspection—not Layer-4 Distributed Firewall alone. L4 allow/deny cannot open files and ask a partner engine whether content is malware.
Distributed firewall Layer-4 rules only cannot perform partner AV offload. A Workspace ONE Access risk engine is not an antivirus service VM. An NSX load balancer with an HTTPS health monitor named antivirus is load balancing, not GI partner introspection.
Exam caveat: file introspection/AV offload requires GI + partner SVM; DFW L4 is a different control.
Operational check: deploy the partner service and GI, assign policy to catalog VMs, verify scan offload events, and keep L4 DFW as complementary network policy—not a substitute AV engine.
Partner AV offload plus GI is the library’s file-inspection path; L4 DFW remains the network door. After deployment, submit an EICAR-like test per partner guidance in a lab catalog VM, confirm offload, and keep network allows least-privilege so malware cannot simply call home on open ports. Keep partner offload test evidence from a lab catalog VM with the library change record so the next on-call engineer can separate L4 DFW doors from file-inspection outcomes without rediscovering product roles under pressure.