
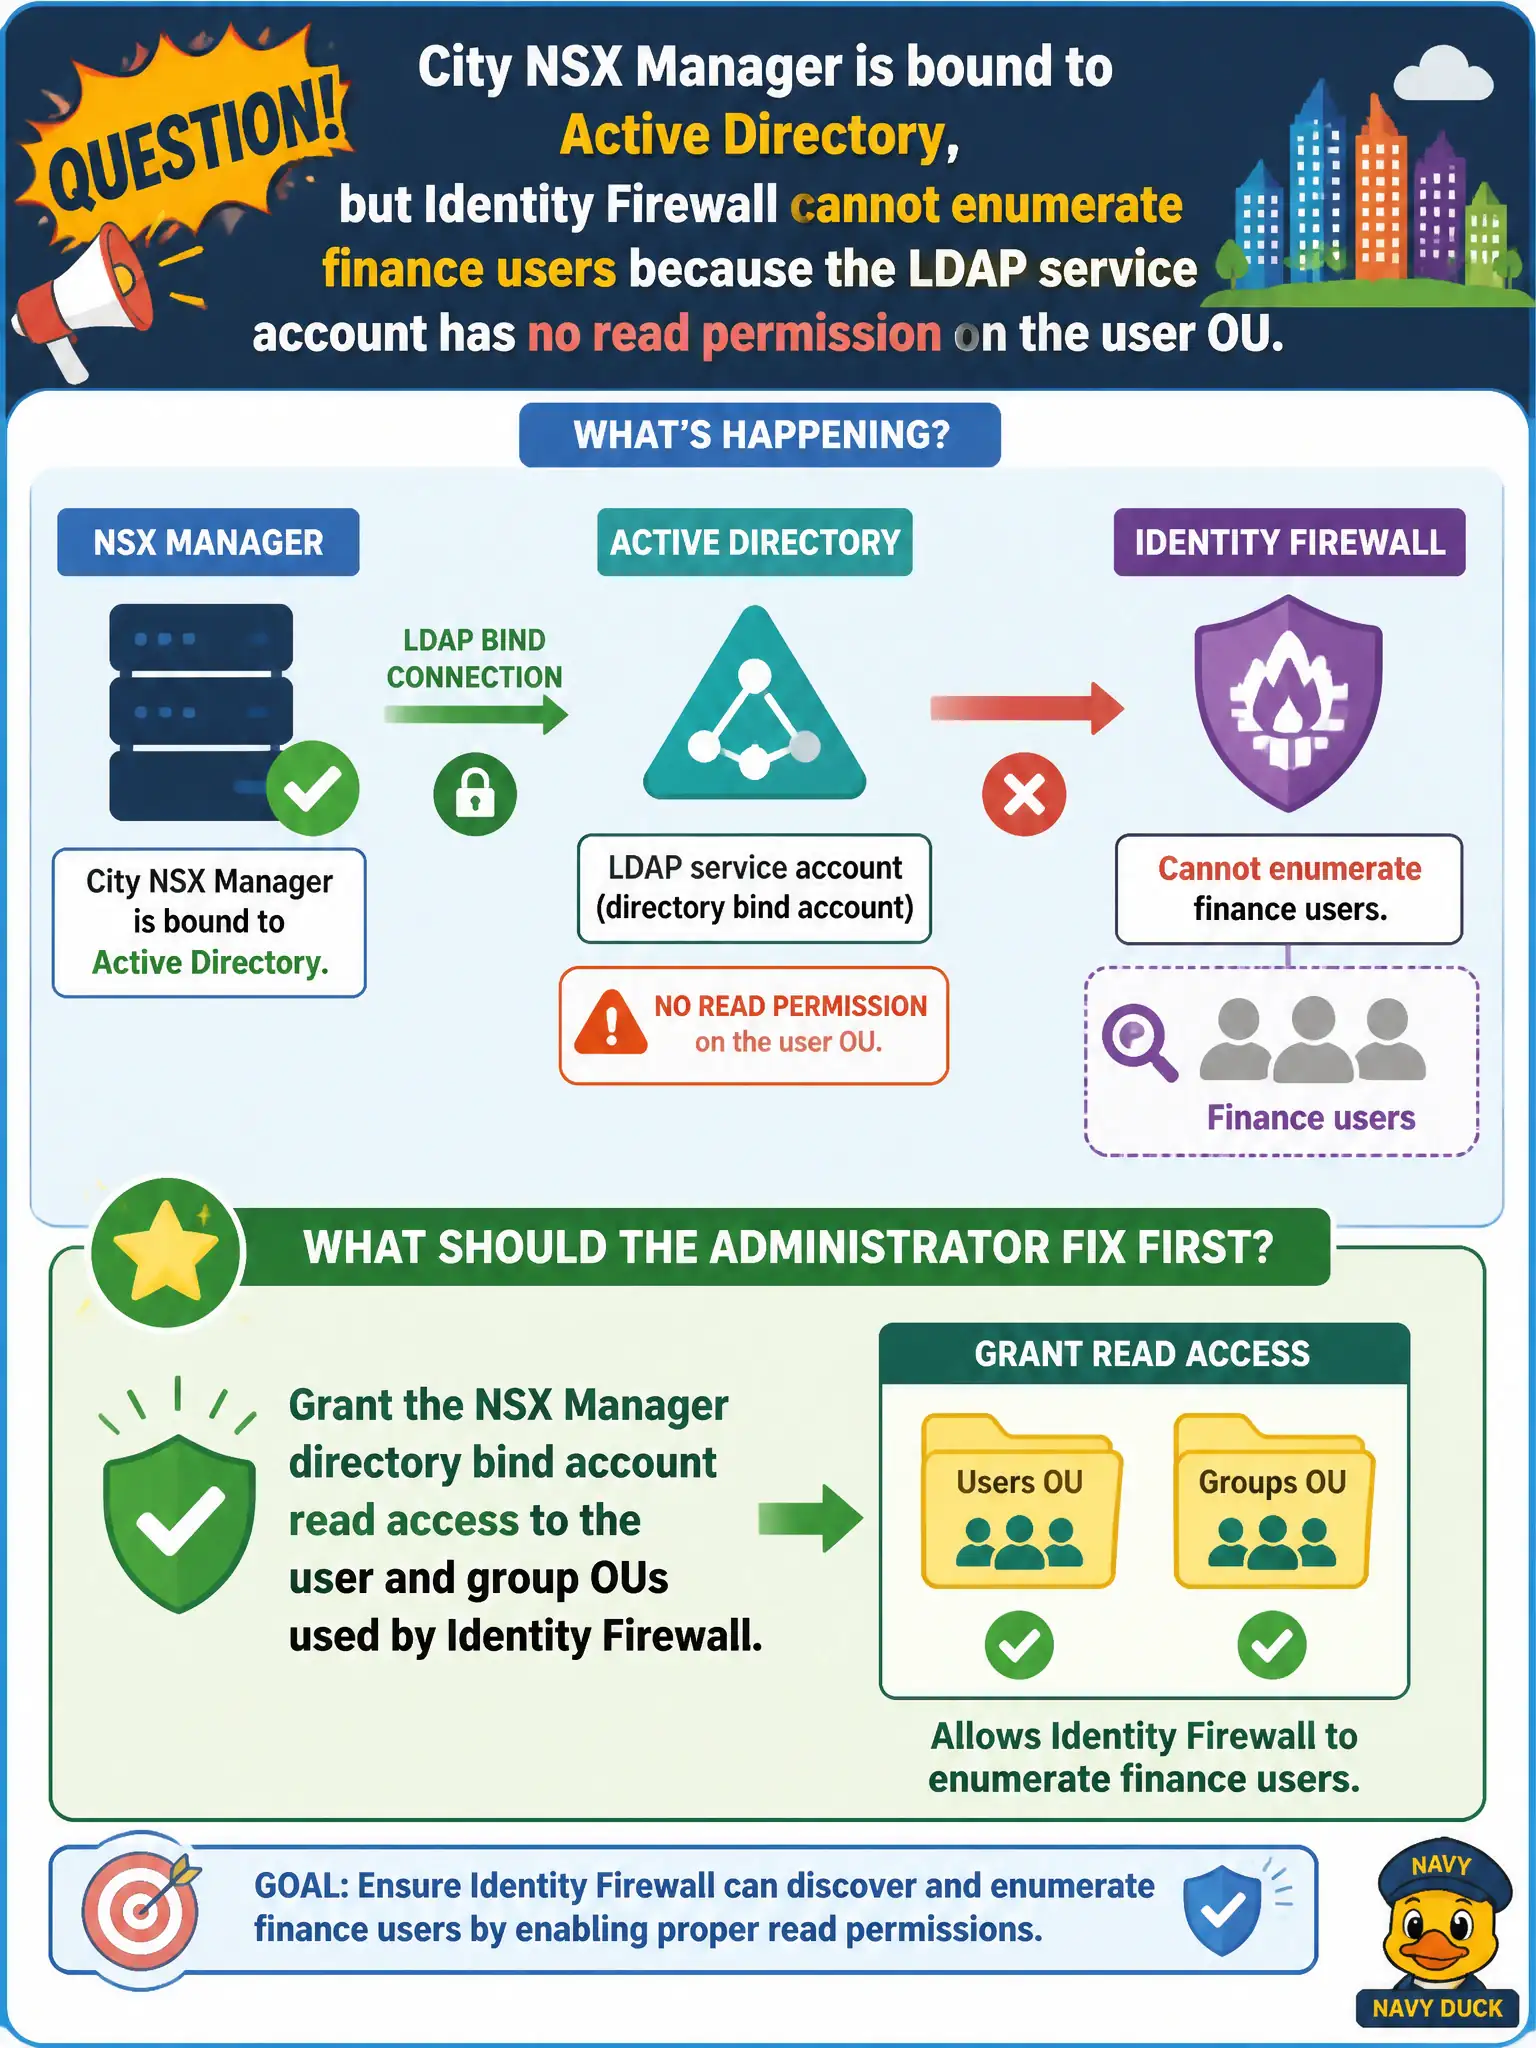
City NSX Manager is bound to Active Directory, but Identity Firewall cannot enumerate finance users because the LDAP service account has no read permission on the user OU. What should the administrator fix first?
Select an answer to reveal the explanation.
Short Explanation
NSX is asking AD who is in Finance with a service account that cannot even open that OU. Fix the bind account’s read rights—do not blow a hole in the default DFW rule.
Full Explanation
When city NSX Manager is bound to Active Directory but Identity Firewall cannot enumerate finance users, fix LDAP service-account permissions first: grant the NSX Manager directory bind account read access to the user and group OUs used by Identity Firewall. Without OU read rights, sync cannot populate finance identities.
Changing the distributed firewall default rule from Drop to Allow so unmapped users pass weakens the fabric instead of fixing directory permissions. Replacing the bind account with the vCenter Single Sign-On administrator confuses vCenter SSO with LDAP bind for IDFW. Disabling LDAPS so the bind account can skip OU permissions is insecure and does not grant missing read rights.
Exam caveat: empty IDFW group enumeration often equals bind-account ACL problems, not DFW default-action problems.
Operational check: grant OU read to the bind account, re-sync, confirm finance users/groups appear, test an IDFW rule, and document least-privilege bind rights with identity admins.
Bind-account OU read rights are the quiet prerequisite behind empty finance IDFW enumerations. Use a dedicated least-privilege LDAP account, grant only needed OUs, and monitor for access-denied bind errors in Manager logs before opening broad DFW allow exceptions.