
Parks seasonal contractors live in a separate Active Directory forest, and Identity Firewall rules must use those contractor groups. What should the administrator configure?
Select an answer to reveal the explanation.
Short Explanation
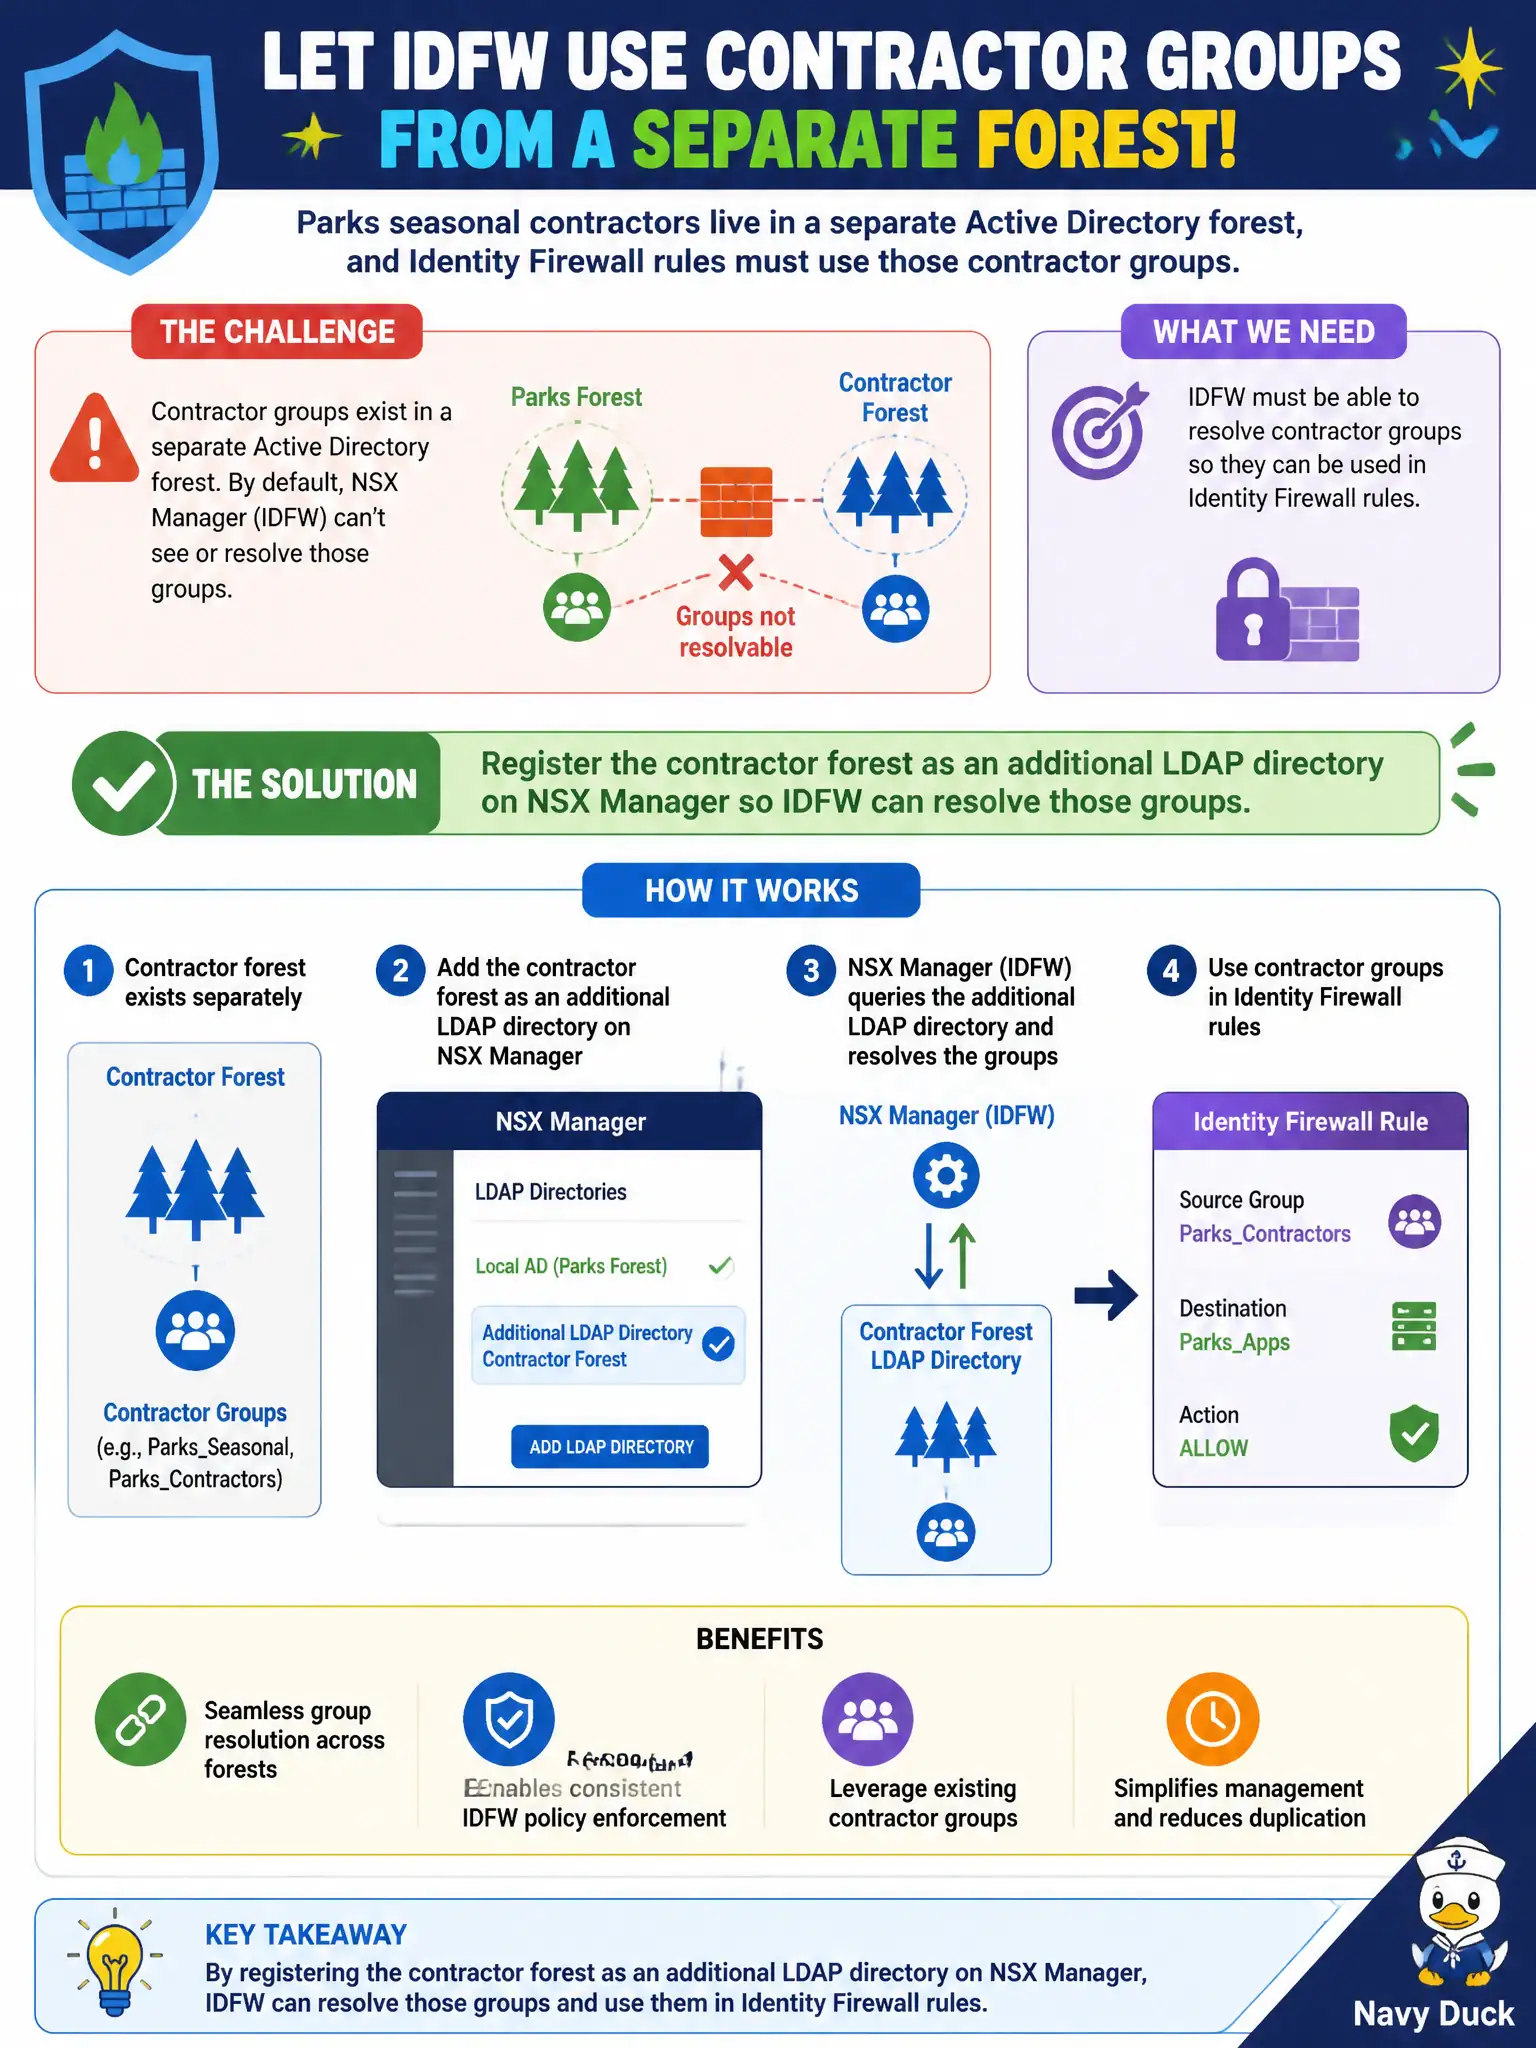
IDFW only knows groups from directories NSX Manager can read. A second forest means a second LDAP registration—not a Carbon Black list and not a pile of contractor IPs.
Full Explanation
Parks seasonal contractors in a separate Active Directory forest require that forest registered as an additional LDAP directory on NSX Manager so Identity Firewall can resolve contractor groups. Multi-directory registration is how IDFW spans forests without flattening identity into unrelated products.
Adding contractors to a Carbon Black watchlist does not make CBC the DFW/IDFW source for those users. Collapsing both forests into one Workspace ONE Access policy and skipping NSX directory config fails IDFW group resolution in NSX. Creating only a static IP set of contractor laptops abandons group-based identity as contractors churn seasonally.
Exam caveat: additional LDAP directories on NSX Manager are the supported path for second-forest IDFW groups.
Operational check: register the contractor forest, sync groups, publish an IDFW rule using a contractor group, test seasonal access, and review directory health each season.
Second-forest LDAP on NSX Manager lets parks contractors keep their home identities. After registration, limit synced OUs to contractor groups needed for seasonal access, review orphaned groups after season end, and avoid static IP sets that never track laptop churn.