
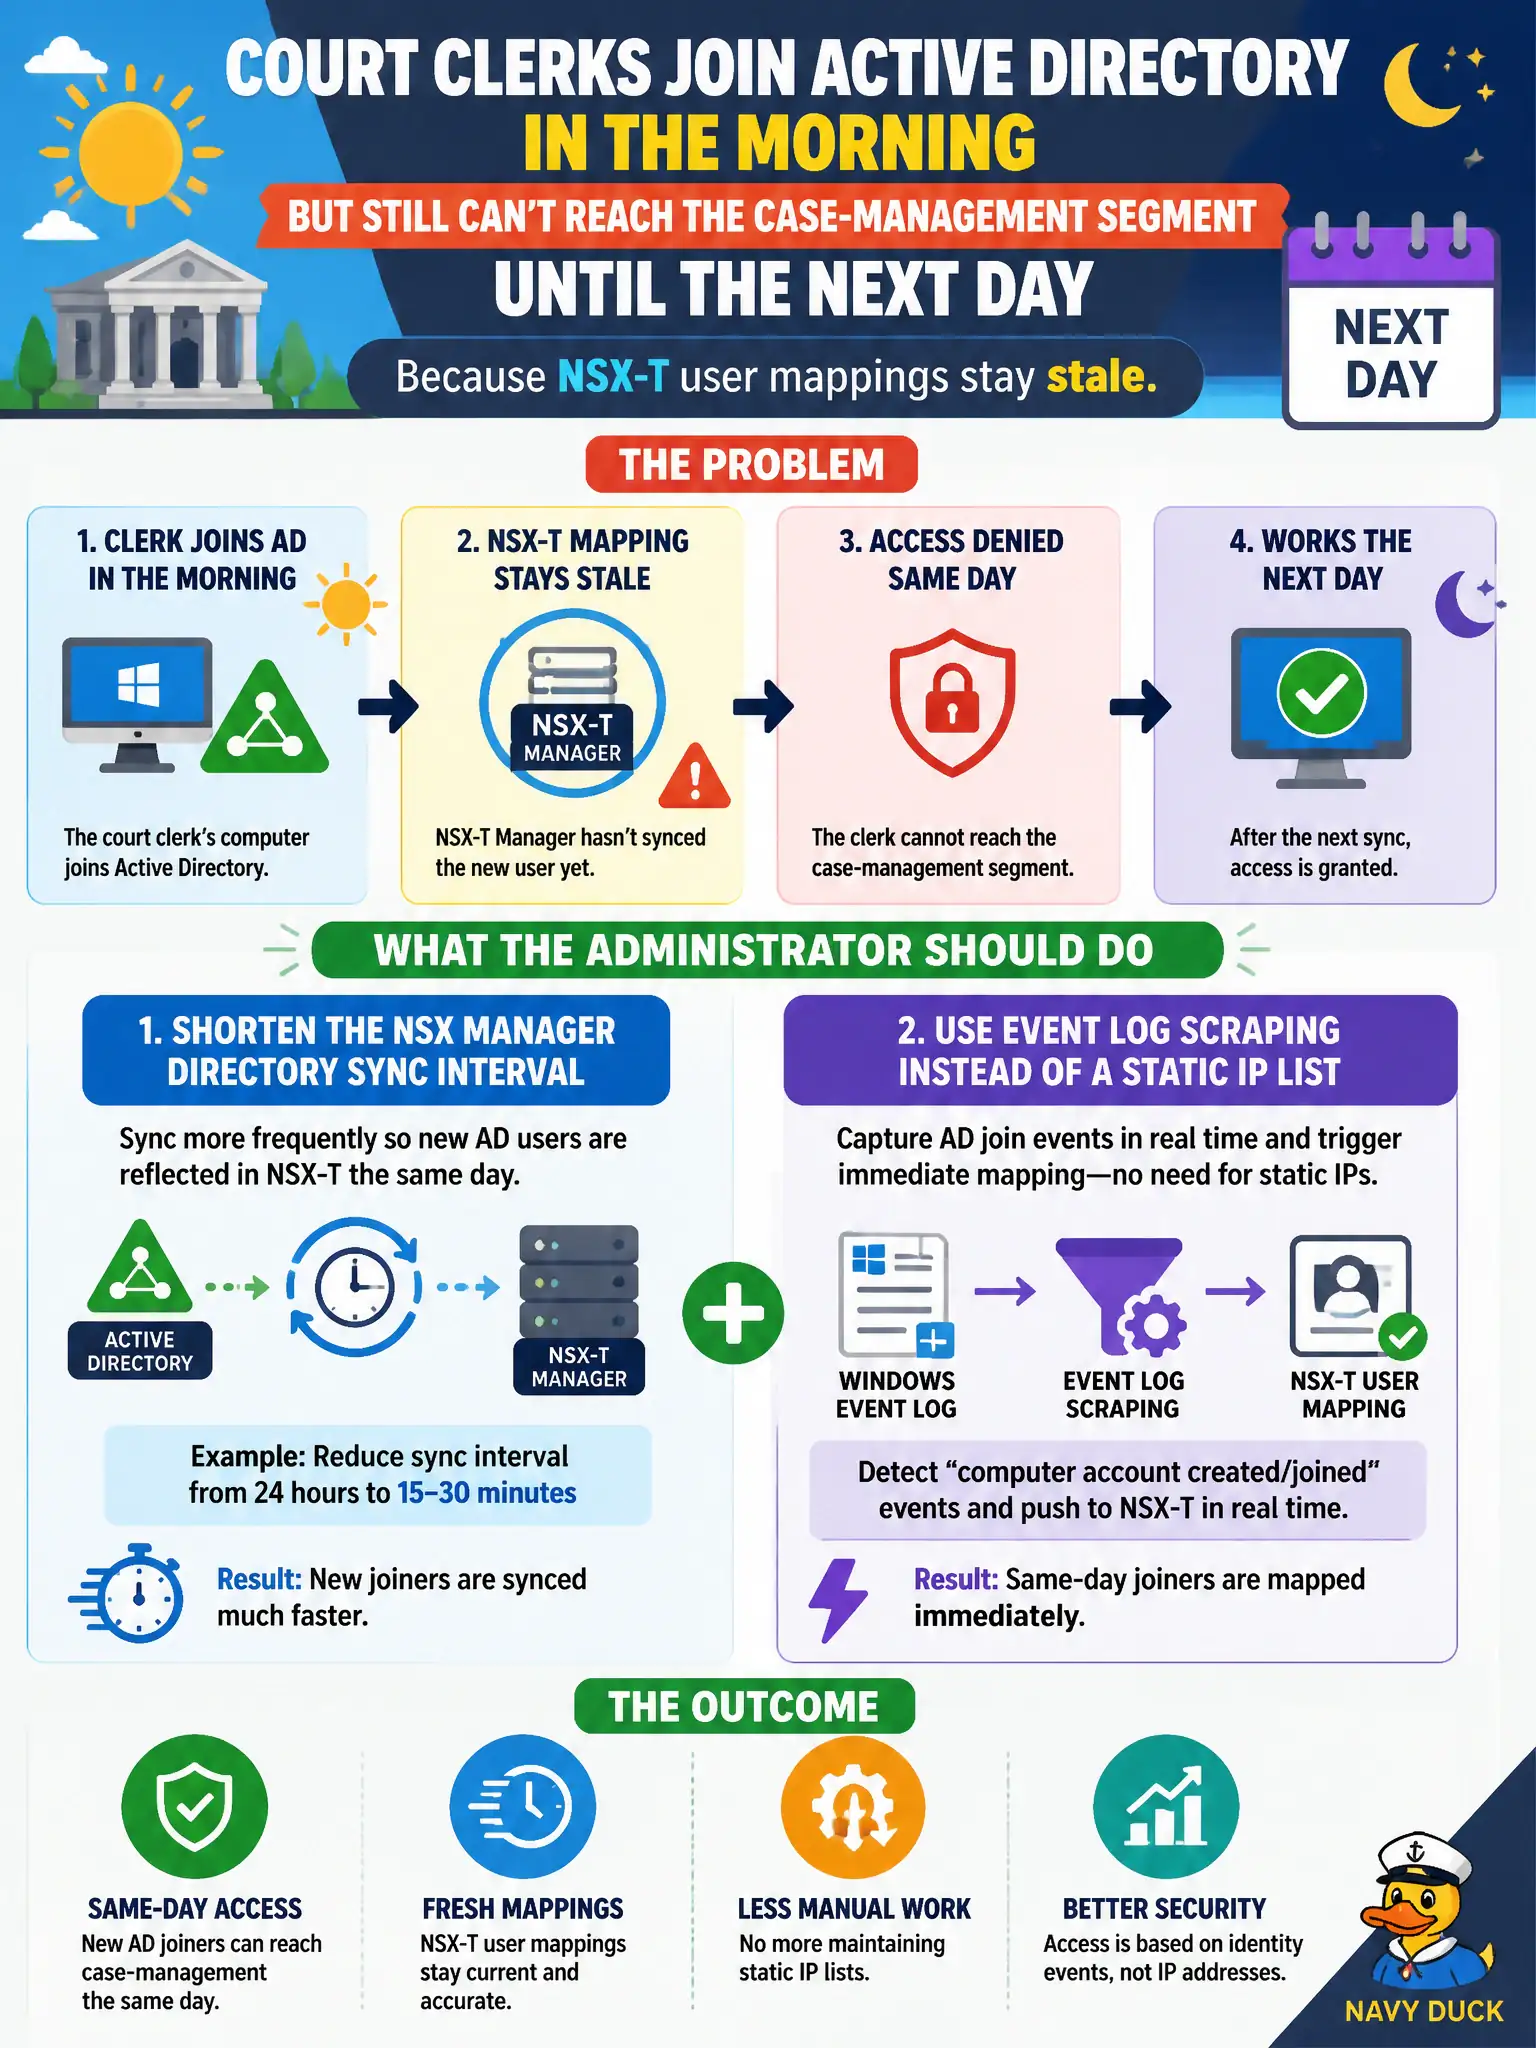
Court clerks who join Active Directory in the morning still cannot reach the case-management segment until the next day because NSX-T user mappings stay stale. What should the administrator do?
Select an answer to reveal the explanation.
Short Explanation
IDFW is a live nametag, not a phone book reprinted at midnight. Speed up directory sync and scrape domain-controller logon events so this morning’s new clerk shows up as a user, not as yesterday’s IP.
Full Explanation
Court clerks who join Active Directory in the morning but cannot reach case-management until the next day suffer stale NSX-T user mappings. Shorten the NSX Manager directory sync interval and use event log scraping so same-day joiners map without relying on a static IP list that goes stale immediately.
Exporting a nightly CSV of clerk workstation IPs into a static DFW source recreates the staleness problem. Replacing directory sync with a Workspace ONE Access policy that lists clerk display names does not drive NSX IDFW user-to-IP mapping. Disabling Guest Introspection so IDFW uses only a weekly LDAP dump removes live logon context and worsens freshness.
Exam caveat: directory sync interval plus logon event mechanisms matter for same-day joiner scenarios.
Operational check: tighten sync interval, confirm event log scraping where applicable, join a test clerk, verify mapping updates same day, and retire static IP spreadsheets for clerk access.
Fresher sync plus logon events stop same-day court clerks from waiting overnight. Measure time-to-map for a newly joined test account each week, and retire CSV IP processes in writing so helpdesk cannot reopen the stale path during busy intake mornings.