
A library after-hours batch job should be allowed only during a nightly window. What is the correct NSX-T firewall approach?
Select an answer to reveal the explanation.
Short Explanation
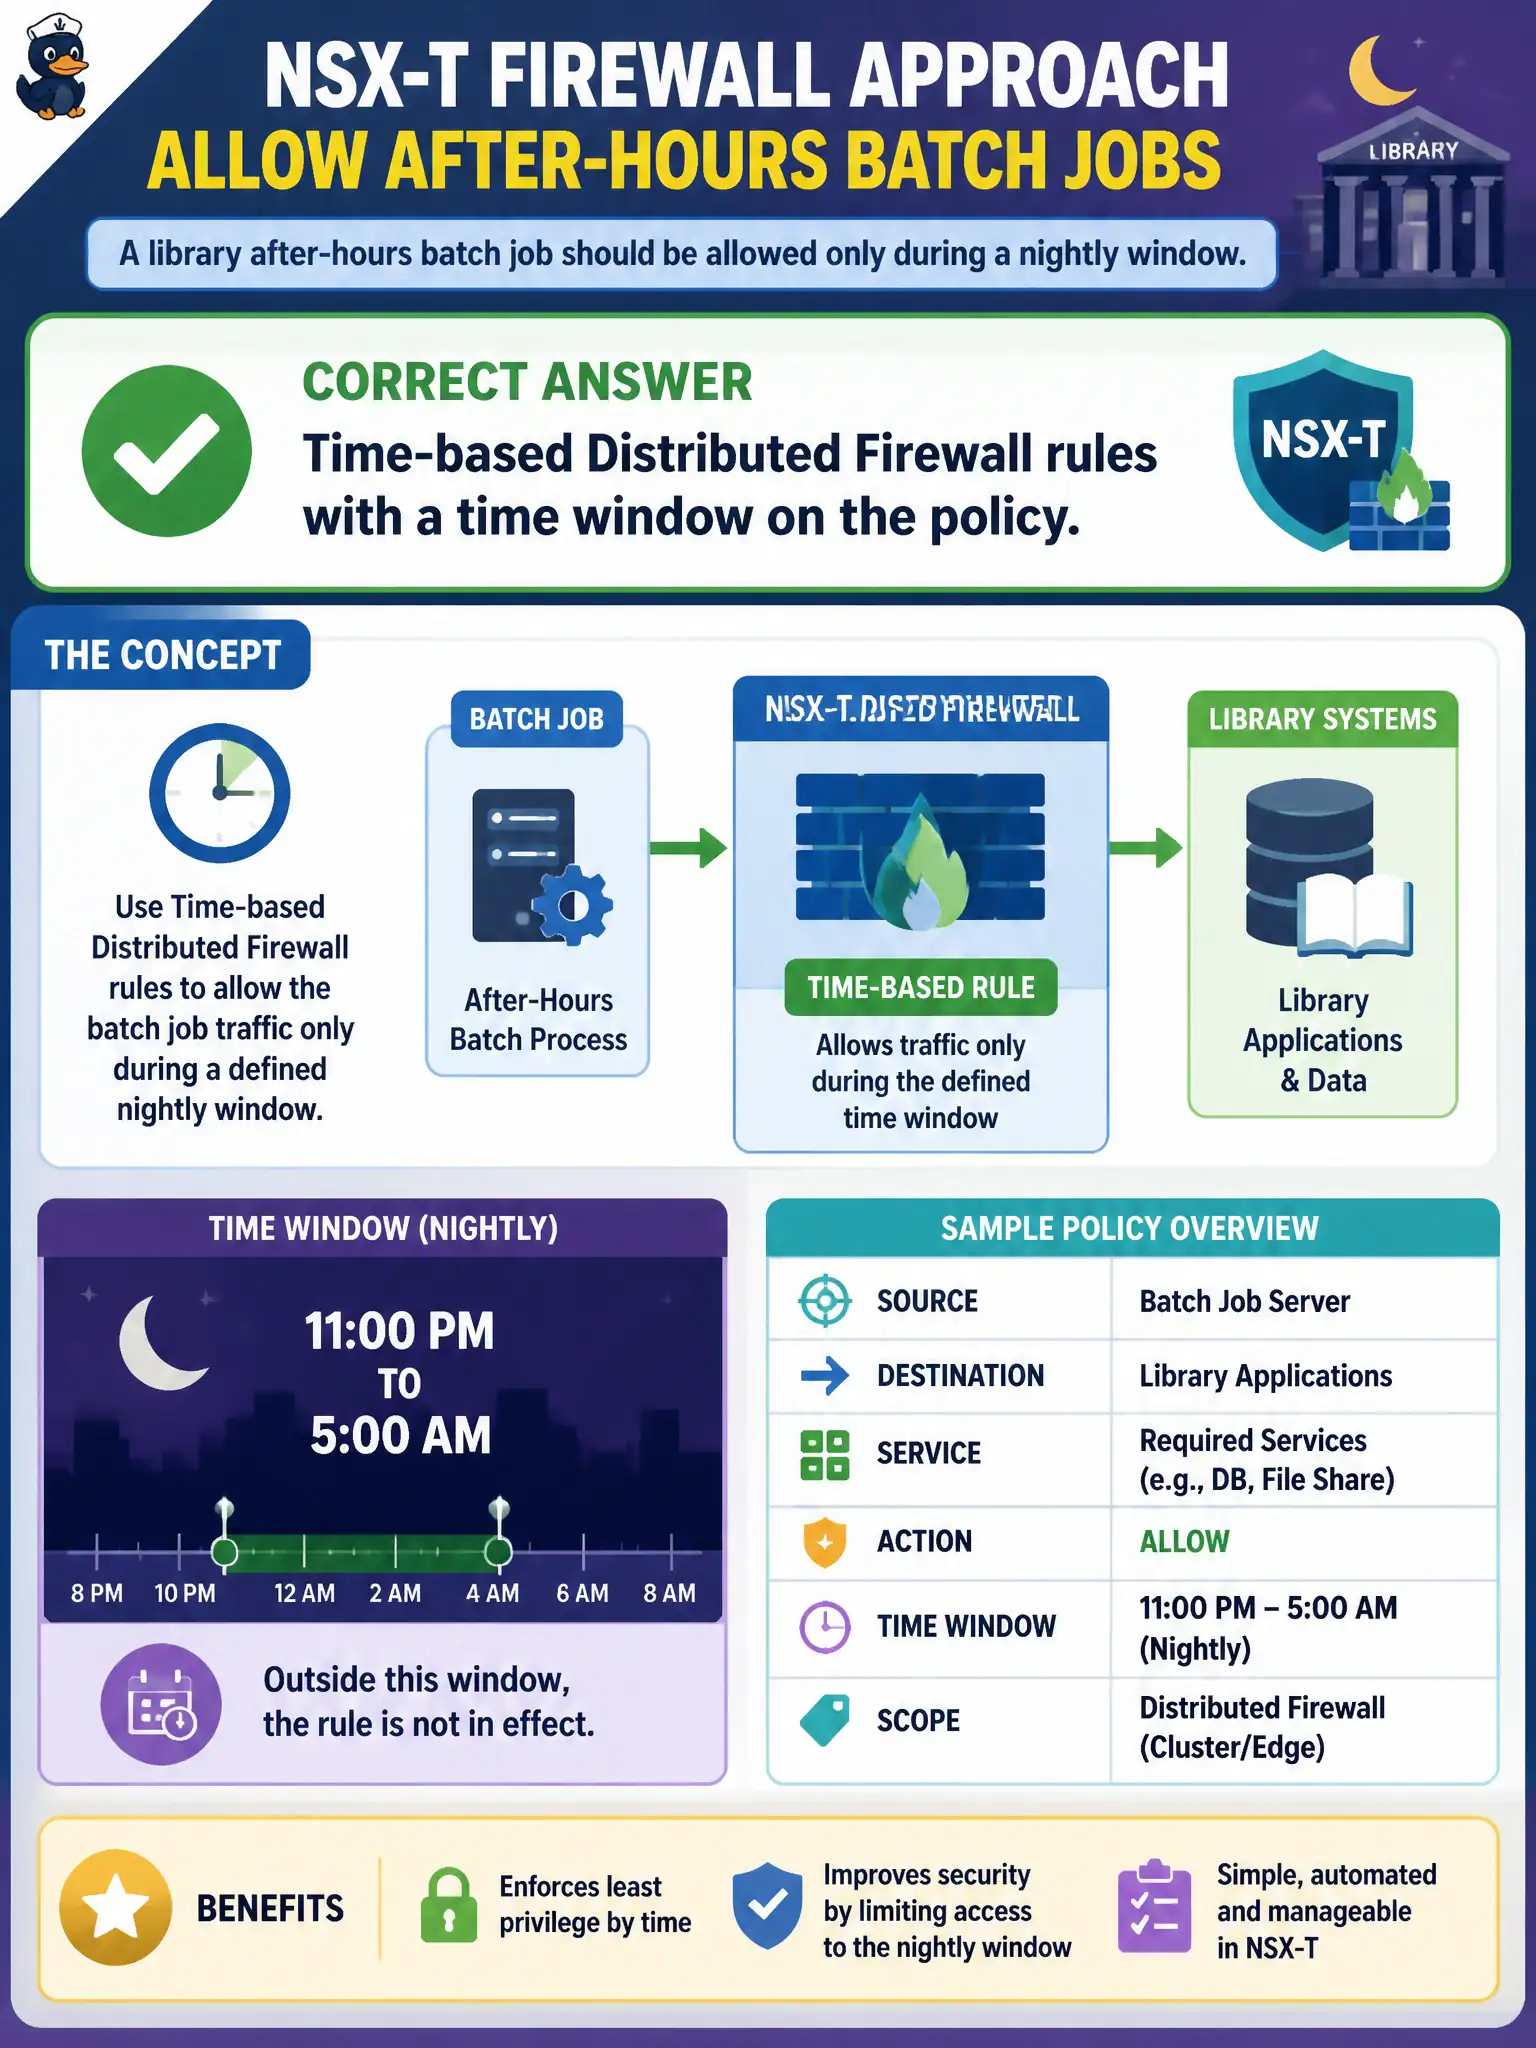
NSX already has a timer on the rule—use it. Time-based Distributed Firewall windows open the after-hours path and close it without a cron that deletes policy. Quarantining sensors or killing the whole firewall is swinging a sledgehammer at a library batch job.
Full Explanation
A library after-hours batch job that may run only in a nightly window belongs on time-based Distributed Firewall rules with a time window on the policy. NSX-T can constrain when the allow is active so the batch path opens at night and closes without human cron surgery on the rule base.
A cron job that deletes allow rules at dawn and recreates them at dusk is brittle operational theater, not the supported time-based policy model. Carbon Black Cloud sensor quarantine on a nightly schedule is endpoint isolation, not scheduled DFW allows for a batch conversation. Disabling the entire Distributed Firewall outside business hours drops all micro-segmentation instead of scoping one batch allow.
Exam caveat: prefer native time-based DFW over external scripts that rewrite policy.
Operational check: attach a time window to the batch allow, test inside and outside the window, confirm hit counters behave as expected, and document the window owners for library operations.
Time-based DFW gives the library a scheduled night door without cron deleting policy. Monitor the first few window transitions, alert if the allow fails to close at dawn, and keep the batch owner’s on-call contact on the rule comment so morning incidents route to the right team.