
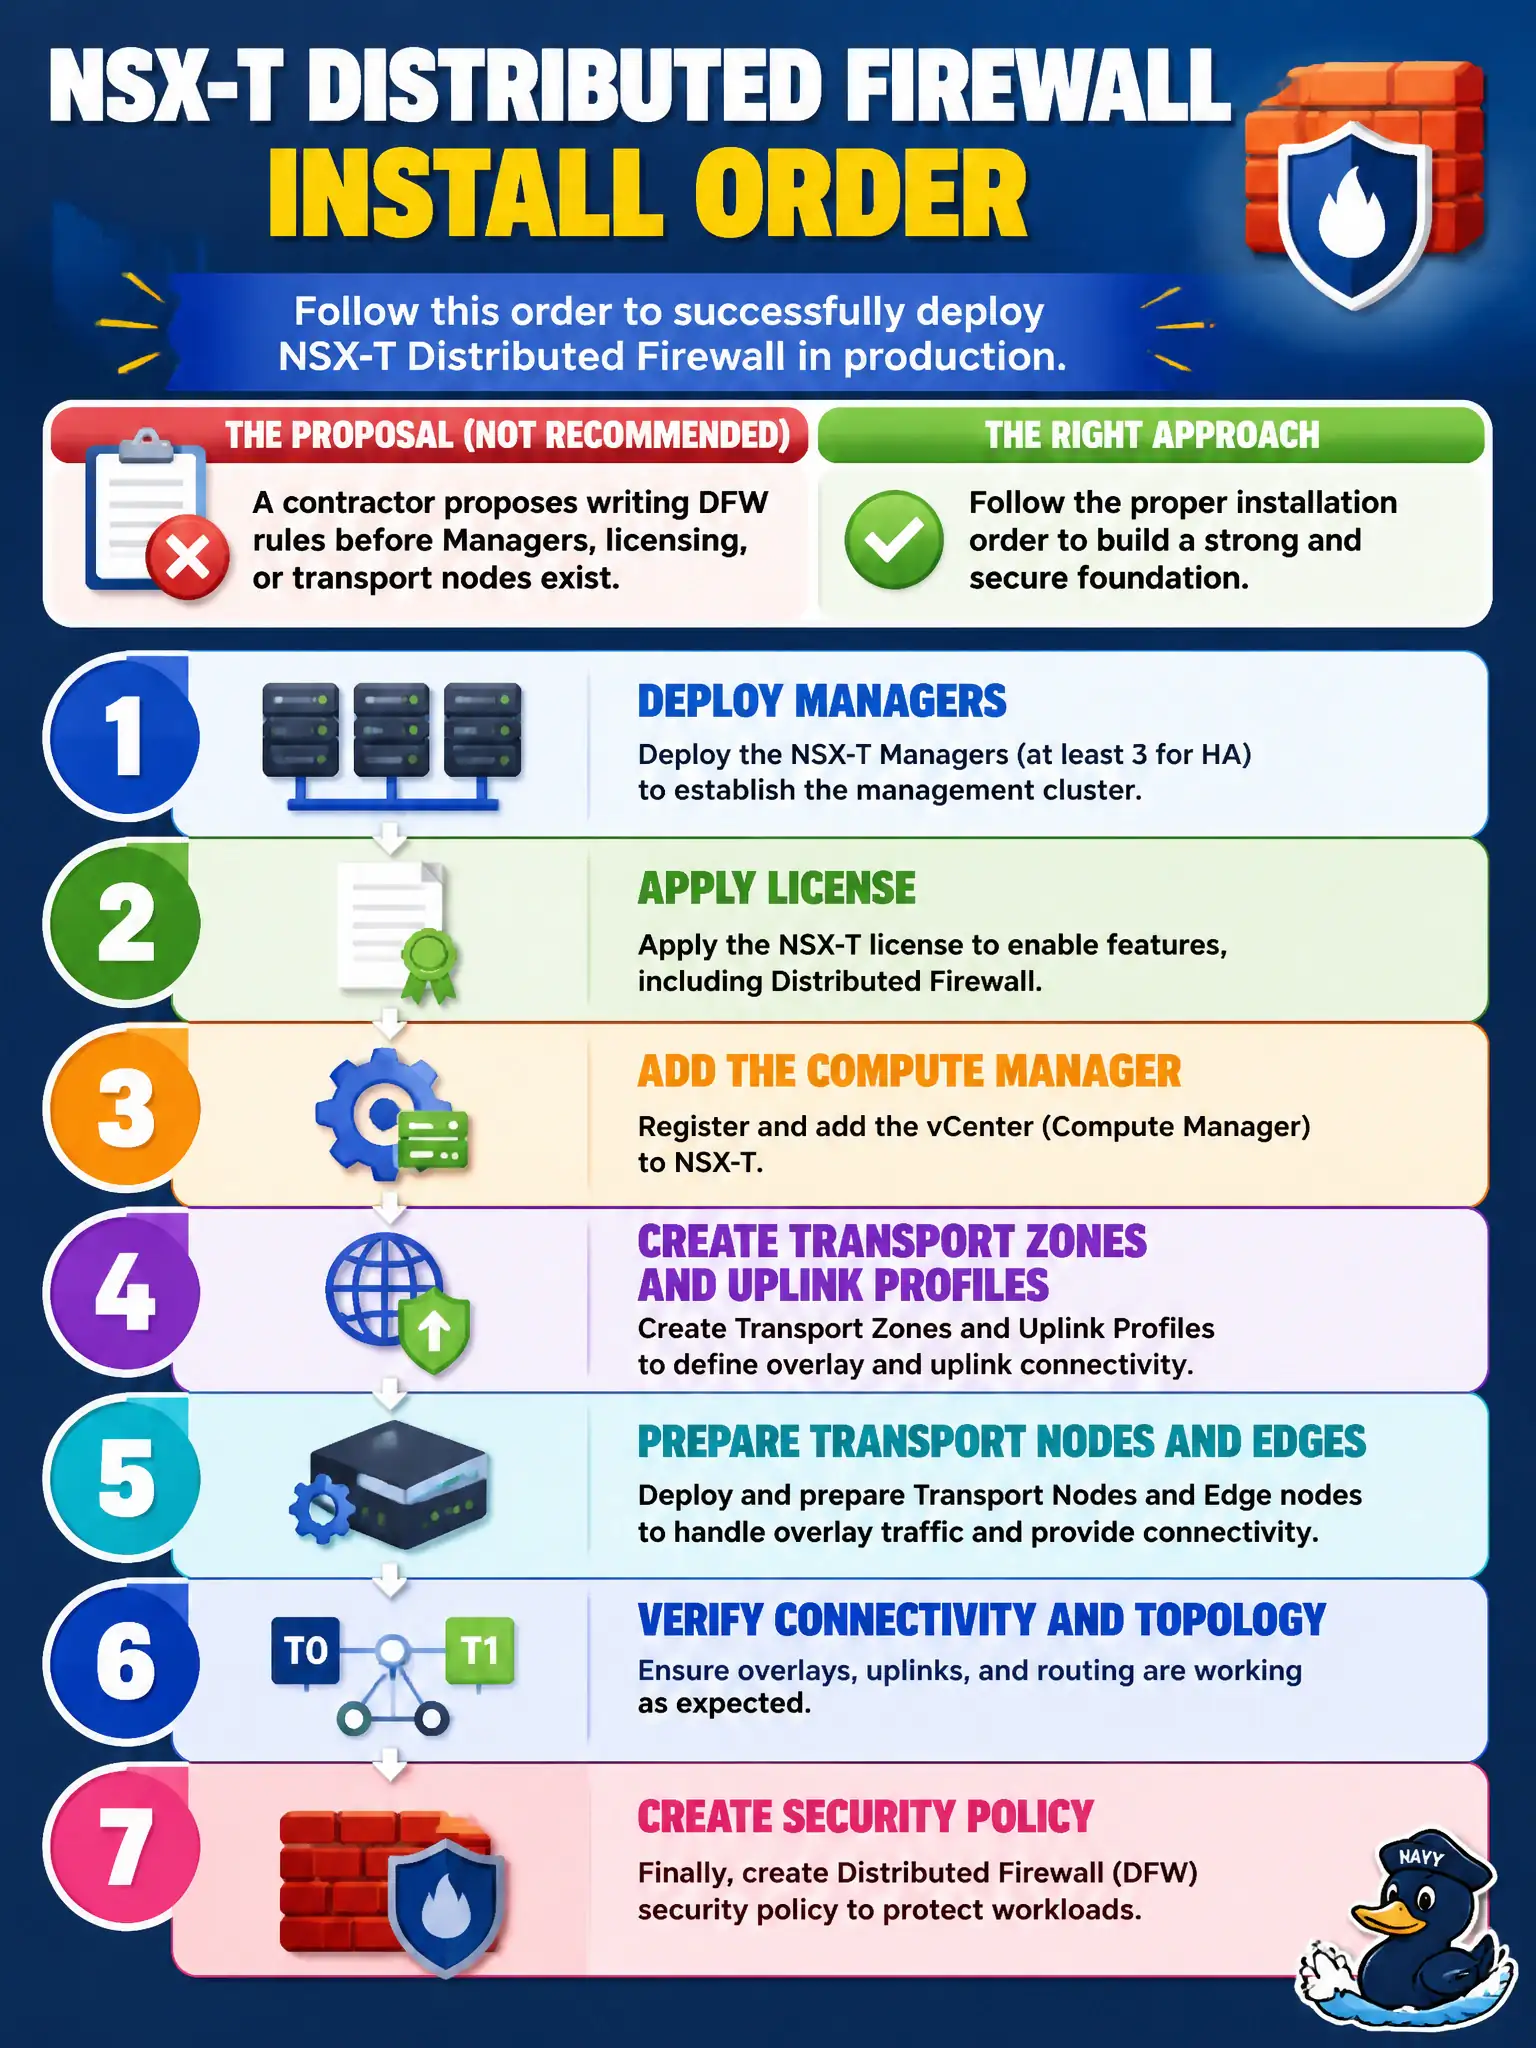
The city wants NSX-T distributed firewall in production. A contractor proposes writing DFW rules before Managers, licensing, or transport nodes exist. What install order should the administrator follow?
Select an answer to reveal the explanation.
Short Explanation
You do not paint lane lines before the road exists. Stand Managers, license, compute manager, transport zones, transport nodes, and Edges first—DFW rules have nowhere to realize until that fabric is up.
Full Explanation
City production NSX-T distributed firewall follows a disciplined install order: deploy Managers, apply license, add the compute manager, create transport zones and uplink profiles, prepare transport nodes and Edges, then create security policy. Rules published before that fabric exists have nowhere to realize and create false confidence in the civic build.
Publishing DFW rules first so they “wait in queue” until Manager install is not a valid bootstrap sequence. Installing Carbon Black Cloud and pasting the same rules into NSX later mixes products and skips NSX prerequisites. Registering Workspace ONE Access cannot replace NSX Managers or realize distributed firewall.
Exam caveat: control plane → license → inventory/transport zones/uplinks → transport nodes/Edges → policy is the order VCP-SEC expects.
Operational check: checklist each prerequisite green before first production rule publish, validate realization on a pilot workload, and keep the ordered build sheet in the city NSX commissioning record.
Install order is the city’s road-before-paint rule for NSX. Keep a gated checklist in the commissioning ticket: Managers healthy, license applied, compute manager trusted, transport zones and uplink profiles present, nodes and Edges Up—only then allow the first production DFW section to publish, with a pilot realization screenshot attached.