
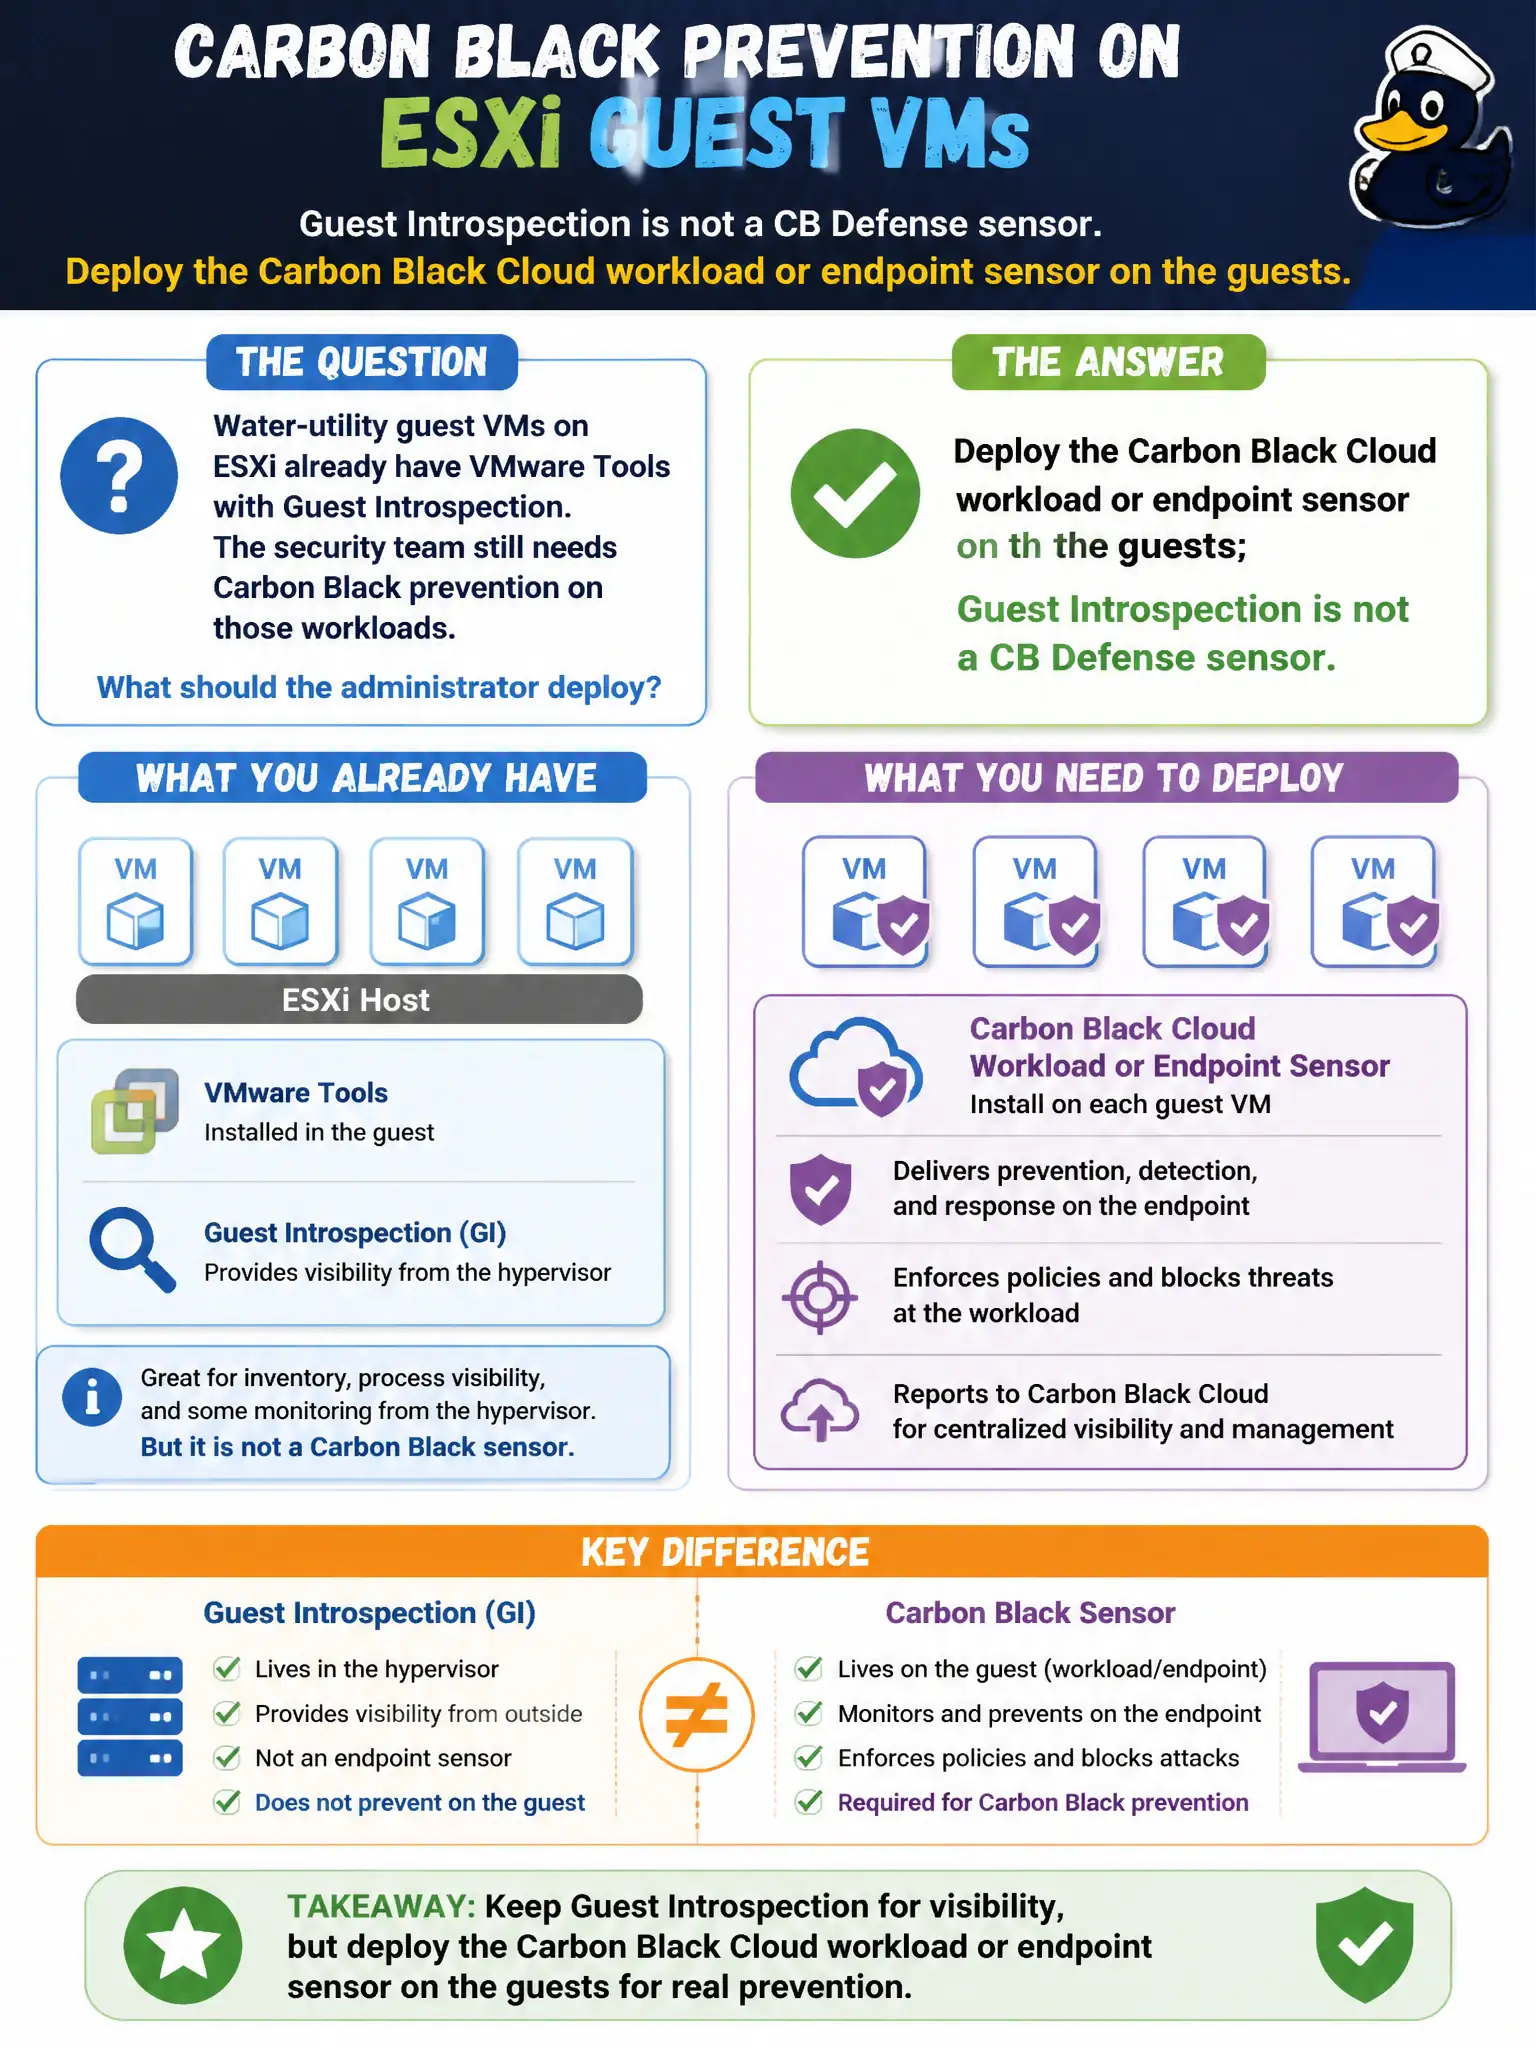
Water-utility guest VMs on ESXi already have VMware Tools with Guest Introspection. The security team still needs Carbon Black prevention on those workloads. What should the administrator deploy?
Select an answer to reveal the explanation.
Short Explanation
Guest Introspection is a different tool on the workbench—handy for NSX guest features, not the Carbon Black smoke detector. Still install the CBC workload or endpoint sensor on those utility VMs. VMTools being present does not check the guest into the Carbon Black console.
Full Explanation
Water-utility guest VMs on ESXi already have VMware Tools with Guest Introspection, yet the security team still needs Carbon Black prevention. Deploy the Carbon Black Cloud workload or endpoint sensor on the guests—Guest Introspection is a different tool on the workbench, handy for NSX guest features, not the Carbon Black smoke detector. Doing nothing further because VMware Tools Guest Introspection already registers the VM in Carbon Black Cloud fails by concept because GI does not check guests into the CBC console as CB Defense sensors. Only an NSX-T distributed firewall any-any allow substituting for an endpoint sensor fails because DFW any-any is network policy, not process prevention, and weakens segmentation. A Workspace ONE UEM iOS profile on the ESXi host fails because iOS profiles do not apply to ESXi hosts or Linux/Windows guests as CBC sensors. Exam caveat: CBC prevention on guests requires the CBC workload/endpoint sensor—GI presence ≠ CBC registration; DFW any-any and UEM iOS profiles are wrong substitutes. Operational check: install the CBC sensor on a utility guest, confirm console registration and policy, verify GI remains for its NSX purposes without being treated as CBC, and reject any-any as a sensor substitute. Update the utility VM build standard so new guests include the CBC sensor package by default.