
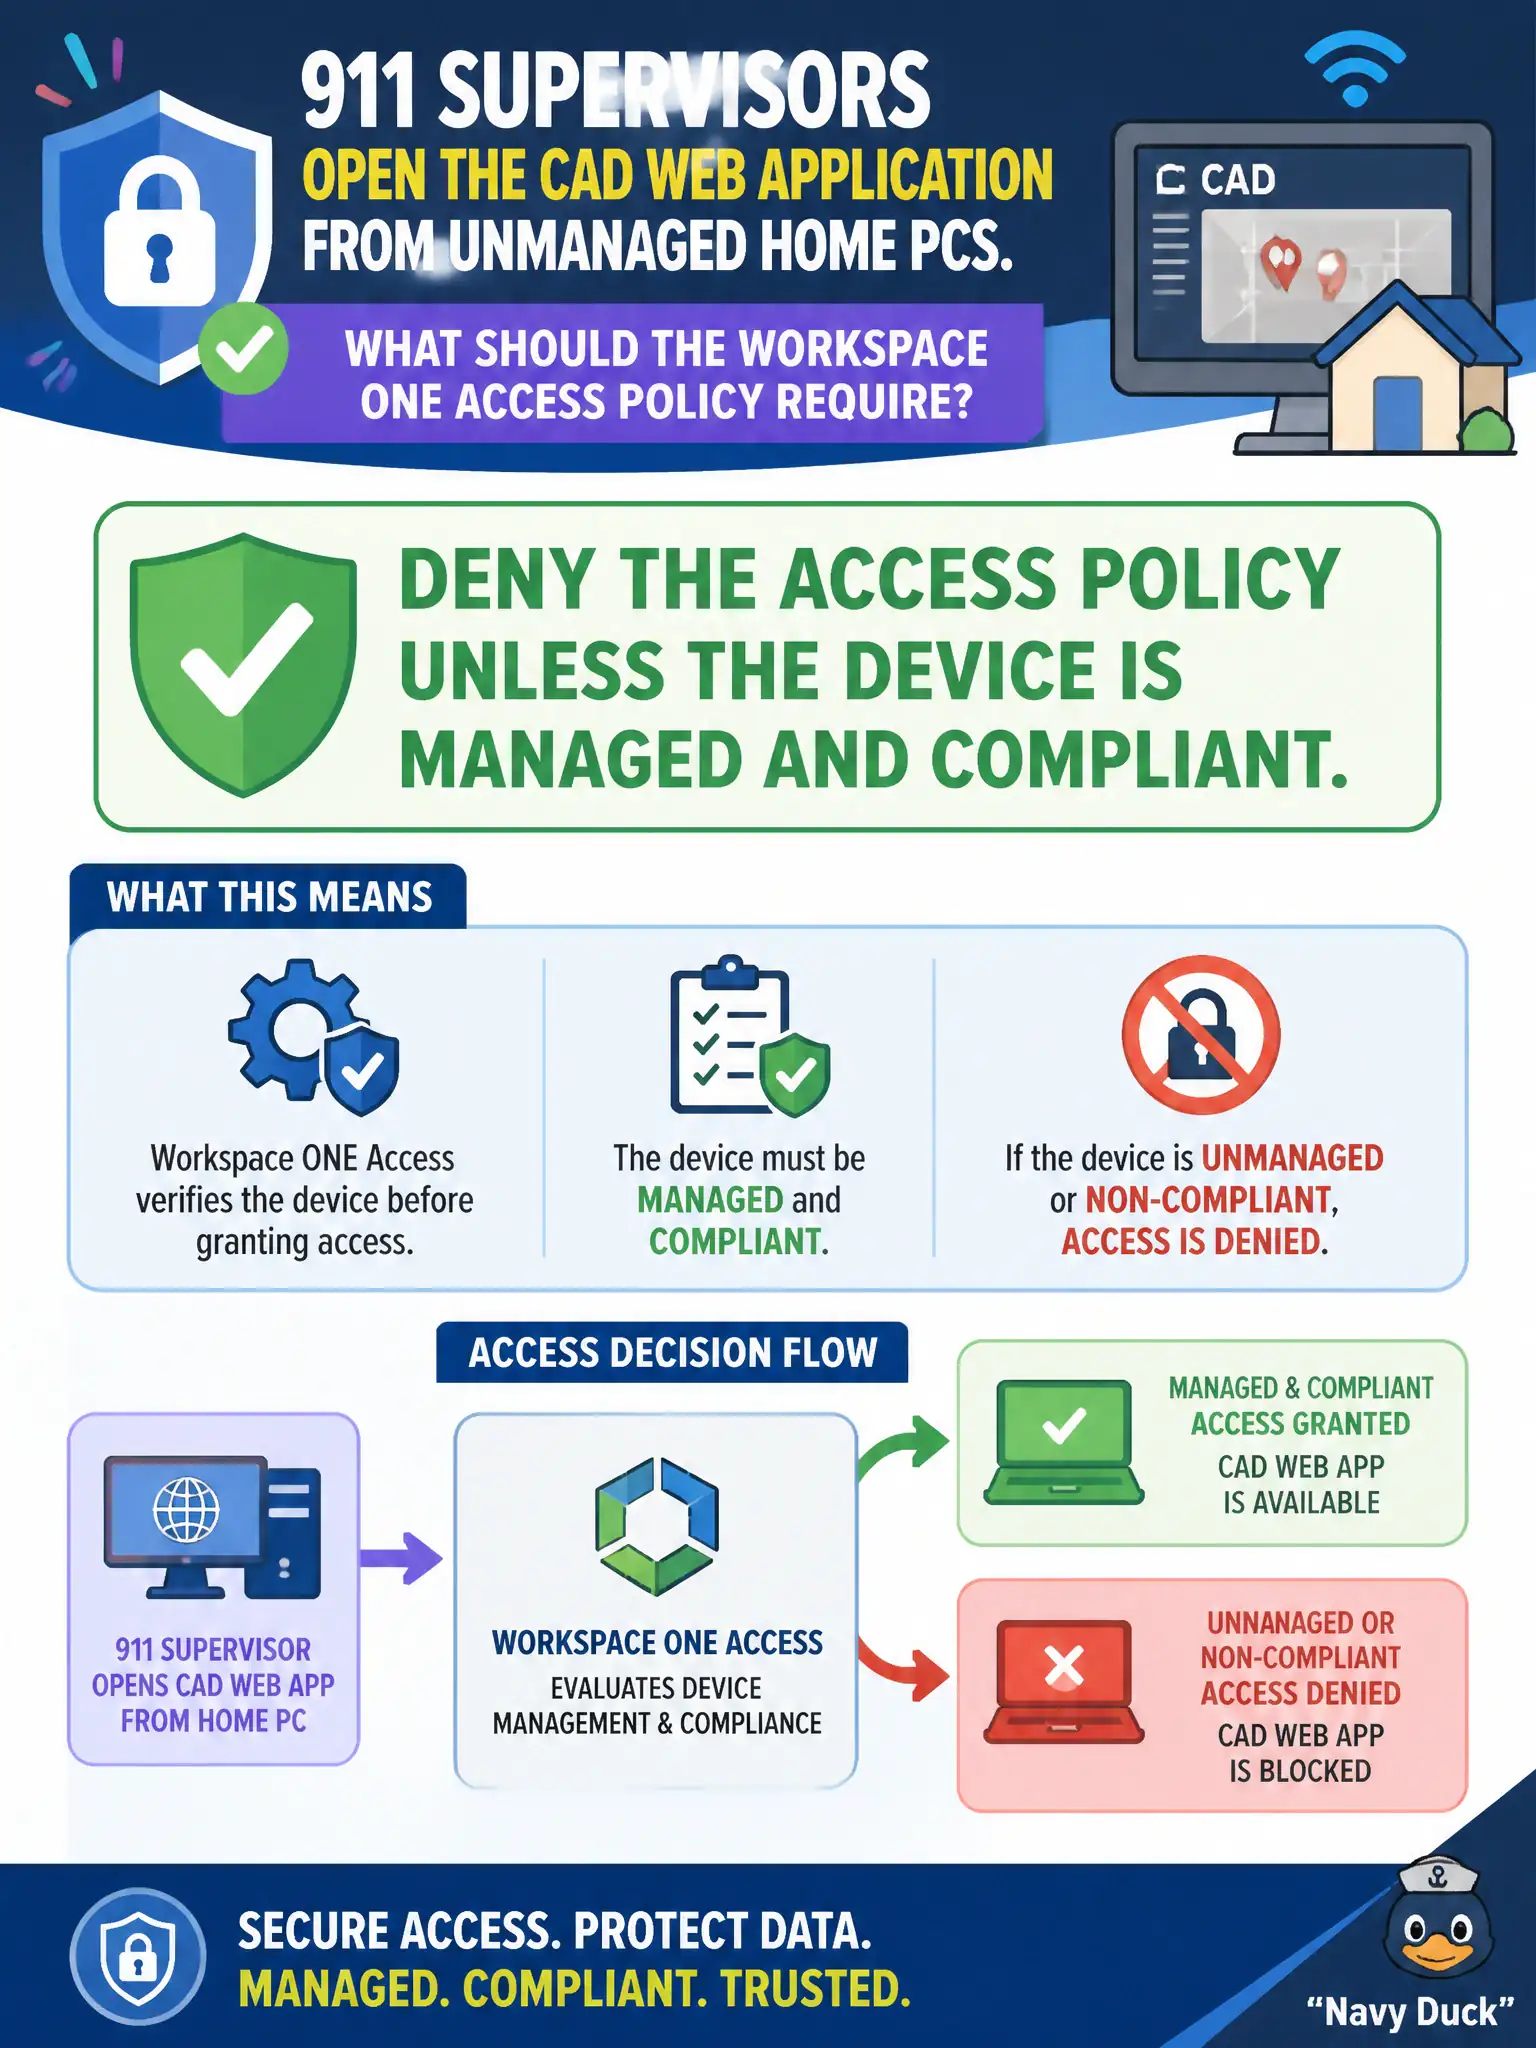
911 supervisors open the CAD web application from unmanaged home PCs. What should the Workspace ONE Access policy require?
Select an answer to reveal the explanation.
Short Explanation
CAD from a mystery home PC is like running 911 from a café kiosk. Access can demand a managed, compliant device before SSO. Password-from-anywhere is convenient and exactly the hole the city does not want.
Full Explanation
911 supervisors opening the CAD web application from unmanaged home PCs should face a Workspace ONE Access policy that denies unless the device is managed and compliant—CAD from a mystery home PC is like running 911 from a café kiosk. Allowing password-only authentication from any network fails by concept because convenience creates exactly the unmanaged exposure the city must avoid for CAD. Publishing CAD as a UEM public web clip with no Access policy fails because a web clip without Access policy does not enforce managed compliant device requirements. Isolating the home PC with Carbon Black Cloud and then allowing password-only CAD fails because CBC isolate is not a substitute for Access device posture on the CAD SSO path, and password-only still weakens CAD. Exam caveat: sensitive CAD access via Access should require managed and compliant devices—not password-from-anywhere, not public web clip without policy, not CBC isolate plus password. Operational check: attempt CAD SSO from a managed compliant device (allow) and from an unmanaged home PC (deny), confirm password-only any-network is not enabled, and document exceptions only through formal public-safety risk acceptance. Provide supervisors a managed device path (city laptop or compliant phone) so operational need does not force a policy rollback.