
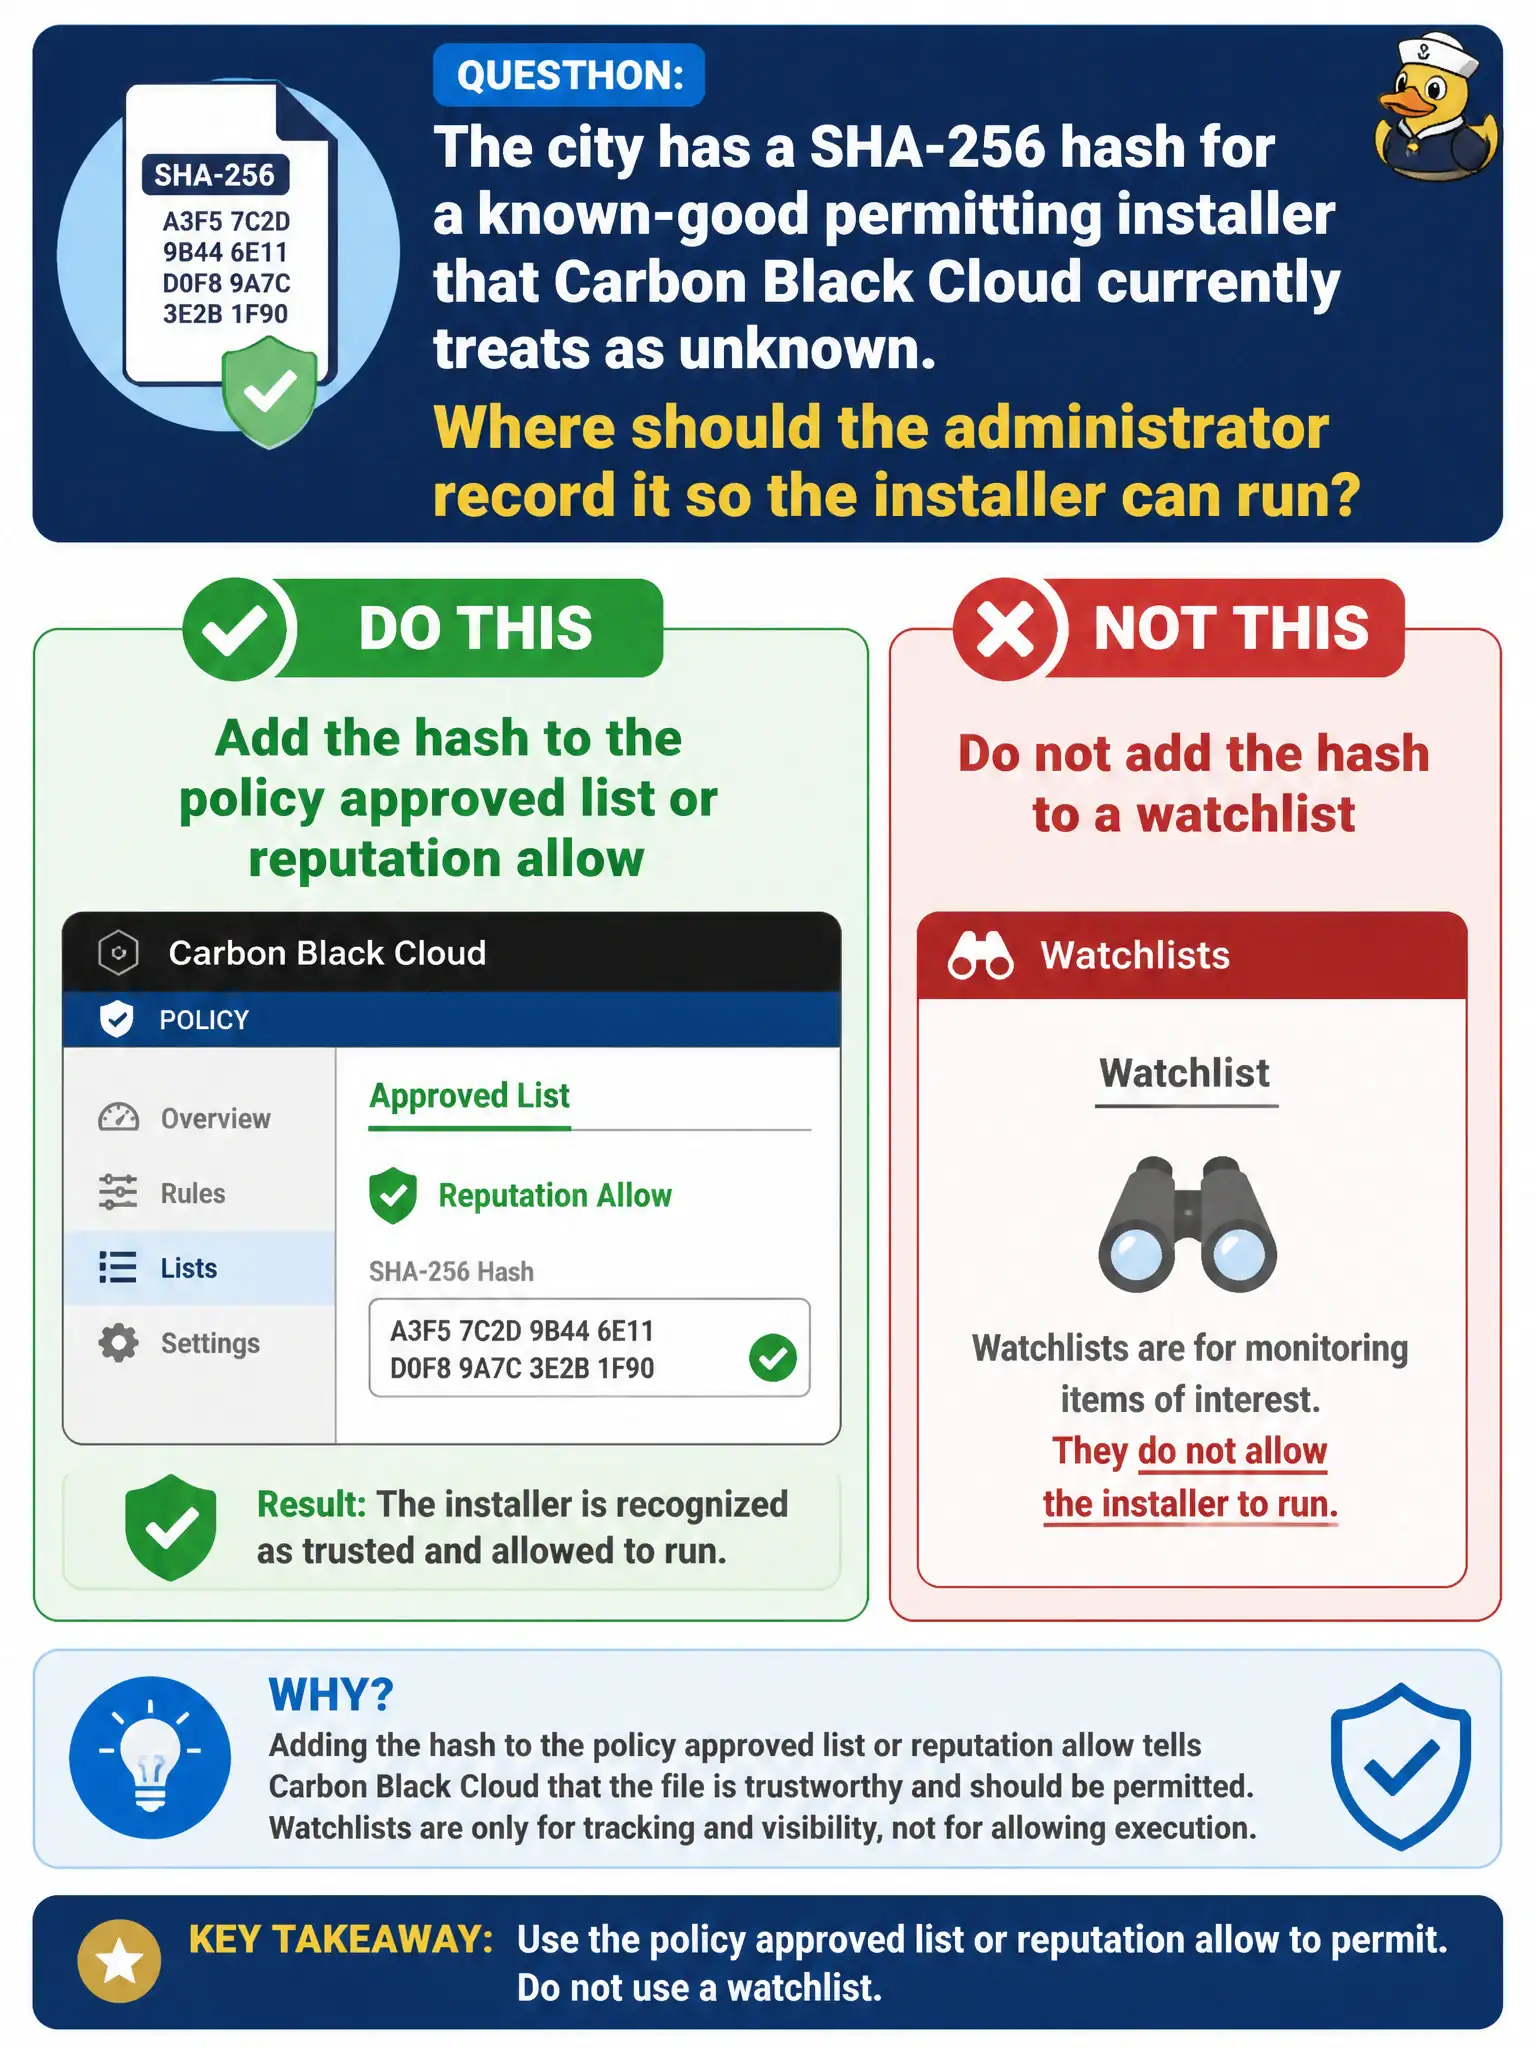
The city has a SHA-256 hash for a known-good permitting installer that Carbon Black Cloud currently treats as unknown. Where should the administrator record it so the installer can run?
Select an answer to reveal the explanation.
Short Explanation
A watchlist is a wanted poster, not a building permit. Put the known-good hash on the policy approved list or reputation allow so the installer can run.
Full Explanation
When the city has a SHA-256 hash for a known-good permitting installer that Carbon Black Cloud treats as unknown, add the hash to the policy approved list or reputation allow—not to a watchlist. A watchlist is a wanted poster, not a building permit. Adding the hash to an Enterprise EDR watchlist used for hunting fails by concept because watchlists surface activity for investigation; they do not grant execution permission. Pasting the hash into an NSX-T context profile on a T1 gateway fails because NSX context profiles classify network traffic, not CBC process reputation on the endpoint. Opening a helpdesk ticket to exclude the hash from syslog only fails because log exclusion does not allow the installer to run under prevention policy. Exam caveat: known-good execution requires CBC approve/allow reputation or policy approved list—not watchlist, not NSX context, not syslog mute. Operational check: add the SHA-256 to the approved list or reputation allow on the relevant policy, run the permitting installer on a test Finance or permitting PC, and confirm it is no longer treated as unknown/blocked. Store the hash and software version in the city change ticket so the next installer build gets a fresh approve rather than an orphaned old hash.