
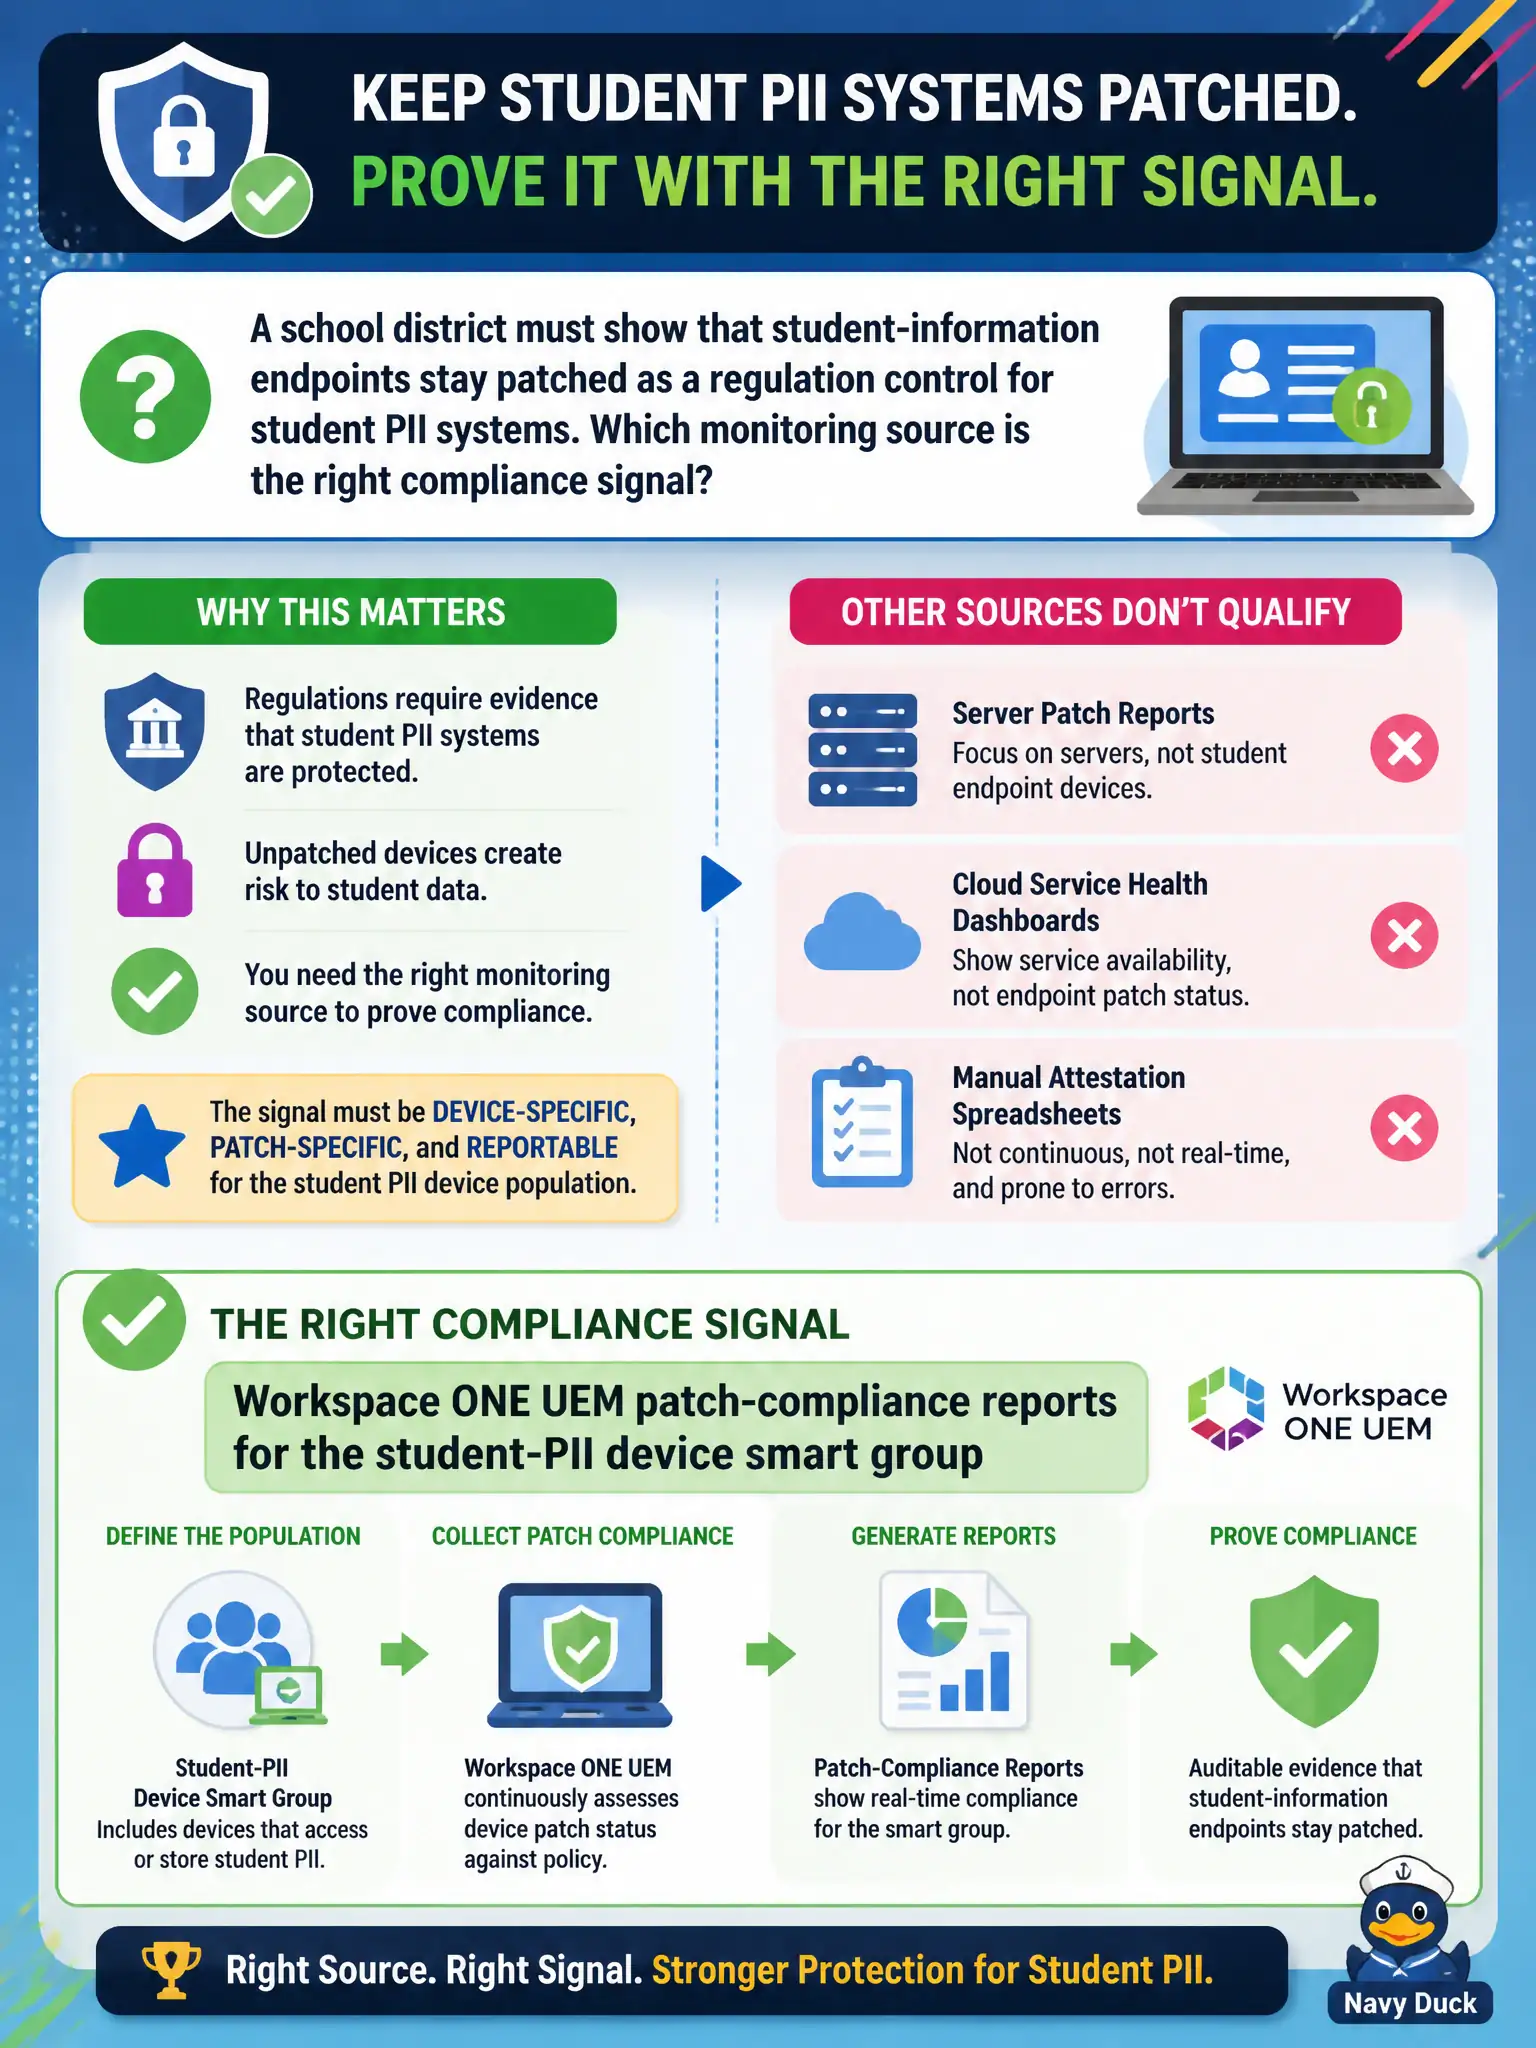
A school district must show that student-information endpoints stay patched as a regulation control for student PII systems. Which monitoring source is the right compliance signal?
Select an answer to reveal the explanation.
Short Explanation
Patch status is the hall pass for student-PII devices. Read it from Workspace ONE UEM compliance on that smart group, not from gateway session counts.
Full Explanation
A school district showing that student-information endpoints stay patched as a regulation control for student PII systems must use Workspace ONE UEM patch-compliance reports for the student-PII device smart group as the compliance signal. Treat UEM patch reports as the classroom inventory of which student-PII devices received the required updates. NSX-T Gateway Firewall session counts on the student VLAN fail by concept because session counts show traffic volume, not patch posture on endpoints. Carbon Black Cloud watchlist hits only, with UEM patching ignored, fail because detections without UEM patch telemetry do not prove patch compliance. Residual-risk scoring with no Workspace ONE UEM telemetry fails because a risk score without product patch reports is not the regulation-assurance signal for patched student-PII devices. Exam caveat: UEM patch-compliance reports for the student-PII smart group are the monitoring source; gateway sessions, CBC watchlists alone, and risk scores without UEM data are not. Operational check: pull UEM patch-compliance for the student-PII smart group, remediate non-compliant devices through UEM workflows, trend compliance for auditors, and document the smart-group scope in the district PII control matrix.