
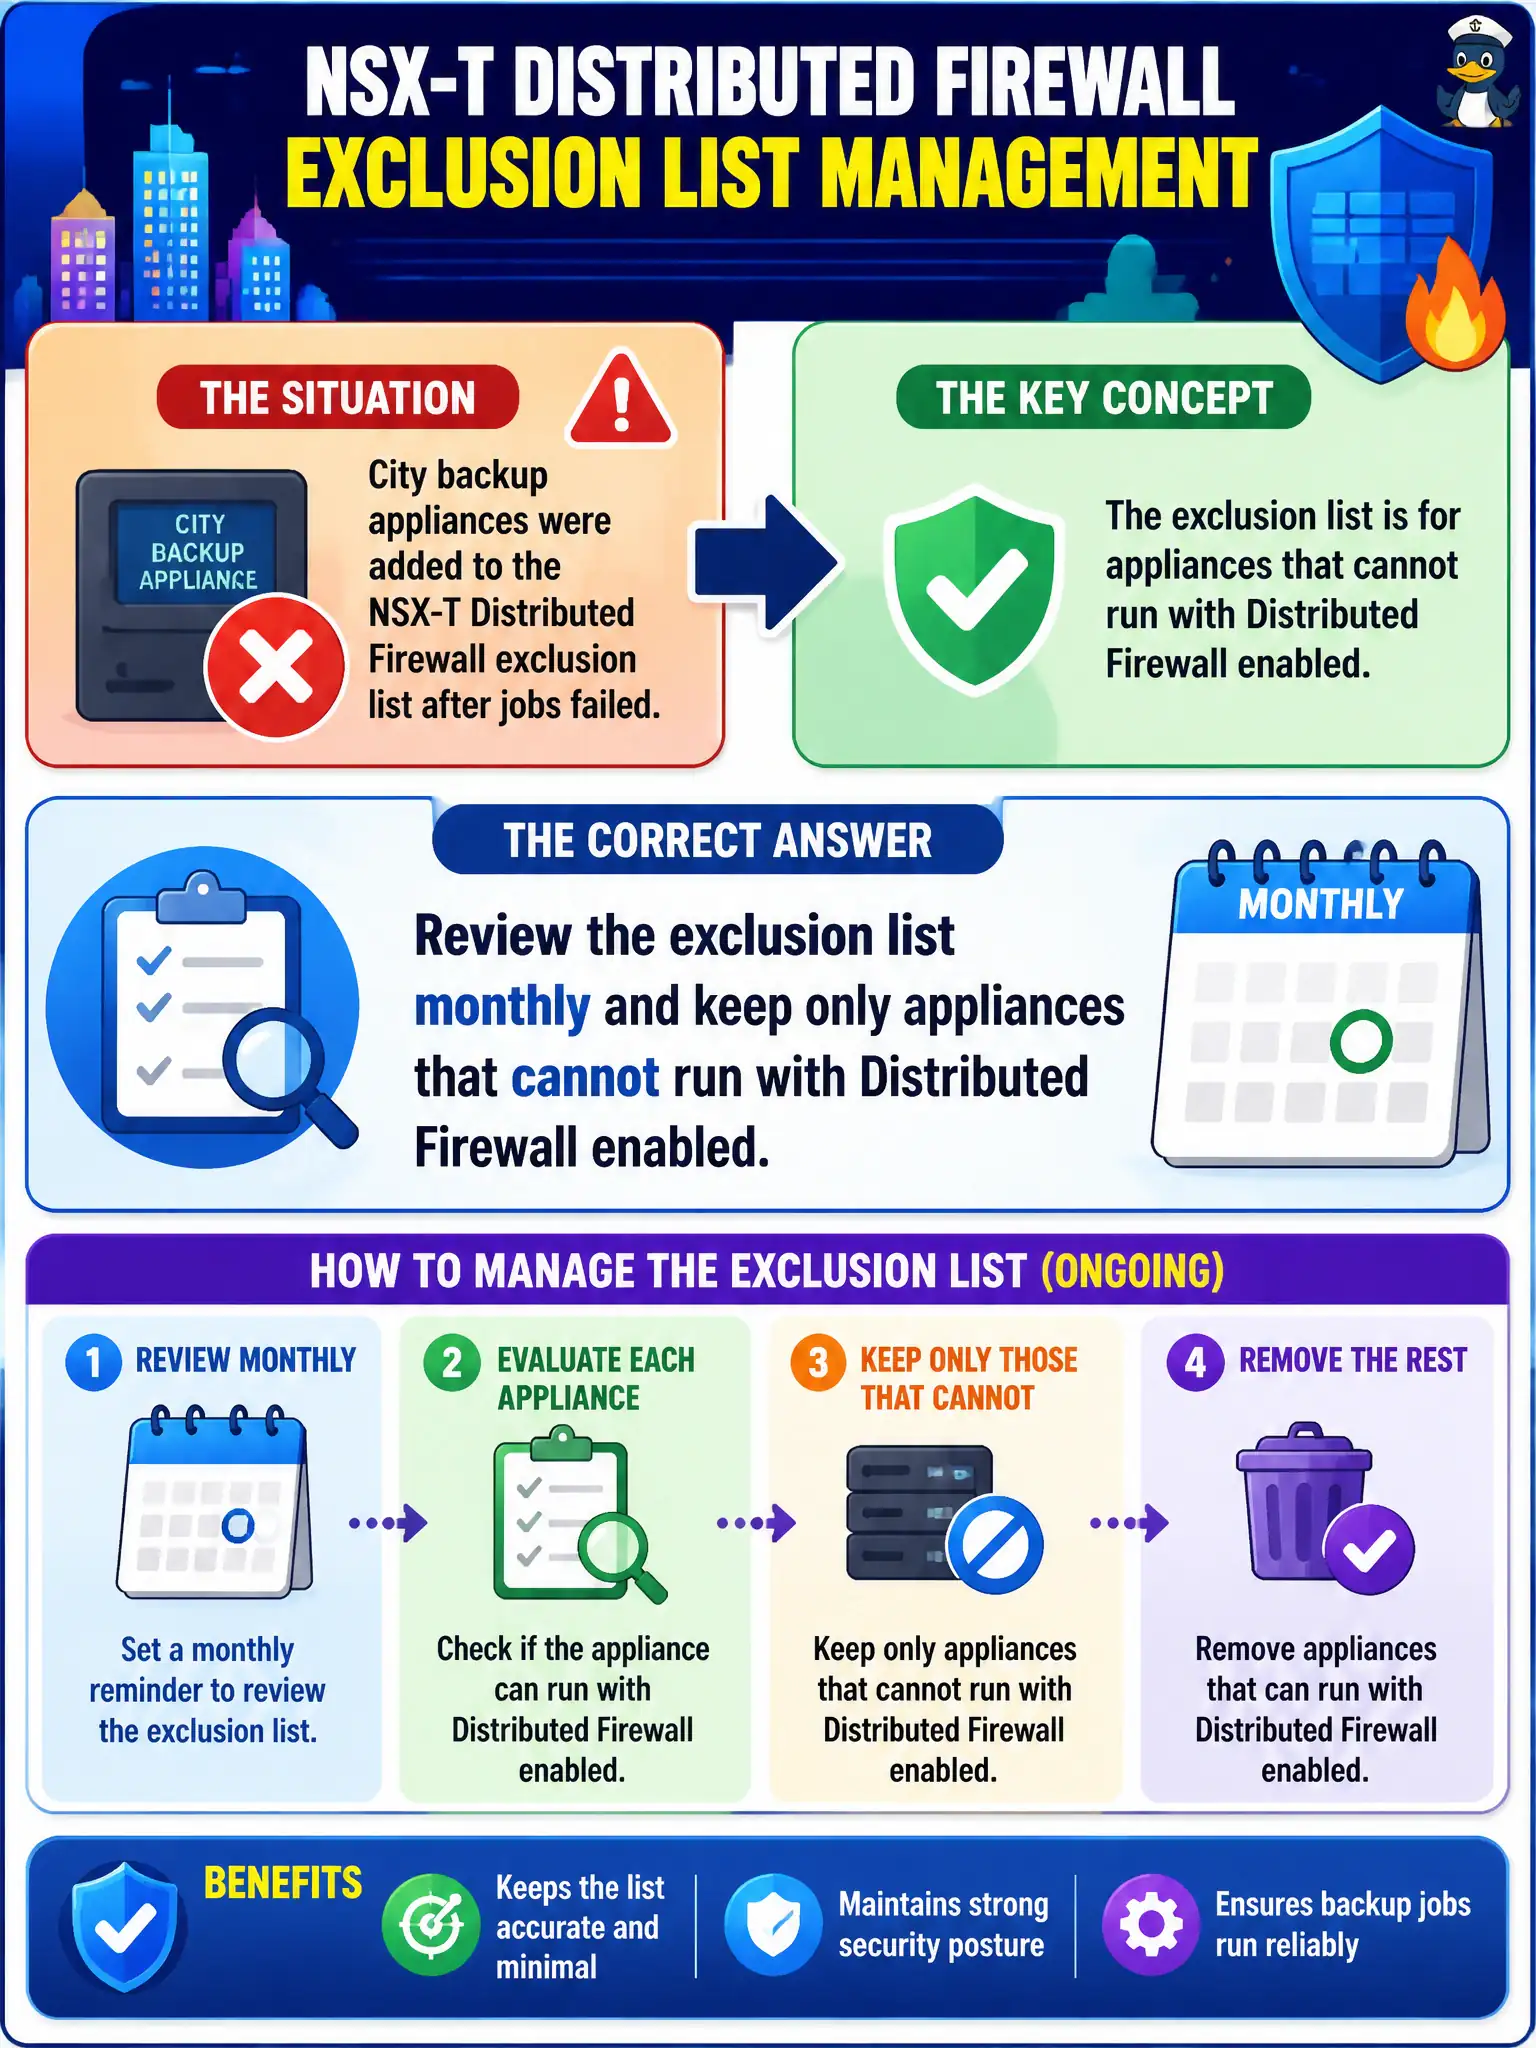
City backup appliances were added to the NSX-T Distributed Firewall exclusion list after jobs failed. What ongoing management should the administrator apply to that list?
Select an answer to reveal the explanation.
Short Explanation
The exclusion list is a side door for a few stubborn backup boxes, not a new front entrance for city hall. Walk that list every month and boot off anything that can live with the Distributed Firewall on.
Full Explanation
When city backup appliances were added to the NSX-T Distributed Firewall exclusion list after jobs failed, ongoing management is to review the exclusion list monthly and keep only appliances that cannot run with Distributed Firewall enabled. Treat exclusion as a short list of special civic vaults that skip the hallway scanners—membership must be inventoried or the list becomes a silent any-path. Adding every production VM to the exclusion list so backup windows never fail fails by concept because mass exclusion removes micro-segmentation from production and is not backup remediation. Treating exclusion as a one-time install step that never needs inventory review fails because appliances come and go and forgotten exclusions accumulate risk. Replacing the exclusion list with a paper exception memo and leaving Distributed Firewall off those hosts without tracking membership fails because paper memos do not enforce an accurate live exclusion inventory. Exam caveat: the DFW exclusion list is an operational control requiring periodic review, not a one-time checkbox or a substitute for scoped allows. Operational check: export the exclusion list monthly, validate each member still requires exclusion, remove recovered or replaced appliances, prefer scoped allows where possible, and document residual exclusions in the city backup security register.