
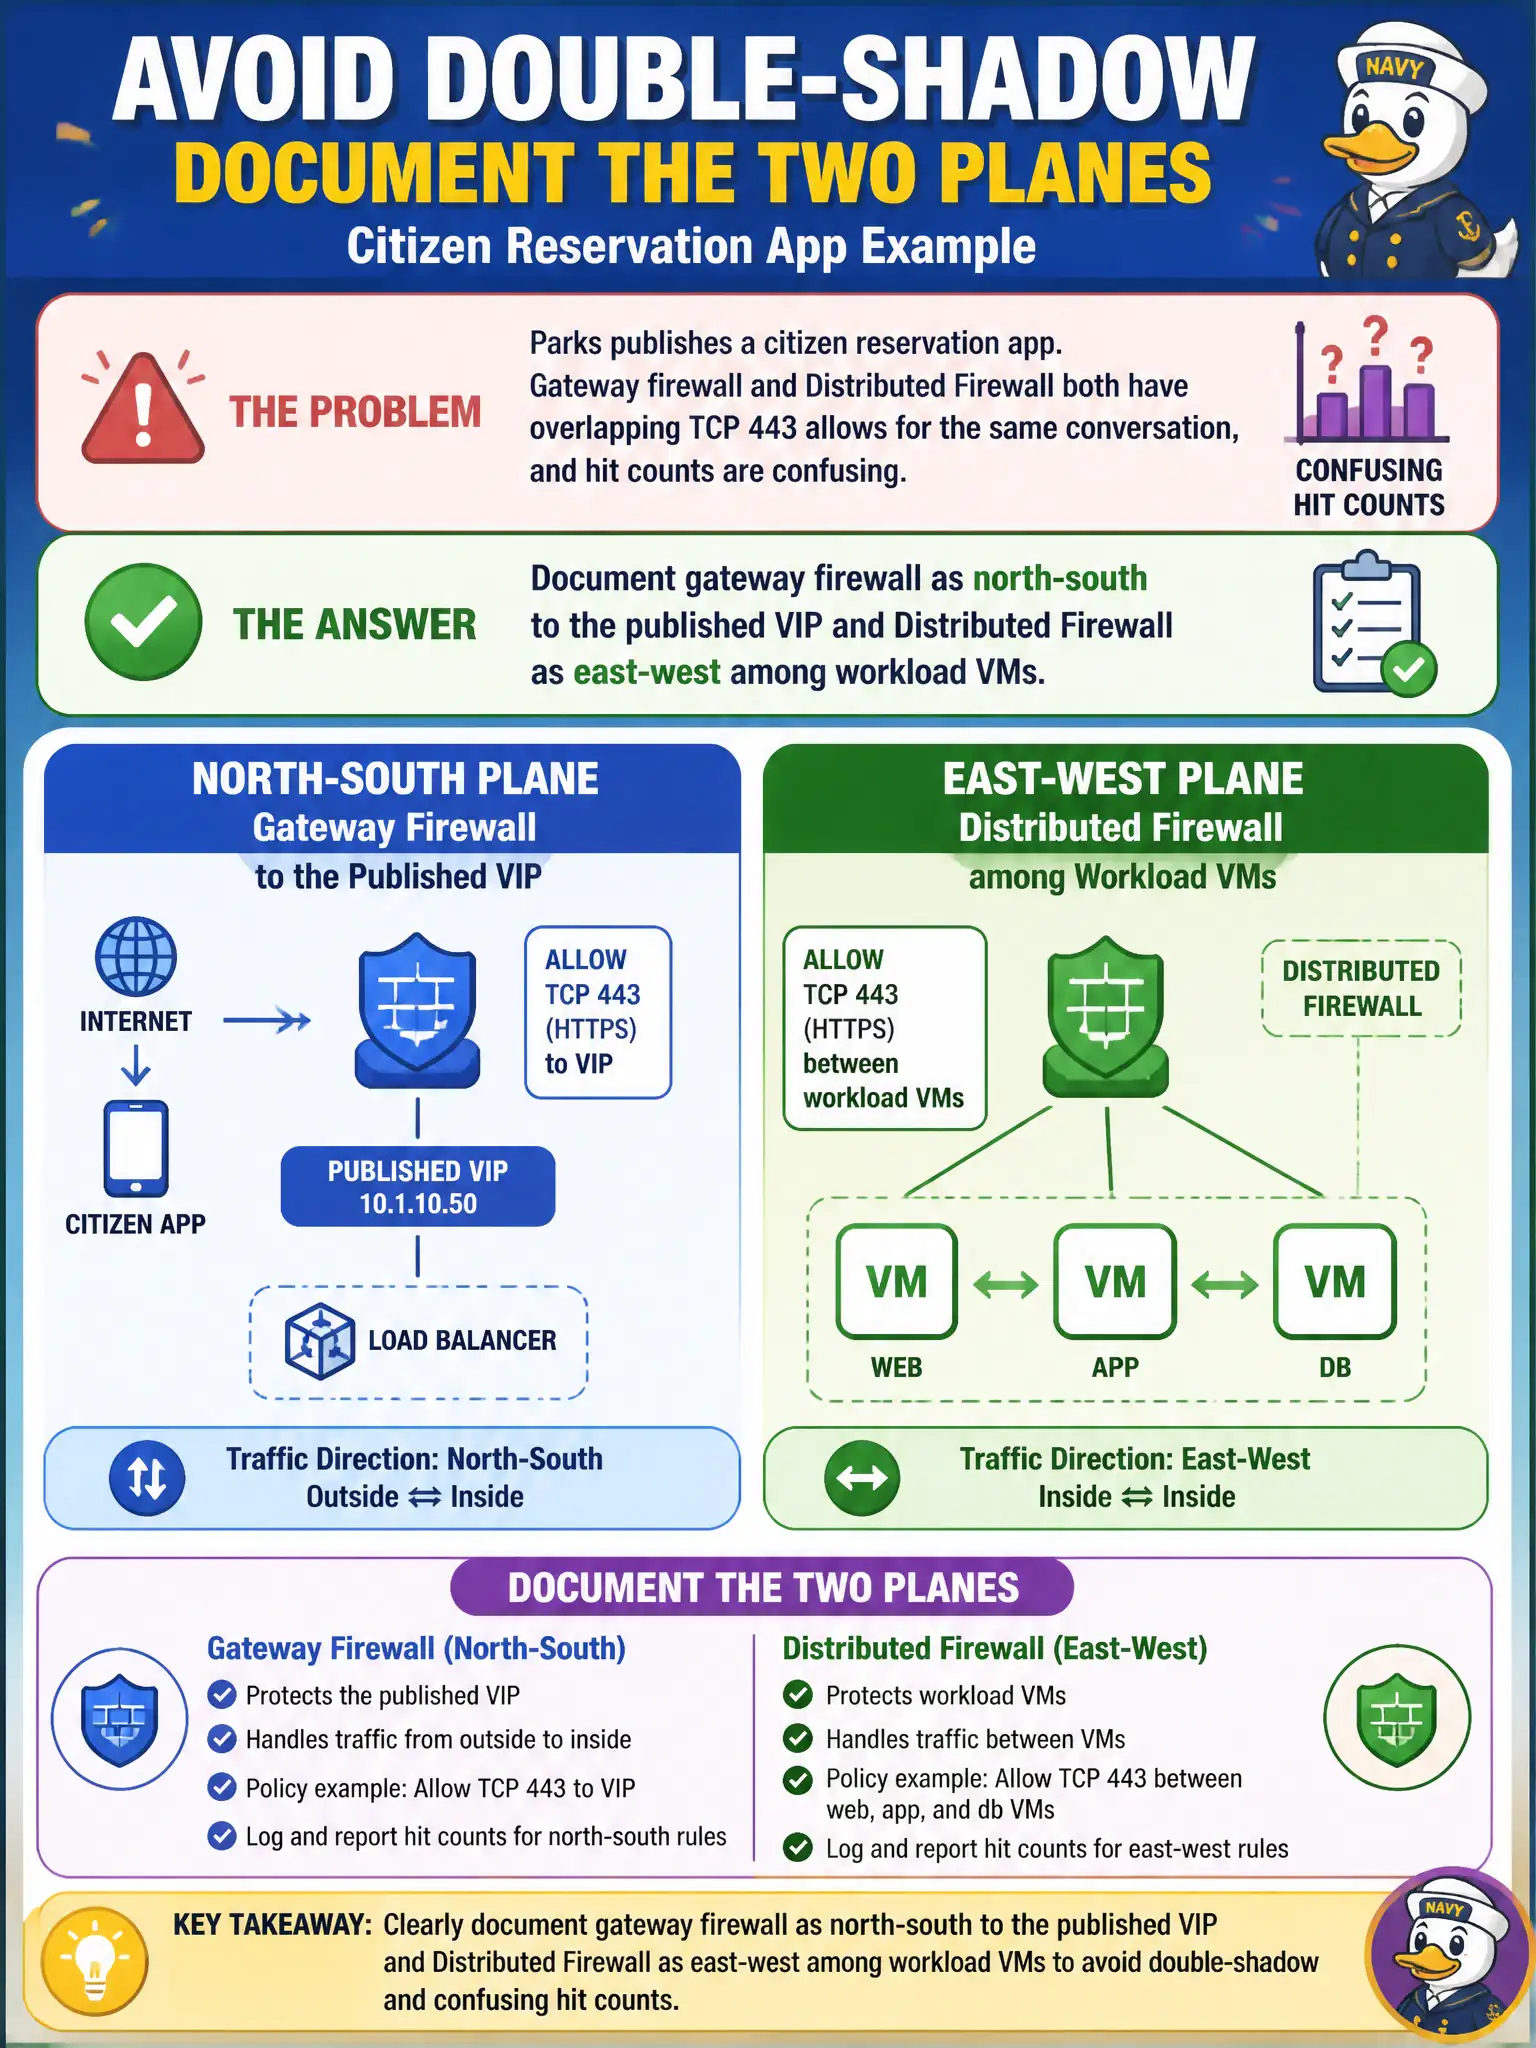
Parks publishes a citizen reservation app. Gateway firewall and Distributed Firewall both have overlapping TCP 443 allows for the same conversation, and hit counts are confusing. How should the administrator document the two planes to avoid double-shadow?
Select an answer to reveal the explanation.
Short Explanation
Two bouncers on the same door will argue about who waved the guest in. Gateway firewall watches the street (north-south); Distributed Firewall watches the rooms inside (east-west). Write that down so overlapping allows stop shadowing each other.
Full Explanation
When Parks publishes a citizen reservation app and Gateway Firewall and Distributed Firewall both have overlapping TCP 443 allows with confusing hit counts, the administrator should document gateway firewall as north-south to the published VIP and Distributed Firewall as east-west among workload VMs. Treat Gateway Firewall as the park gate for citizens arriving from the street and Distributed Firewall as the interior office doors between park workloads so each plane's hit counts mean something. Leaving any-any allows on both firewalls so neither policy can shadow the other fails by concept because dual any-any destroys meaningful enforcement and makes hit counts useless for troubleshooting. Documenting only the Tier-0 OSPF adjacency because routing is the security control fails because adjacency state is not a substitute for documenting which firewall plane owns north-south versus east-west. Disabling Distributed Firewall on Edge nodes so gateway policy is the only layer that ever logs fails because Edge DFW disable does not clarify plane roles and can remove needed east-west or Edge-local enforcement. Exam caveat: avoid double-shadow by documenting GFW as north-south to the VIP and DFW as east-west among workloads; any-any on both, OSPF docs alone, or disabling Edge DFW are not the documentation fix. Operational check: map citizen VIP flows to Gateway Firewall hits and intra-workload flows to Distributed Firewall hits, remove redundant overlapping allows where one plane owns the conversation, and update the parks firewall design document with that plane split.