
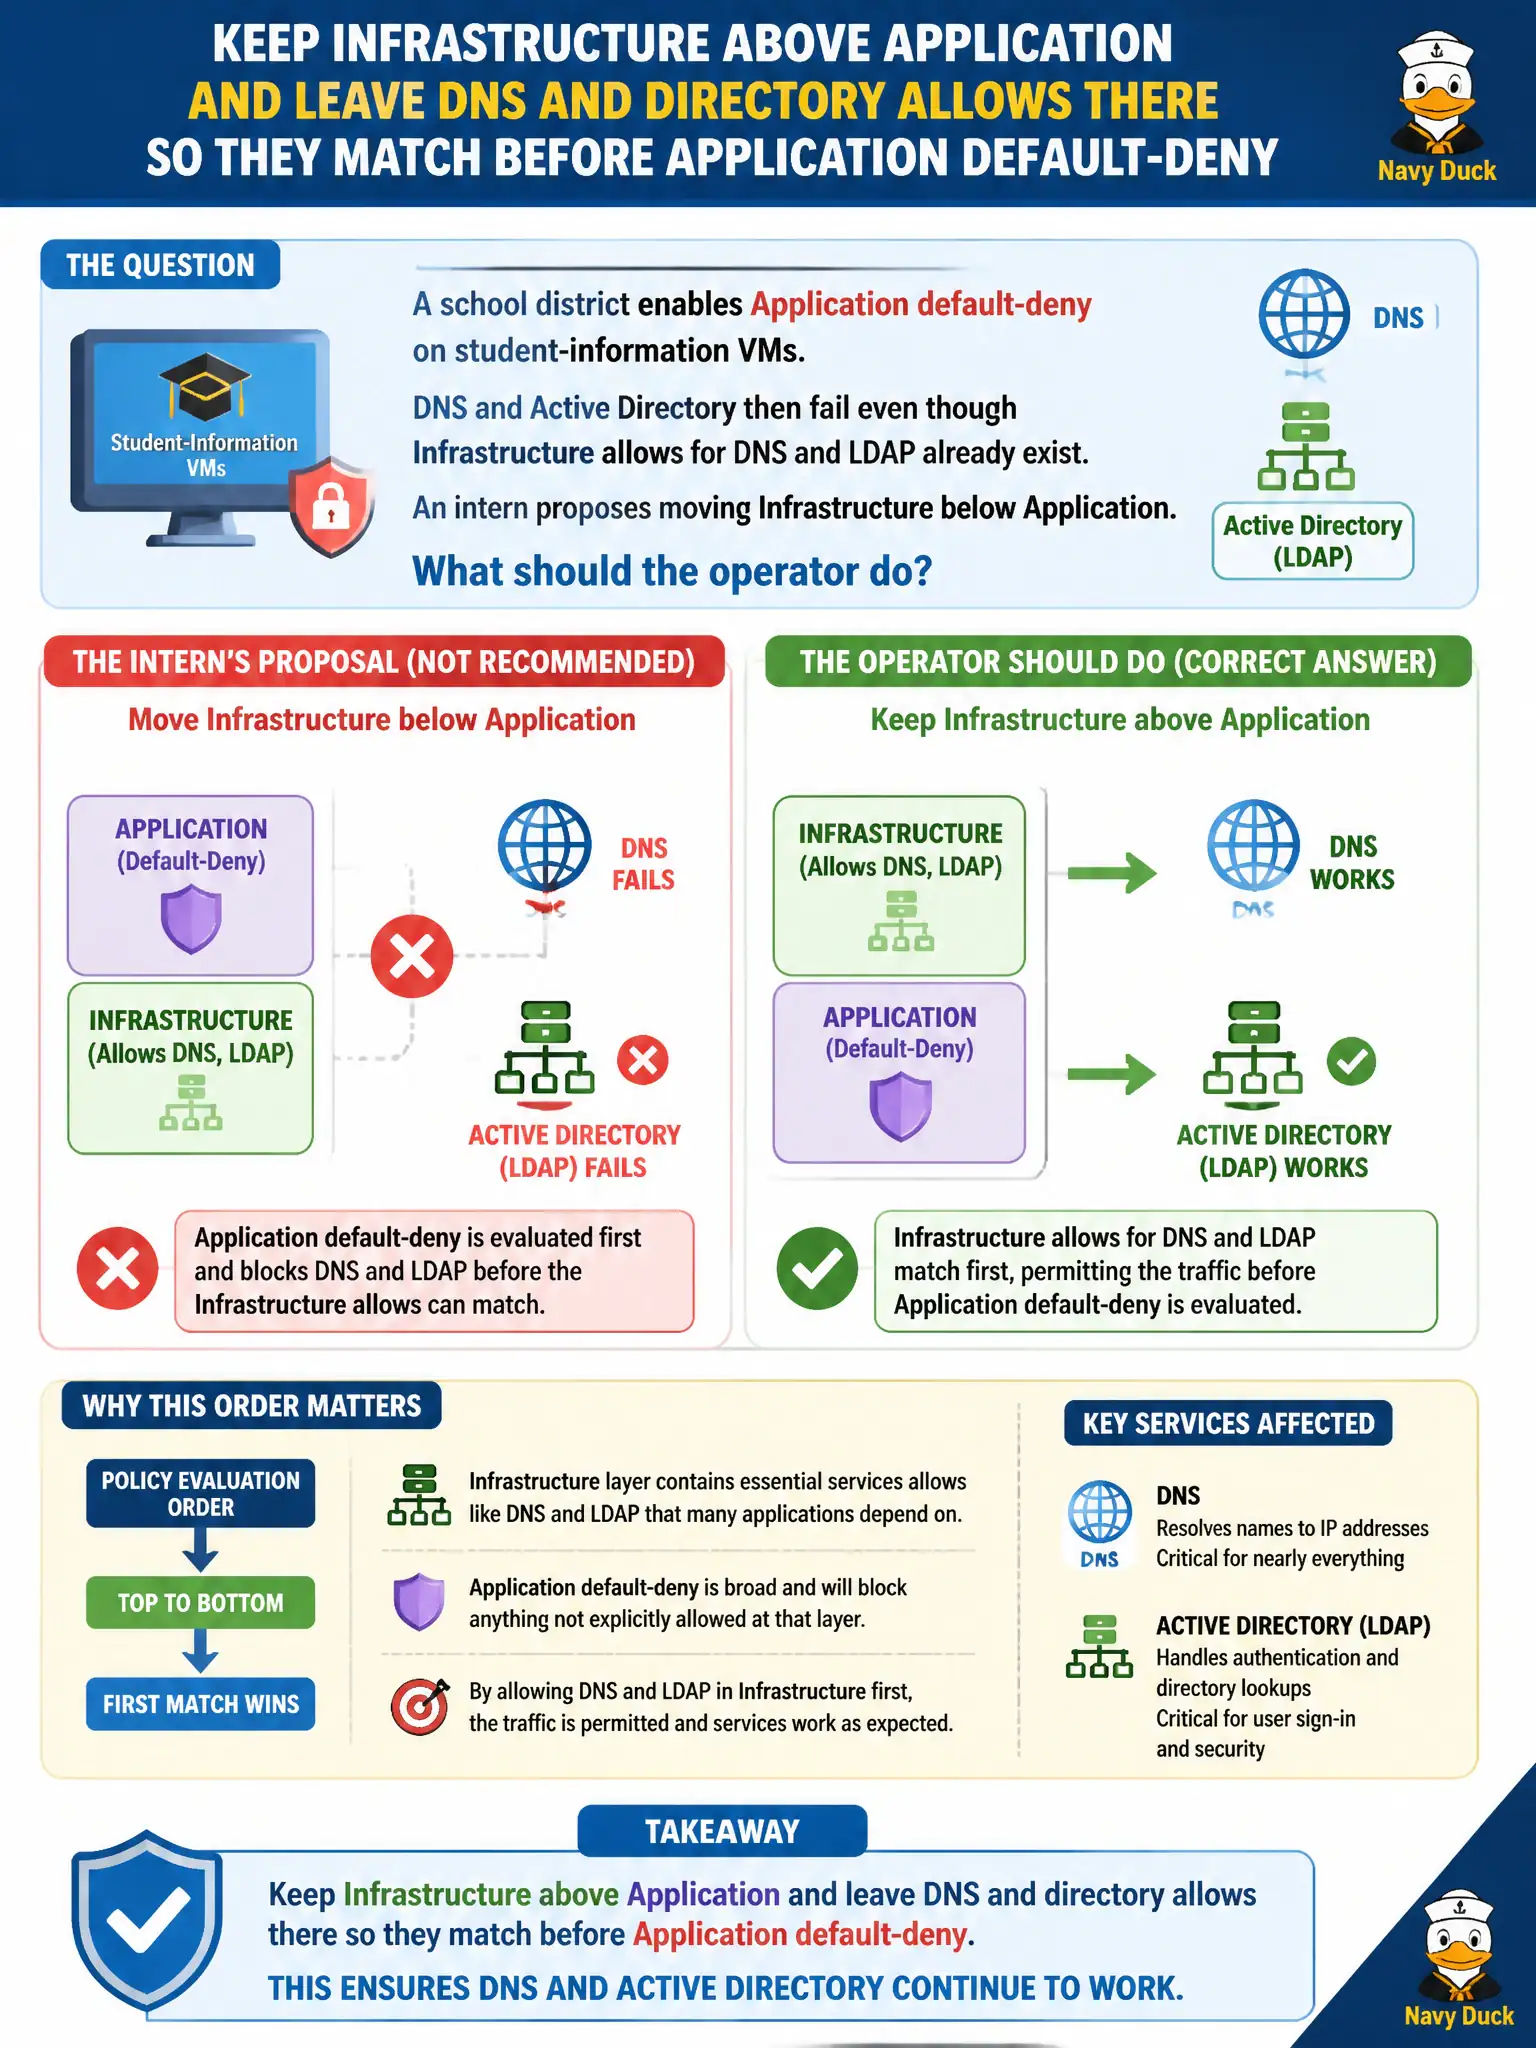
A school district enables Application default-deny on student-information VMs. DNS and Active Directory then fail even though Infrastructure allows for DNS and LDAP already exist. An intern proposes moving Infrastructure below Application. What should the operator do?
Select an answer to reveal the explanation.
Short Explanation
Think of Infrastructure as the hallway lights and Application as the classroom door. If you put the door in front of the lights, nobody can even find DNS. Leave Infrastructure above Application so name and directory traffic still work when app default-deny turns on.
Full Explanation
When a school district enables Application default-deny on student-information VMs and DNS and Active Directory fail even though Infrastructure allows for DNS and LDAP already exist, the operator must keep Infrastructure above Application and leave those DNS and directory allows there so they match before Application default-deny. Treat Infrastructure as the school utility closet (DNS, DHCP, NTP, directory) that must stay above classroom Application default-deny so name and directory services still work. Moving Infrastructure below Application so the student-information default-deny always wins fails by concept because NSX-T evaluates categories in a fixed order with Infrastructure above Application; reversing them breaks that model and still leaves DNS unmatched if allows sit below a default-deny. Converting DNS to Tier-0 static routes so Distributed Firewall categories no longer apply fails because routing does not replace Distributed Firewall service allows for DNS and LDAP. Disabling Guest Introspection on the school cluster to restore name resolution fails because Guest Introspection supports Identity Firewall and related services and is not the fix for category-order DNS failure. Exam caveat: keep DNS and directory allows in Infrastructure above Application default-deny; do not reorder categories, substitute T0 routes, or disable Guest Introspection to fix name resolution. Operational check: verify Infrastructure category order and DNS/LDAP allows, Traceflow from a student-information VM to DNS and domain controllers, confirm hits in Infrastructure before Application default-deny, and document category placement in the school DFW design.