
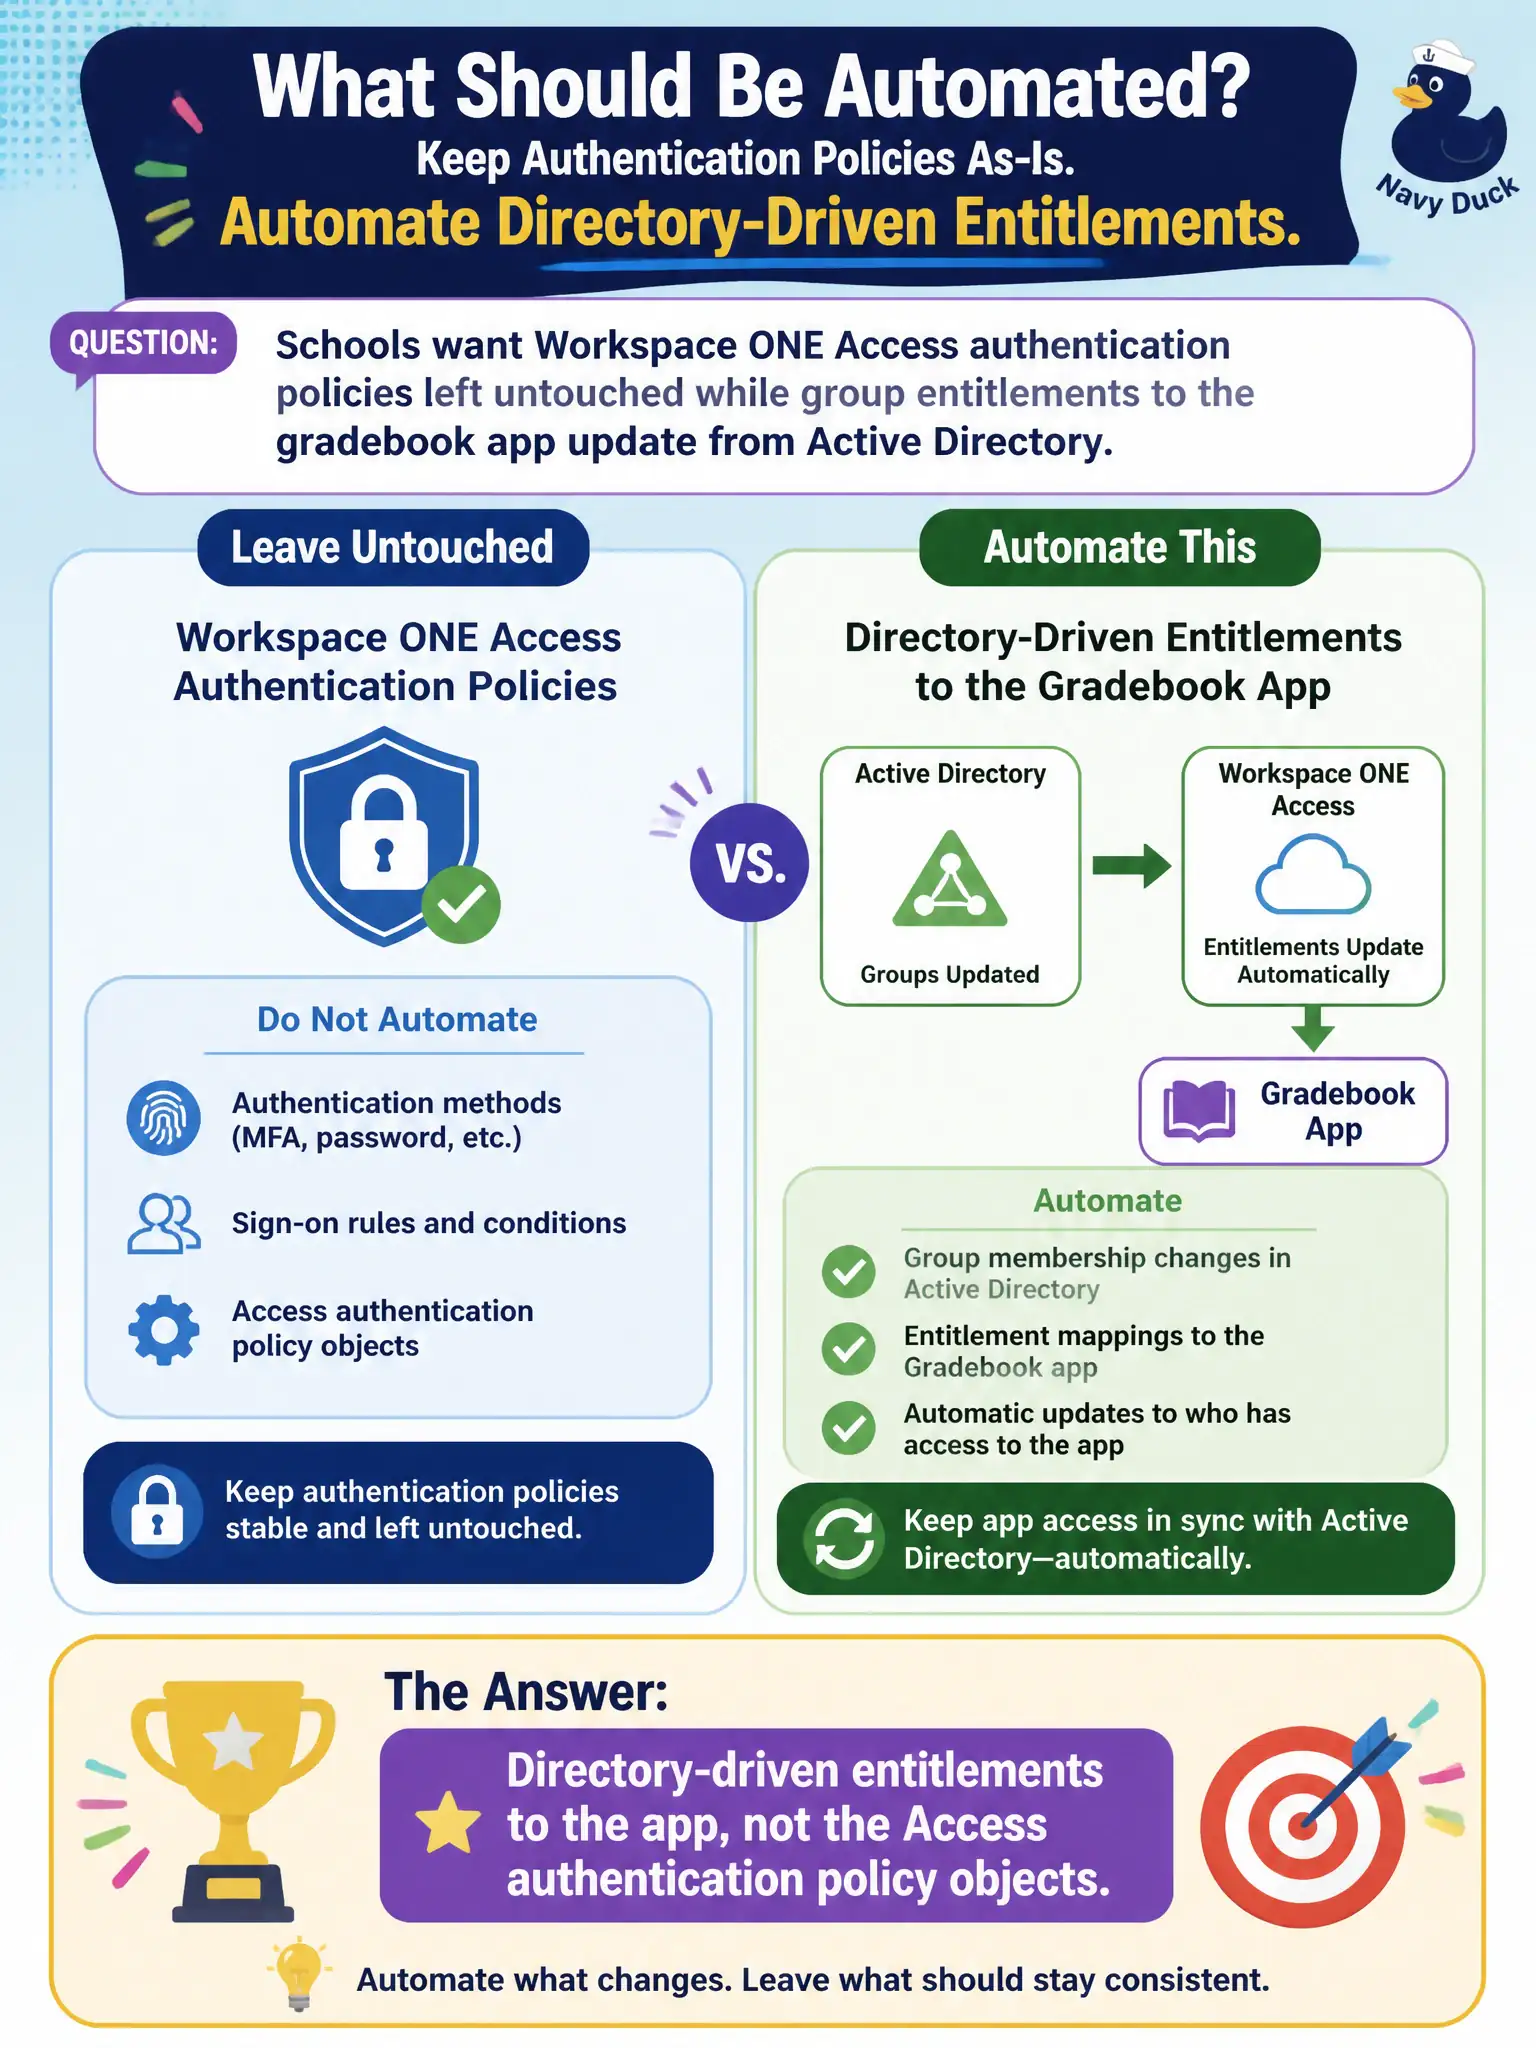
Schools want Workspace ONE Access authentication policies left untouched while group entitlements to the gradebook app update from Active Directory. What should be automated?
Select an answer to reveal the explanation.
Short Explanation
Entitlements are who gets a key to the gradebook; Access policies are the lock on the front door. Automate the key roster from Active Directory and leave the lock policy alone.
Full Explanation
Schools should automate directory-driven entitlements to the gradebook app while leaving Workspace ONE Access authentication policy objects untouched. Treat Access authentication policies as the schoolhouse front-door locks (MFA, network ranges, device posture) and entitlements as the class roster for who may open the gradebook: AD group membership can update the roster without rewriting the locks. Automating the Access policy rules that set MFA for all identity providers fails by concept because that changes authentication behavior for every app and IdP path, which is exactly what the schools asked to leave alone. Changing the NSX-T Gateway Firewall default action fails because gateway default action is an overlay north-south control, not Access entitlement automation. Changing the Carbon Black Cloud sensor version fails because sensor versioning is endpoint-agent lifecycle, not gradebook app entitlement from Active Directory. Exam caveat: Access separates authentication policies from entitlements; automate directory-driven entitlements when the requirement is group membership to an app without touching MFA or IdP policy objects. Operational check: change an AD group for gradebook access, confirm Access entitlement updates without diffs on authentication policy objects, verify MFA and network-range rules remain unchanged, and document the entitlement sync in the school identity runbook.