
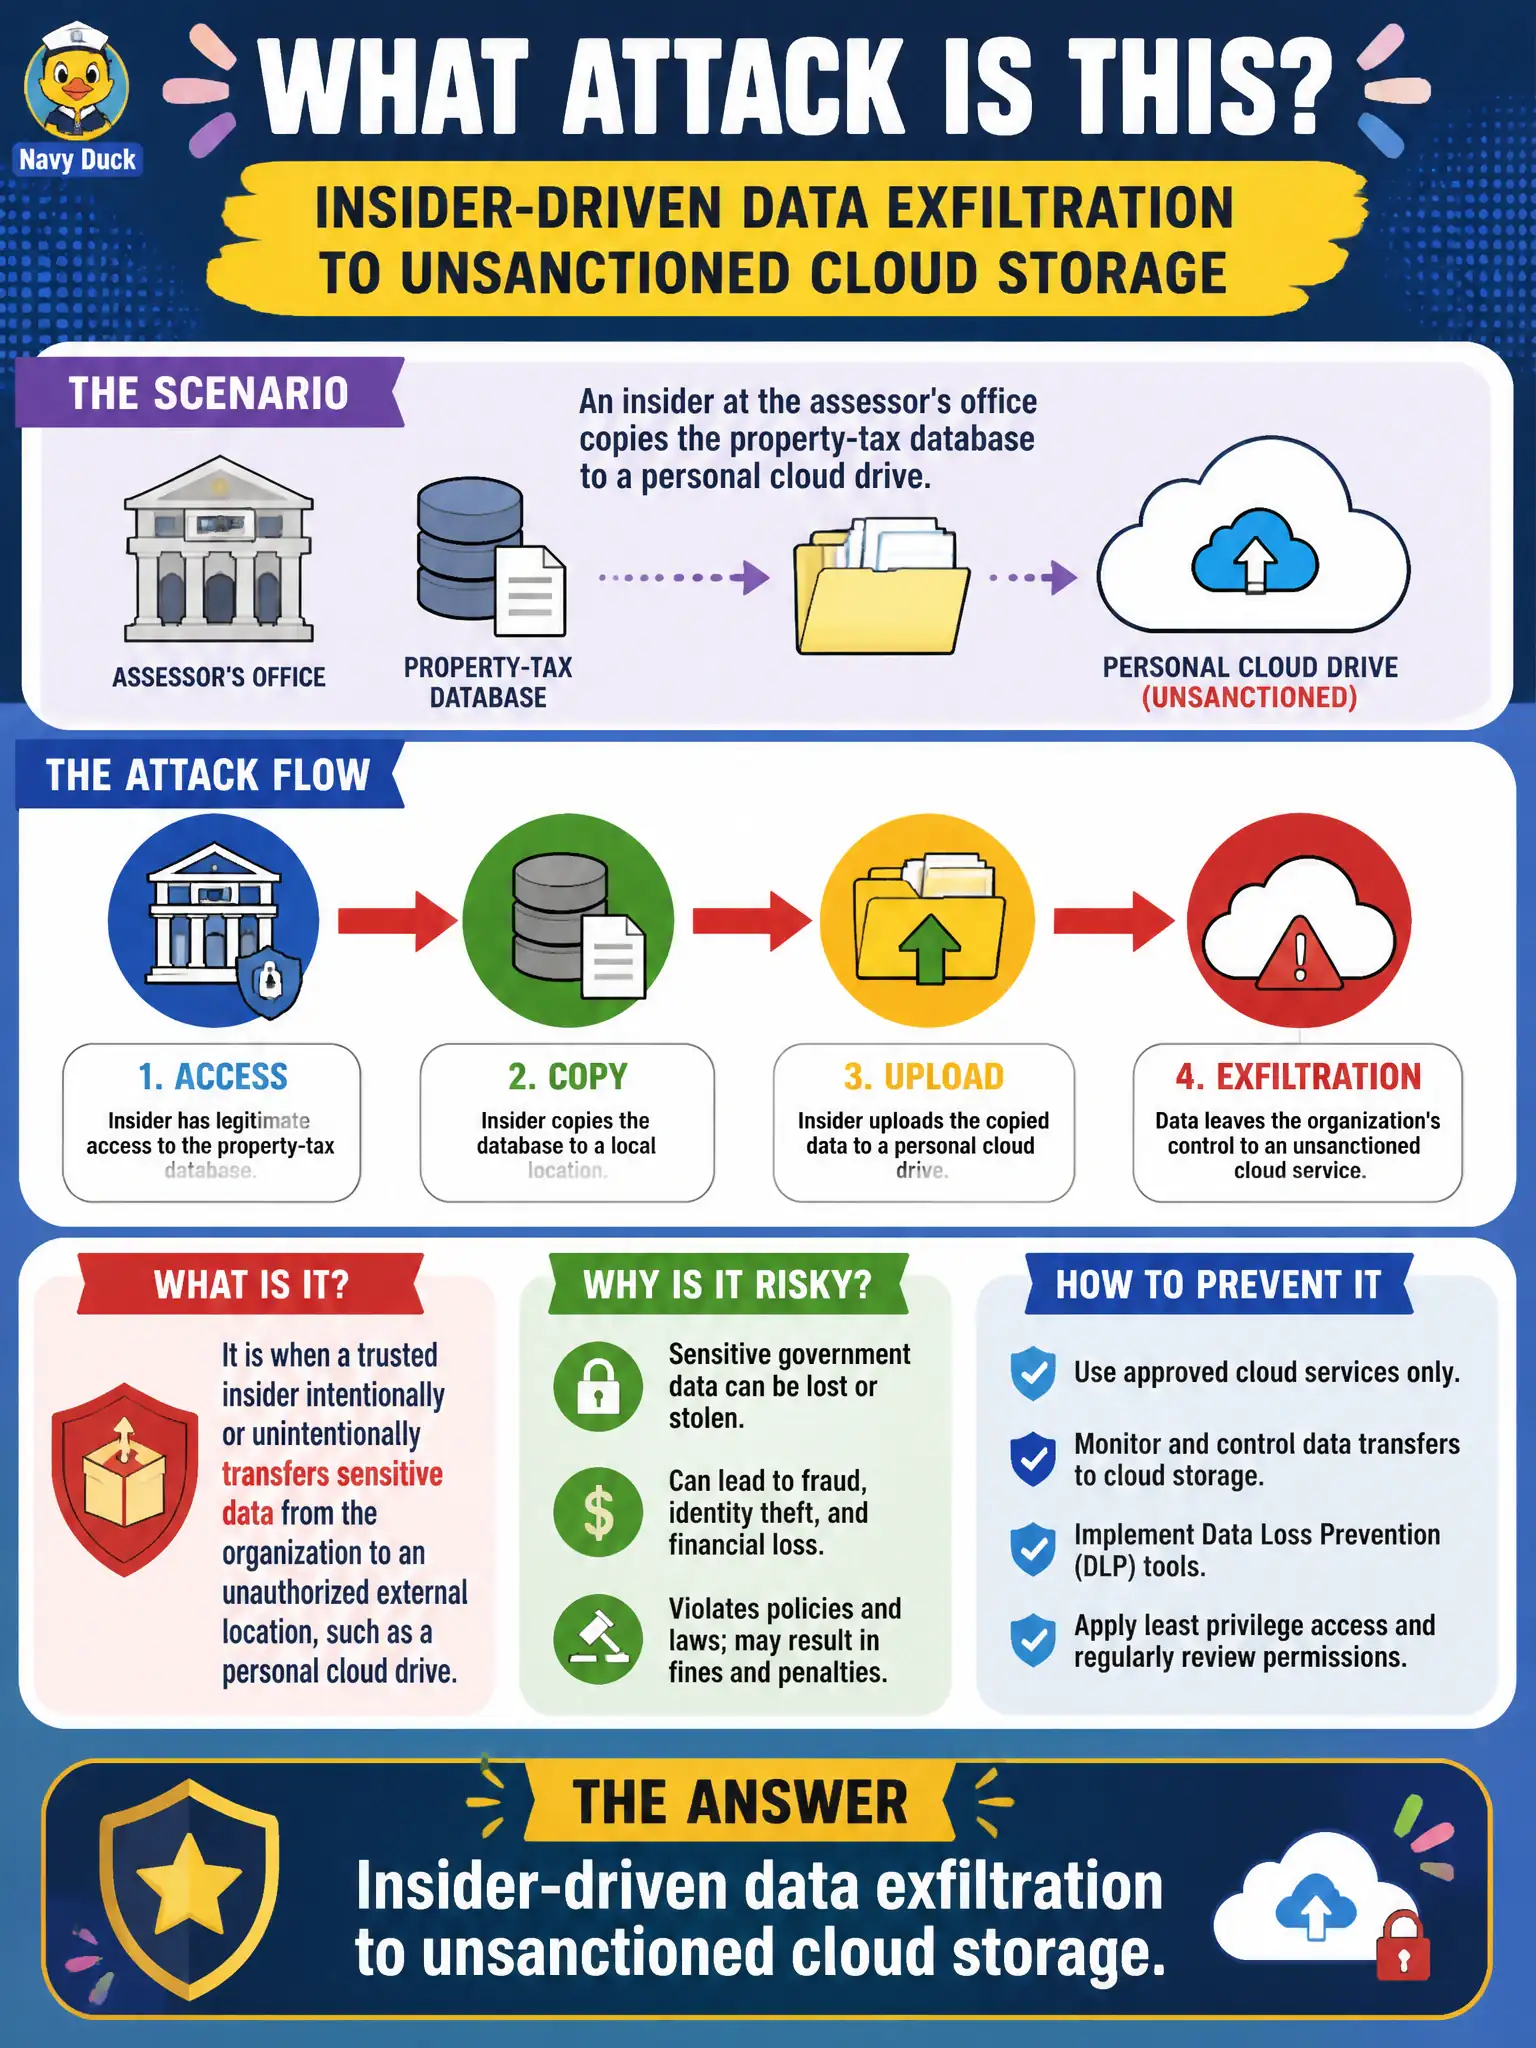
An insider at the assessor's office copies the property-tax database to a personal cloud drive. What attack type is this?
Select an answer to reveal the explanation.
Short Explanation
A trusted assessor account just trucked the tax roll to a personal cloud locker. That is insider exfiltration, not encryption and not a website flood. The data left; it was not locked for ransom.
Full Explanation
An insider at the assessor's office copying the property-tax database to a personal cloud drive is insider-driven data exfiltration to unsanctioned cloud storage. A trusted assessor account trucked the tax roll to a personal locker; the data left the civic boundary without authorization. County privacy, appraisal integrity, and resident trust all hinge on naming that outbound copy as exfiltration rather than calling every large file event ransomware or a website flood.
Calling it ransomware encrypting the assessor file share fails by concept: copying data out to personal cloud storage is not encryption-for-extortion on the share. Calling it a SYN-flood DDoS against the assessor website fails by concept: website floods are unrelated to a database copy-out performed by an insider account. Calling it a watering-hole on the parks events page fails by concept: no trusted-site malware delivery is involved in this insider path.
Exam caveat: Trusted user plus unauthorized copy to personal cloud equals insider-driven data exfiltration.
Operational check: Disable or restrict the account, preserve cloud and file-share audit logs in Enterprise Security, notify appropriate legal and privacy officers for tax-roll exposure, and tune detections for large after-hours uploads to unsanctioned destinations.