
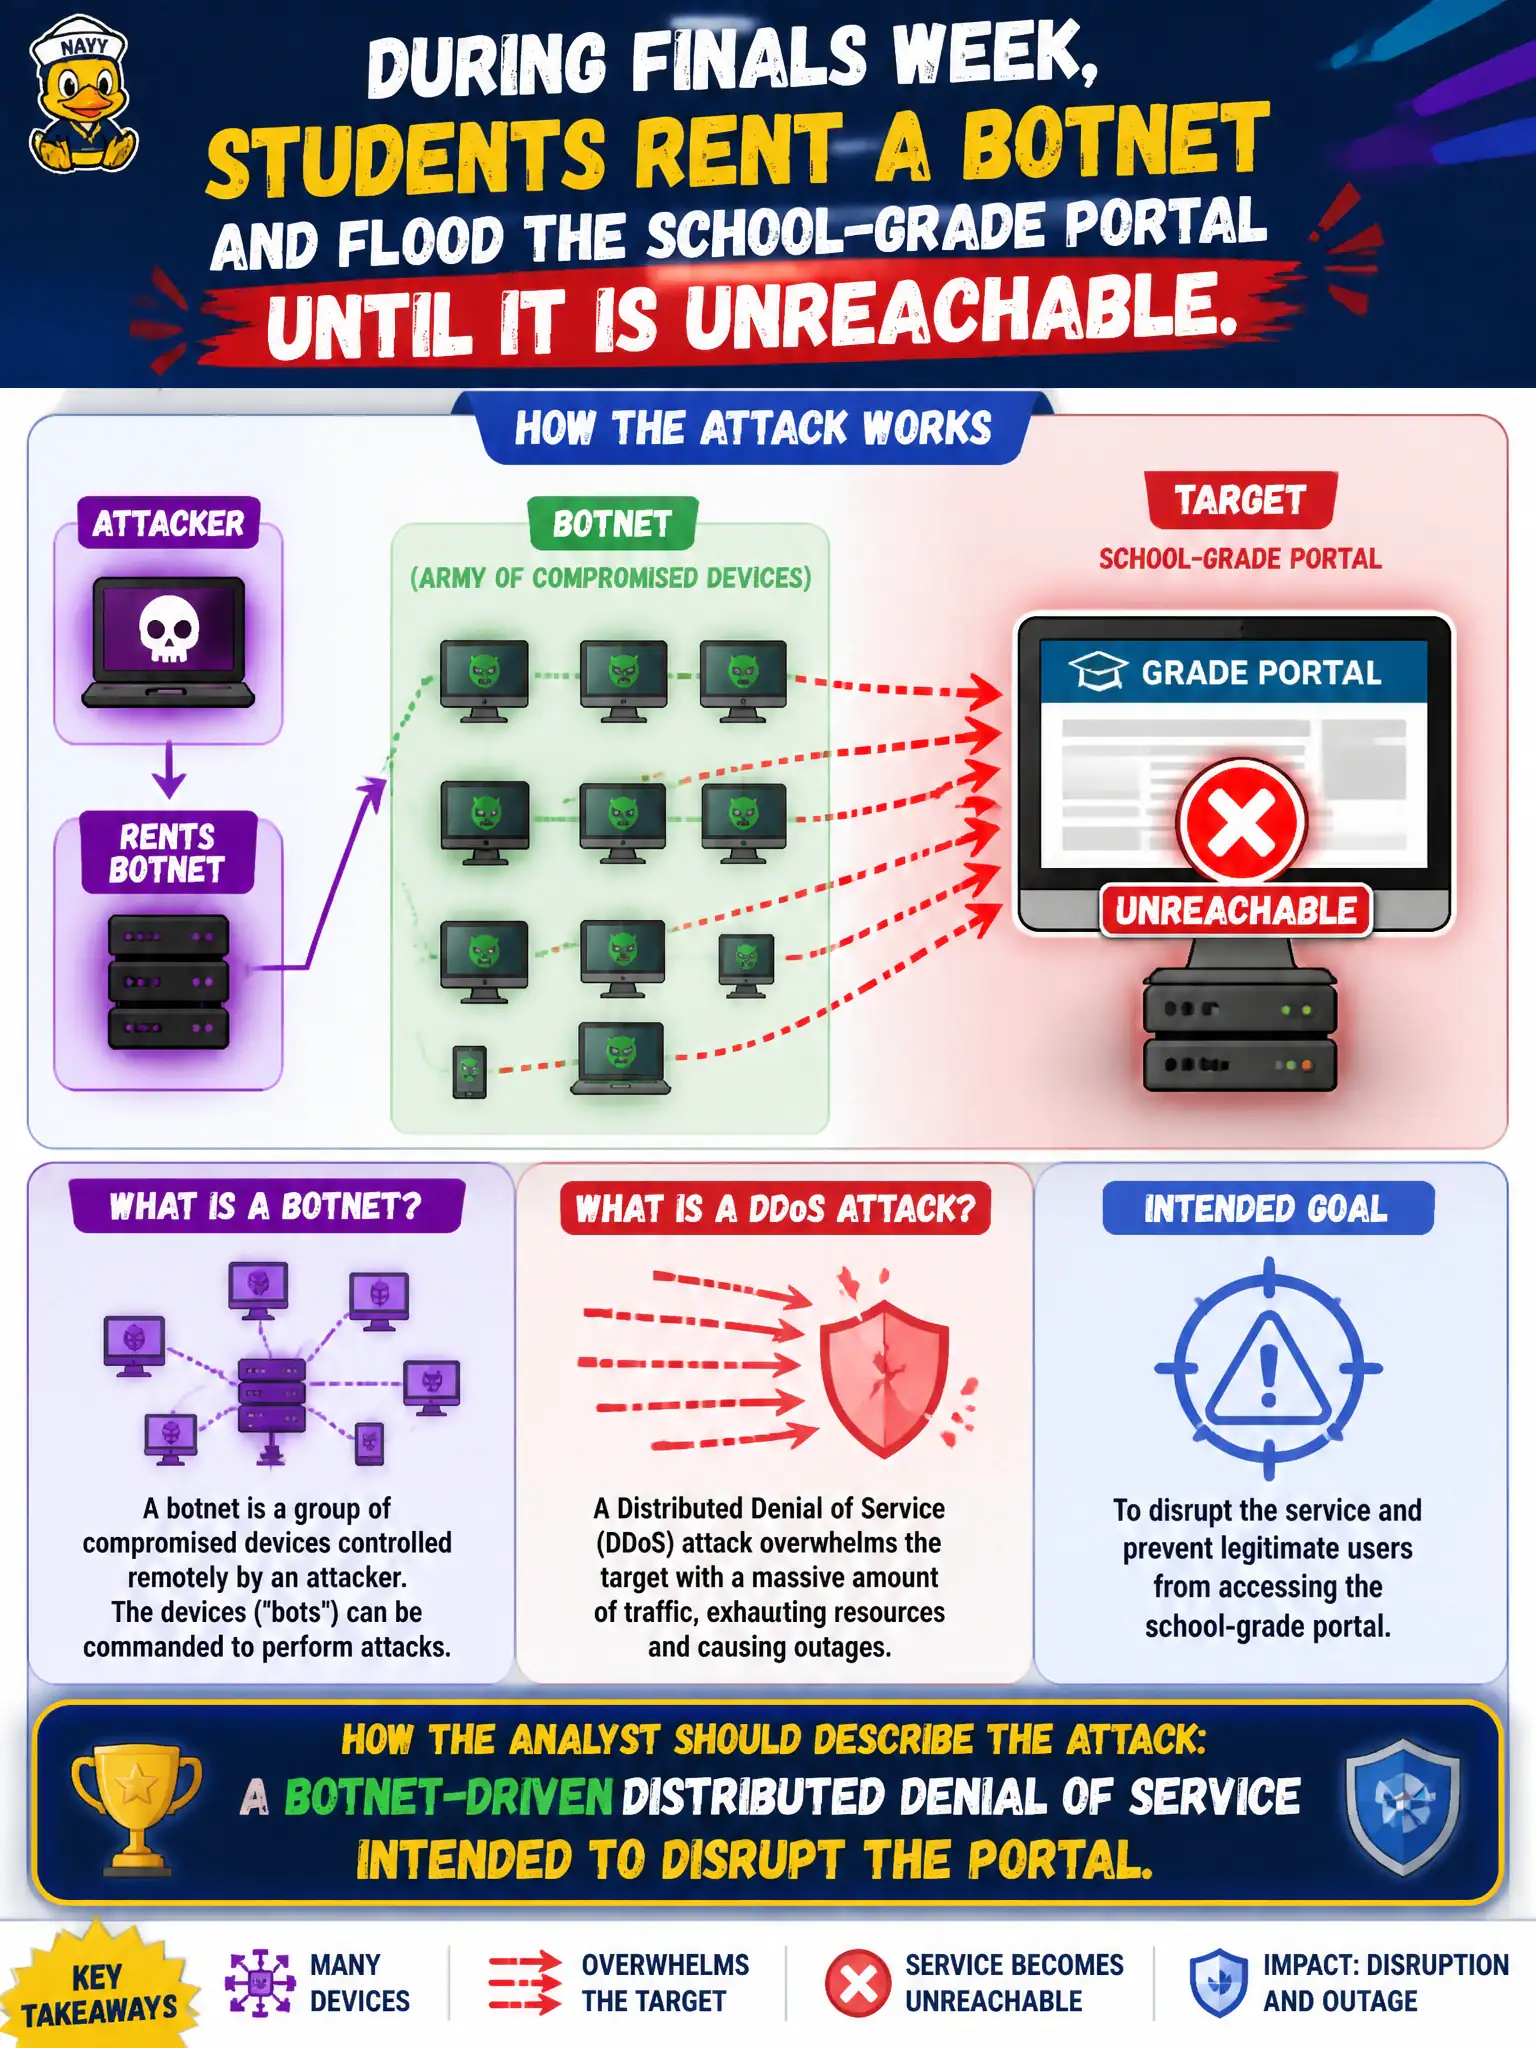
During finals week, students rent a botnet and flood the school-grade portal until it is unreachable. How should the analyst describe the attack?
Select an answer to reveal the explanation.
Short Explanation
Finals week, a rented botnet, and a grade portal that will not load—that is disruption for hire, not a stolen mailbox. The fleet of bots is the DDoS engine. Motivation is knocking the civic site down, not stealing the database.
Full Explanation
During finals week, students renting a botnet to flood the school-grade portal until it is unreachable is a botnet-driven distributed denial of service intended to disrupt the portal. Motivation and mechanism align: a rented bot fleet knocks down a civic education service for disruption during a high-stakes academic window. The correct description emphasizes DDoS via botnet so responders engage scrubbing, ISP help, and portal resilience rather than opening the wrong case type for theft or mailbox compromise.
Calling it insider exfiltration of the grade database fails by concept: the effect described is unreachability of the portal, not unauthorized copying of grade data. Calling it a supply-chain compromise of the grade-portal software publisher fails by concept: no trusted update abuse or trojanized installer is described. Calling it account takeover of a single counselor mailbox fails by concept: compromise of one mailbox does not explain a portal-wide flood that makes the site unreachable.
Exam caveat: Rented botnet plus flood plus unreachable civic site equals botnet-driven DDoS intended to disrupt service.
Operational check: Engage DDoS protections, preserve netflow and portal logs in Splunk, coordinate with school leadership on academic continuity messaging, and avoid opening exfiltration cases without evidence of data leaving.