
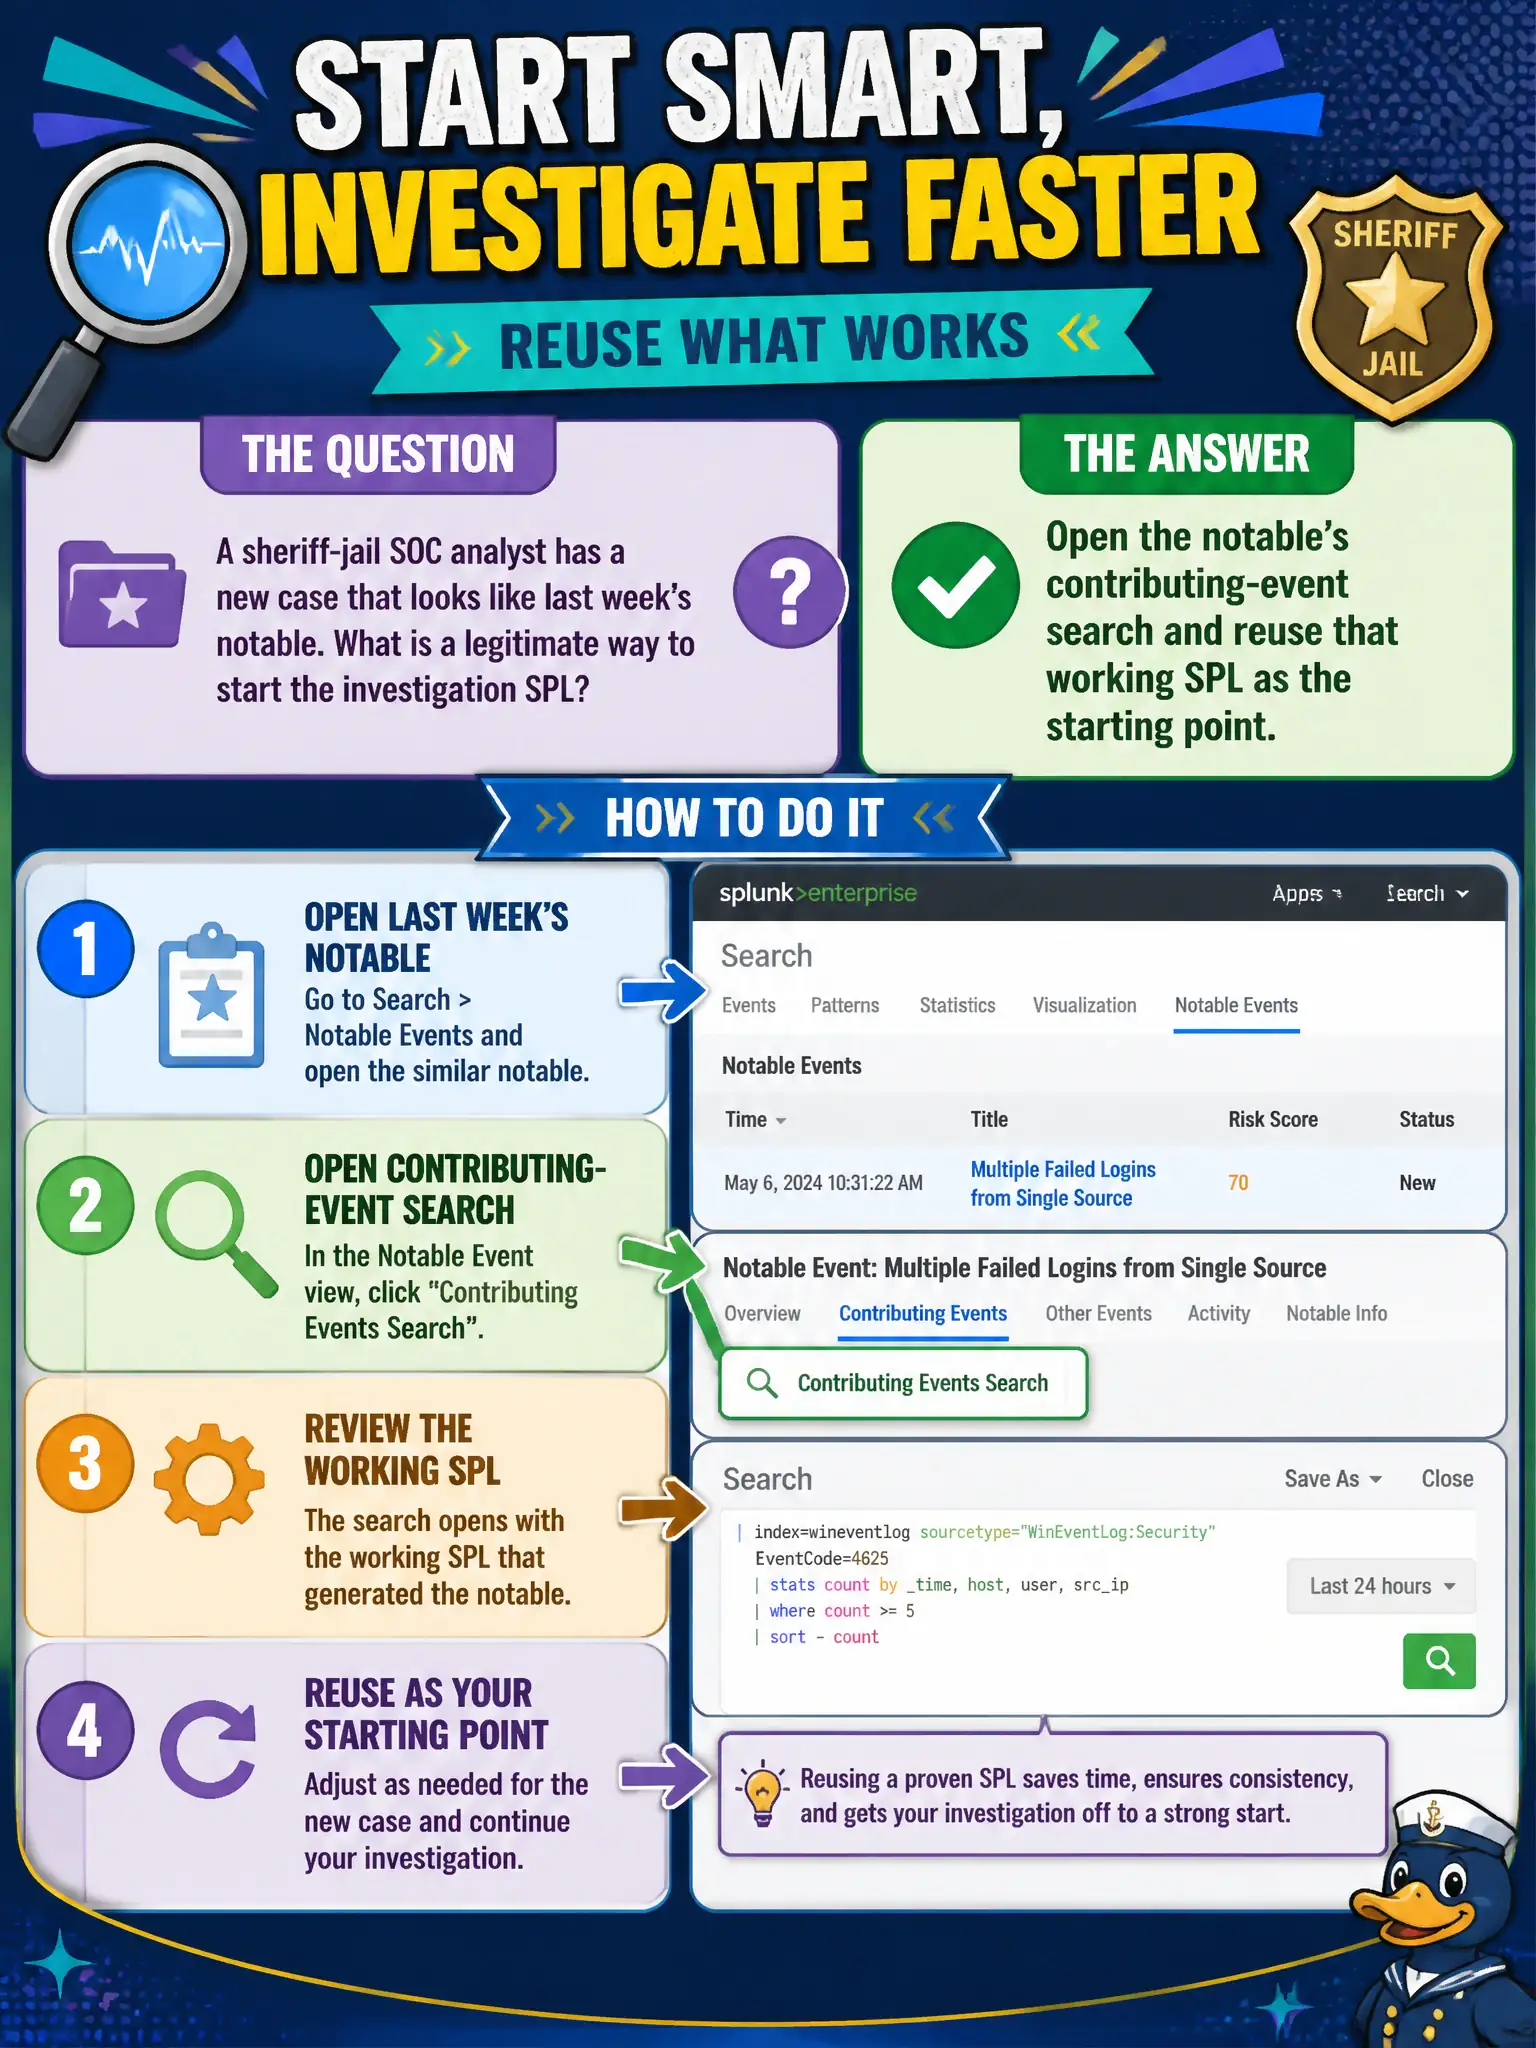
A sheriff-jail SOC analyst has a new case that looks like last week's notable. What is a legitimate way to start the investigation SPL?
Select an answer to reveal the explanation.
Short Explanation
Last week's notable already ran a search that found the contributing events. Open that search and reuse it; that is stealing in the good way. Rewriting CIM or dumping to Excel just throws away working jail-SOC SPL.
Full Explanation
When a new sheriff-jail case resembles last week's notable, a legitimate start is to open that notable's contributing-event search and reuse the working SPL as the investigation seed. Contributing-event SPL already scopes the evidence Enterprise Security used; adapting it is faster and safer than inventing a fresh query under pressure. Rewriting the CIM Authentication model from scratch is engineer-scale work and unrelated to starting one case. Exporting raw contributing events to Excel to rebuild the search abandons SPL and the ES investigation trail. Disabling the original correlation search to prevent copying destroys detection coverage and is not how reuse works. Exam caveat: reuse the search logic, then adjust time, identity, and host scope for the new case—do not blindly replay another inmate population's window without retargeting. Operational check: from last week's notable, open contributing events, copy the search, retarget to the new case entities and time, and confirm the adapted SPL surfaces the expected jail-SOC evidence before expanding scope. Document the revised approach in the civic SOC runbook so the next on-call analyst inherits the correct pattern rather than the anti-pattern. Retain Job Inspector evidence with the change ticket for municipal audit readiness.