
A new courts-SOC analyst thinks reusable security SPL exists only in the Search app. Where else in Enterprise Security should they look?
Select an answer to reveal the explanation.
Short Explanation
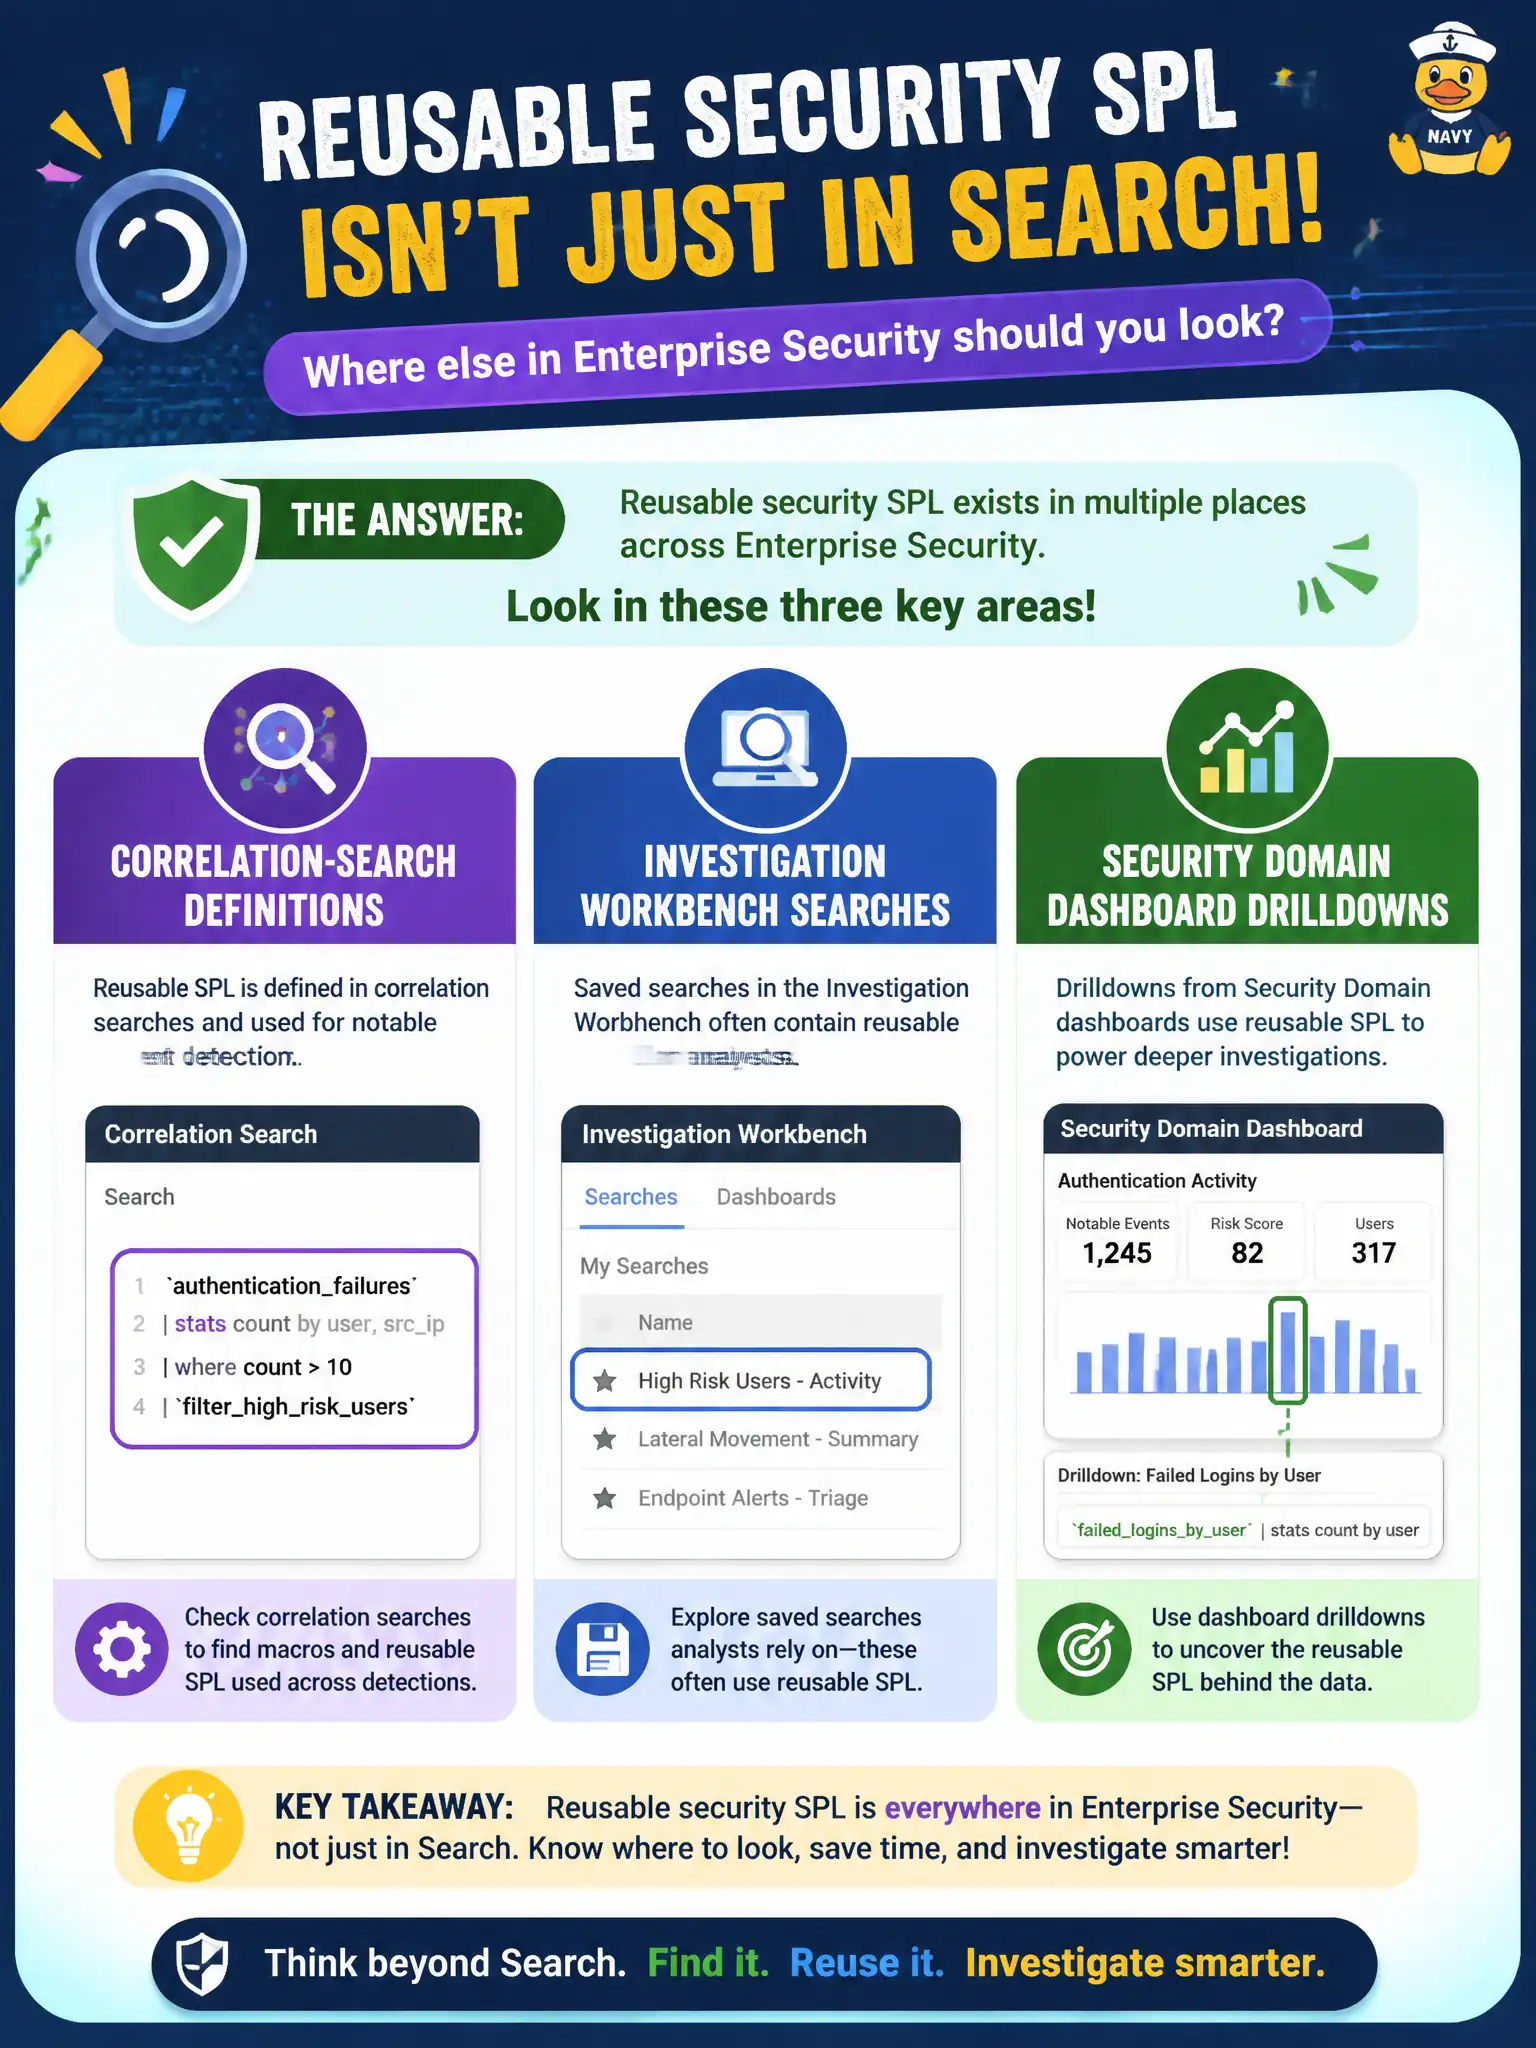
The Search app is not the only drawer of working security SPL. ES itself ships correlation-search definitions, investigation workbench searches, and Security Domain drilldowns. Clustering, license, and KV Store screens are admin furniture, not the analyst's SPL library.
Full Explanation
Reusable security SPL in Enterprise Security is not limited to the Search app. Courts-SOC analysts should also open correlation-search definitions, investigation workbench searches, and Security Domain dashboard drilldowns—those are first-class SPL resources for defending civic workloads. Indexer clustering dashboards store cluster health views, not the canonical library of CIM investigation searches. The license-master usage report is billing and capacity telemetry, not an SPL catalog. KV Store admin pages are not where analysts retrieve the macros and searches used during investigations. Exam caveat: permissions may hide some correlation-search definitions from junior roles; know which ES objects your role can open without assuming Search app is the only drawer. Operational check: for a recent courts notable type, open the correlation search, a related workbench search, and a Security Domain drilldown, save those SPL snippets to the team library, and show new analysts those three ES locations on day one. Document the revised approach in the civic SOC runbook so the next on-call analyst inherits the correct pattern rather than the anti-pattern. Retain Job Inspector evidence with the change ticket for municipal audit readiness.