
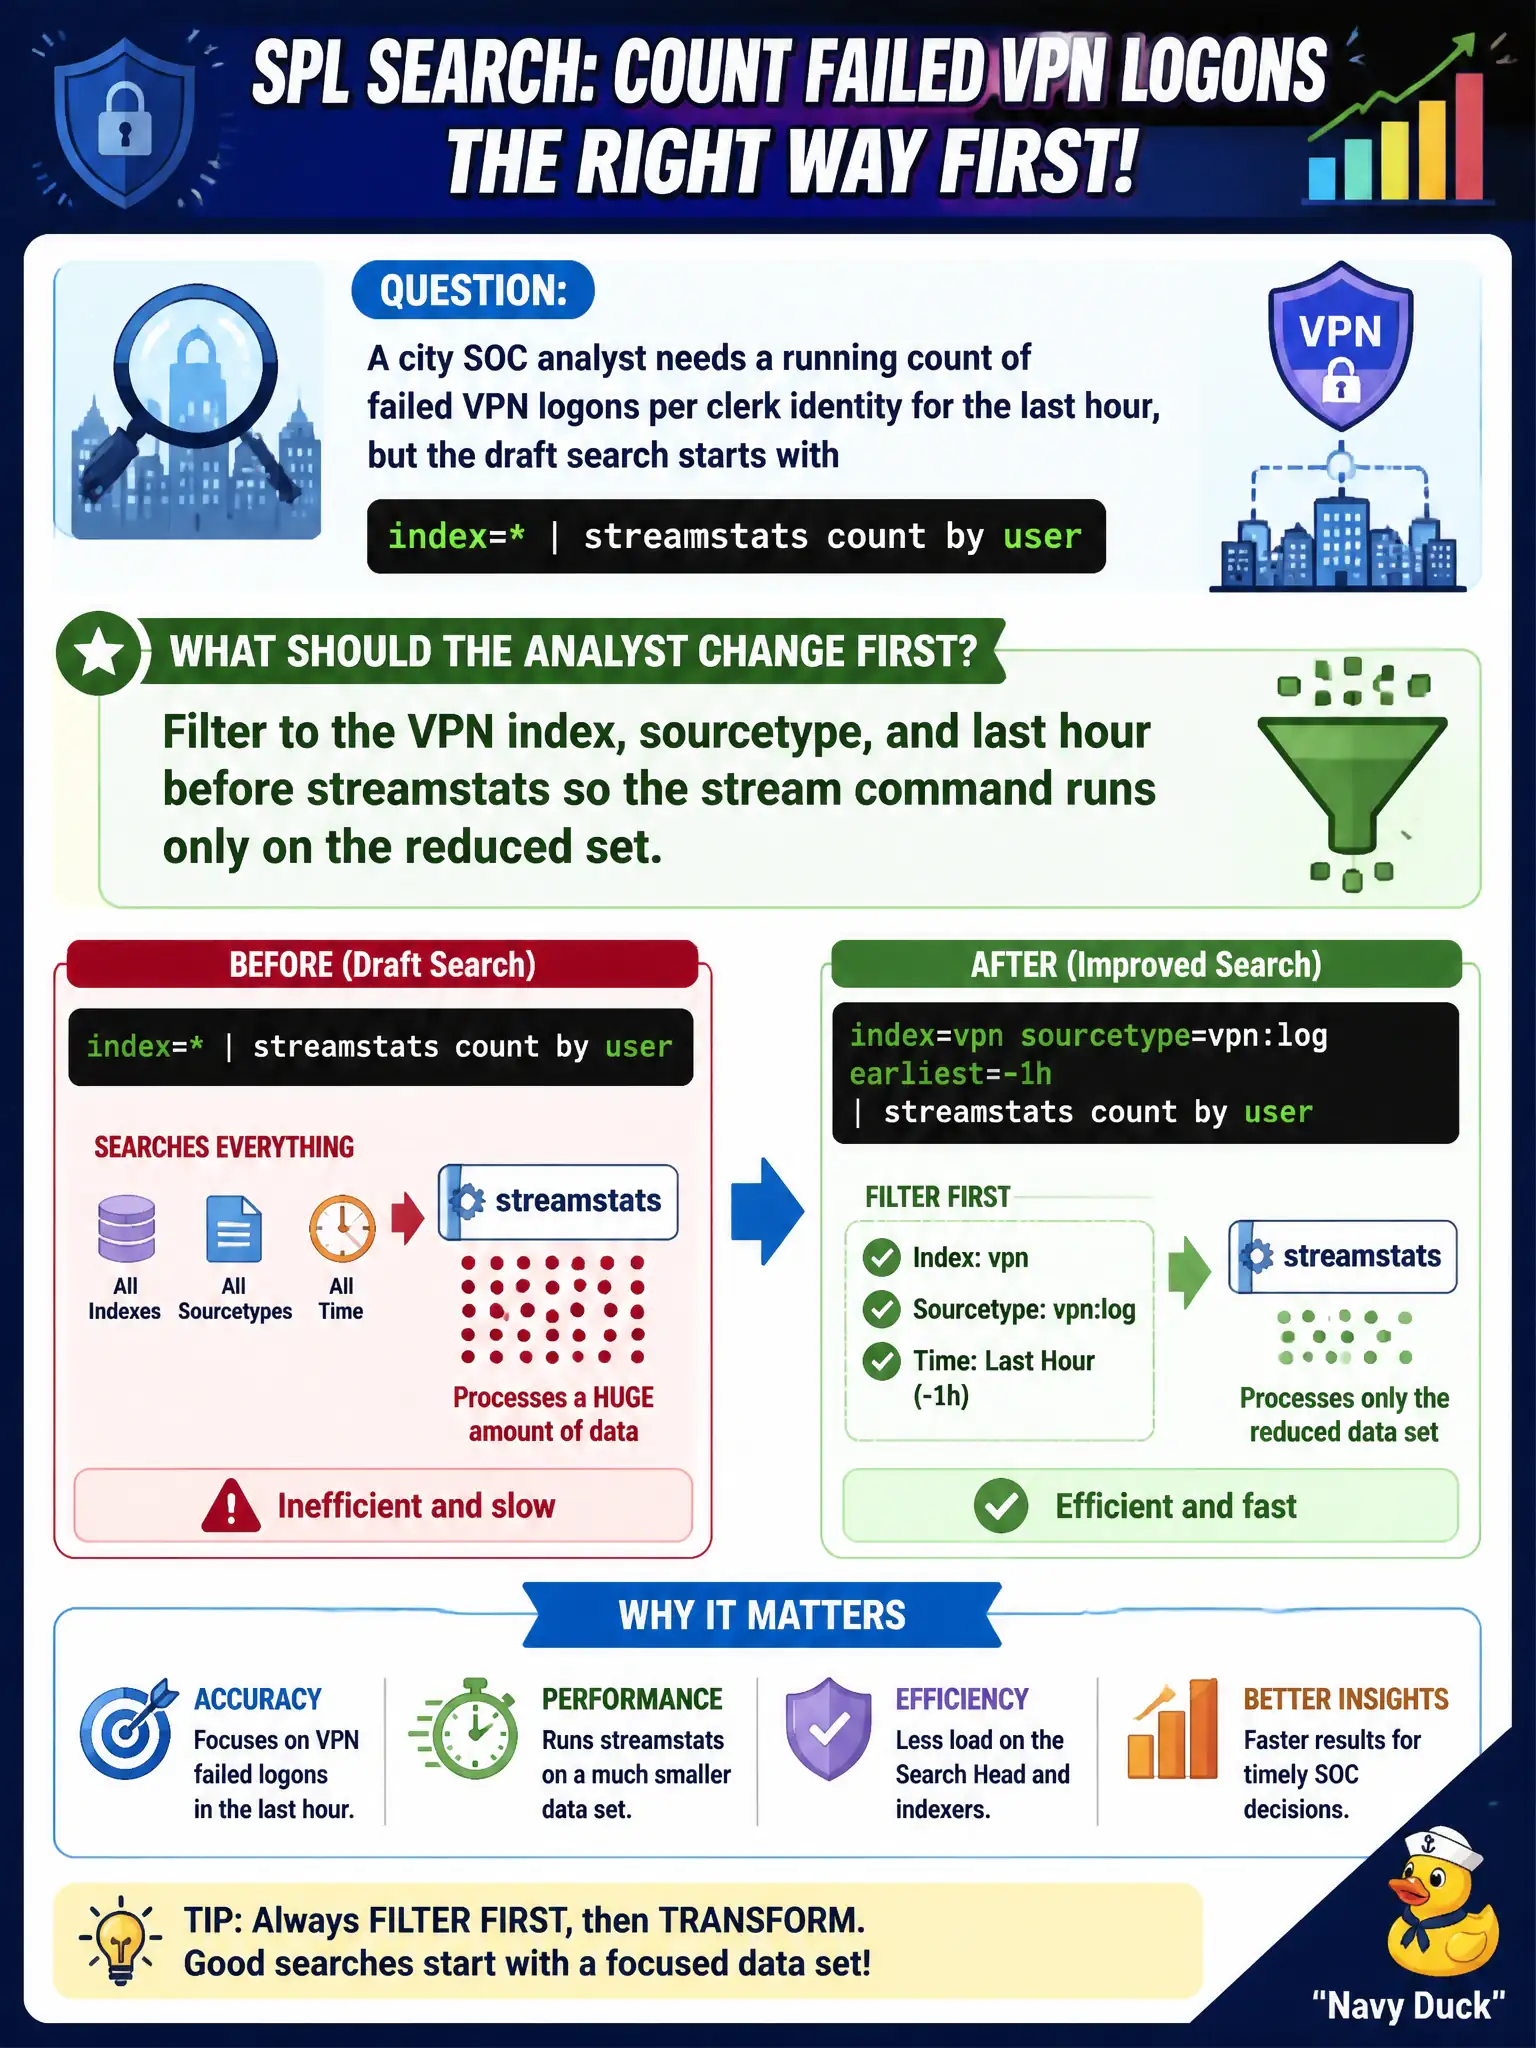
A city SOC analyst needs a running count of failed VPN logons per clerk identity for the last hour, but the draft search starts with index=* | streamstats count by user. What should the analyst change first?
Select an answer to reveal the explanation.
Short Explanation
streamstats is a lawn mower: useful on a small yard, brutal if you run it across the whole city park. Filter the VPN index, sourcetype, and hour first, then stream. eventstats on index=* is the same expensive mistake with a different name.
Full Explanation
streamstats and similar expensive streaming transforms should run only after the event set is reduced. A city SOC draft that starts with index= | streamstats count by user forces the stream command across every municipal index before any VPN selectivity exists. The correct first change is to filter to the VPN index, sourcetype, and last-hour window so streamstats computes the running failed-logon count only on the reduced clerk set. Adding transaction on the unfiltered index= search makes the problem heavier. Swapping to eventstats on the same index= base still scans everything and only changes how the total is calculated. Moving streamstats into a subsearch that scans every index repeats the anti-pattern behind another layer. Exam caveat: streamstats is appropriate for running counts once time, index, and sourcetype are constrained—not as the first command on an unbounded civic search. Operational check: rewrite the VPN failed-logon hunt with index/sourcetype/last-hour filters before streamstats, confirm the running per-user counts still answer the question, and compare scanned events to the index= version in Job Inspector. Document the revised approach in the civic SOC runbook so the next on-call analyst inherits the correct pattern rather than the anti-pattern. Retain Job Inspector evidence with the change ticket for municipal audit readiness.