
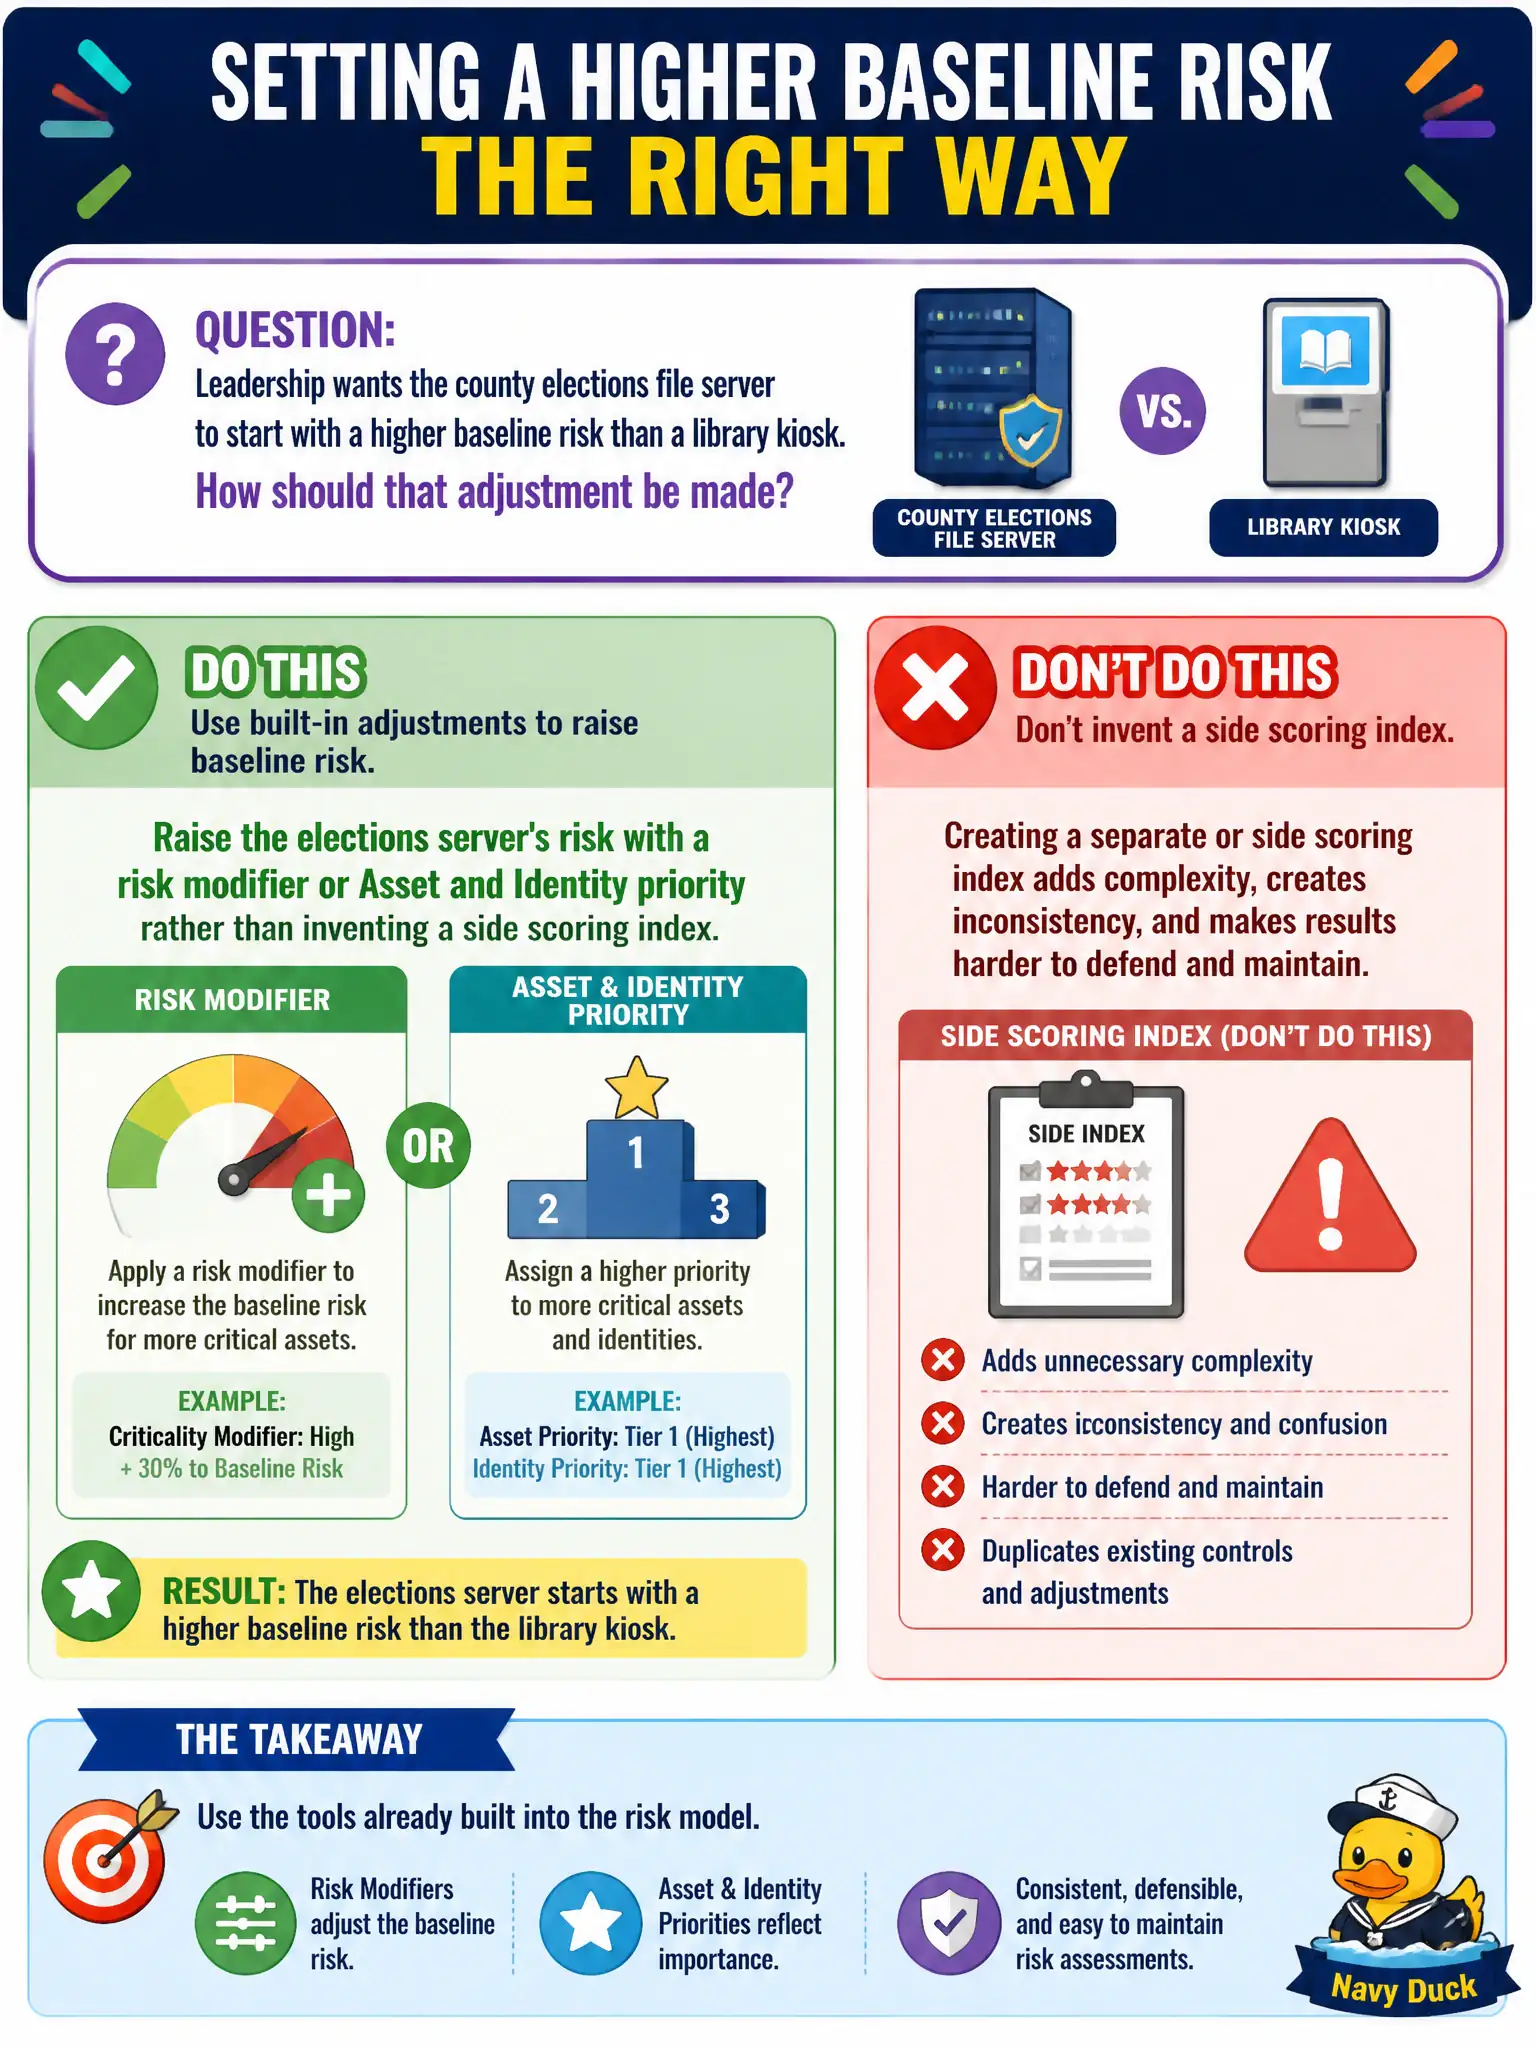
Leadership wants the county elections file server to start with a higher baseline risk than a library kiosk. How should that adjustment be made?
Select an answer to reveal the explanation.
Short Explanation
The elections server is a vault; the kiosk is a brochure rack. Raise the vault's baseline with a risk modifier or Asset and Identity priority. Do not invent a second scoreboard in a leftover index.
Full Explanation
In Splunk Enterprise Security for a municipal SOC, baseline risk for high-impact entities is adjusted with risk modifiers and with Asset and Identity attributes such as priority, so aggregation and risk notables remain inside one RBA framework. Raising the county elections file server’s baseline relative to a library kiosk belongs in that framework: a risk modifier or higher asset priority increases how quickly contributing events produce a leadership-visible notable without inventing a parallel score. Creating a new raw index named elections_risk and copying syslog there for a separate score fails by concept because a side index is not the ES risk index and will not drive risk notables. Doubling the license quota on the elections index so risk mathematically increases fails by concept because license volume is unrelated to risk scoring. Renaming the correlation search to include elections so Enterprise Security treats every match as critical fails by concept because search names are not risk modifiers or asset priority. Exam caveat: SPLK-5001 expects analysts to request Asset and Identity or risk-modifier changes for civic criticality, not side indexes, license tricks, or search-name cosmetics. Operational check: set or request a risk modifier / higher priority on the elections file server asset, generate comparable contributing events against the elections server and a library kiosk, and confirm the elections object accumulates actionable risk faster while both still use the same risk index and notable path.