
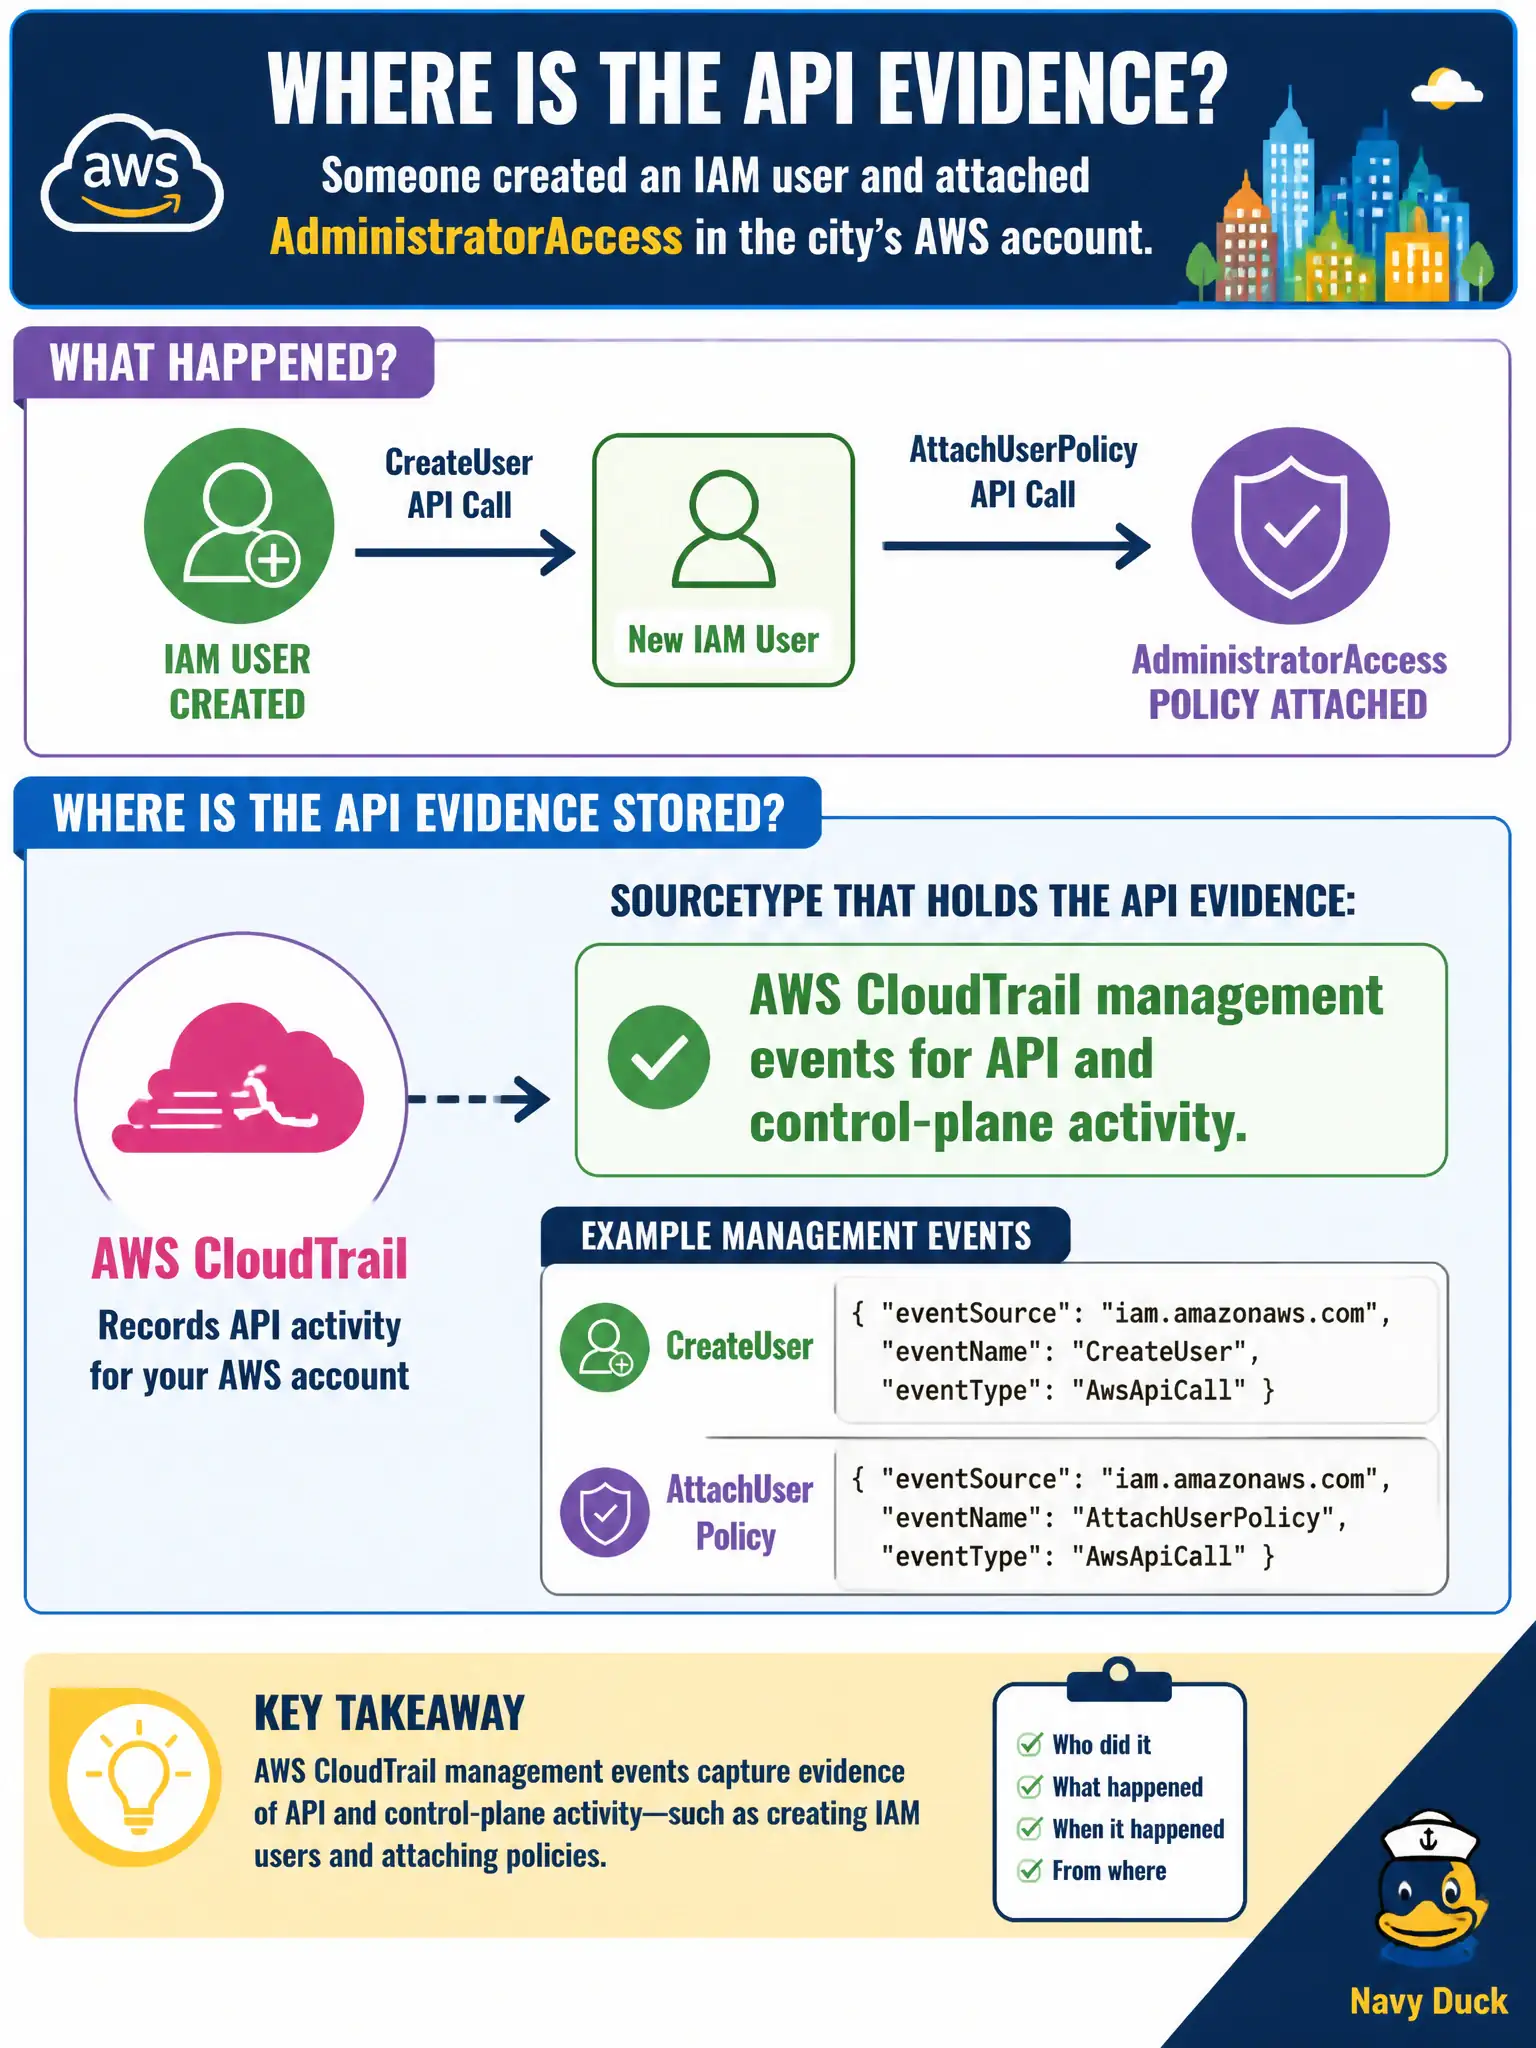
Someone created an IAM user and attached AdministratorAccess in the city's AWS account. Which sourcetype holds that API evidence?
Select an answer to reveal the explanation.
Short Explanation
Creating an IAM admin is an API call, and CloudTrail is the AWS API diary. VPC flow sees packets, not AttachUserPolicy. GuardDuty may later shout, but the authoritative who-did-what is CloudTrail.
Full Explanation
Someone creating an IAM user and attaching AdministratorAccess in the city's AWS account leaves evidence in AWS CloudTrail management events for API and control-plane activity. CloudTrail records CreateUser, AttachUserPolicy, and related calls with principal, time, source IP, and request parameters—the authoritative municipal audit trail for that privilege-escalation path in the cloud account.
VPC Flow Logs record network five-tuples, not IAM AttachUserPolicy API semantics, so they cannot hold that control-plane evidence no matter how carefully they are searched. Claiming GuardDuty only and that CloudTrail never logs IAM changes is false—CloudTrail is the primary IAM API log; GuardDuty may alert but does not replace CloudTrail history. On-premises WinEventLog:Security from a library PC that is not in AWS cannot record AWS IAM mutations.
Exam caveat: AWS IAM and control-plane changes map to CloudTrail management events, not VPC Flow, GuardDuty-only, or Windows logs.
Operational check: query CloudTrail for CreateUser and AttachUserPolicy or equivalent in the city account, identify the caller and source IP, revoke excess access, and enable or tune Enterprise Security detections that require CloudTrail.