
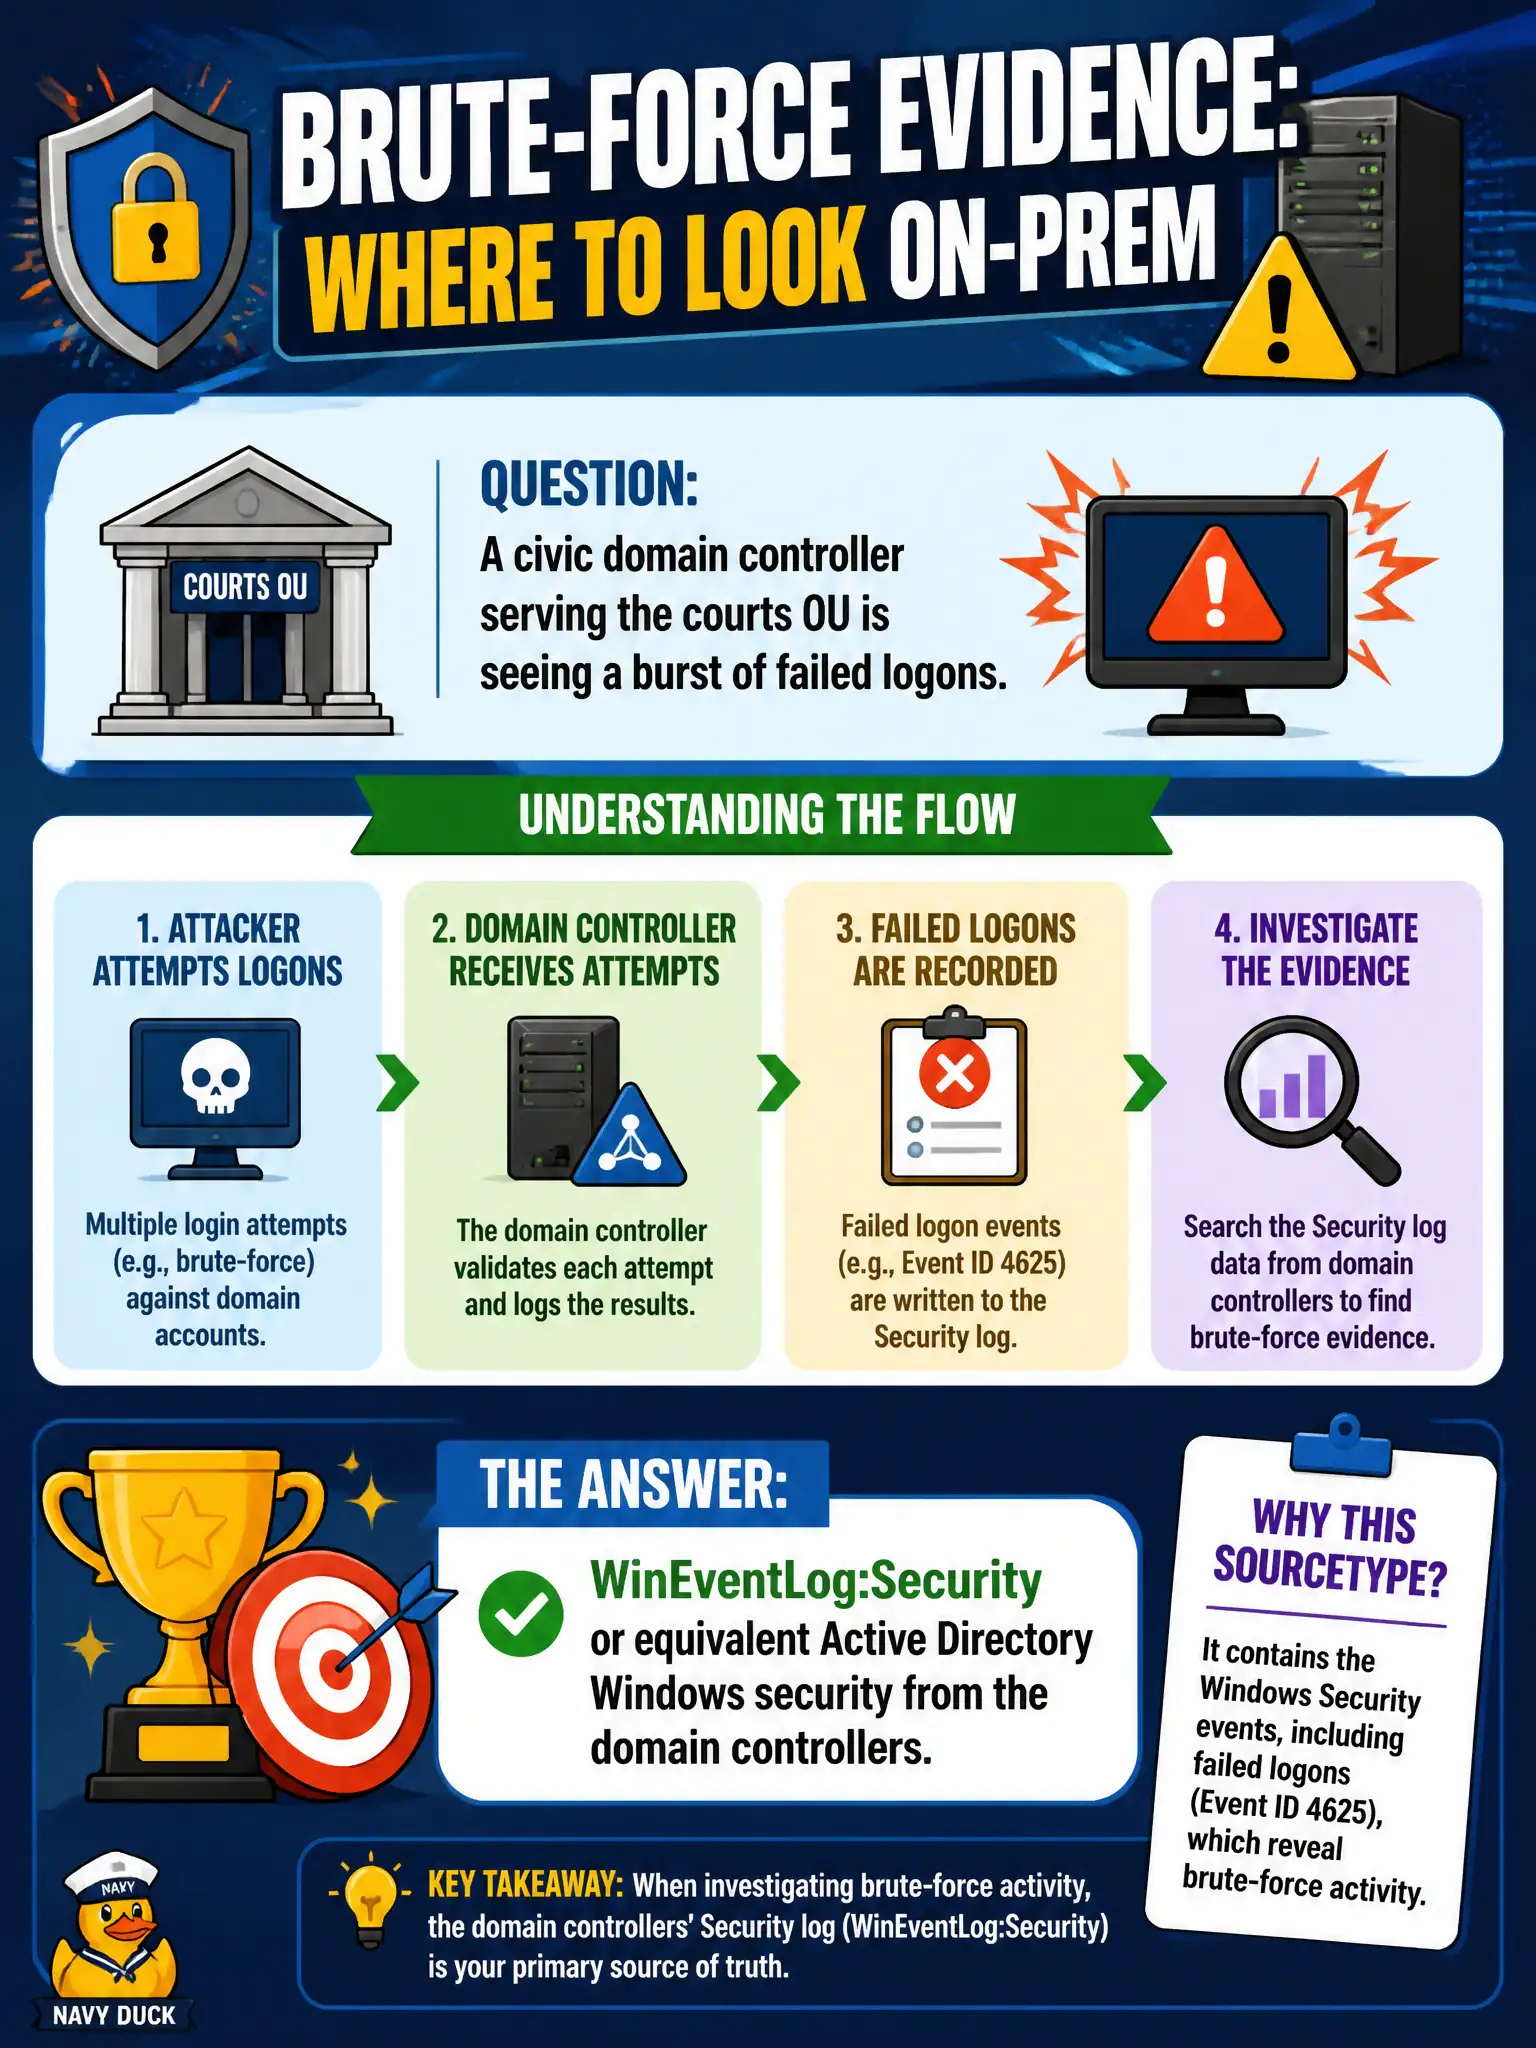
A civic domain controller serving the courts OU is seeing a burst of failed logons. Which on-prem sourcetype should hold the brute-force evidence?
Select an answer to reveal the explanation.
Short Explanation
Failed logons on a courthouse DC live in Windows security logs—the same sourcetype every on-prem AD hunt starts with. Firewall syslog and DHCP leases are useful neighbors, but they are not the DC's attendance sheet. Match the evidence to the box that saw the attack.
Full Explanation
A civic domain controller serving the courts OU that is seeing a burst of failed logons needs on-premises Windows security evidence: WinEventLog:Security or equivalent Active Directory Windows security from the domain controllers. Those events carry logon failure codes, accounts, and source workstations required for brute-force analysis against court identities and service accounts.
Cisco or Palo Alto syslog from the edge firewall does not record domain-controller logon event codes and cannot replace DC security auditing for this identity question. DHCP lease logs from the library branch that last assigned an address explain IP assignment history, not failed domain logons on the courts OU controllers. Linux auth logs from a parks kiosk that is not a domain controller are the wrong host role and wrong directory plane for Active Directory brute force.
Exam caveat: domain brute-force evidence maps to DC WinEventLog:Security or equivalent; firewall, DHCP, and unrelated Linux auth are recurring distractors.
Operational check: search WinEventLog:Security on courts OU domain controllers for failure spikes, feed the Authentication CIM model, and correlate source addresses with Asset and Identity for the attacking hosts.