
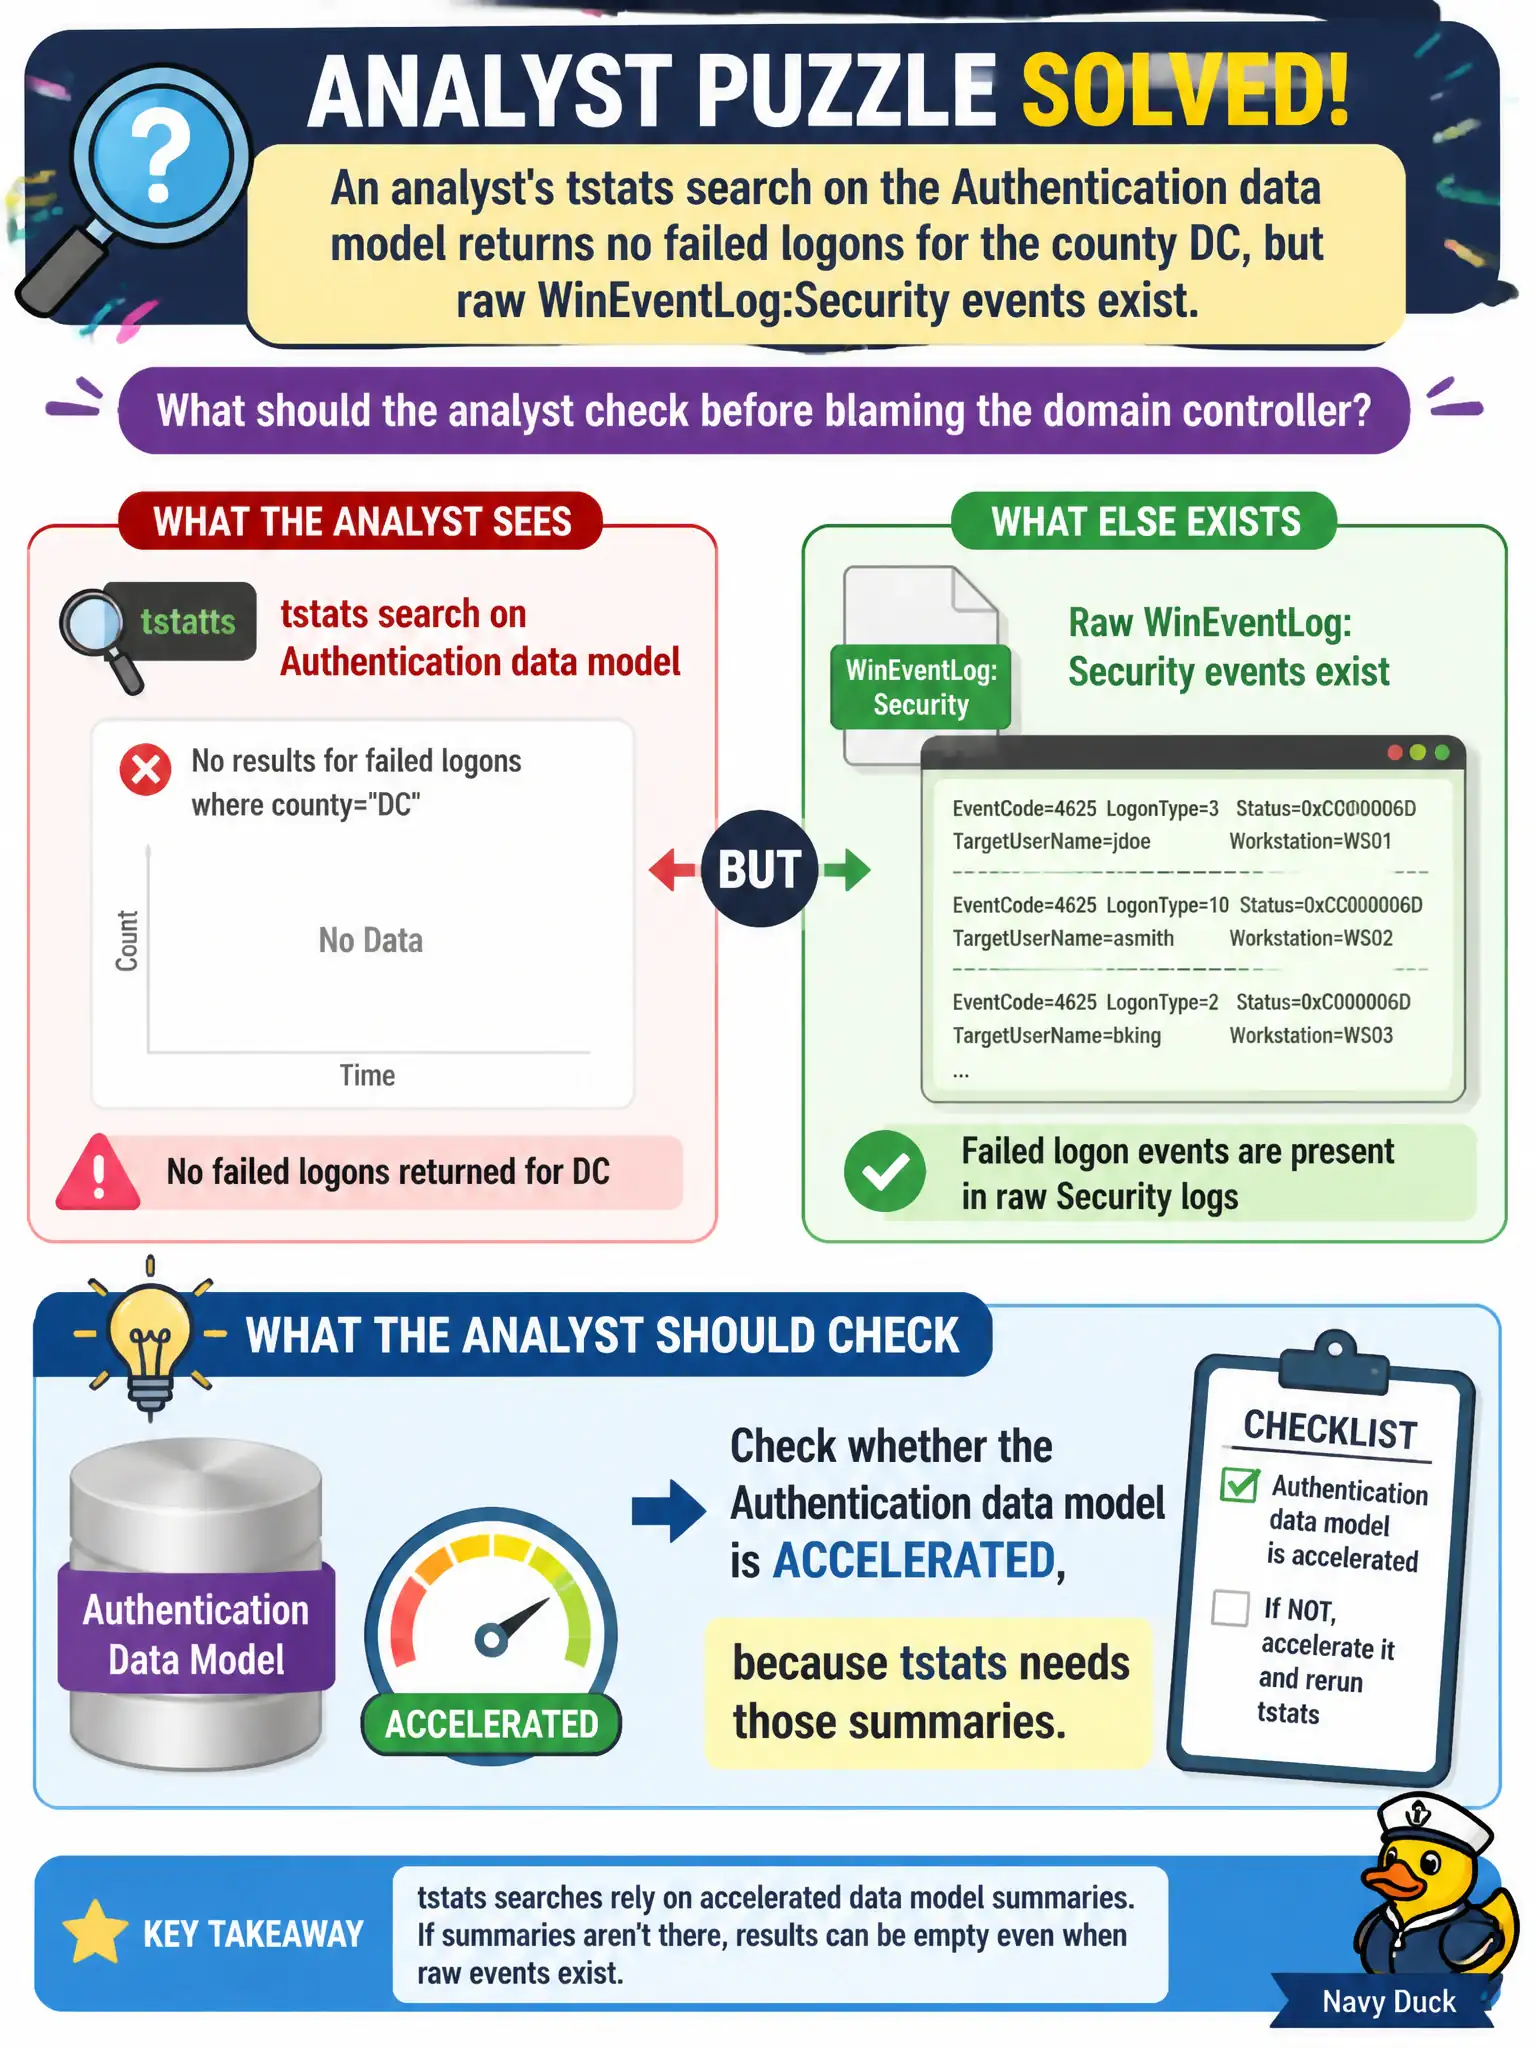
An analyst's tstats search on the Authentication data model returns no failed logons for the county DC, but raw WinEventLog:Security events exist. What should the analyst check before blaming the domain controller?
Select an answer to reveal the explanation.
Short Explanation
tstats reads the cliff notes, not the whole book. If acceleration is off, the notes are blank even though the DC is still writing Security events. Do not blame the domain controller until those summaries exist.
Full Explanation
When tstats on Authentication returns no failed logons for the county domain controller but raw WinEventLog Security events exist, check whether the Authentication data model is accelerated before blaming the domain controller. tstats depends on data-model summaries; if acceleration is missing, stalled, or the sourcetype is not constrained into the model, tstats stays empty while raw search still sees the municipal events investigators need.
Checking whether the mayor's office website CMS is down is unrelated to Authentication acceleration and wastes triage time. Checking library RFID CIM mapping does not explain domain-controller authentication gaps in tstats and mixes physical library systems into an identity-model problem. Blaming SOAR playbook Python because playbooks supposedly populate tstats invents a dependency—SOAR does not build Splunk data-model summaries.
Exam caveat: empty tstats with present raw events points first to acceleration, constraints, and tagging—not unrelated civic systems or SOAR health.
Operational check: inspect Authentication data-model acceleration status and coverage windows, confirm WinEventLog Security is tagged for authentication, rebuild summaries if needed, then re-run tstats for the domain controller and compare counts to a scoped raw search.