
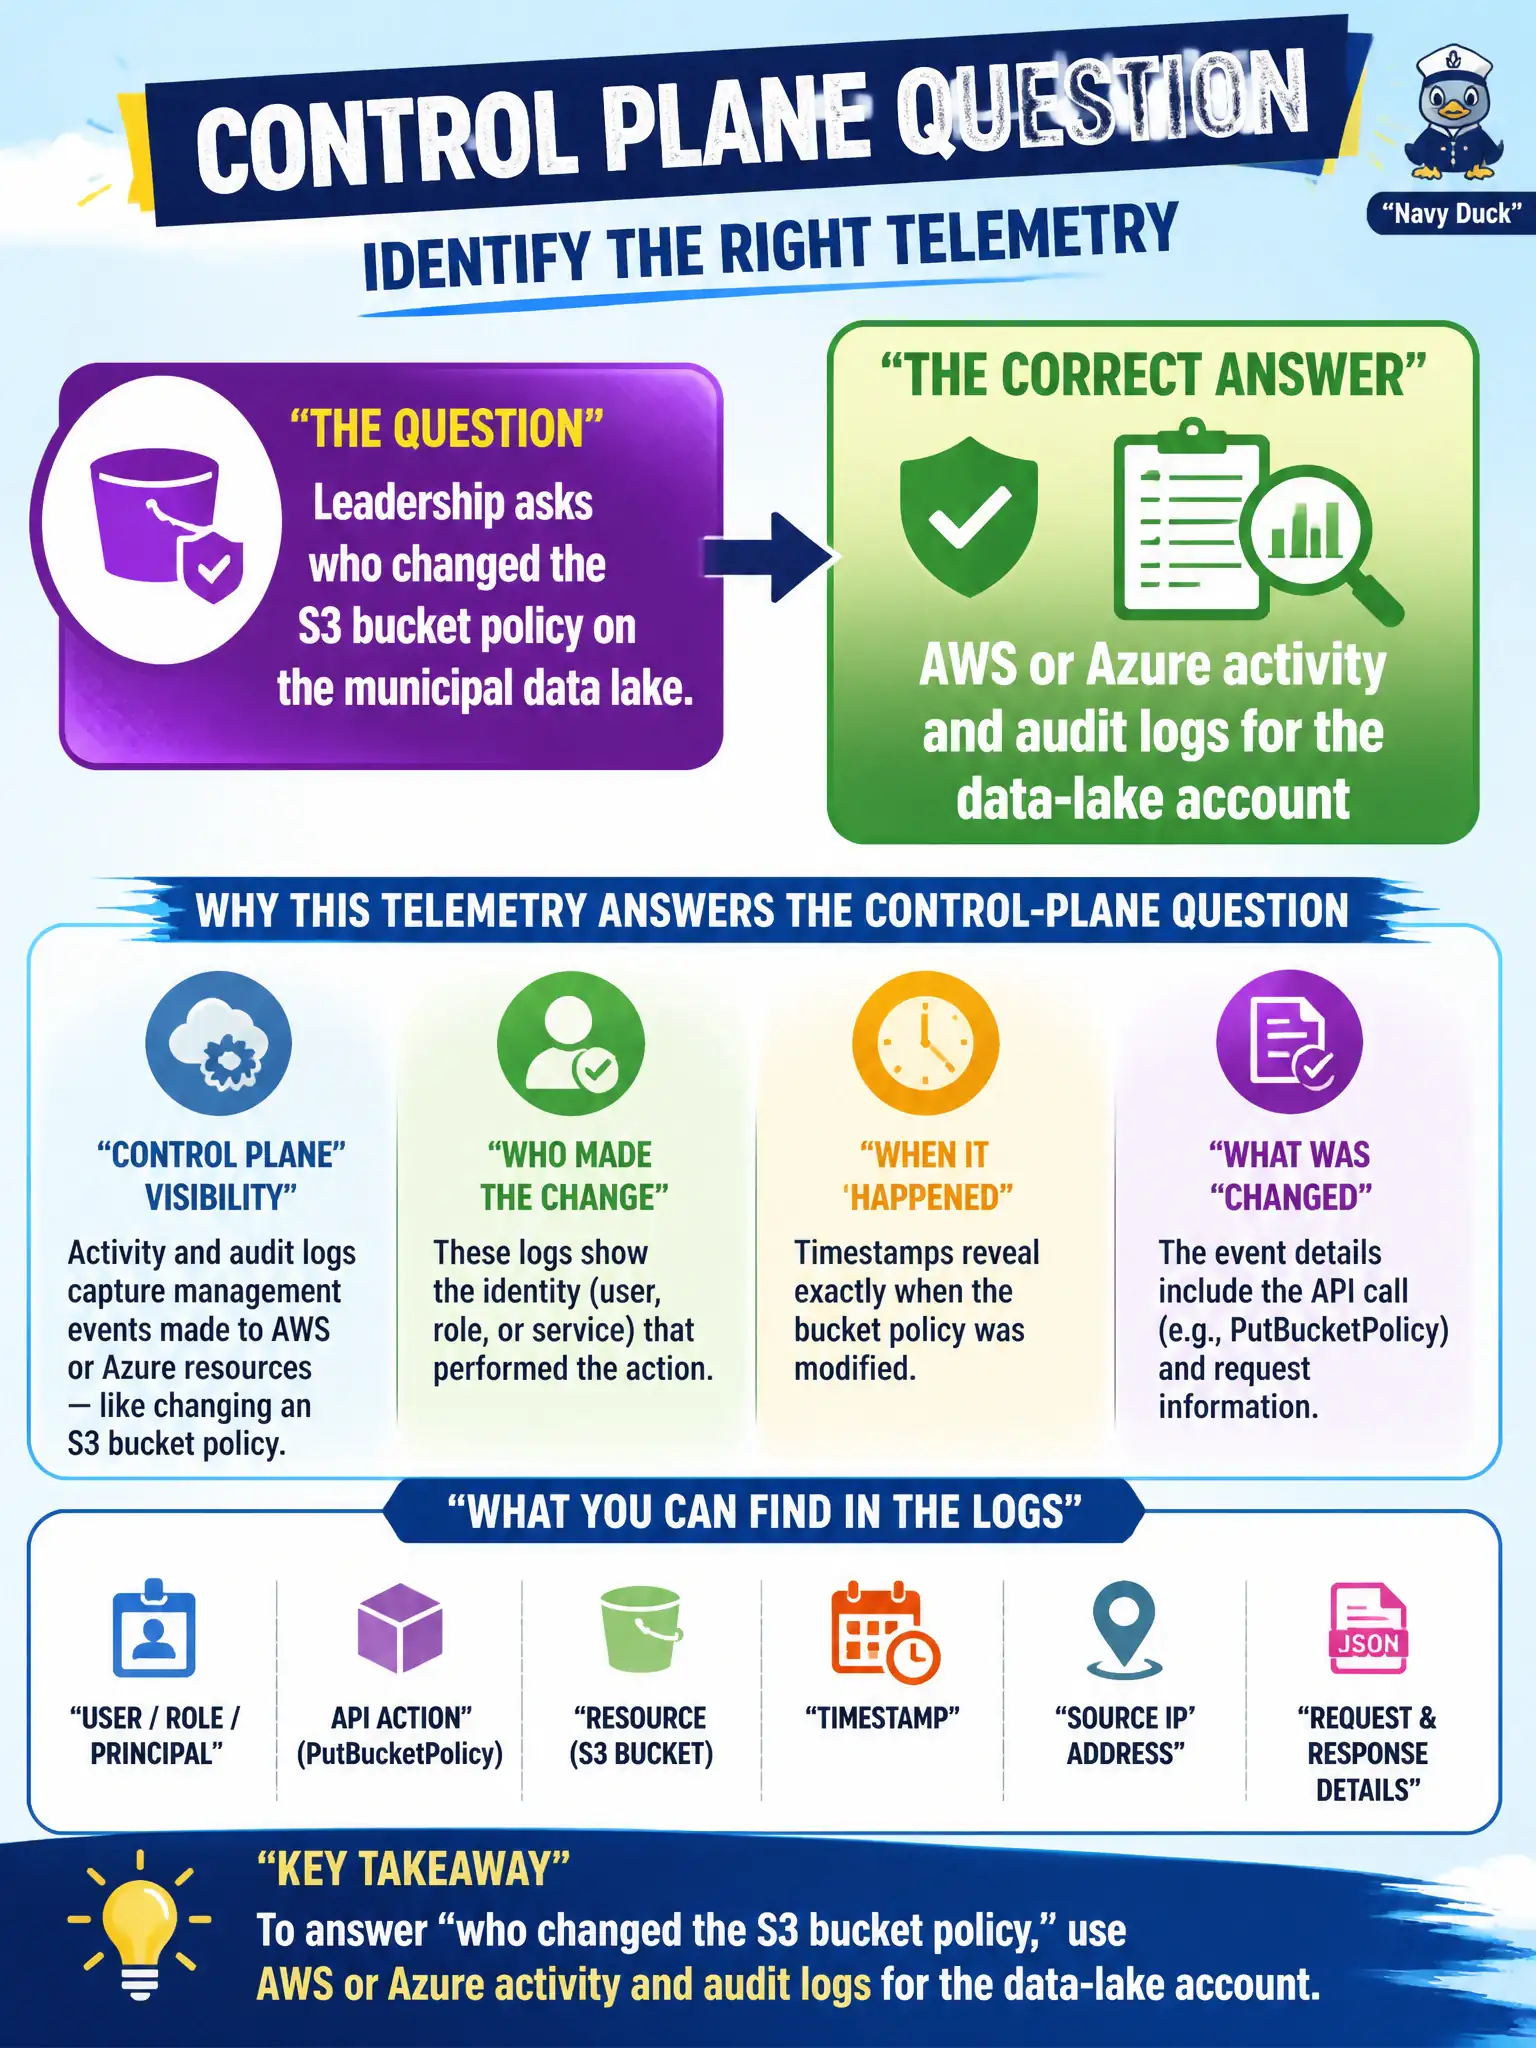
Leadership asks who changed the S3 bucket policy on the municipal data lake. Which telemetry answers that control-plane question?
Select an answer to reveal the explanation.
Short Explanation
Who edited the bucket policy is a cloud control-plane question, not a badge-swipe. Pull AWS CloudTrail or Azure activity logs for that data-lake account—the pump-station gate never signed the API call.
Full Explanation
Who changed the S3 bucket policy on the municipal data lake is a cloud control-plane question. AWS or Azure activity and audit logs for the data-lake account—for example CloudTrail or Azure Activity Log—record PutBucketPolicy and equivalent API calls with principal, time, source IP, user agent, and request parameters. Those audit trails are the authoritative answer to leadership's change-control question for object-storage IAM; physical access logs and DNS cannot reconstruct a cloud API mutation.
Badge-swipe events at the pump-station gate show physical access to a plant gate, not cloud IAM API calls against the data lake. Recursive DNS queries from clerk workstations show name resolution behavior on the municipal network, not bucket-policy mutations. The library catalog's overdue-book table is an application dataset about loans and fines and has no bearing on cloud storage IAM changes.
Exam caveat: control-plane who-changed-X-in-the-cloud questions require cloud activity or audit logs; keep physical and DNS sources for their own question types on SPLK-5001.
Operational check: query CloudTrail or Activity Log for bucket-policy or IAM changes on the data-lake account, identify the principal and source IP, verify against change tickets and break-glass procedures, and alert if the caller or policy document was unexpected.