
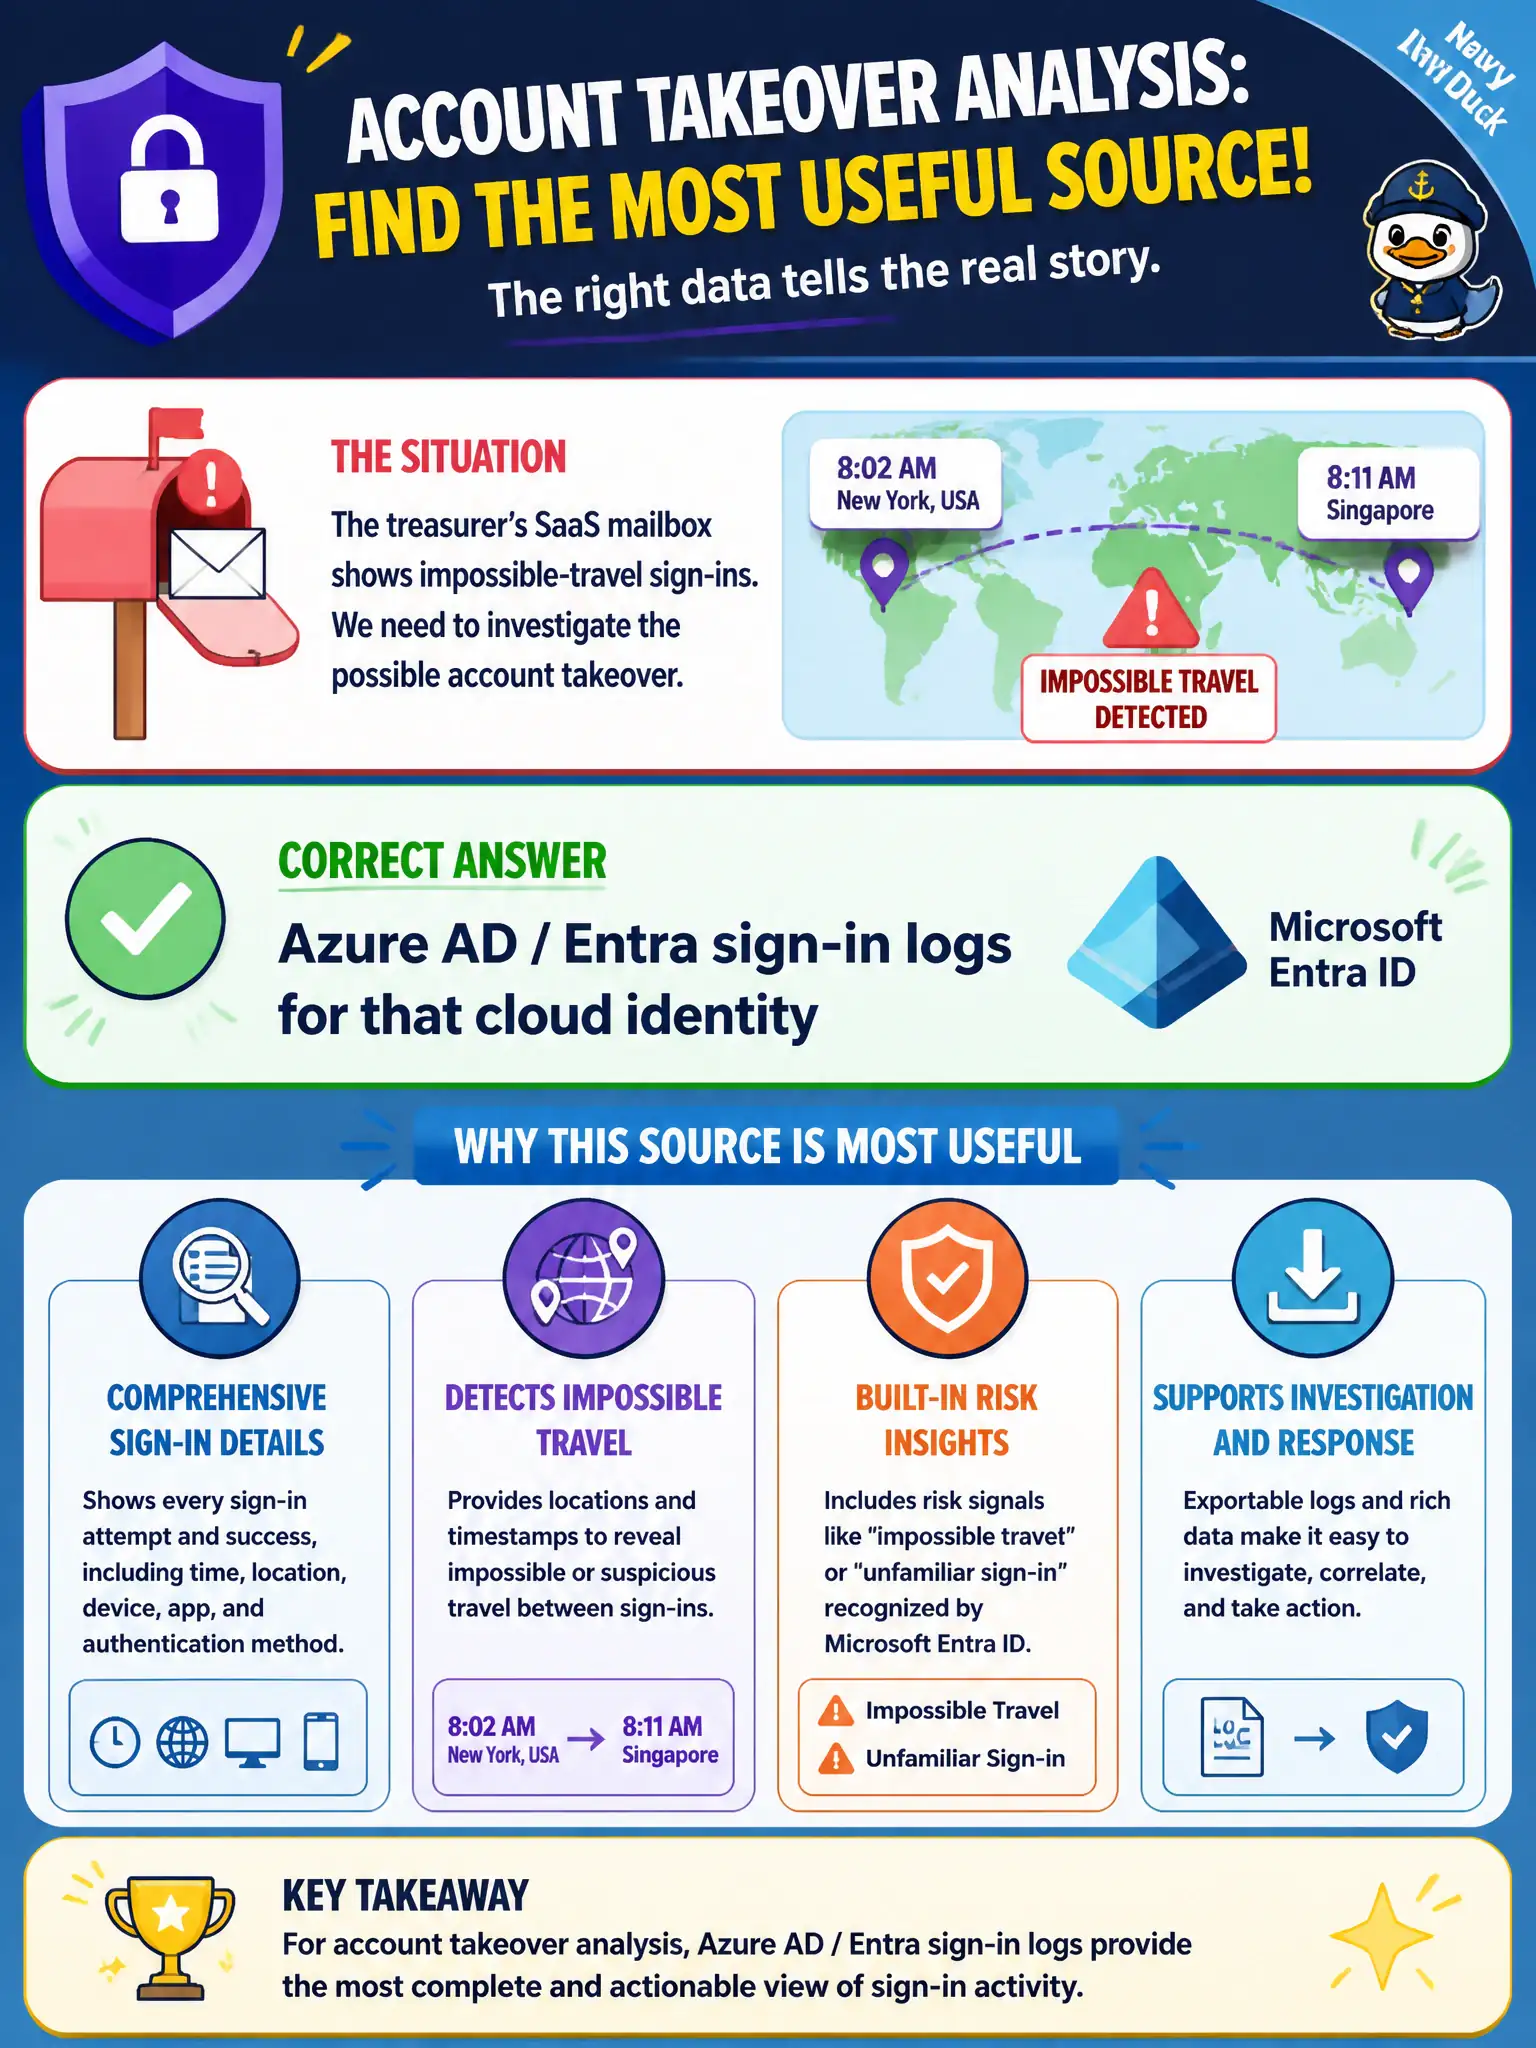
The treasurer's SaaS mailbox shows impossible-travel sign-ins. Which source is most useful for that account-takeover analysis?
Select an answer to reveal the explanation.
Short Explanation
Impossible travel on a cloud mailbox is an identity story. Entra (Azure AD) sign-in logs saw the token; the city firewall, the pump historian, and the office badge reader did not.
Full Explanation
Impossible-travel sign-ins on the treasurer's SaaS mailbox are a cloud identity question. Azure AD or Entra sign-in logs for that cloud identity are the most useful source: they record IP, location, client application, conditional access, MFA result, and success or failure for the account. On-premises perimeter devices and OT systems do not hold SaaS token claims for that mailbox and cannot prove or disprove impossible travel in the identity provider.
The on-premises perimeter firewall will not list every SaaS token claim; it may show egress addresses but not Entra authentication detail needed for account-takeover analysis. The wastewater historian for pump RPM is OT process data unrelated to cloud sign-in risk. Badge-reader events at the treasurer's office door do not complete Entra multifactor authentication and cannot substitute for IdP telemetry when travel impossibility is the claim.
Exam caveat: SaaS and account-takeover stems point to IdP sign-in logs such as Entra or Azure AD, not firewall, OT, or badge as the primary source.
Operational check: open Entra sign-in logs for the treasurer UPN across the impossible-travel window, note unfamiliar countries or IPs and MFA status, correlate risky sign-ins with mailbox forwarding rules, and use firewall only for secondary egress corroboration.