
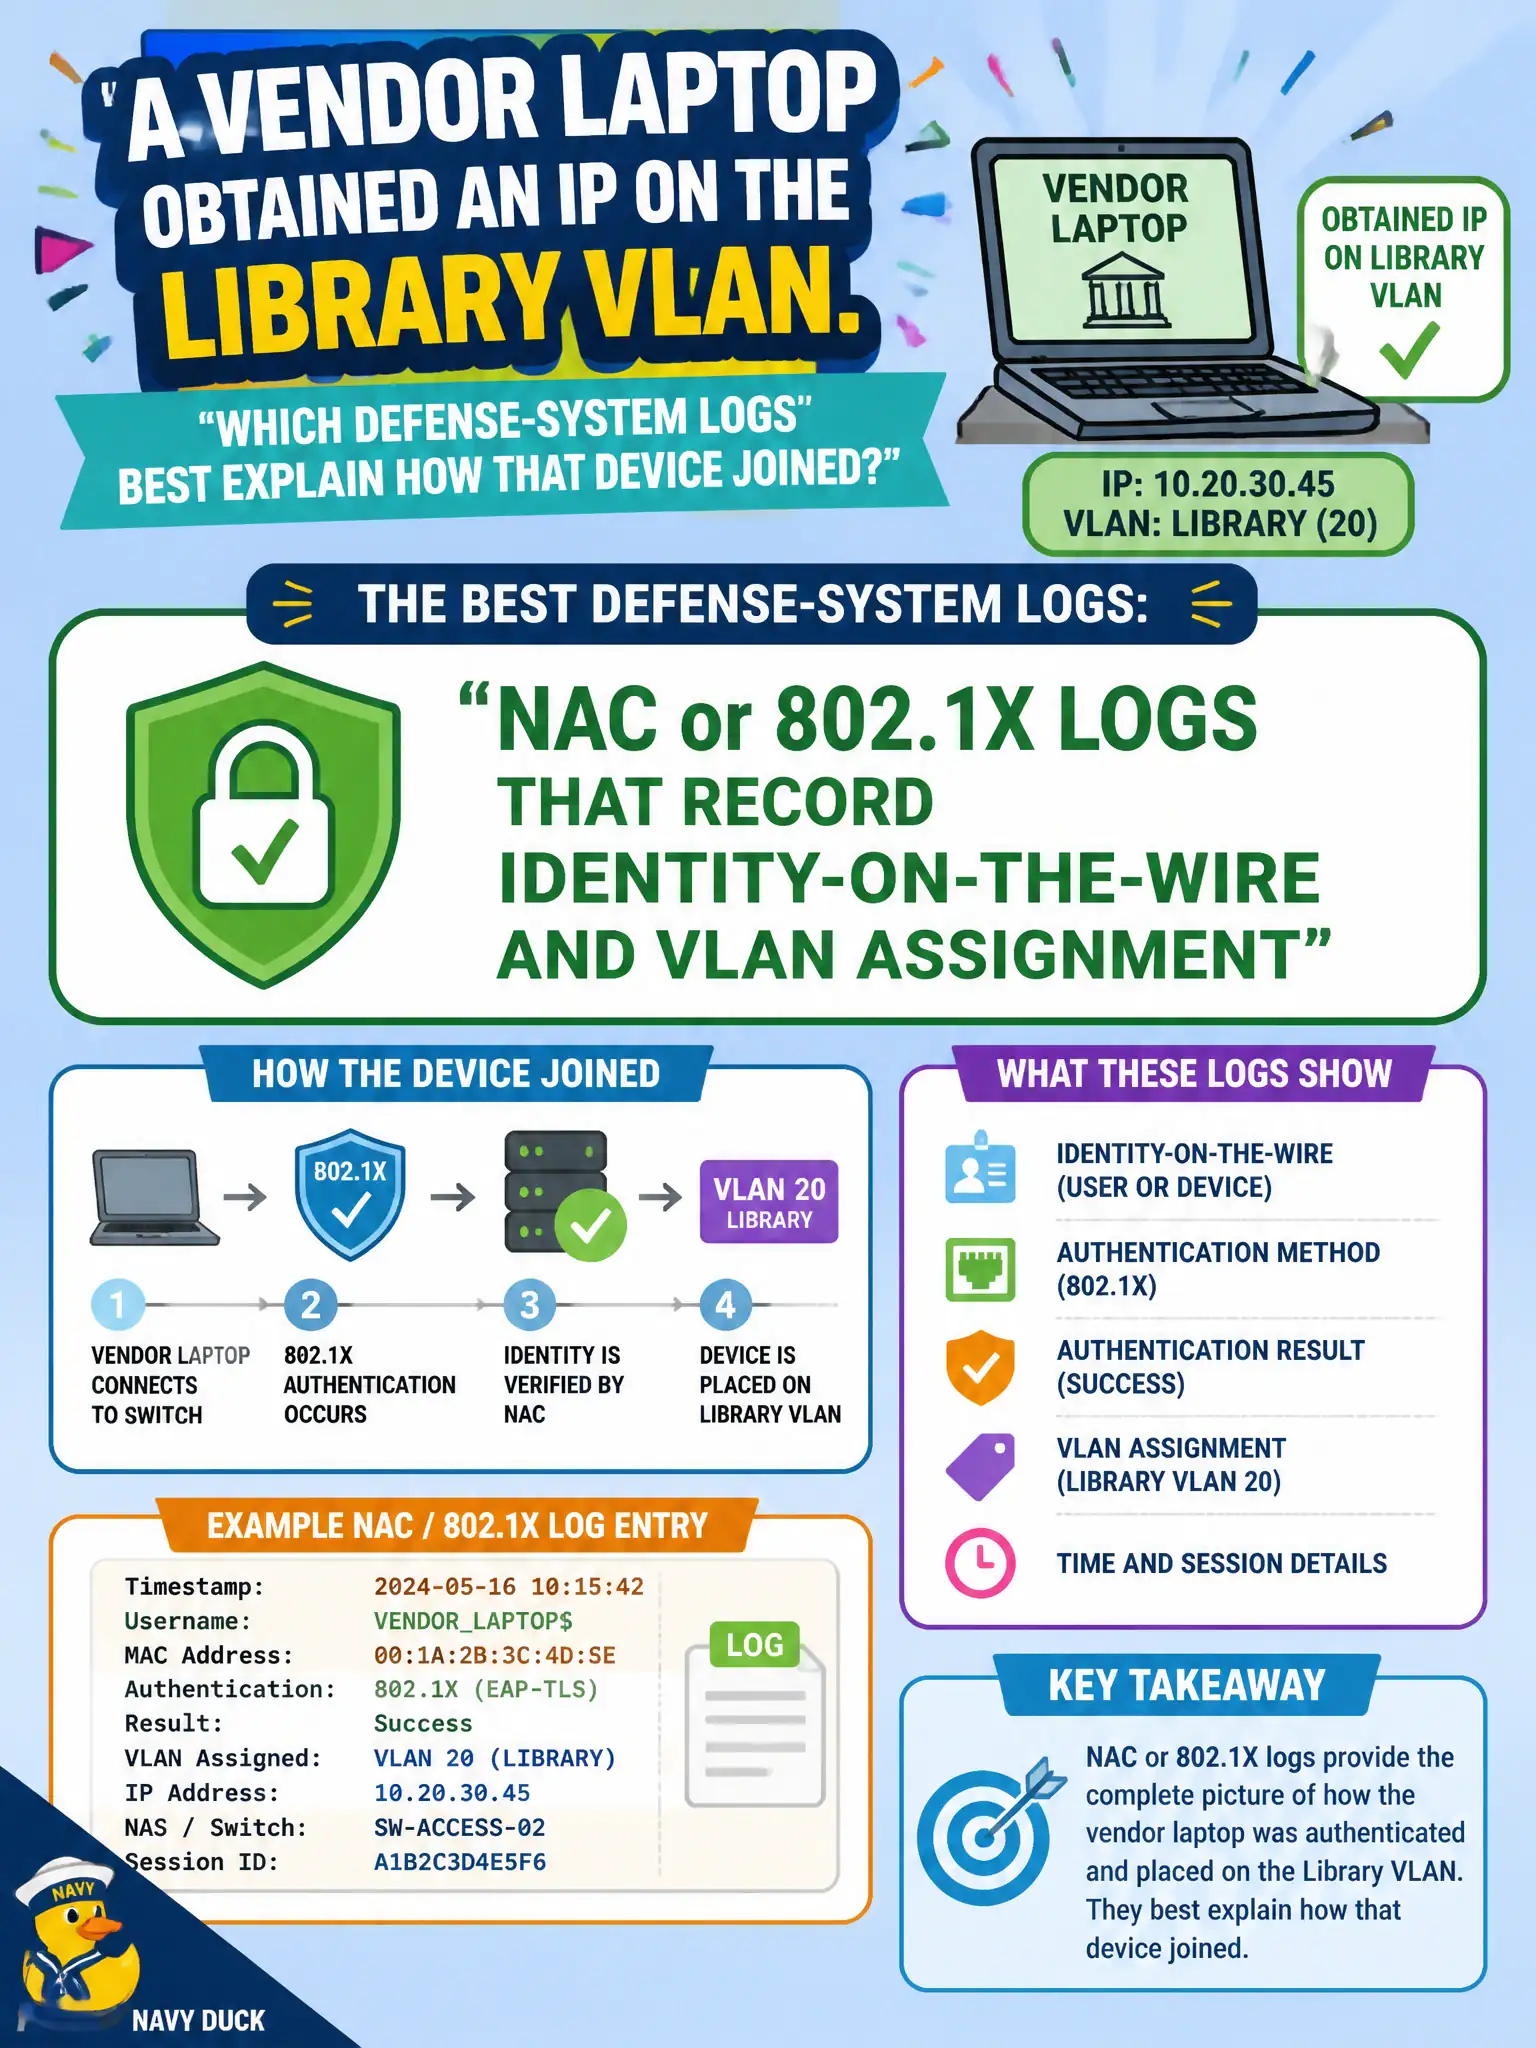
A vendor laptop obtained an IP on the library VLAN. Which defense-system logs best explain how that device joined?
Select an answer to reveal the explanation.
Short Explanation
How did the laptop get a seat on the library VLAN? Ask the bouncer. NAC and 802.1X logs are identity-on-the-wire—CMS authors, mailbox rules, and S3 policies never issued that IP.
Full Explanation
A vendor laptop obtaining an IP on the library VLAN is an identity-on-the-wire and network-admission question. NAC or 802.1X logs best explain how that device joined—supplicant identity, certificate or credential result, and VLAN assignment. Those records tell the defense analyst whether the laptop was authorized, guest-quarantined, or mis-assigned onto library segments that should not host unmanaged vendor gear.
The public website CMS author table documents who edits web content, not switch-port authentication or VLAN placement. Mailbox audit forwarding rules on the library director explain mail configuration changes, not how a laptop joined a VLAN. CloudTrail bucket-policy events for the municipal data lake are cloud control-plane audit for object storage and do not describe library 802.1X admission.
Exam caveat: device-join and VLAN questions map to NAC or 802.1X (or equivalent); CMS, mailbox, and cloud storage audit are wrong planes for wired or wireless admission.
Operational check: query NAC or RADIUS for the laptop MAC or certificate identity at the join time, note VLAN and authentication result, correlate with switch port and DHCP lease, and escalate if a vendor device landed on an unexpected library segment.