
A municipal compliance officer asks whether Enterprise Security is NIST. What should the analyst say?
Select an answer to reveal the explanation.
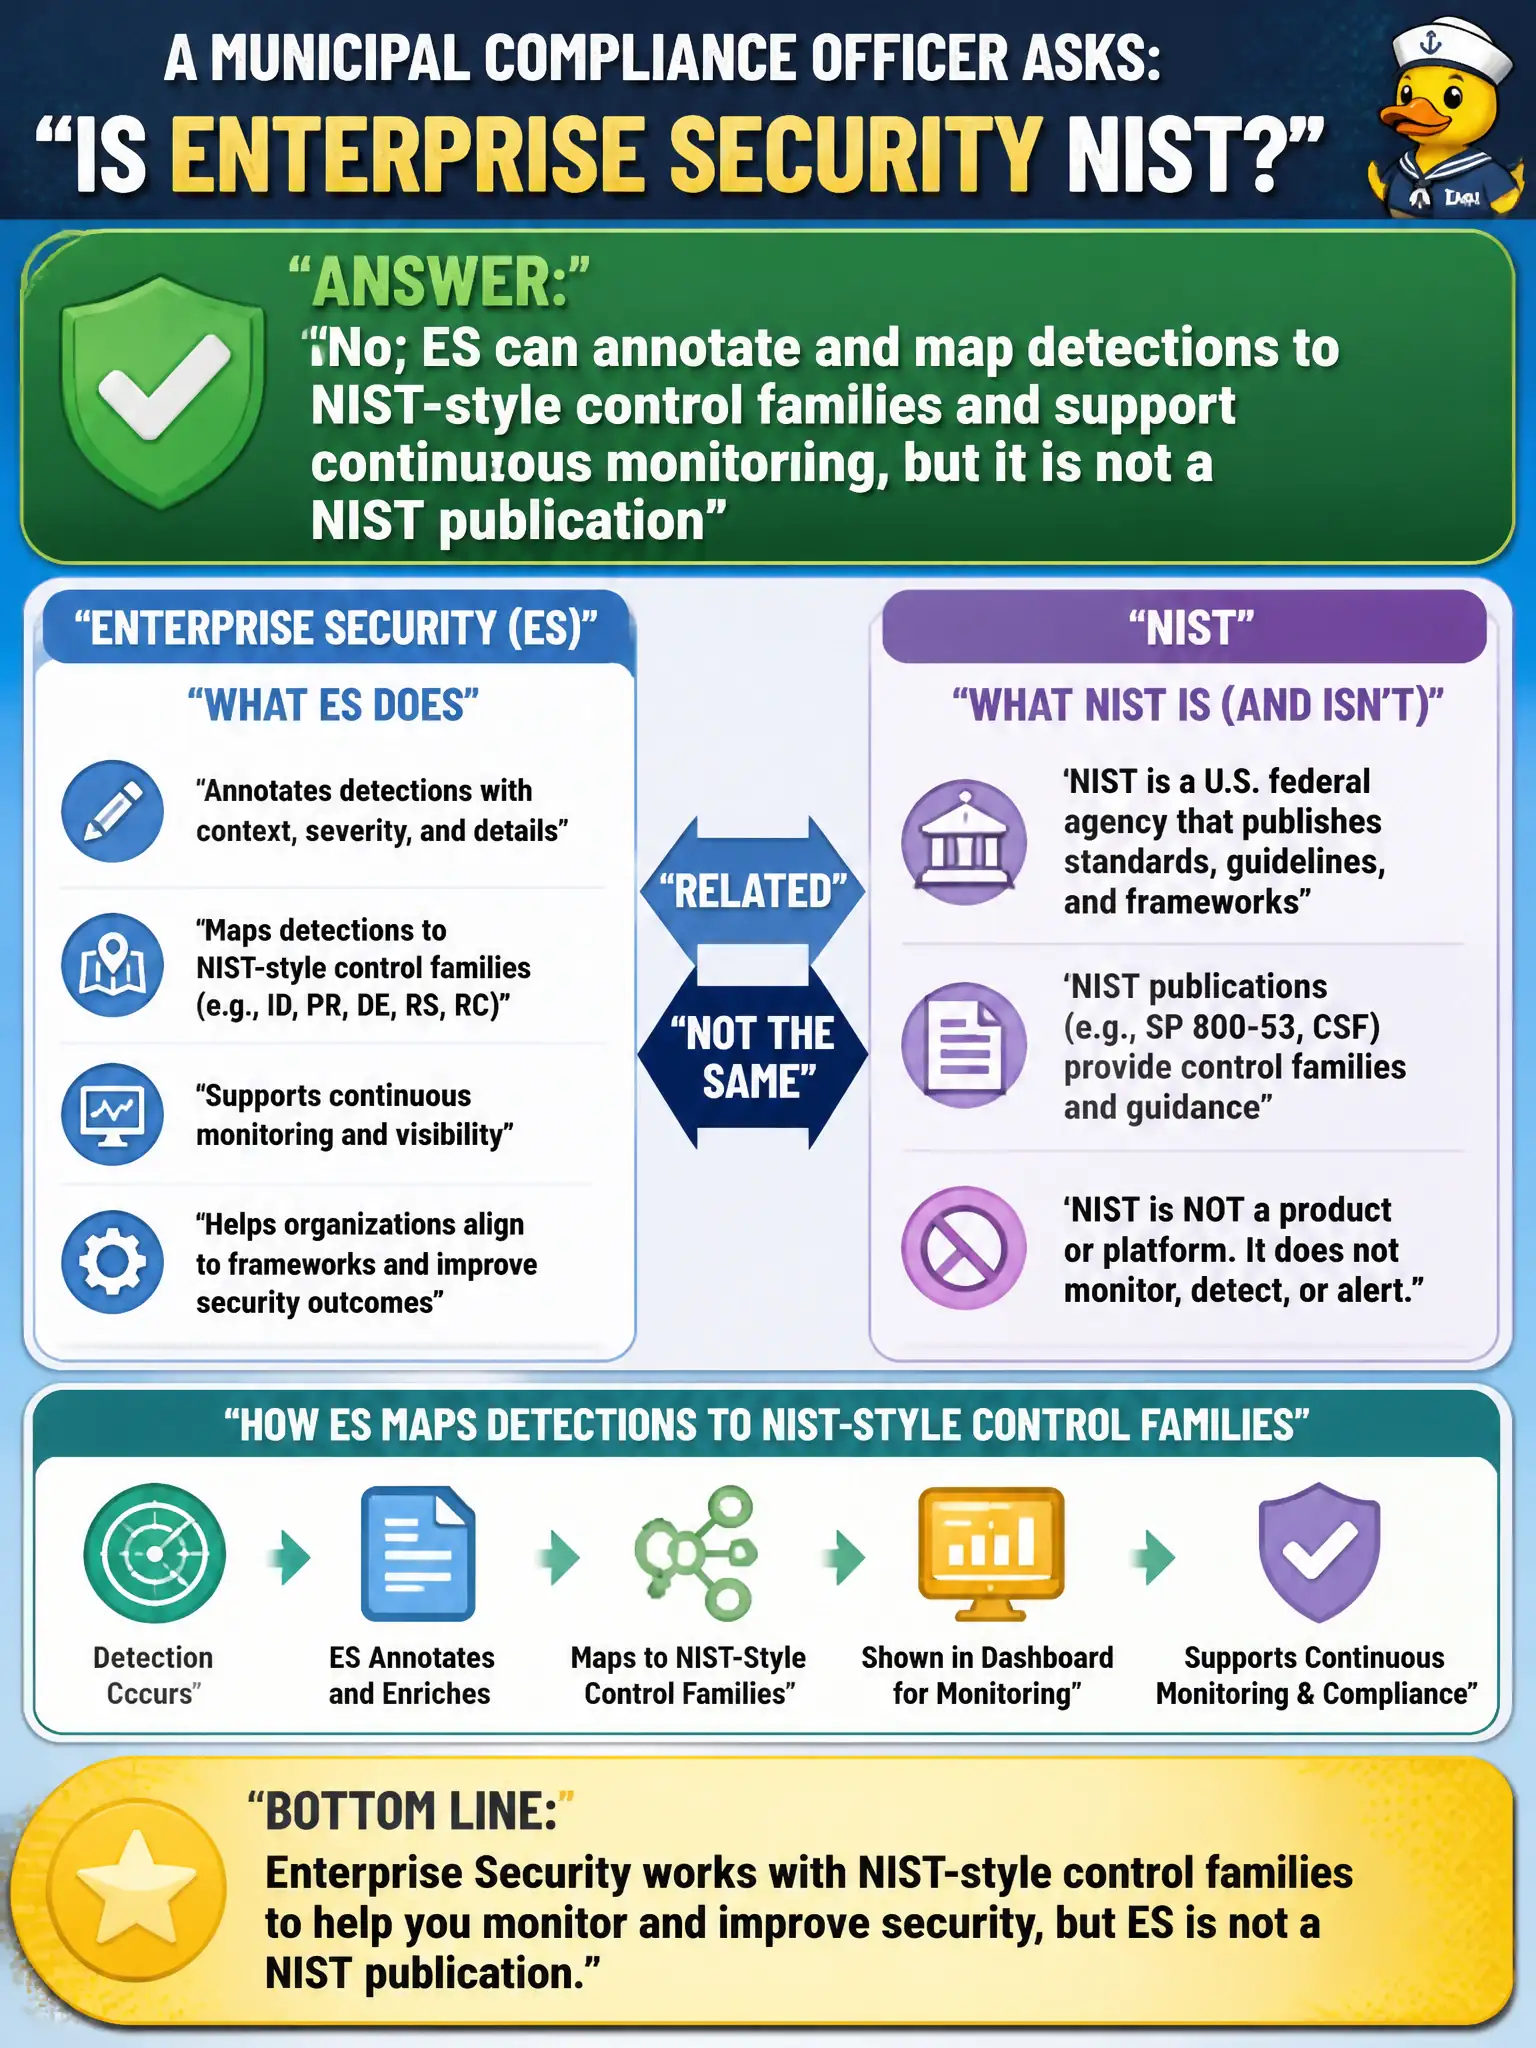
Short Explanation
ES is the camera system, not the building code. It can map detections to NIST-style families and keep watch, but installing it does not make the city NIST-certified. CIM is a schema, not the Cybersecurity Framework.
Full Explanation
A municipal compliance officer asking whether Enterprise Security "is NIST" should hear no: ES can annotate and map detections to NIST-style control families and support continuous monitoring, but it is not a NIST publication and installing it does not certify the city. Civic compliance conversations stay honest when the SIEM is framed as evidence and analytics supporting a control program, not as the standard itself.
Claiming installing ES certifies the city against NIST SP 800-53 fails by concept: a product install is not an authorization or certification outcome. Claiming the CIM Authentication data model is the NIST Cybersecurity Framework fails by concept: CIM is a Splunk normalization schema, not CSF. Claiming ES cannot map to any control family and is only a log store fails by concept: ES explicitly supports mapping and monitoring use cases tied to control language.
Exam caveat: Distinguish standards/frameworks (NIST) from platforms that help implement and evidence them (ES)—install ≠ certified.
Operational check: In compliance narratives, list the NIST or CSF families in scope, show how ES detections and investigations produce evidence for those families, and never write "Enterprise Security" in the blank reserved for the governing standard.