
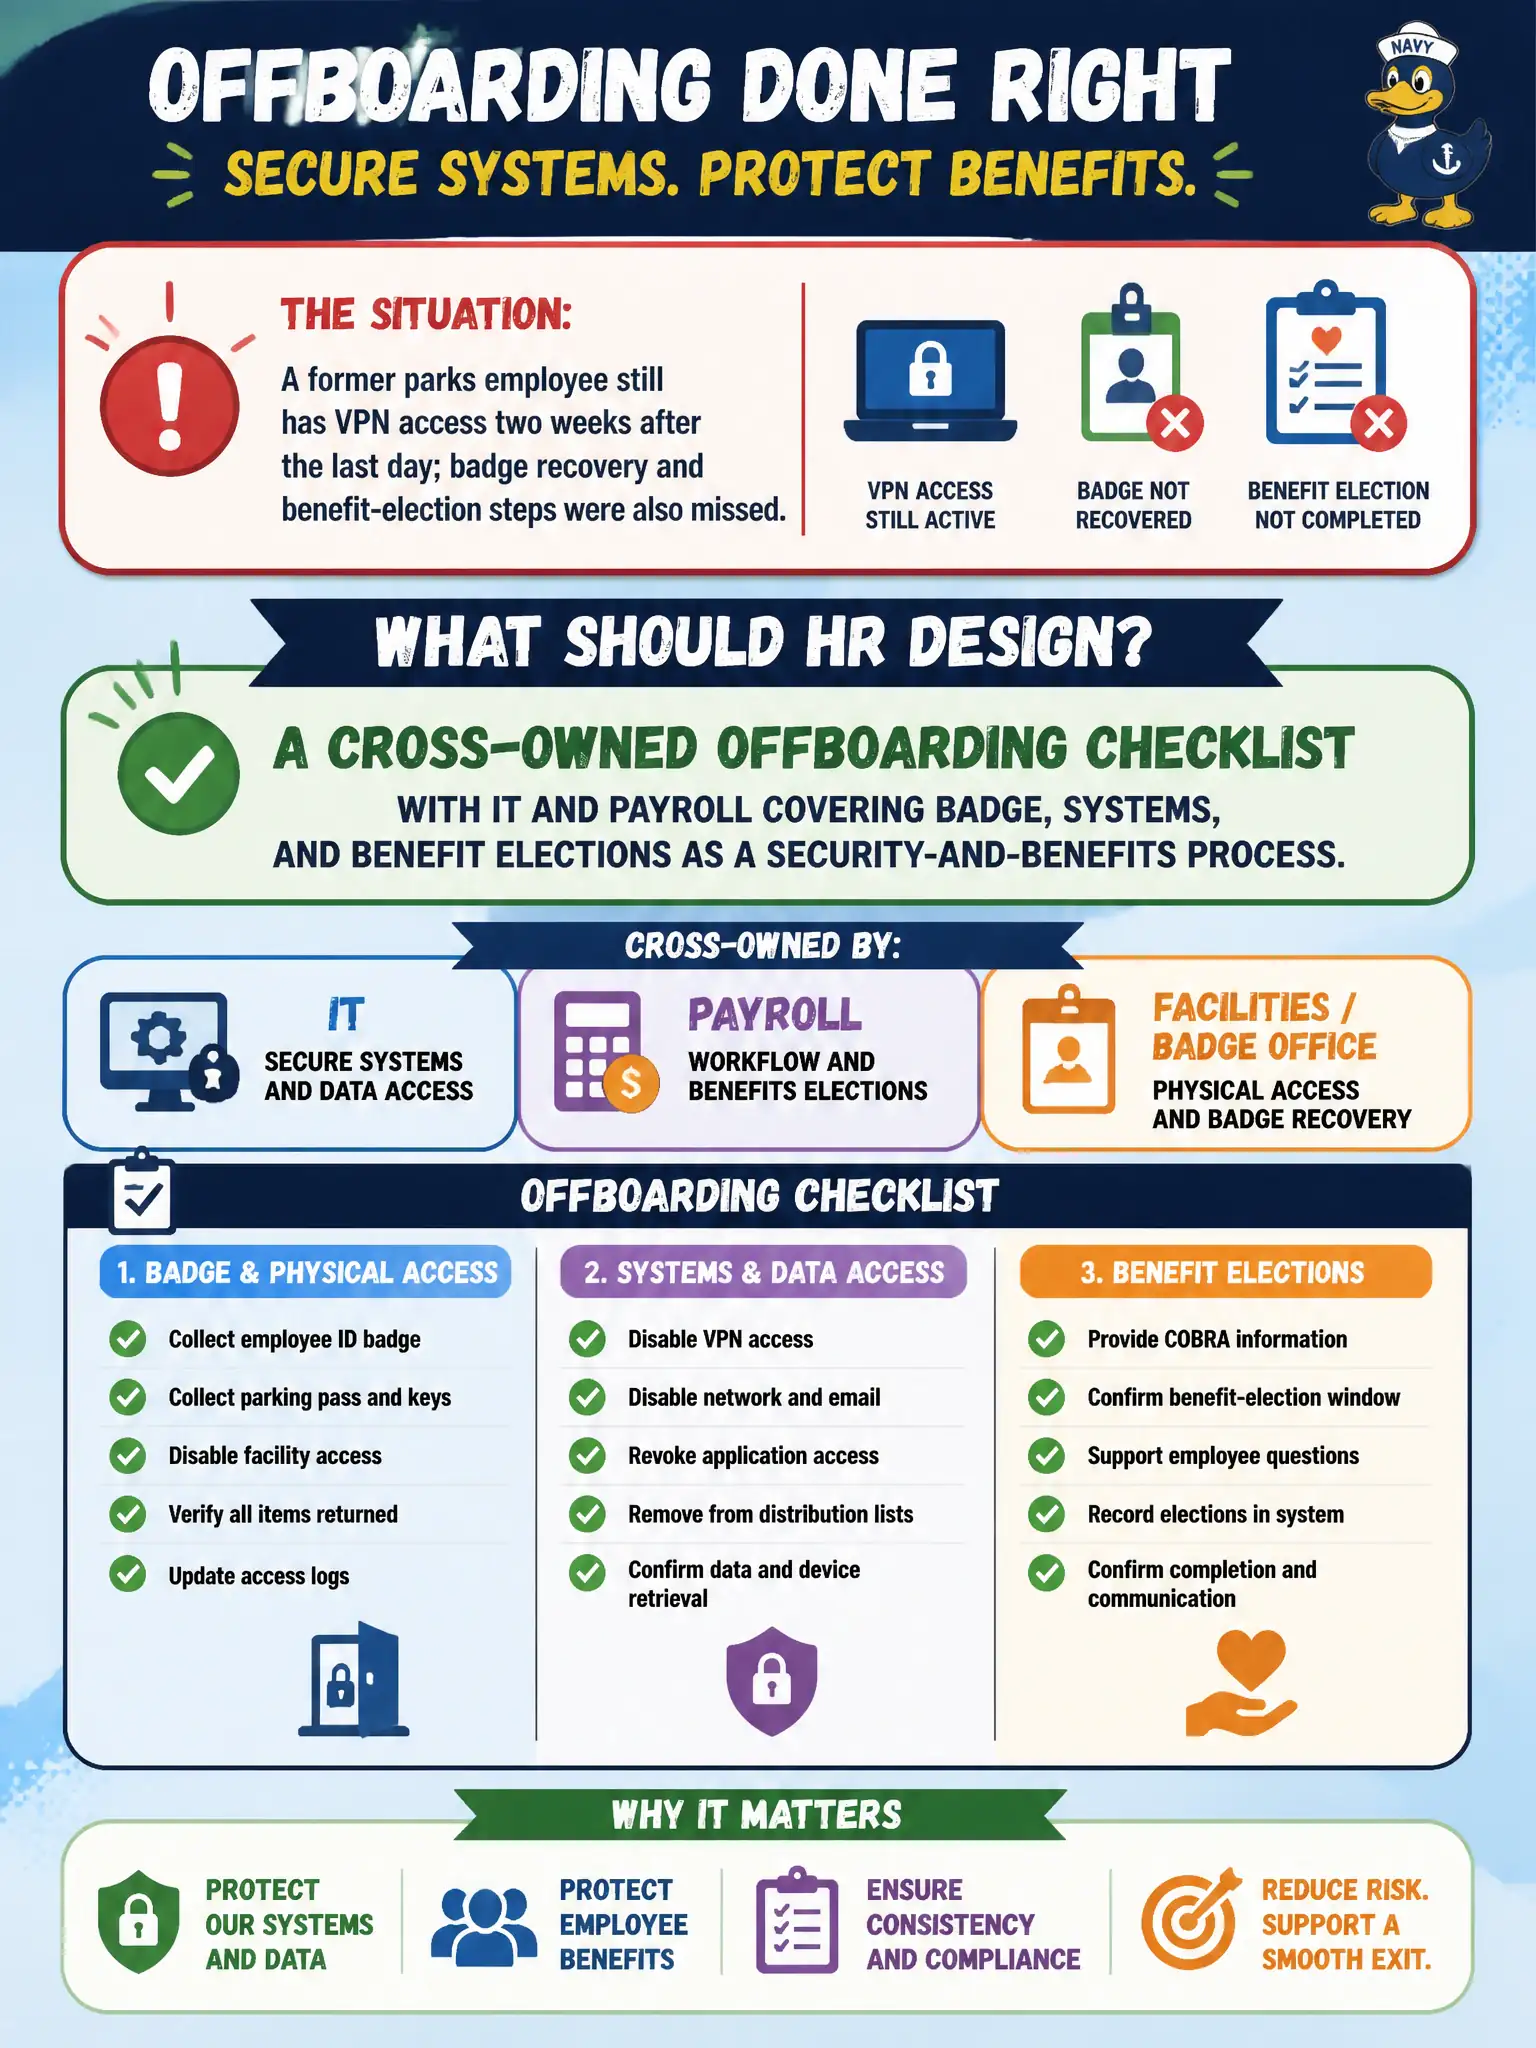
A former parks employee still has VPN access two weeks after the last day; badge recovery and benefit-election steps were also missed. What should HR design?
Select an answer to reveal the explanation.
Short Explanation
Offboarding is not a sheet cake. If the VPN still works, the city still has a hole. Badge, systems, and benefits need named owners—HR, IT, payroll—not a hope that someone remembers.
Full Explanation
A former parks employee with VPN access two weeks after the last day, plus missed badge recovery and benefit-election steps, shows offboarding failed as a security-and-benefits process. HR should design a cross-owned checklist with IT and payroll covering badge, systems, and benefit elections. If the VPN still works, the city still has a hole; civic cybersecurity and benefits compliance need named owners, not sheet-cake hope.
A farewell-lunch checklist owned only by the supervisor's intern fails by concept: critical controls cannot sit with temporary social owners. Keeping access open for 90 days in case of return fails security baseline. Emailing the former employee to turn in the badge when convenient fails by outsourcing the control to someone with no duty.
Exam caveat: disable access effective last day unless a documented, time-limited exception exists with owner approval. Operational check: implement a multi-owner checklist, audit recent separations for lingering accounts, and report exception aging to IT security and HR leadership. Public employers should record the chosen control and rejected options in the talent or labor file so future leaders understand how the decision protects continuity of resident services.