
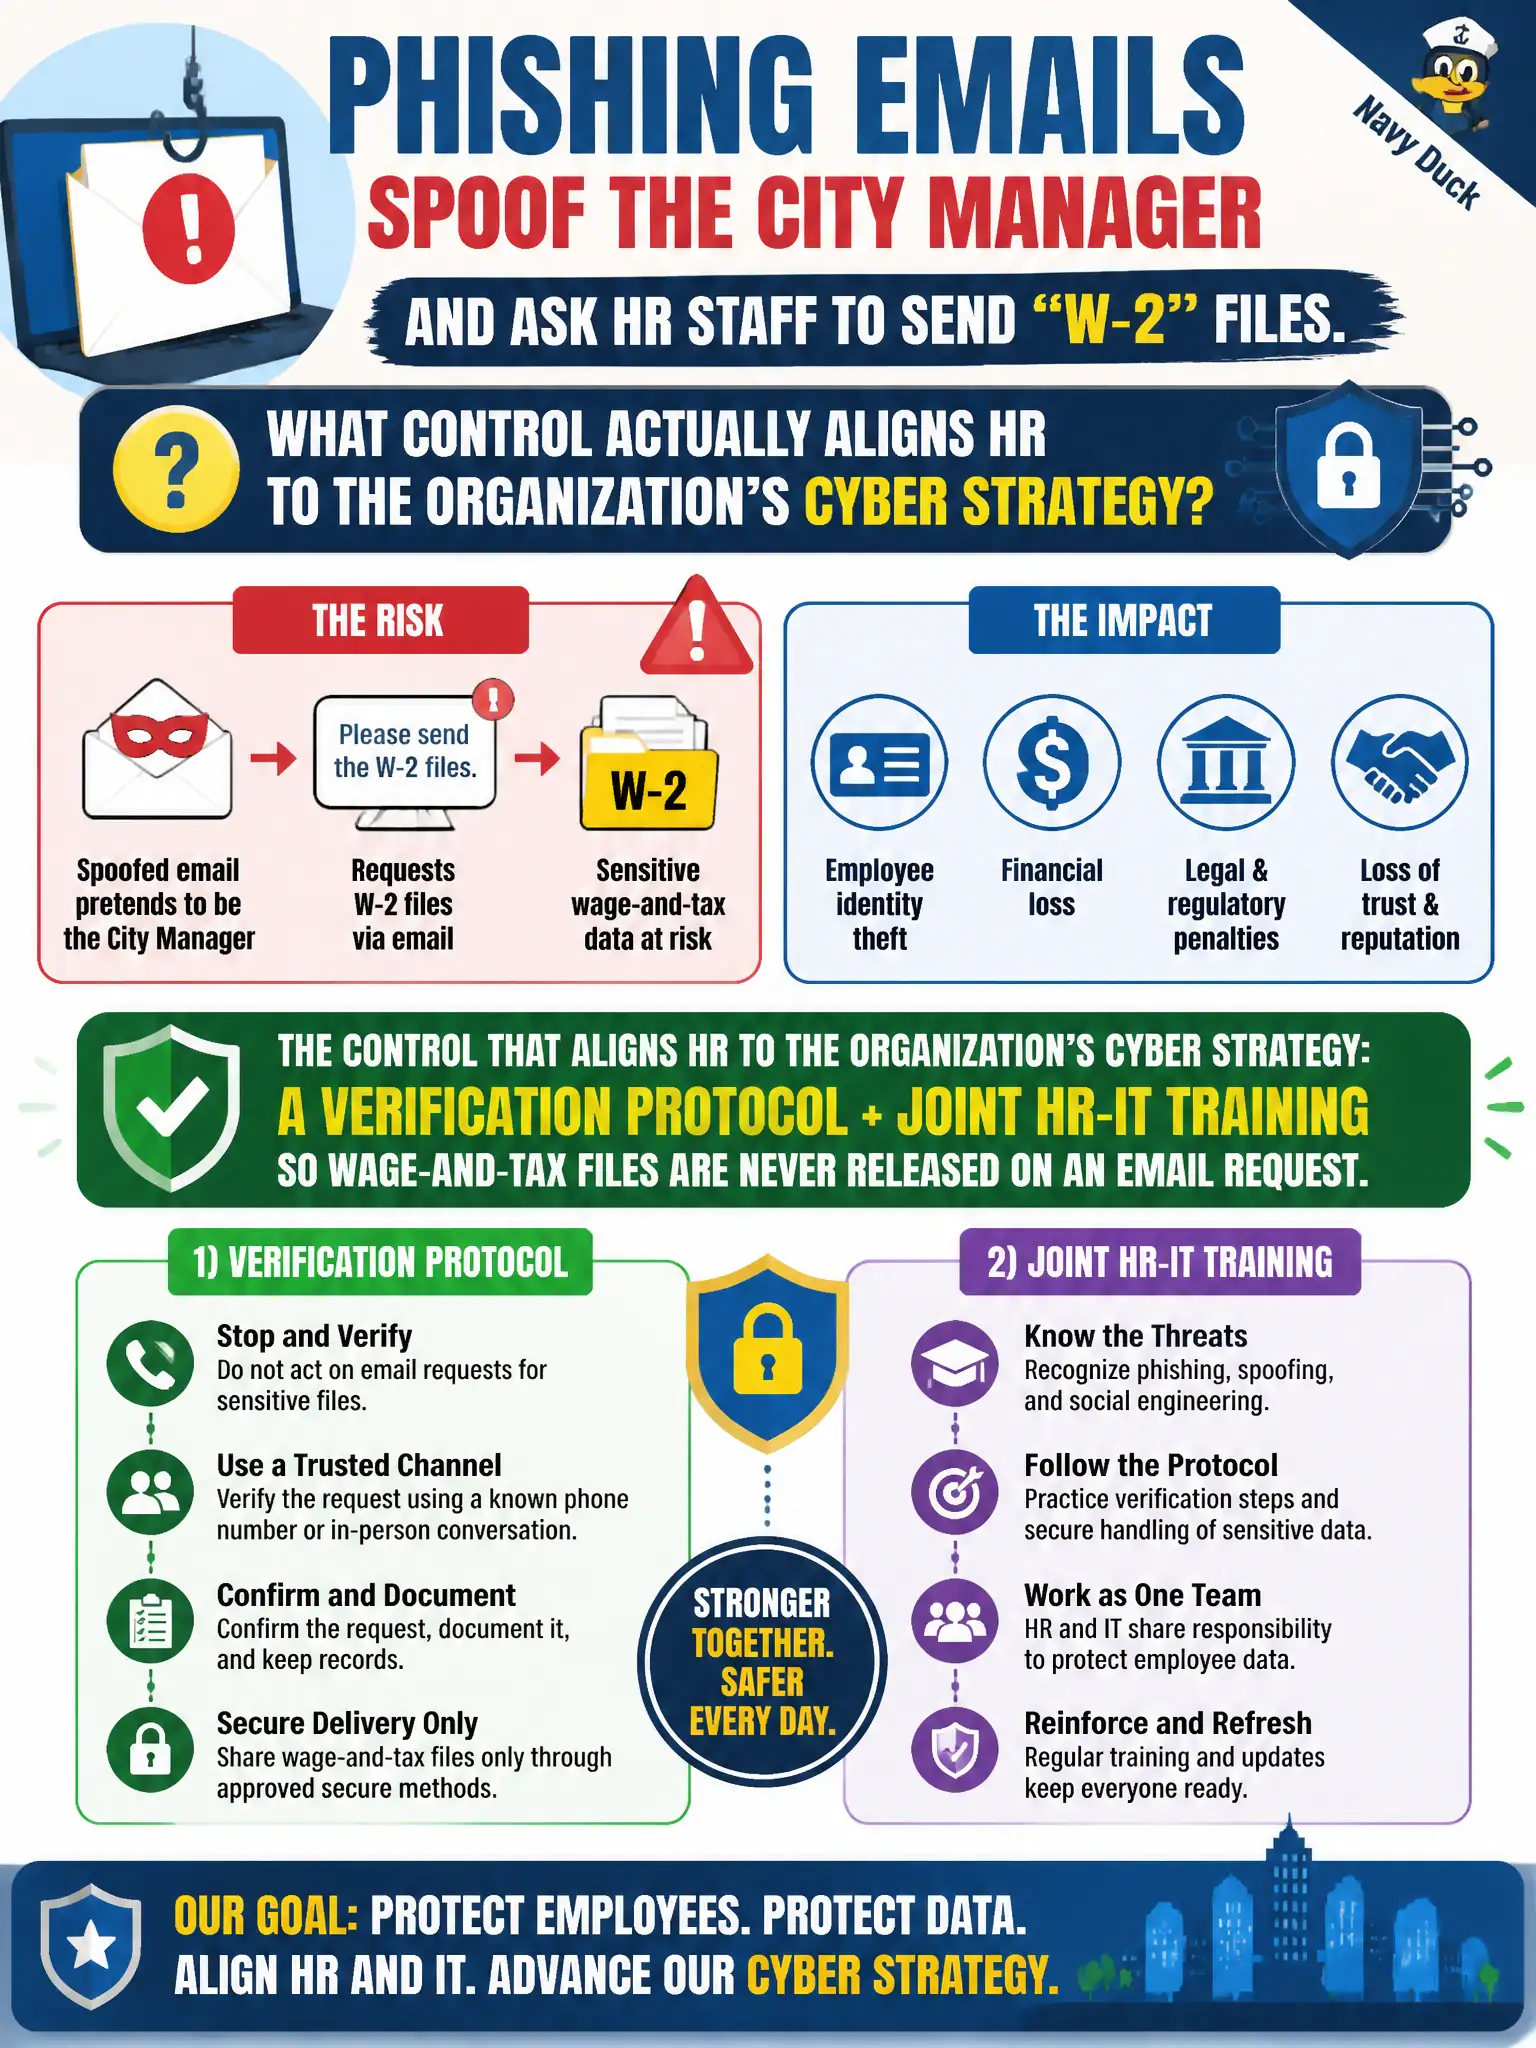
Phishing emails spoof the city manager and ask HR staff to send W-2 files. What control actually aligns HR to the organization's cyber strategy?
Select an answer to reveal the explanation.
Short Explanation
A wanted poster about pickpockets does not replace keeping the wallet zipped. HR is a phishing target because it holds W-2s and SSNs. The control is a call-back rule and practice with IT, not a cute sign.
Full Explanation
HR is a high-value phishing target because it can release wage, tax, and identity data. Alignment to the municipal cyber strategy is a process control: out-of-band verification plus joint HR-IT training so W-2 and similar files are never released on an email request that spoofs the city manager. The release protocol is the control, not awareness décor.
A break-room poster that phishing exists, with no change to release procedures, leaves the attack path open. Automatically fulfilling any request that displays the city manager's name optimizes for executive convenience and is exactly the failure mode attackers rely on. Moving all W-2 files into an unencrypted shared mailbox concentrates the prize and removes encryption that the cyber strategy expects for tax data.
Exam caveat: verification must be practical under time pressure—callback to a known number or ticketed request—not an informal chat that can also be spoofed. Operational check: publish a written W-2 release protocol, run a joint phishing tabletop with payroll and benefits staff, and confirm no tax file leaves the system without a logged out-of-band check. Document ownership so auditors can see who maintains the control.