
An international logistics company wants to transition from a generic, compliance-by-template model to a risk-based compliance program. Which approach best represents this principle?
Select an answer to reveal the explanation.
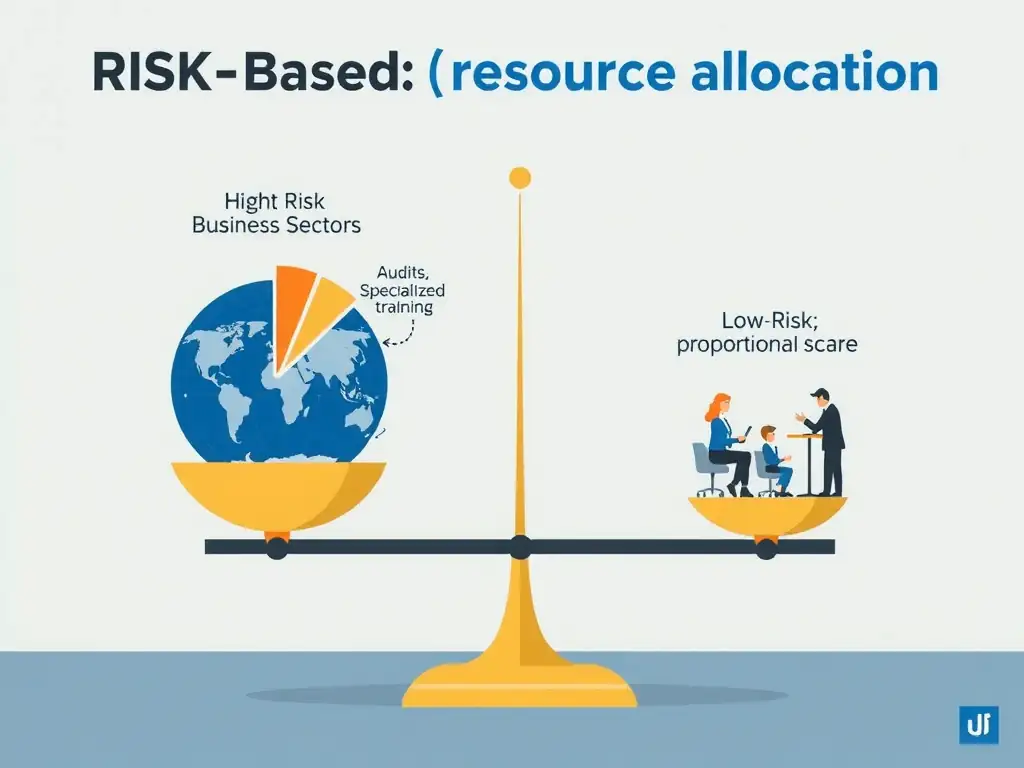
Short Explanation
Think of it like this: you wouldn't spend the same amount of money securing a small tool shed as you would securing a vault filled with gold. You put your security cameras and locks where the valuable stuff is. A risk-based compliance program does the same thing: you assess your biggest exposures, like high-corruption sales operations, and focus monitoring and audit resources there.
Full Explanation
One key principle of effective corporate compliance, as emphasized by the U.S. Federal Sentencing Guidelines and international regulatory bodies like the OECD, is that compliance programs must be tailored to the specific risks faced by the organization. A one-size-fits-all approach is inefficient and often ineffective, as it spreads compliance resources too thin and fails to address deep-seated systemic risks.
Allocating compliance monitoring and auditing resources proportionally to business operations and jurisdictions that present the highest probability and impact of legal breaches is correct because a risk-based compliance program prioritizes resources, oversight, and monitoring controls based on the results of a formal risk assessment. High-risk areas, such as operations involving government contracts, high-risk geographic locations, or complex regulatory requirements, receive more frequent audits, stricter controls, and specialized training. Conversely, low-risk areas receive proportional, less intensive oversight.
Deploying standard compliance templates and policies across all subsidiaries without adjusting for local regulatory differences is incorrect because using un-tailored templates fails to account for the unique operational and geographical risks of the subsidiaries, which is the opposite of a risk-based approach.
Mandating identical internal control procedures and daily auditing requirements for all departments, regardless of their operational functions, is incorrect because applying identical controls across all business units ignores the risk profiles of different departments, such as finance and sales versus internal facilities management, leading to operational bottlenecks in low-risk areas and insufficient controls in high-risk areas.
Suspending formal risk assessments to allocate all budget resources directly to general employee awareness training is incorrect because risk assessments are the very foundation of a risk-based compliance program; you cannot build a risk-based model if you avoid risk assessments.