
Which of the following best describes the primary purpose of establishing a formal Compliance Management System (CMS) within an enterprise?
Select an answer to reveal the explanation.
Short Explanation
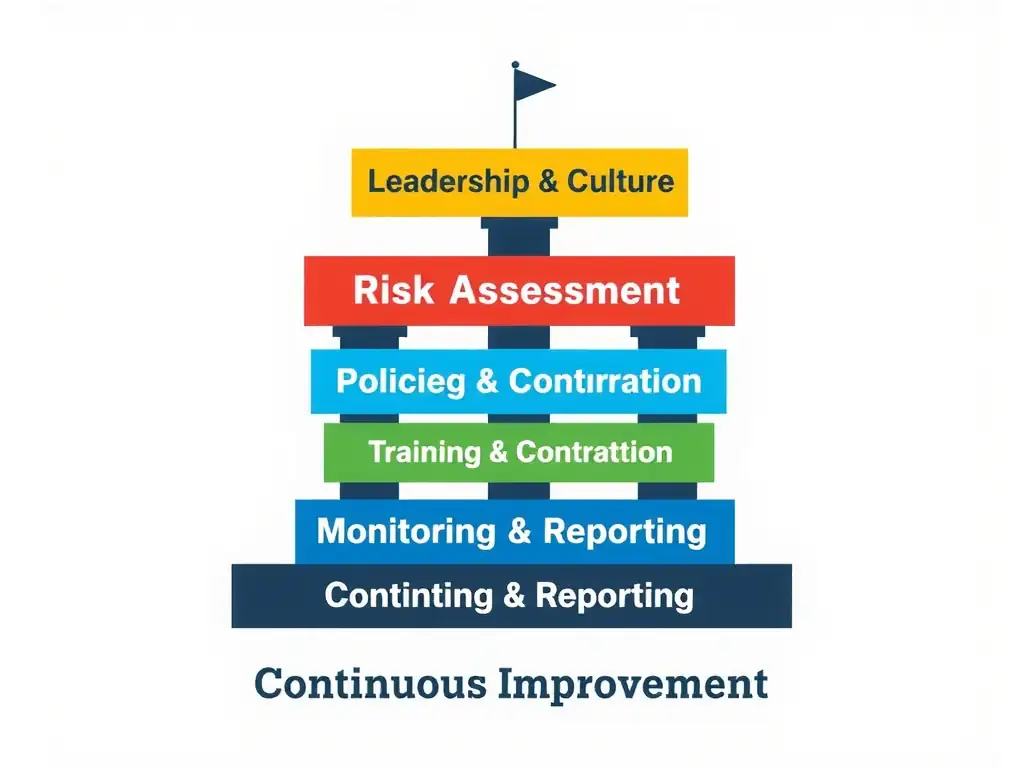
Think of a CMS as your blueprint for staying compliant. It gives you a structured way to spot and manage regulatory risks before they blow up, and it proves regulators your program actually works. It doesn't replace people or turn compliance into a sales tool.
Full Explanation
The correct answer is the option describing a structured framework to identify and manage non-compliance risks while demonstrating effectiveness. The Compliance Management System (CMS) is an integrated framework of policies, procedures, controls, training, monitoring, and corrective actions designed to ensure an organization complies with applicable laws, regulations, and internal standards. According to standards such as ISO 37301, a CMS must be structured, repeatable, and tailored to the organization's risks. Its ultimate objective is to provide a systematic approach to identifying compliance risks, implementing controls to prevent violations, detecting failures early, and demonstrating the program's overall effectiveness to board members, auditors, and external regulators.
The option about automating and replacing human decision-making in daily business transactions is incorrect because a CMS is designed to manage regulatory risks and ethical behavior, not to automate all general operational decisions, which still require executive and human judgment. The option about optimizing sales pipelines and managing customer relationship databases is incorrect because managing sales pipelines and customer relationships is the role of Customer Relationship Management (CRM) systems and sales management, not a compliance system. The option about eliminating the operational requirement for a dedicated compliance officer is incorrect because a CMS does not replace a compliance officer; in fact, a dedicated, empowered compliance officer is a critical component required to oversee and manage the CMS itself.
Ultimately, a well-implemented CMS serves as an organization's primary defense during regulatory audits or investigations, showcasing a proactive commitment to compliance.