
When establishing an organizational compliance framework, how should a compliance officer design the risk assessment process to ensure its long-term viability and effectiveness?
Select an answer to reveal the explanation.
Short Explanation
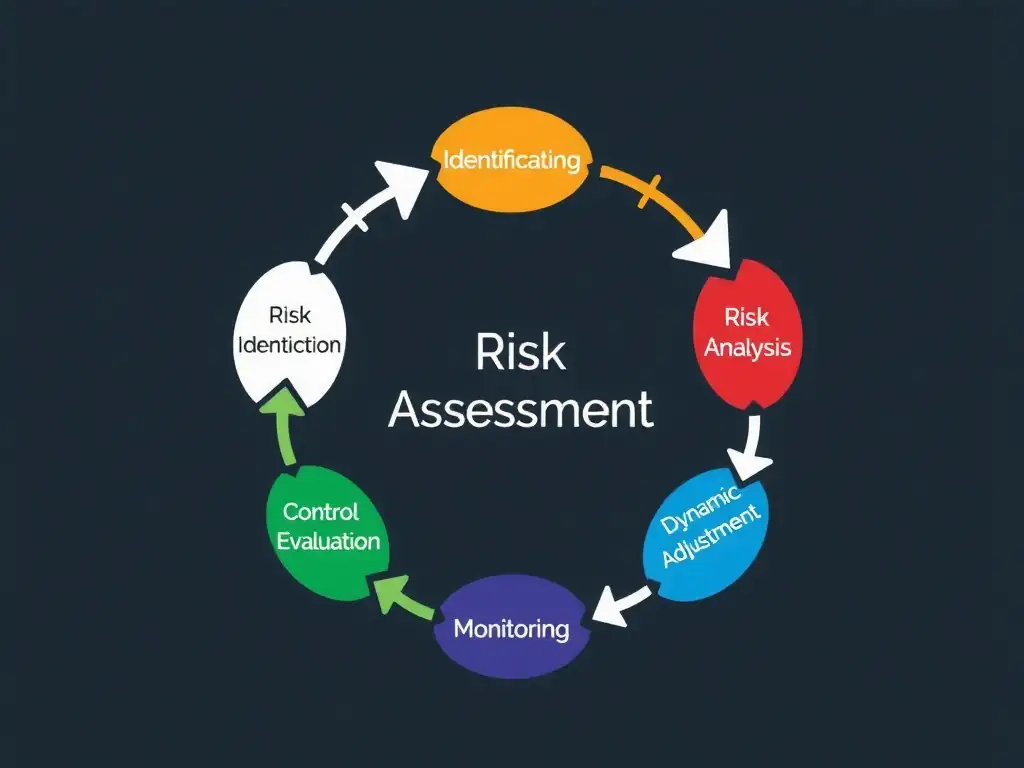
Think of risk assessment like the GPS on your car dashboard: if you update the map once and then drive for years, you'll get lost because roads, rules, and threats keep changing. You've got to keep evaluating and adapting so the compliance program stays alive. Don't make the rookie mistake of only watching financial risks or handing the whole job to outside auditors who don't know your day-to-day operations.
Full Explanation
The risk evaluation that is continuous and dynamically adapts to changes within the company and its external environment is the right design for long-term viability and effectiveness because risk assessment is not a static document or a one-time event; it is a foundational, continuous process. Ethics and compliance standards, including the ISO 37301 compliance management systems standard and the U.S. Department of Justice guidelines, emphasize that risk assessments must be updated regularly to reflect changes in an organization's size, operational structure, geographic footprint, and regulatory environment. Static risk assessment quickly becomes obsolete as mergers and acquisitions, new product launches, structural shifts, or geopolitical developments introduce entirely new risk vectors.
The static, one-time baseline audit during the initial launch phase of the compliance program is incorrect because treating risk assessment as a static, one-time exercise fails to capture new, evolving risks that emerge after the initial program design. This creates a false sense of security and leaves the organization blind to new regulatory requirements.
The approach that focuses the assessment scope exclusively on direct financial and accounting controls is incorrect because restricting the scope of risk assessment to financial and accounting controls ignores crucial non-financial compliance risks. Effective compliance programs must cover areas such as anti-bribery and corruption, data privacy, environmental regulations, health and safety, and trade sanctions.
The approach that outsources the entire process to external auditors to maintain absolute organizational independence is incorrect because while external consultants and auditors can provide valuable support and objectivity, the internal compliance function and business leaders must actively own and participate in the risk assessment. Internal teams possess the operational knowledge required to identify hidden compliance issues and cultivate a strong compliance culture.
Ultimately, a dynamic and continuous risk assessment process allows compliance teams to allocate resources efficiently, preempt emerging compliance threats, and demonstrate the effectiveness of the program to external regulators.