
When establishing a robust risk assessment framework within an international organization, which characteristic is absolutely critical to ensure its long-term viability and effectiveness?
Select an answer to reveal the explanation.
Short Explanation
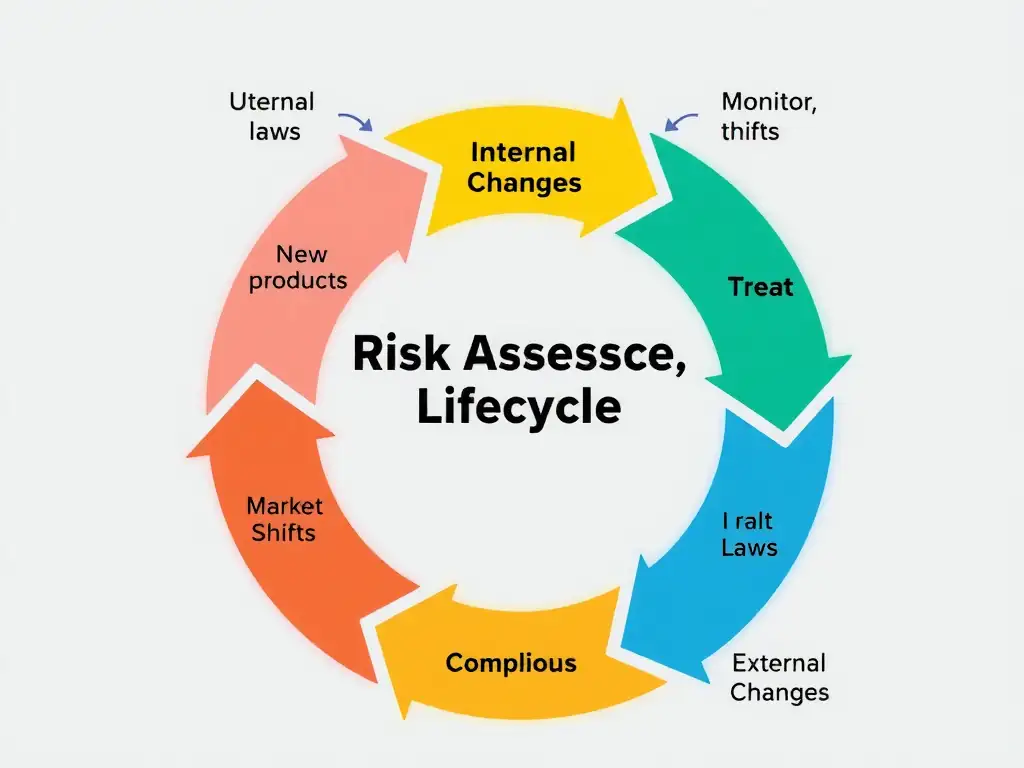
Here's the deal: a risk assessment can't be a one-and-done binder report. You've got to keep it alive, updating it as operations, regulations, and threats change. That continuous, iterative cycle is what keeps the framework viable.
Full Explanation
In compliance and risk management, an effective risk assessment must be a continuous and dynamic process rather than a static, one-time event. Organizations operate in highly fluid environments where internal variables—such as expansion into new markets, launching new products, or changing personnel—and external variables—such as new legislation, geopolitical shifts, or emerging security threats—constantly evolve. A static assessment quickly becomes obsolete, leaving the organization exposed to undetected vulnerabilities.
The correct characteristic is the evaluation being a continuous, iterative cycle that actively adapts to internal operational changes and shifting external regulatory landscapes. This alignment is supported by major compliance frameworks, including the COSO Enterprise Risk Management framework and guidelines from the U.S. Department of Justice, which emphasize that risk assessments must be updated periodically and dynamically to respond to change.
The approach requiring assessment to be performed exclusively by third-party auditors is incorrect because, while external audits provide valuable independent verification, relying exclusively on them prevents the internal compliance team from developing the deep, day-to-day operational understanding needed to manage risks proactively.
The approach requiring risk profiling to remain static to preserve baseline comparisons is incorrect because a rigid, static template fails to capture emerging risks. Baseline comparisons are useful, but they should not come at the expense of ignoring new, critical risk factors.
The approach restricting the scope strictly to direct financial and balance-sheet liabilities is incorrect because limiting the scope to financial liabilities ignores regulatory, operational, reputational, and strategic risks, which can often be far more damaging to an organization's survival.