
When establishing an organizational compliance committee, why is it critical to recruit members from a wide variety of operational and business departments rather than staffing it solely with compliance or legal specialists?
Select an answer to reveal the explanation.
Short Explanation
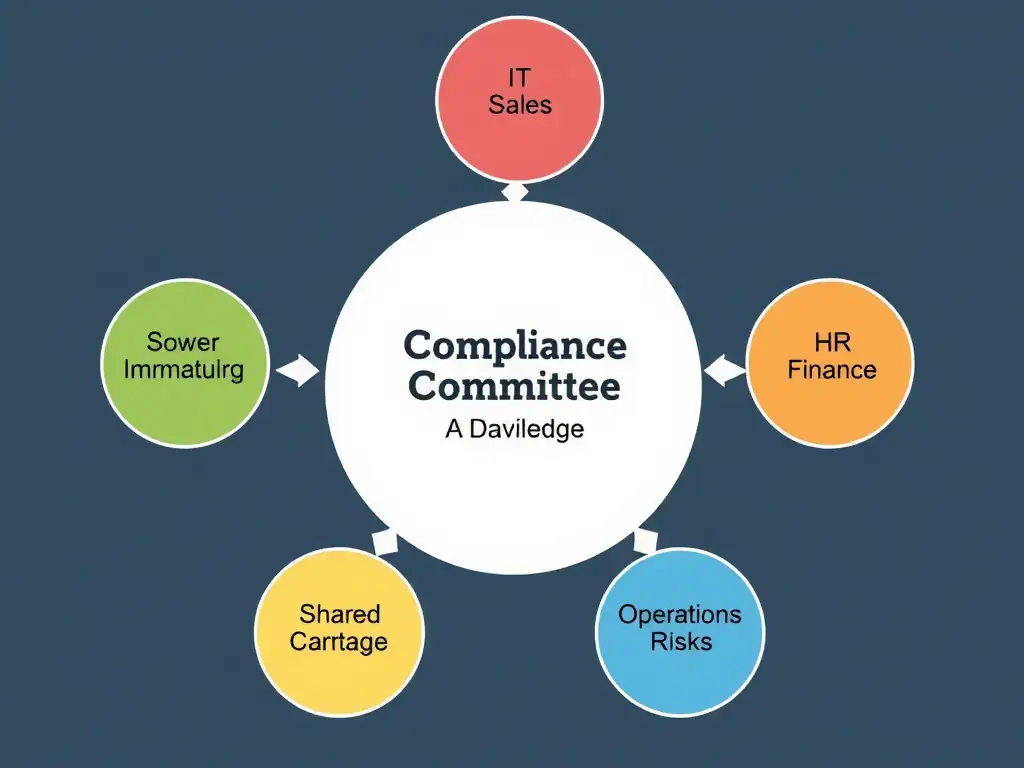
If you only put lawyers and compliance specialists on the committee, you'll miss how risks actually show up on the sales floor, in technology teams, or in operations. Cross-functional members build buy-in and give you fuller picture of operational risk. You still need leadership and consistent corporate rules, not departments making up their own rules.
Full Explanation
The compliance committee should be composed of members from different business units (such as human resources, sales, information technology, finance, operations, and legal) to promote compliance program ownership throughout the organization. This cross-functional composition brings diverse perspectives on operational risks from multiple business areas that a centralized compliance department might not fully appreciate or detect. Representatives from each business unit understand the granular workflows, vulnerabilities, and cultural dynamics of their respective areas, enabling the committee to design more practical and effective controls. Furthermore, when department leaders participate in compliance oversight, they act as ambassadors, facilitating better adoption of compliance policies within their teams. The idea of creating a buffer that shields the primary compliance department from direct legal liability during external regulatory audits is incorrect because establishing a compliance committee does not shield the compliance department or chief compliance officer from regulatory accountability. In fact, regulatory bodies like the Department of Justice look at the committee's activity to verify that the compliance function has sufficient executive support and oversight. The idea of completely replacing the role of a chief compliance officer by decentralizing all compliance decision-making to business unit managers is incorrect because a compliance committee does not replace the compliance officer. The Federal Sentencing Guidelines for Organizations require that specific high-level personnel, such as a chief compliance officer, be given overall responsibility for the compliance and ethics program. The idea of granting individual business units the authority to bypass corporate policies when local market conditions require it is incorrect because the committee's purpose is to align operational units with the organization's standards, not to allow individual departments to bypass corporate policies or create their own arbitrary rules.