
What is the primary purpose of establishing a comprehensive Third-Party Risk Management (TPRM) framework within an organization?
Select an answer to reveal the explanation.
Short Explanation
You can outsource work, but you can't outsource responsibility. A TPRM framework helps you identify, assess, and mitigate the regulatory, operational, and reputational risks that external partners bring, so you can collaborate safely without letting vendor failures become your headline.
Full Explanation
Third-Party Risk Management (TPRM) is a critical discipline that focuses on analyzing and controlling the risks that arise when organizations partner with external entities. Modern enterprises rely heavily on third parties, such as vendors, cloud service providers, distributors, and agents, to execute core business functions. While outsourcing offers operational efficiencies, it also exposes organizations to significant legal, financial, operational, cybersecurity, and reputational risks.
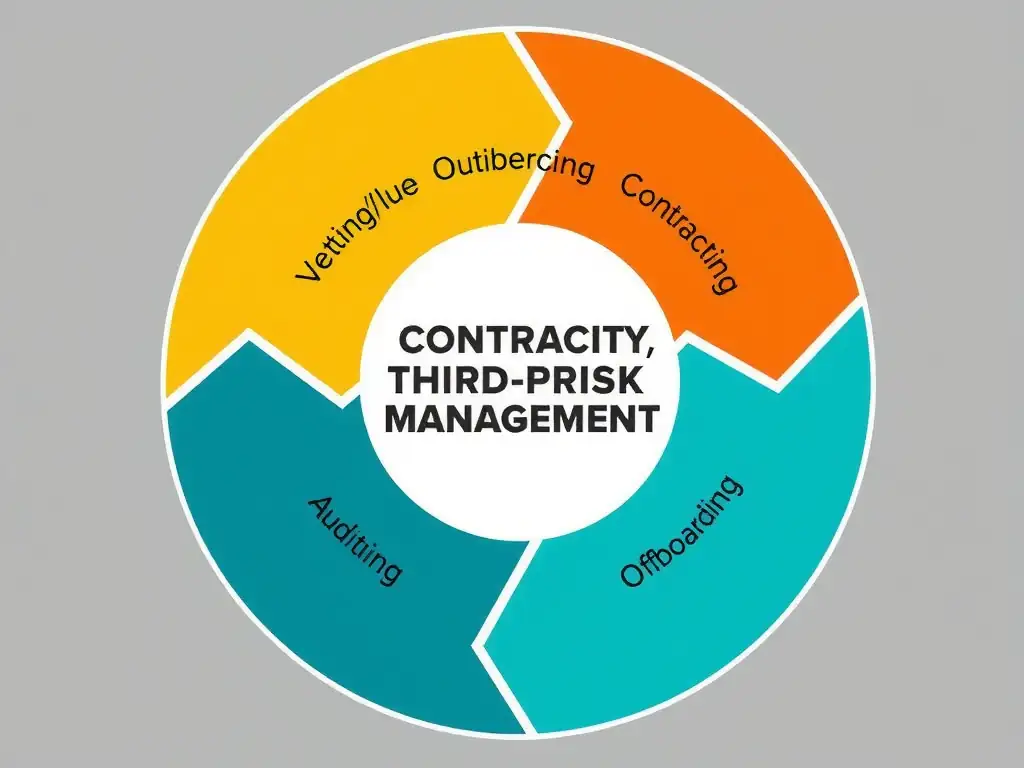
The correct approach is the one that says TPRM systematically identifies, assesses, and mitigates the regulatory, operational, and reputational risks of external partners, because a TPRM framework provides a structured methodology throughout the lifecycle of a third-party relationship. This lifecycle includes pre-contractual due diligence, risk-tiering, contract negotiation (incorporating compliance clauses), continuous monitoring, and eventual offboarding. By doing this, organizations protect themselves from liabilities arising from data breaches, supply chain disruptions, corruption, or labor violations committed by their partners.
The accounts payable automation approach is incorrect because ensuring timely payments to vendors is an operational accounting and accounts payable function, not the objective of a risk management framework. The internal payroll and benefits administration approach is incorrect because internal payroll administration is managed by Human Resources and Finance departments, focusing on employees rather than external third-party risks. The eliminate-all-commercial-transactions approach is incorrect because avoiding all external suppliers is commercially unfeasible for modern businesses. TPRM is designed to enable safe, compliant engagement with third parties, not to eliminate outsourcing entirely.
Regulators look closely at an organization's TPRM program to determine if the compliance culture extends beyond its corporate walls.