
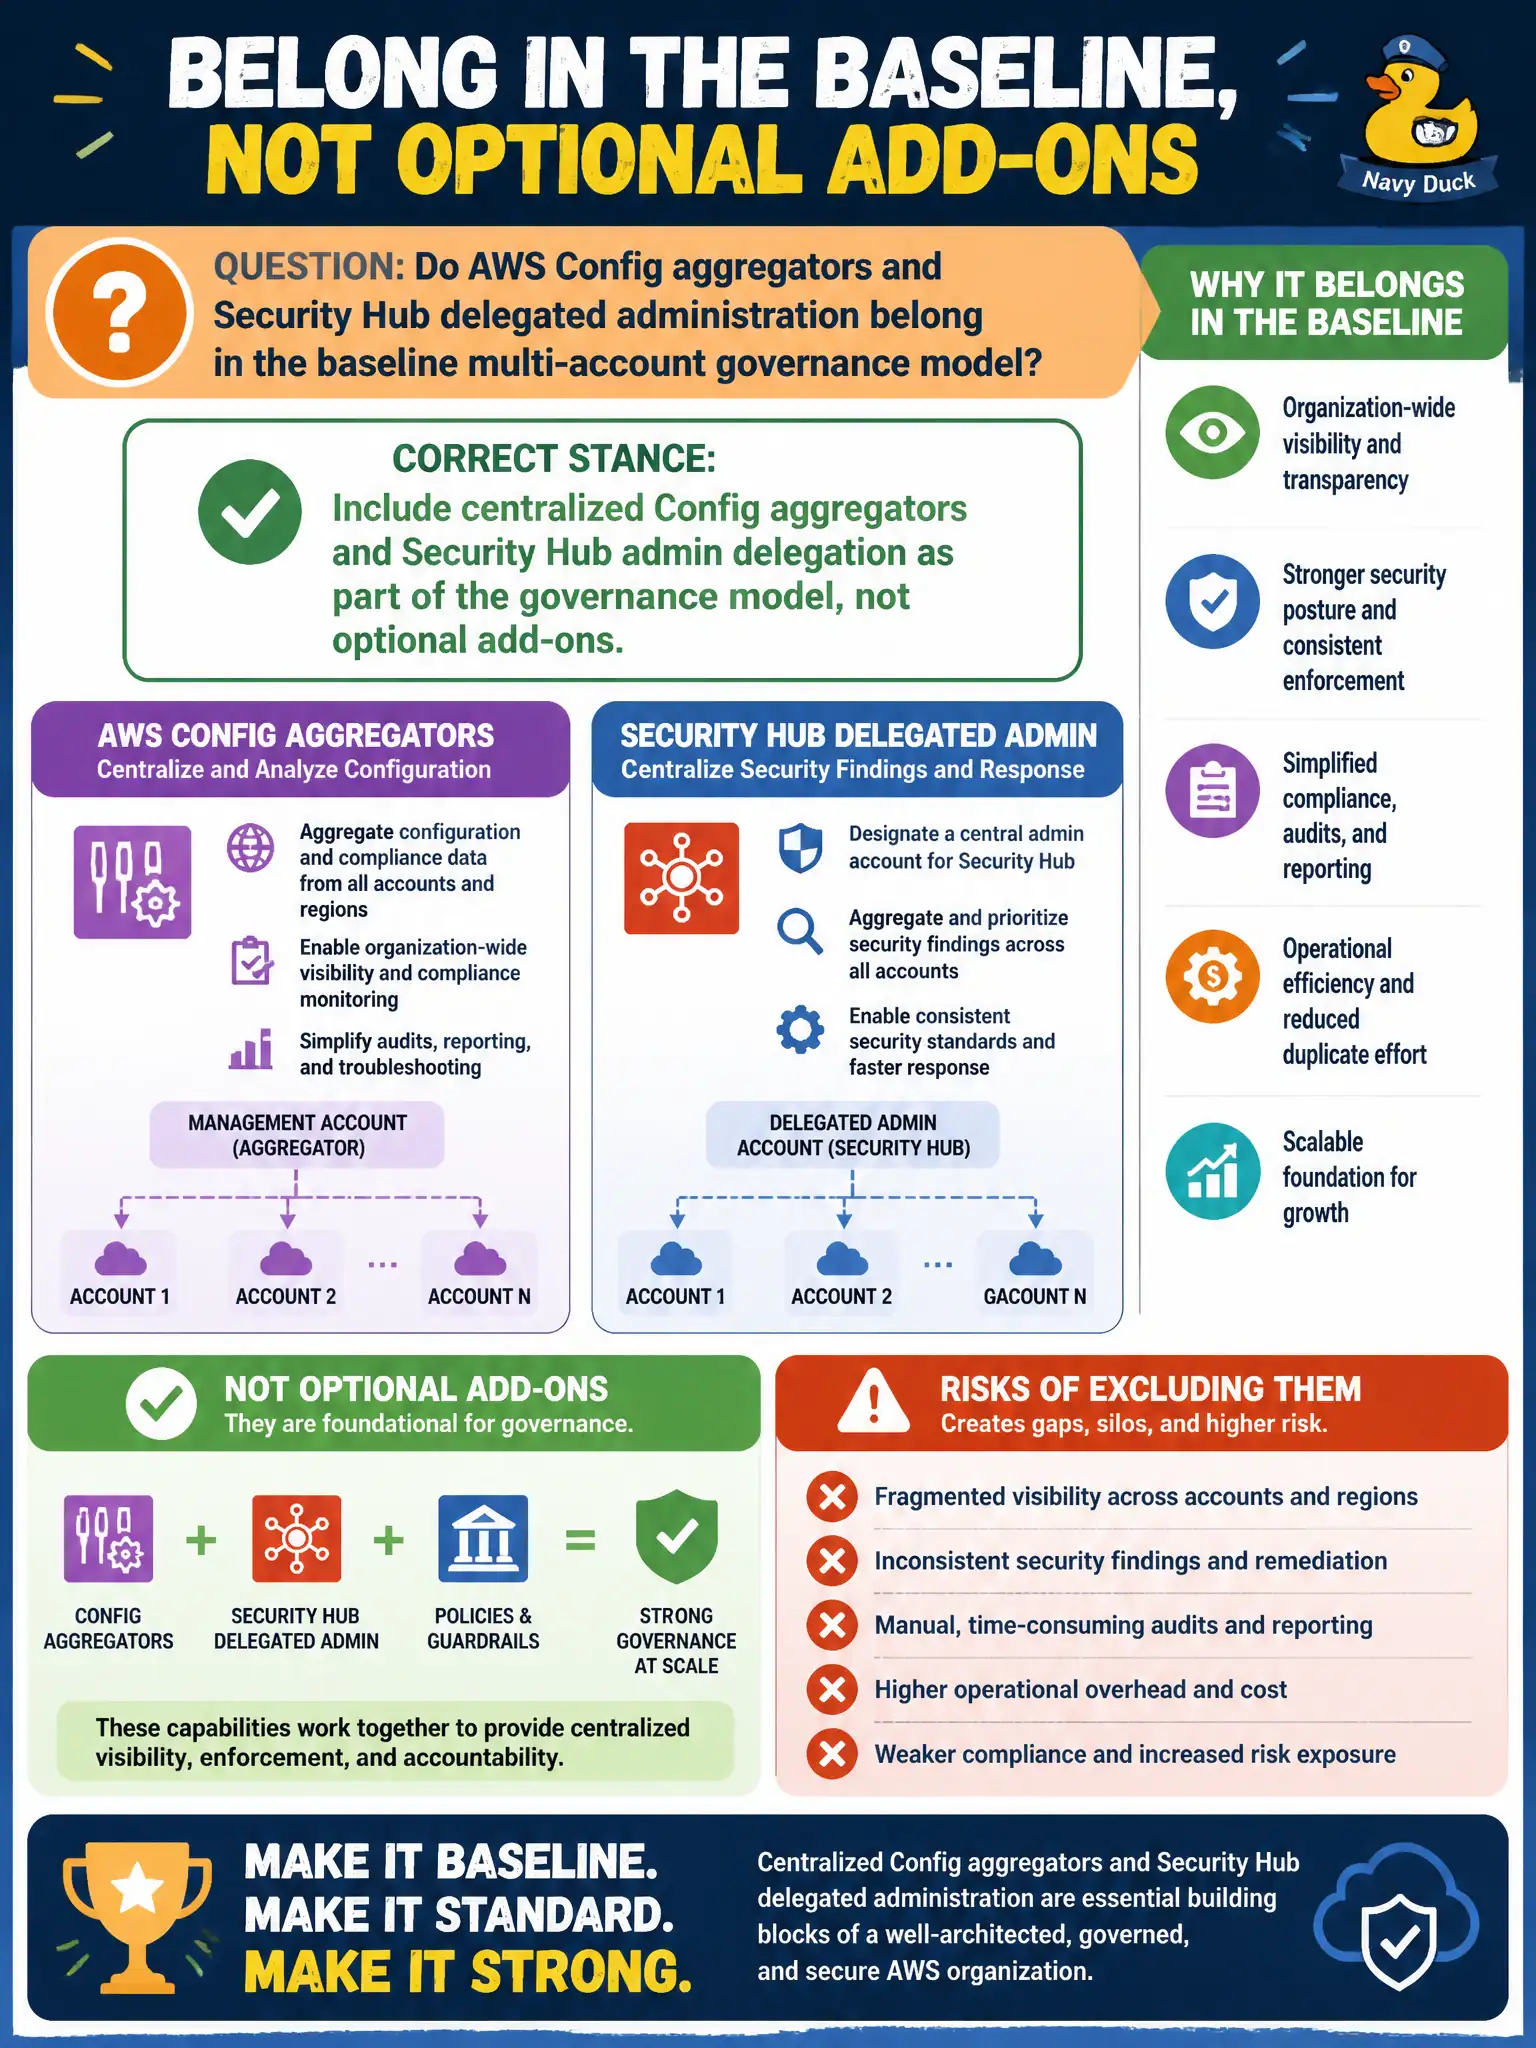
Leadership asks whether AWS Config aggregators and Security Hub delegated administration belong in the baseline multi-account governance model. What is the correct stance?
Select an answer to reveal the explanation.
Short Explanation
Citywide building codes are not a weekend craft project. Config aggregation and Security Hub delegated admin belong in the landing-zone blueprint from day one, not as an afterthought when something burns down.
Full Explanation
AWS Config aggregators and Security Hub delegated administration belong in the baseline multi-account governance model, not as optional hobby tools after the first major breach. Centralized Config aggregation provides organization-wide configuration inventory and compliance rules, while Security Hub delegated admin normalizes and routes security findings. Municipal landing zones that omit these capabilities lack continuous detective coverage across parks, courts, and utilities accounts.
Treating them as optional hobby tools after the first major breach accepts preventable blind spots until damage occurs. Enabling Config only in sandboxes and never aggregating across accounts leaves production without continuous configuration visibility. Running Security Hub in one developer laptop account without organization delegation fails multi-account administration and durability.
Exam caveat: Config aggregators plus Security Hub org admin are expected pieces of a governed multi-account security baseline on SAP-C02. Operational check: enable a Config aggregator in the security or audit account, designate Security Hub delegated admin, auto-enable members, and verify a misconfiguration and a GuardDuty finding both appear centrally within expected latency.