
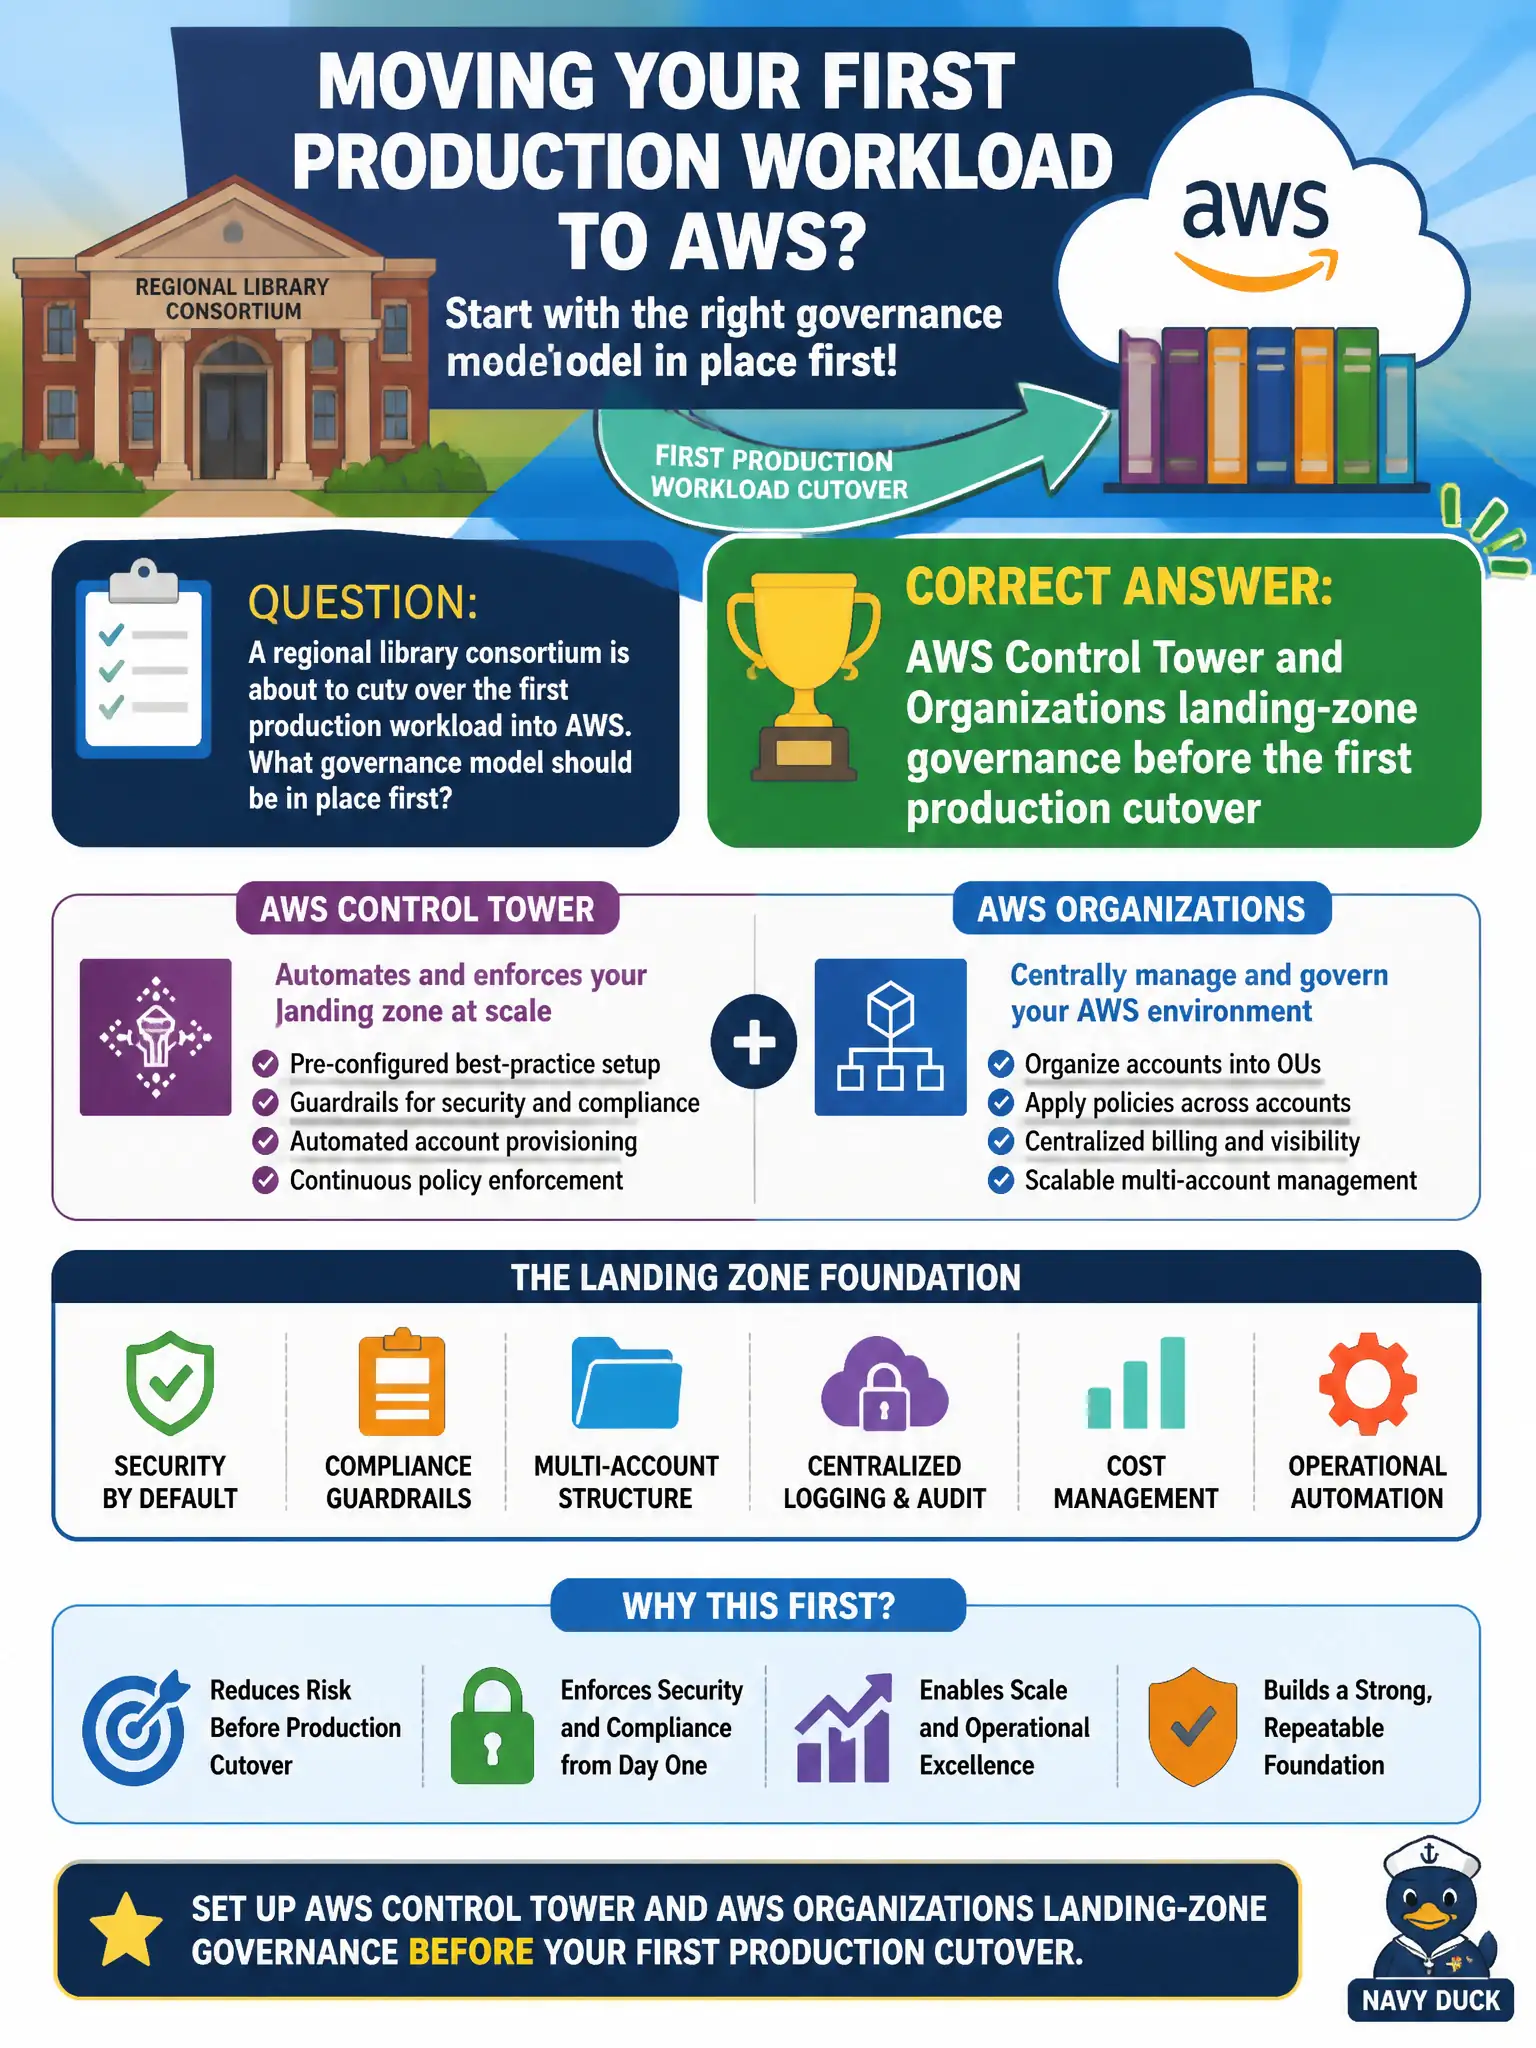
A regional library consortium is about to cut over the first production workload into AWS. What governance model should be in place first?
Select an answer to reveal the explanation.
Short Explanation
Don't move into a new campus without keys, fences, and address numbers. Stand up Control Tower and Organizations landing zones before the first production cutover—not after ten apps are already camping in one messy account.
Full Explanation
A regional library consortium about to cut over the first production workload into AWS needs landing-zone governance first. Put AWS Control Tower and Organizations landing-zone governance in place before the first production cutover so accounts, guardrails, and logging exist when citizen-facing library systems go live. A single shared developer IAM user reused across every account with AdministratorAccess fails least privilege and destroys accountability. Waiting for no multi-account structure until at least ten apps are live in one unmanaged account fails by accumulating ungoverned blast radius. Ad-hoc console clicks in each account without Organizations or preventive guardrails fail scalable municipal governance. Exam caveat: Control Tower/Organizations precede production cutover; do not grow wild in one account first. Operational check: deploy Control Tower, create OU structure for libraries and shared services, enable SCPs and CloudTrail/Config baselines, provision the first workload account from the landing zone, then cut over with logging already on. Document the decision in the municipal architecture decision record and re-verify controls after the first production wave so auditors see continuous improvement, not one-time tribal knowledge.