
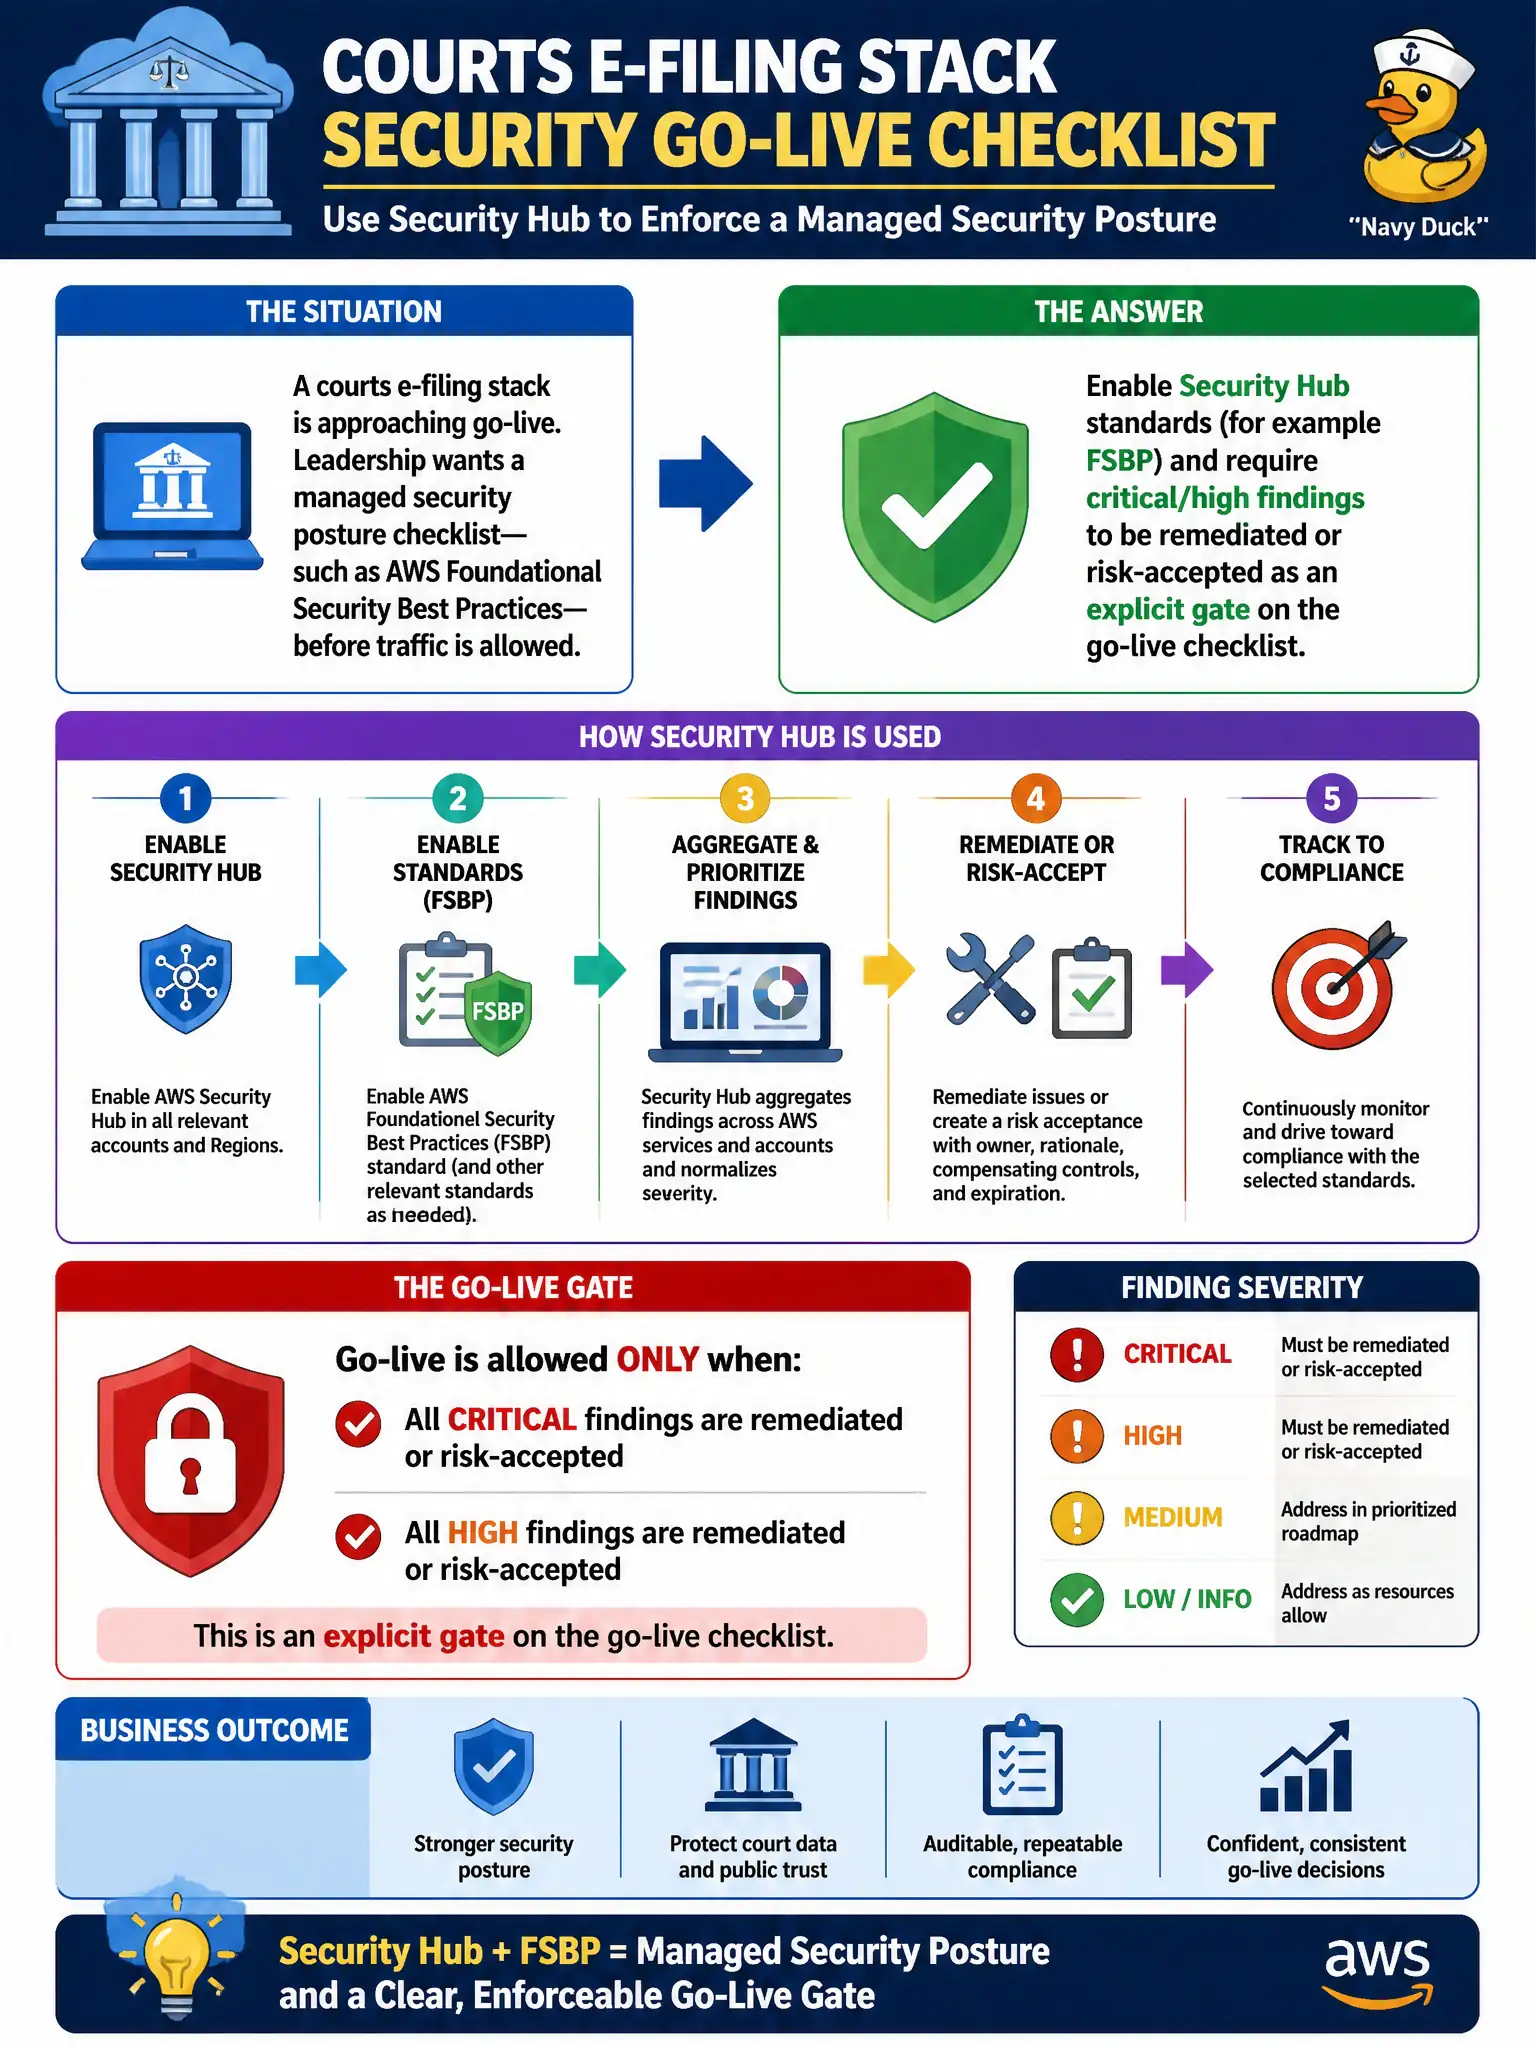
A courts e-filing stack is approaching go-live. Leadership wants a managed security posture checklist—such as AWS Foundational Security Best Practices—before traffic is allowed. How should Security Hub be used?
Select an answer to reveal the explanation.
Short Explanation
Security Hub FSBP is the pre-flight checklist for the courthouse launch—fix the red items or formally accept the risk before you open the doors. Skipping the checklist is hoping turbulence stays friendly.
Full Explanation
Courts e-filing approaching go-live needs a managed security posture checklist before traffic is allowed. Enabling Security Hub standards such as AWS Foundational Security Best Practices and requiring critical and high findings to be remediated or formally risk-accepted before go-live turns Security Hub into a launch gate rather than a passive dashboard. Ignoring Security Hub until months after launch delays visibility into baseline misconfigurations. Treating Security Hub as optional decoration without remediation ownership fails leadership's checklist intent. Disabling Security Hub standards to hide failing controls manufactures green status without reducing risk. Exam caveat: Security Hub aggregates findings—teams still need owners, SLAs, and exceptions tracked in the city's risk register. Operational check: enable FSBP in the e-filing accounts, export critical/high findings, remediate or risk-accept each with tickets, and re-run the standard until launch criteria pass. In municipal cloud governance, record the owners, success metrics, and rollback or restore contacts beside this technical choice so the next incident, budget review, or audit does not rediscover the decision from scratch under time pressure.