
Baseline IAM roles must be pushed to every account under the city’s OUs from the management plane. Which IaC pattern best fits org-scale deployment?
Select an answer to reveal the explanation.
Short Explanation
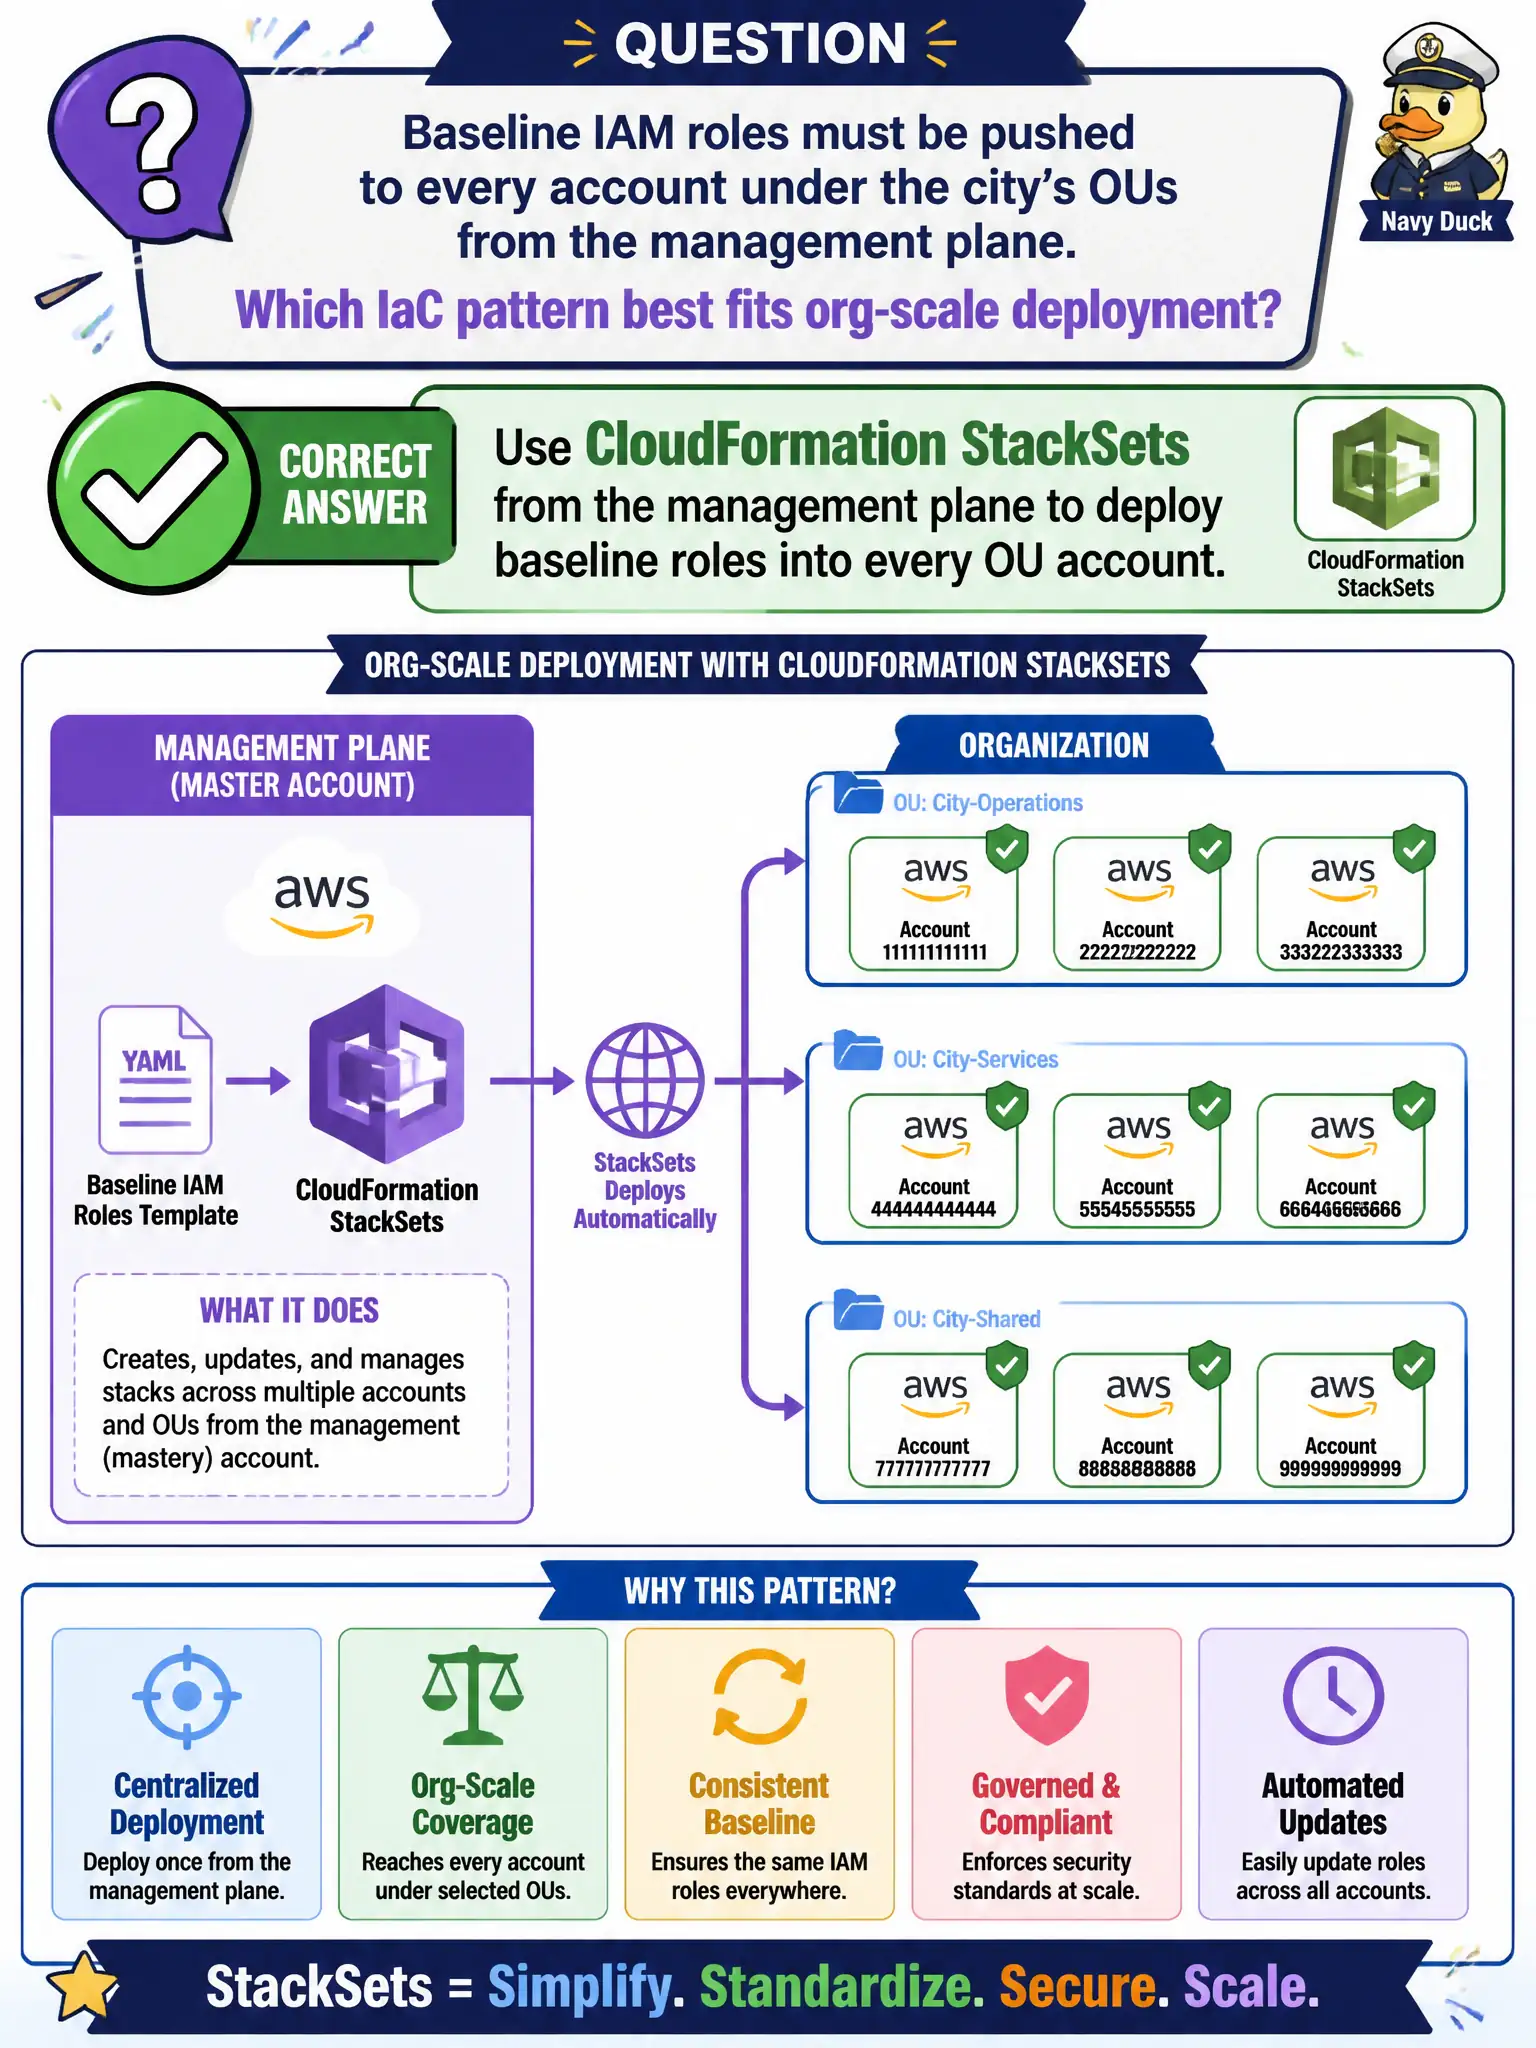
One management-plane lever, many accounts. StackSets push the same baseline roles into every OU member so nobody is waiting on a ZIP file and a rainy-day click-through.
Full Explanation
Baseline IAM roles must be stamped consistently into every account under the city's organizational units from the management plane. CloudFormation StackSets are designed for that pattern: define the role templates once and deploy or update them across OU-targeted accounts with centralized operations and compliance visibility for auditors. Emailing a template ZIP for each owner to click through manually fails scale, creates version skew, and leaves incomplete coverage when someone forgets during a busy permitting season. Creating roles only in the management account does not give member-account workloads the local principals they need and concentrates privilege incorrectly for day-to-day civic apps. Undocumented console clicks tracked in a spreadsheet cannot prove what exists in each account during an audit. Exam caveat: StackSets still require the right Organizations trusted access and execution roles; without them, deployments silently skip accounts. Operational check: deploy a StackSet to a pilot OU, inventory IAM roles in a member account for the expected baseline, update the template and confirm drift-free rollout, and review StackSet operation failures for any account that missed the push.