
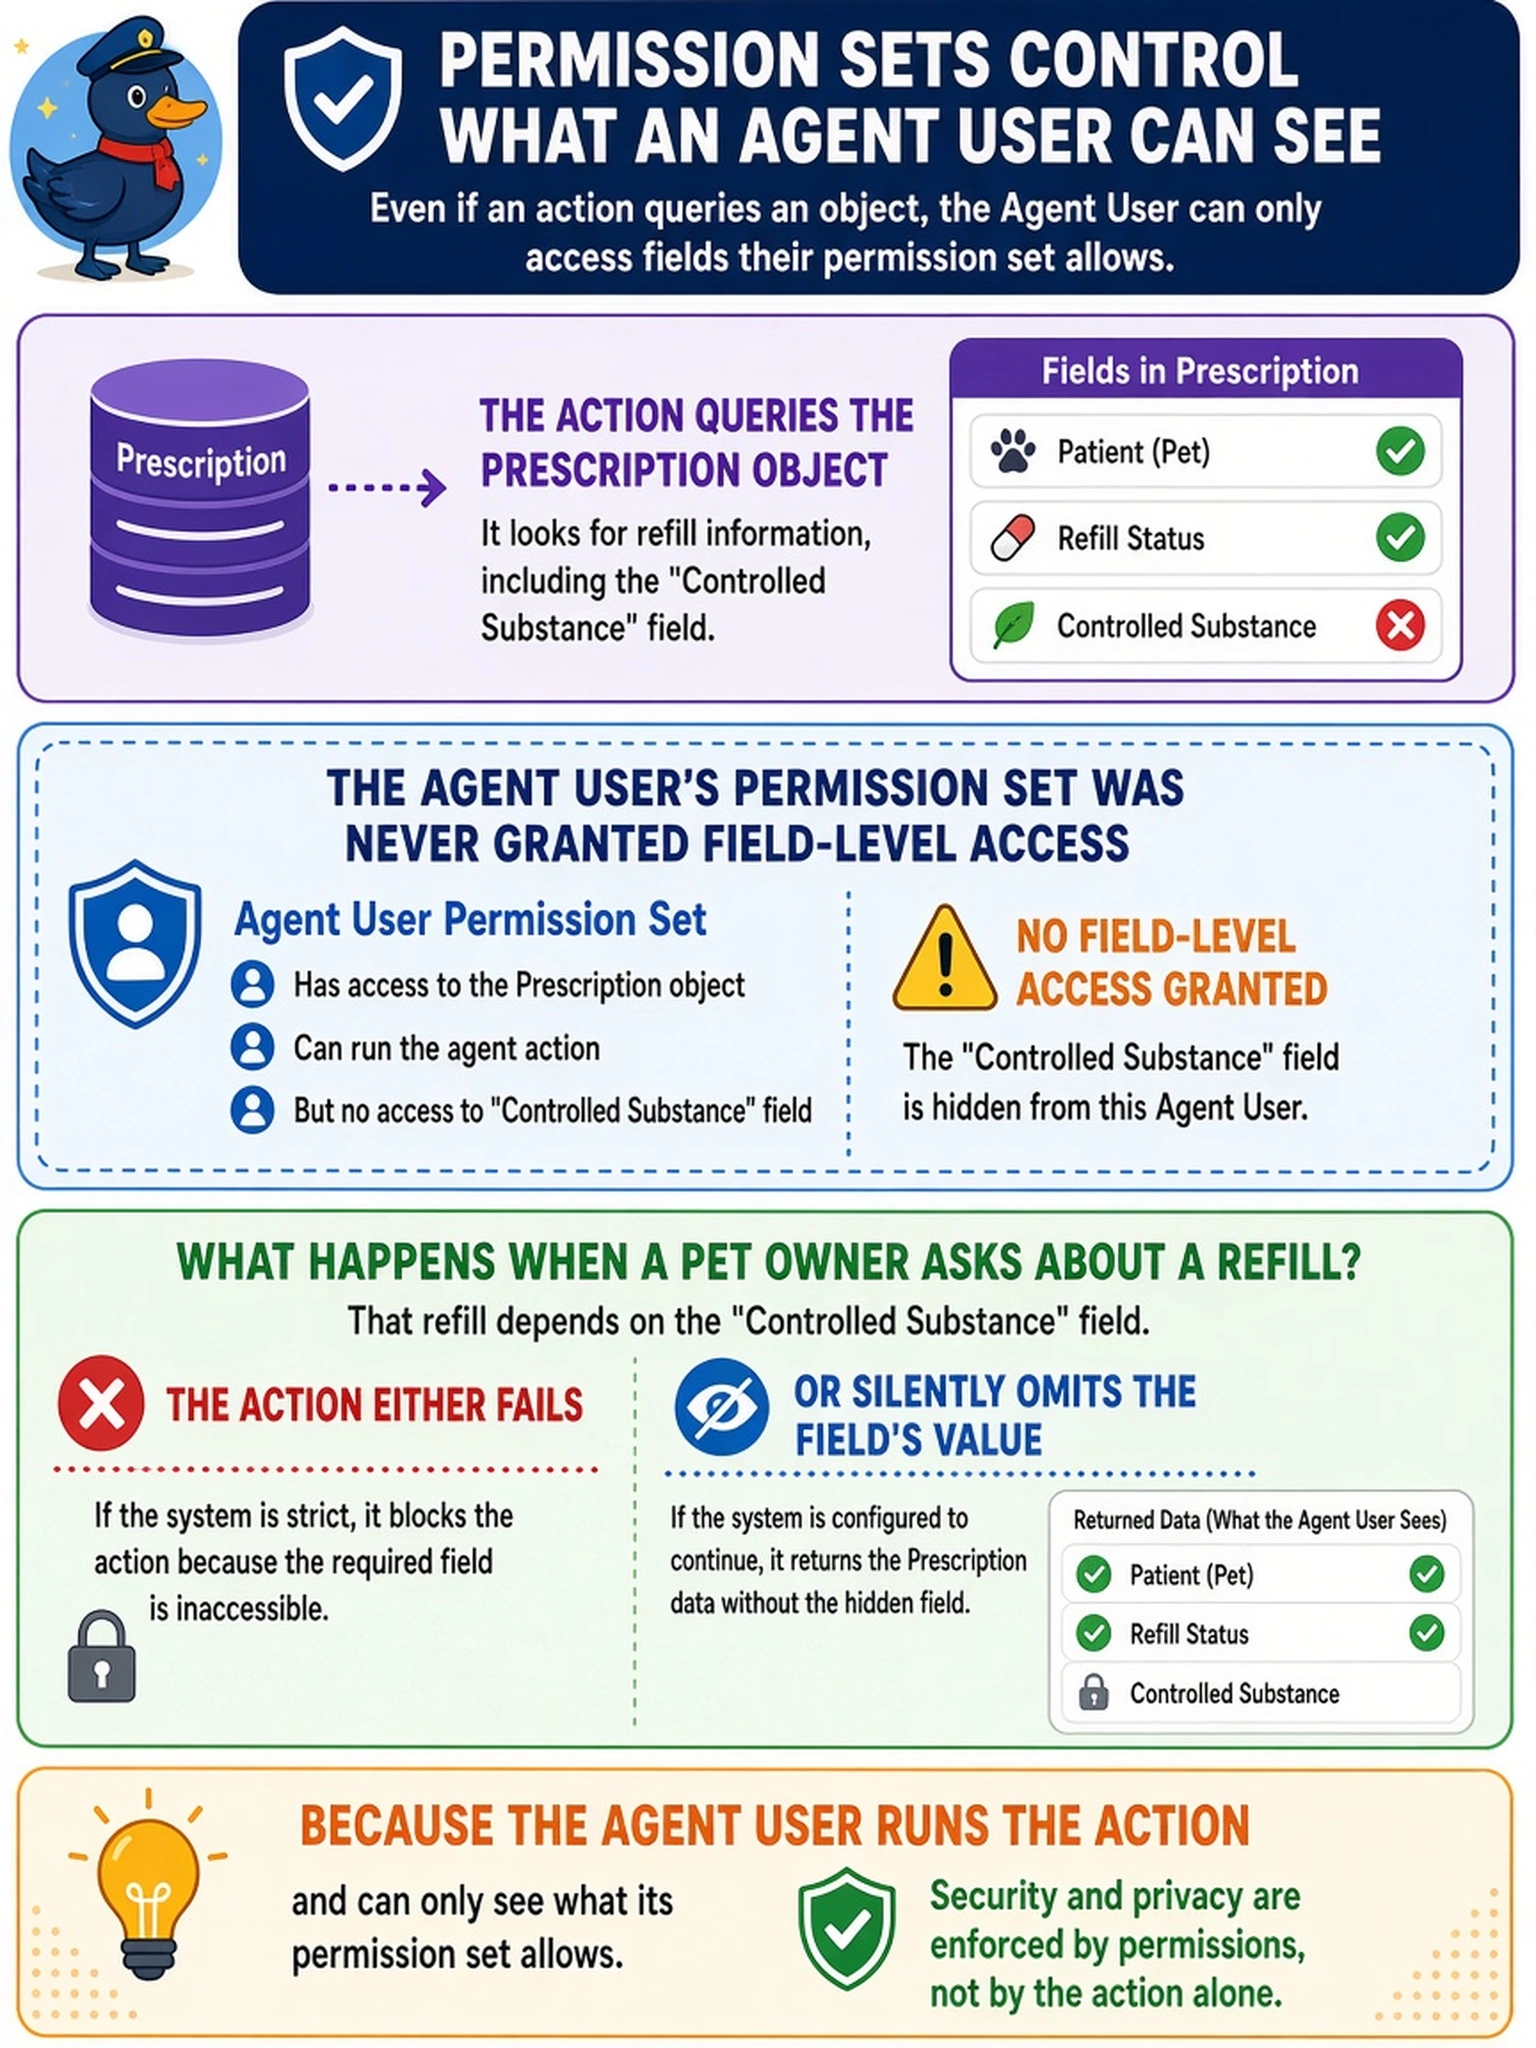
An agent action queries the Prescription object, but the Agent User's permission set was never granted field-level access to the "Controlled Substance" field. What is the most likely result when a pet owner asks about a refill that depends on that field?
Select an answer to reveal the explanation.
Short Explanation
The agent isn't secretly you, or the owner, or an admin, it's a user record of its own, and it can only see what its own badge lets it see. No badge access, no field, full stop.
Full Explanation
Every action an agent invokes runs in the security context of the Agent User, a real user record with its own profile and permission sets. If that permission set lacks field-level access to "Controlled Substance," the Agent User cannot see that field's value regardless of what the pet owner is asking, so the action fails outright or returns without that field depending on how the action is built, and the agent has no legitimate value to reason about or report. There is no automatic Trust Layer override for missing FLS; the Trust Layer's job is masking and toxicity detection on data that is already visible, not granting access that was never configured. There is no caching-based fallback to a previously viewed value; Salesforce security does not work by remembering what some other user once saw. The claim that agent actions bypass field-level security entirely is the dangerous myth this question is testing against: agent actions are ordinary automation running as a real user and are fully subject to FLS, object permissions, and sharing, exactly like any other integration user. The practical consequence specialists must internalise: a missing permission does not surface as a friendly error, it surfaces as data quietly not being there.