
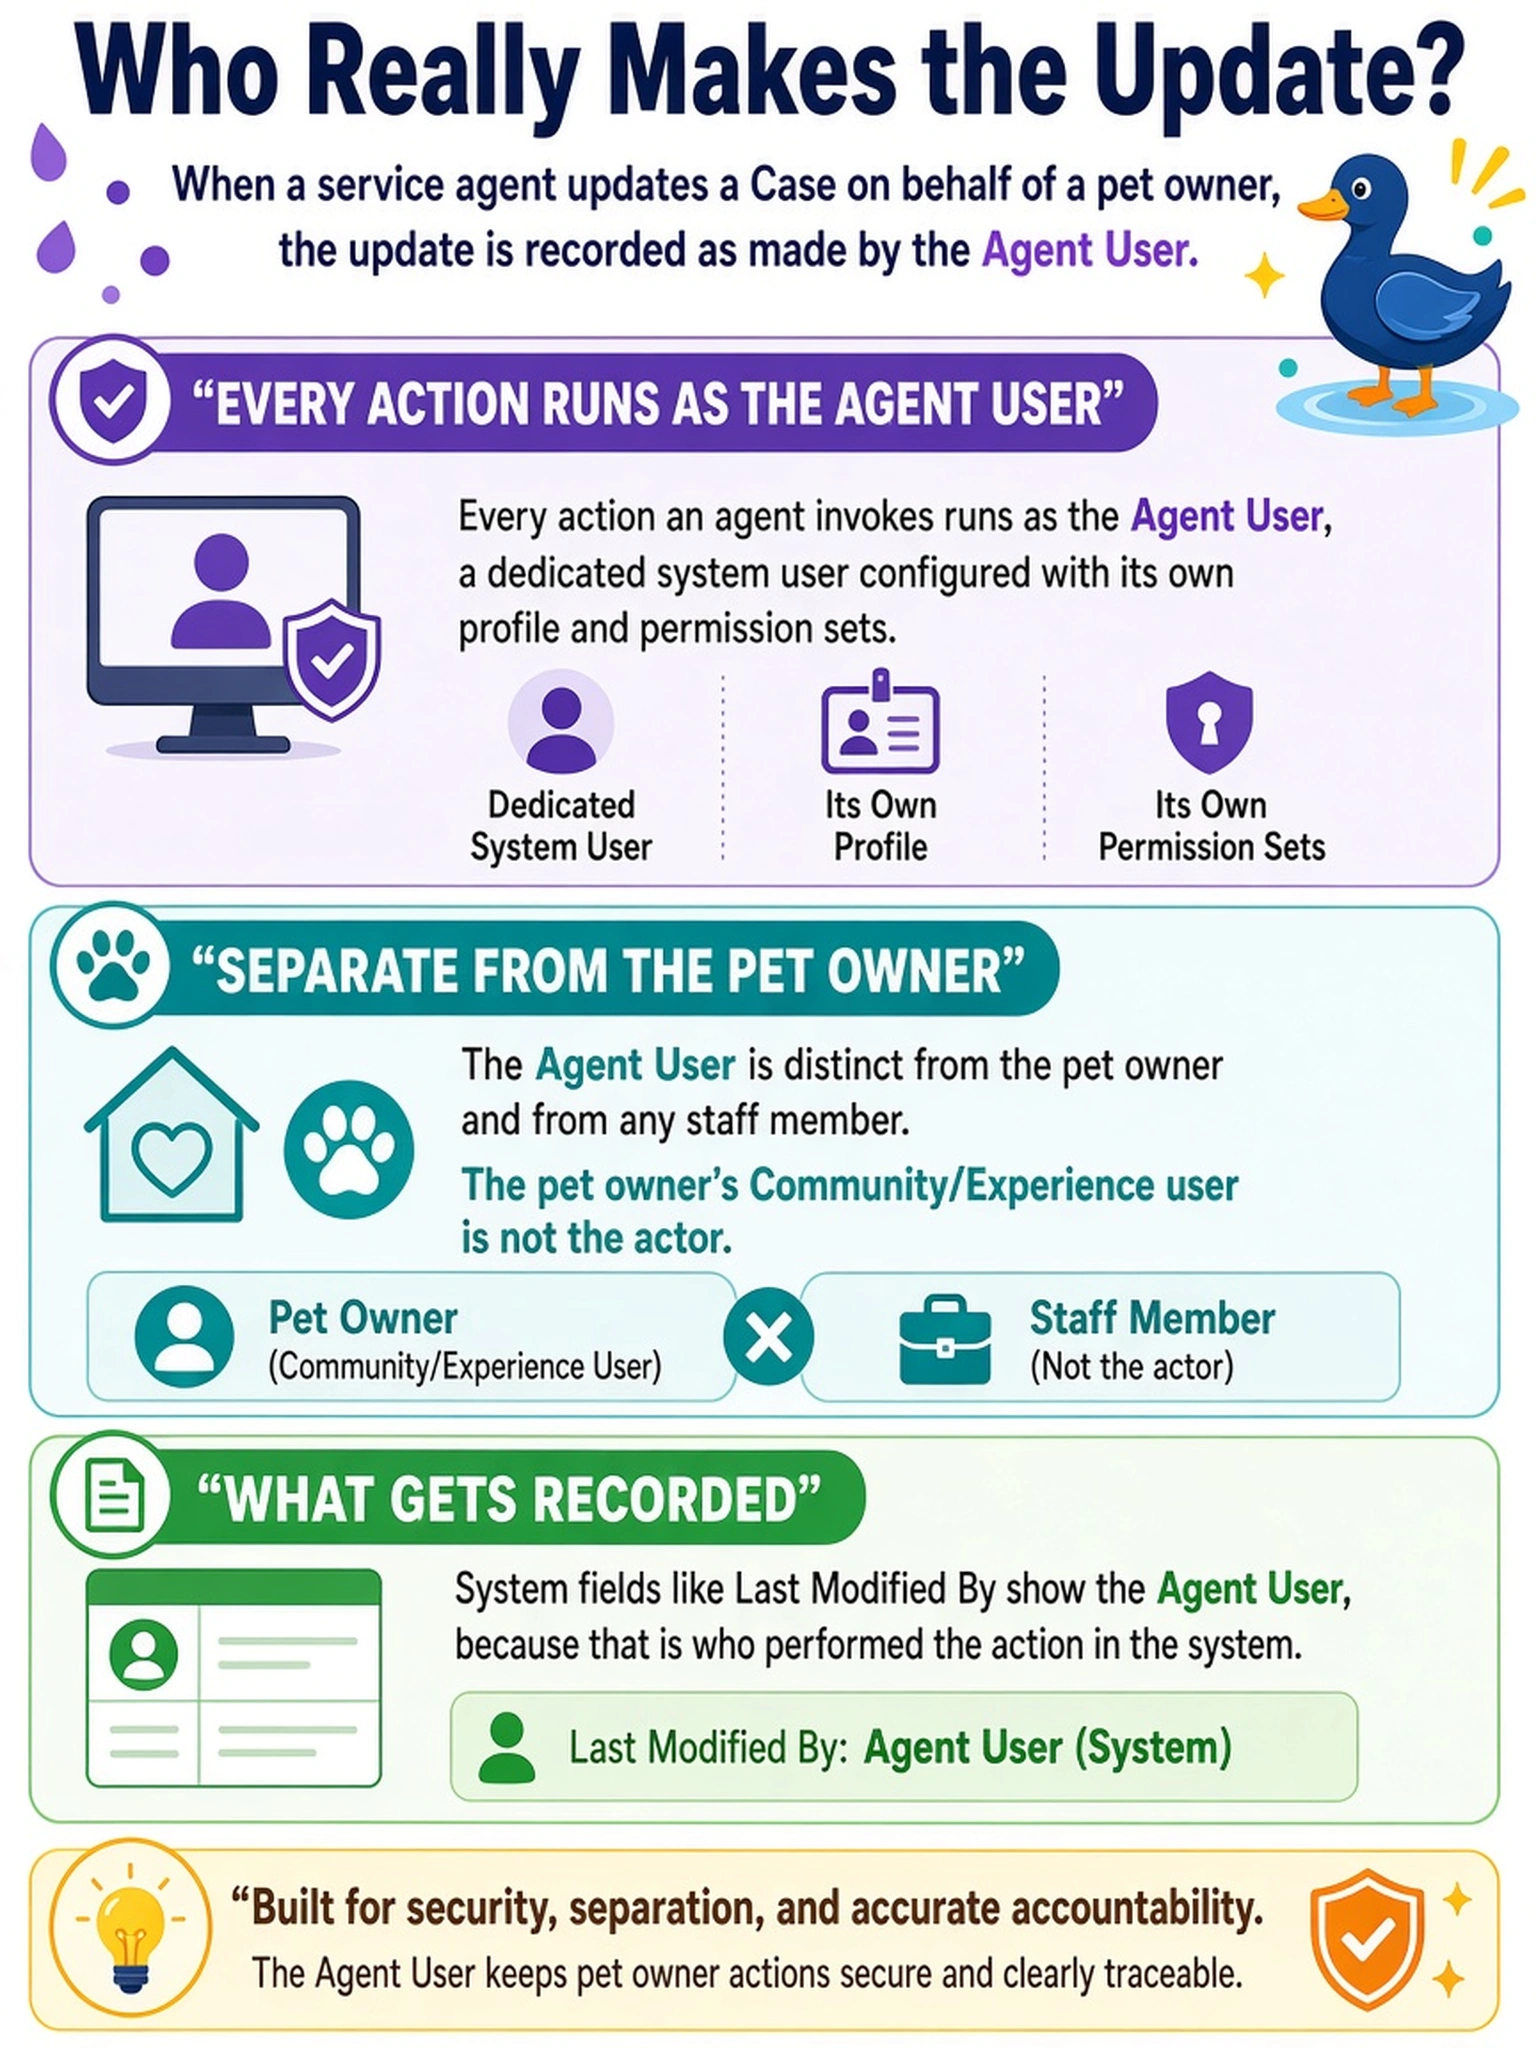
A new specialist assumes that when the service agent updates a Case on behalf of a pet owner, the update is recorded as having been made by that pet owner's Community/Experience user. Why is this assumption wrong?
Select an answer to reveal the explanation.
Short Explanation
The agent has its own name tag at the front desk. It isn't wearing the owner's badge or borrowing a vet's, it's got its own, and everything it touches gets stamped with that badge, not whoever happened to be chatting with it.
Full Explanation
Agentforce actions execute under a dedicated Agent User, a genuine user record created and licensed specifically for the agent, carrying its own profile and permission set assignments. This is what makes the security model auditable and controllable: administrators grant the Agent User exactly the object, field, and record access it needs, independent of whatever access the human on the other end of the conversation has. The pet owner's Experience Cloud login authenticates them to the portal and may establish who the conversation is about, but it does not become the acting user for record changes; conflating the two would mean an owner's limited portal permissions somehow expand to whatever the agent needs, which is backwards and insecure. Saying updates are unattributed is simply false; they are attributed to the Agent User like any other automated process, which is exactly why permission-set hygiene on that user matters so much. Attribution is also not channel-dependent; whether the conversation happens on the web, in the app, over email, or in Slack, the same Agent User performs the underlying action. The adjacent fact worth remembering: this is why over-provisioning the Agent User's permission set is dangerous, since it applies uniformly across every channel and every owner the agent talks to.