
A citizen permit portal sits behind an internet-facing Application Load Balancer. How should the architect place the application servers and security groups?
Select an answer to reveal the explanation.
Short Explanation
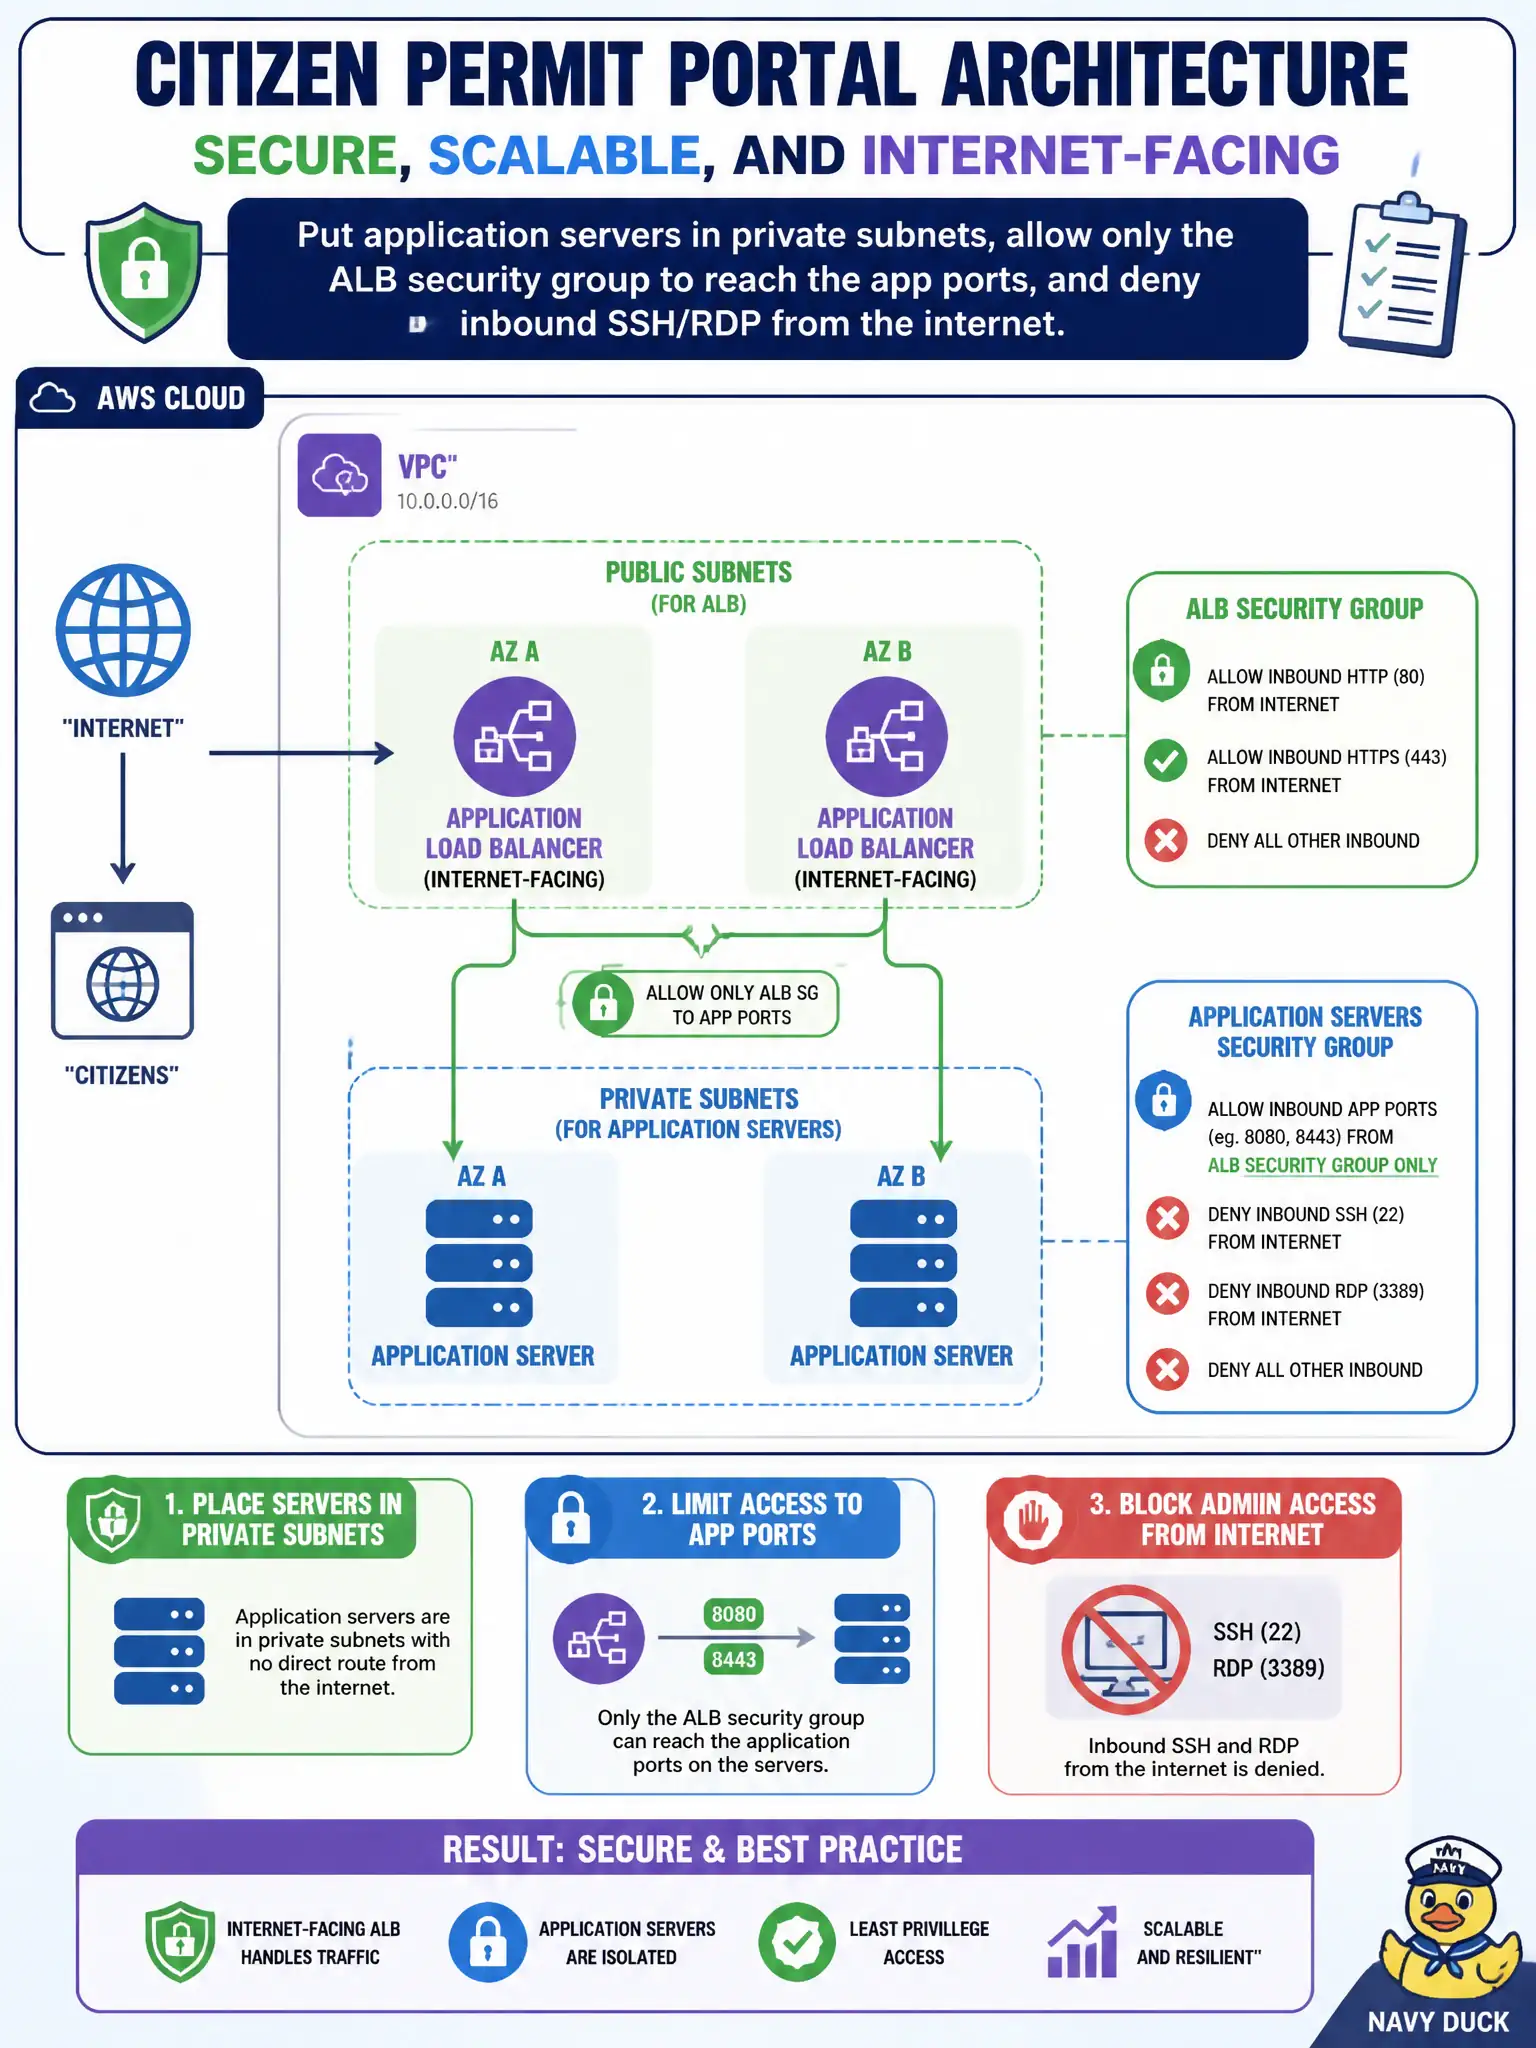
The ALB is the front desk; the clerks stay in the back office. App servers live in private subnets and only accept traffic from the ALB’s security group—no internet SSH or RDP on the apps. Wide-open public instances or EIP-per-server HTTPS are how you turn a portal into a target range.
Full Explanation
For a citizen permit portal behind an internet-facing Application Load Balancer, place application servers in private subnets, allow only the ALB security group to reach the application ports, and deny inbound SSH/RDP from the internet to those hosts. The ALB terminates citizen traffic in public subnets while the application tier remains unreachable except through the load balancer path—standard three-tier hardening for municipal public services.
Placing application servers in public subnets with security groups open to 0.0.0.0/0 on all ports fails because it exposes the compute tier directly and removes meaningful network least privilege. Attaching Elastic IPs and terminating HTTPS on every instance without a load balancer fails conceptually: it multiplies public attack surface, complicates certificate and scaling operations, and loses centralized health checks and routing. Allowing SSH from 0.0.0.0/0 on the ALB and forwarding that to private instances fails because load balancers are not a substitute for bastion/Session Manager controls, and internet-wide SSH on the front door is an invitation to brute force.
Exam caveat: private placement still requires controlled egress (NAT or endpoints), patch channels, and an admin path—privacy of the subnet is not the same as a complete operations design. Operational check: verify app security groups list only the ALB SG as source on app ports, confirm instances have no public IPs, probe that direct internet hits to app ports fail, and route administration through Session Manager or a hardened bastion with MFA.