
A parks department application in a private subnet must call Amazon S3 without sending traffic across the public internet. Which design combines private connectivity with secure access controls?
Select an answer to reveal the explanation.
Short Explanation
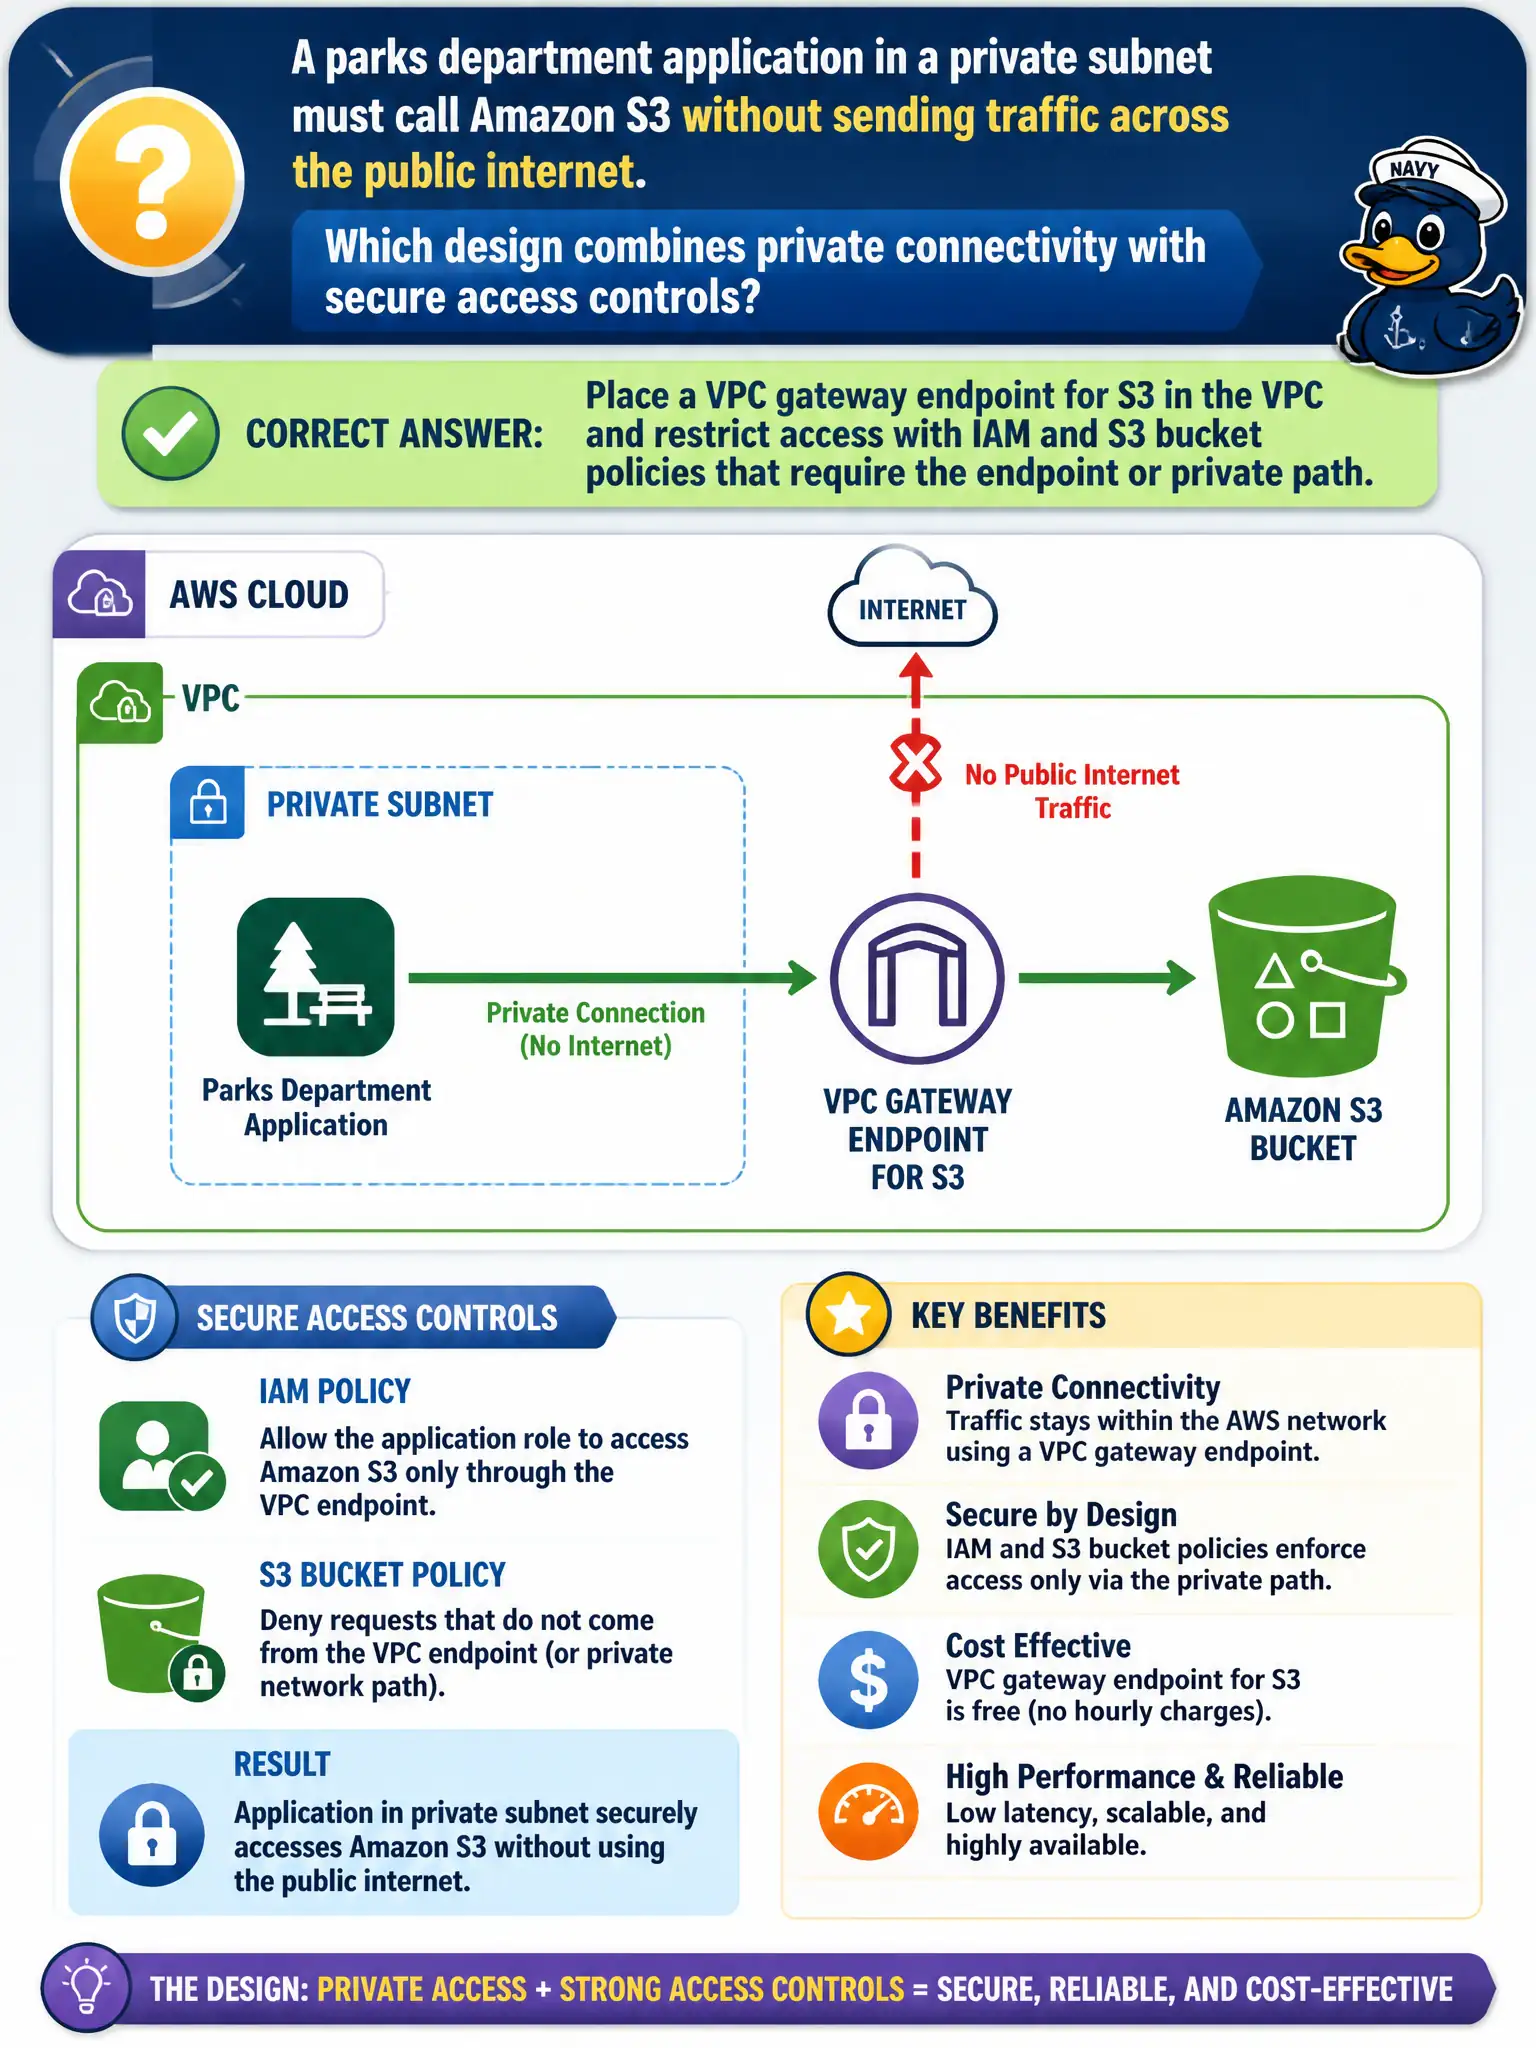
Private apps talking to S3 should use the building’s private hallway, not the street. A VPC gateway endpoint for S3 keeps traffic on the AWS network, and IAM plus bucket policies lock who may use that path. Public IPs, SSH tunnels, or anonymous puts are the opposite of private, least-privilege access.
Full Explanation
A parks department application in a private subnet should reach Amazon S3 through a VPC gateway endpoint for S3, with IAM and S3 bucket policies that restrict access to that private path (often conditioned on the VPC endpoint). Gateway endpoints keep S3 traffic on the AWS network without requiring a NAT or internet gateway hop for those requests, and policy conditions prevent the bucket from being used as an open side door—matching municipal requirements to keep operational data paths off the public internet when possible.
Assigning public IP addresses to every private-subnet instance so they can hit public S3 endpoints fails because it forces internet egress addressing and expands exposure contrary to the private-subnet design. Opening security group egress to 0.0.0.0/0 on port 22 and tunneling uploads over SSH fails conceptually: SSH is not an object-storage access pattern, and wide-open port 22 invites administrative compromise. Disabling all bucket policies and relying on anonymous PutObject fails because anonymous writes abandon authentication and allow anyone who can reach the bucket API to plant or overwrite objects.
Exam caveat: gateway endpoints are regional and S3-specific; they do not privately reach arbitrary HTTPS APIs—other AWS services typically need interface endpoints. Operational check: confirm the private subnet route table includes the S3 prefix list to the gateway endpoint, verify bucket policies deny non-endpoint access where required, test Put/Get from the app role only, and ensure NAT is not the unnoticed fallback for S3 traffic.