
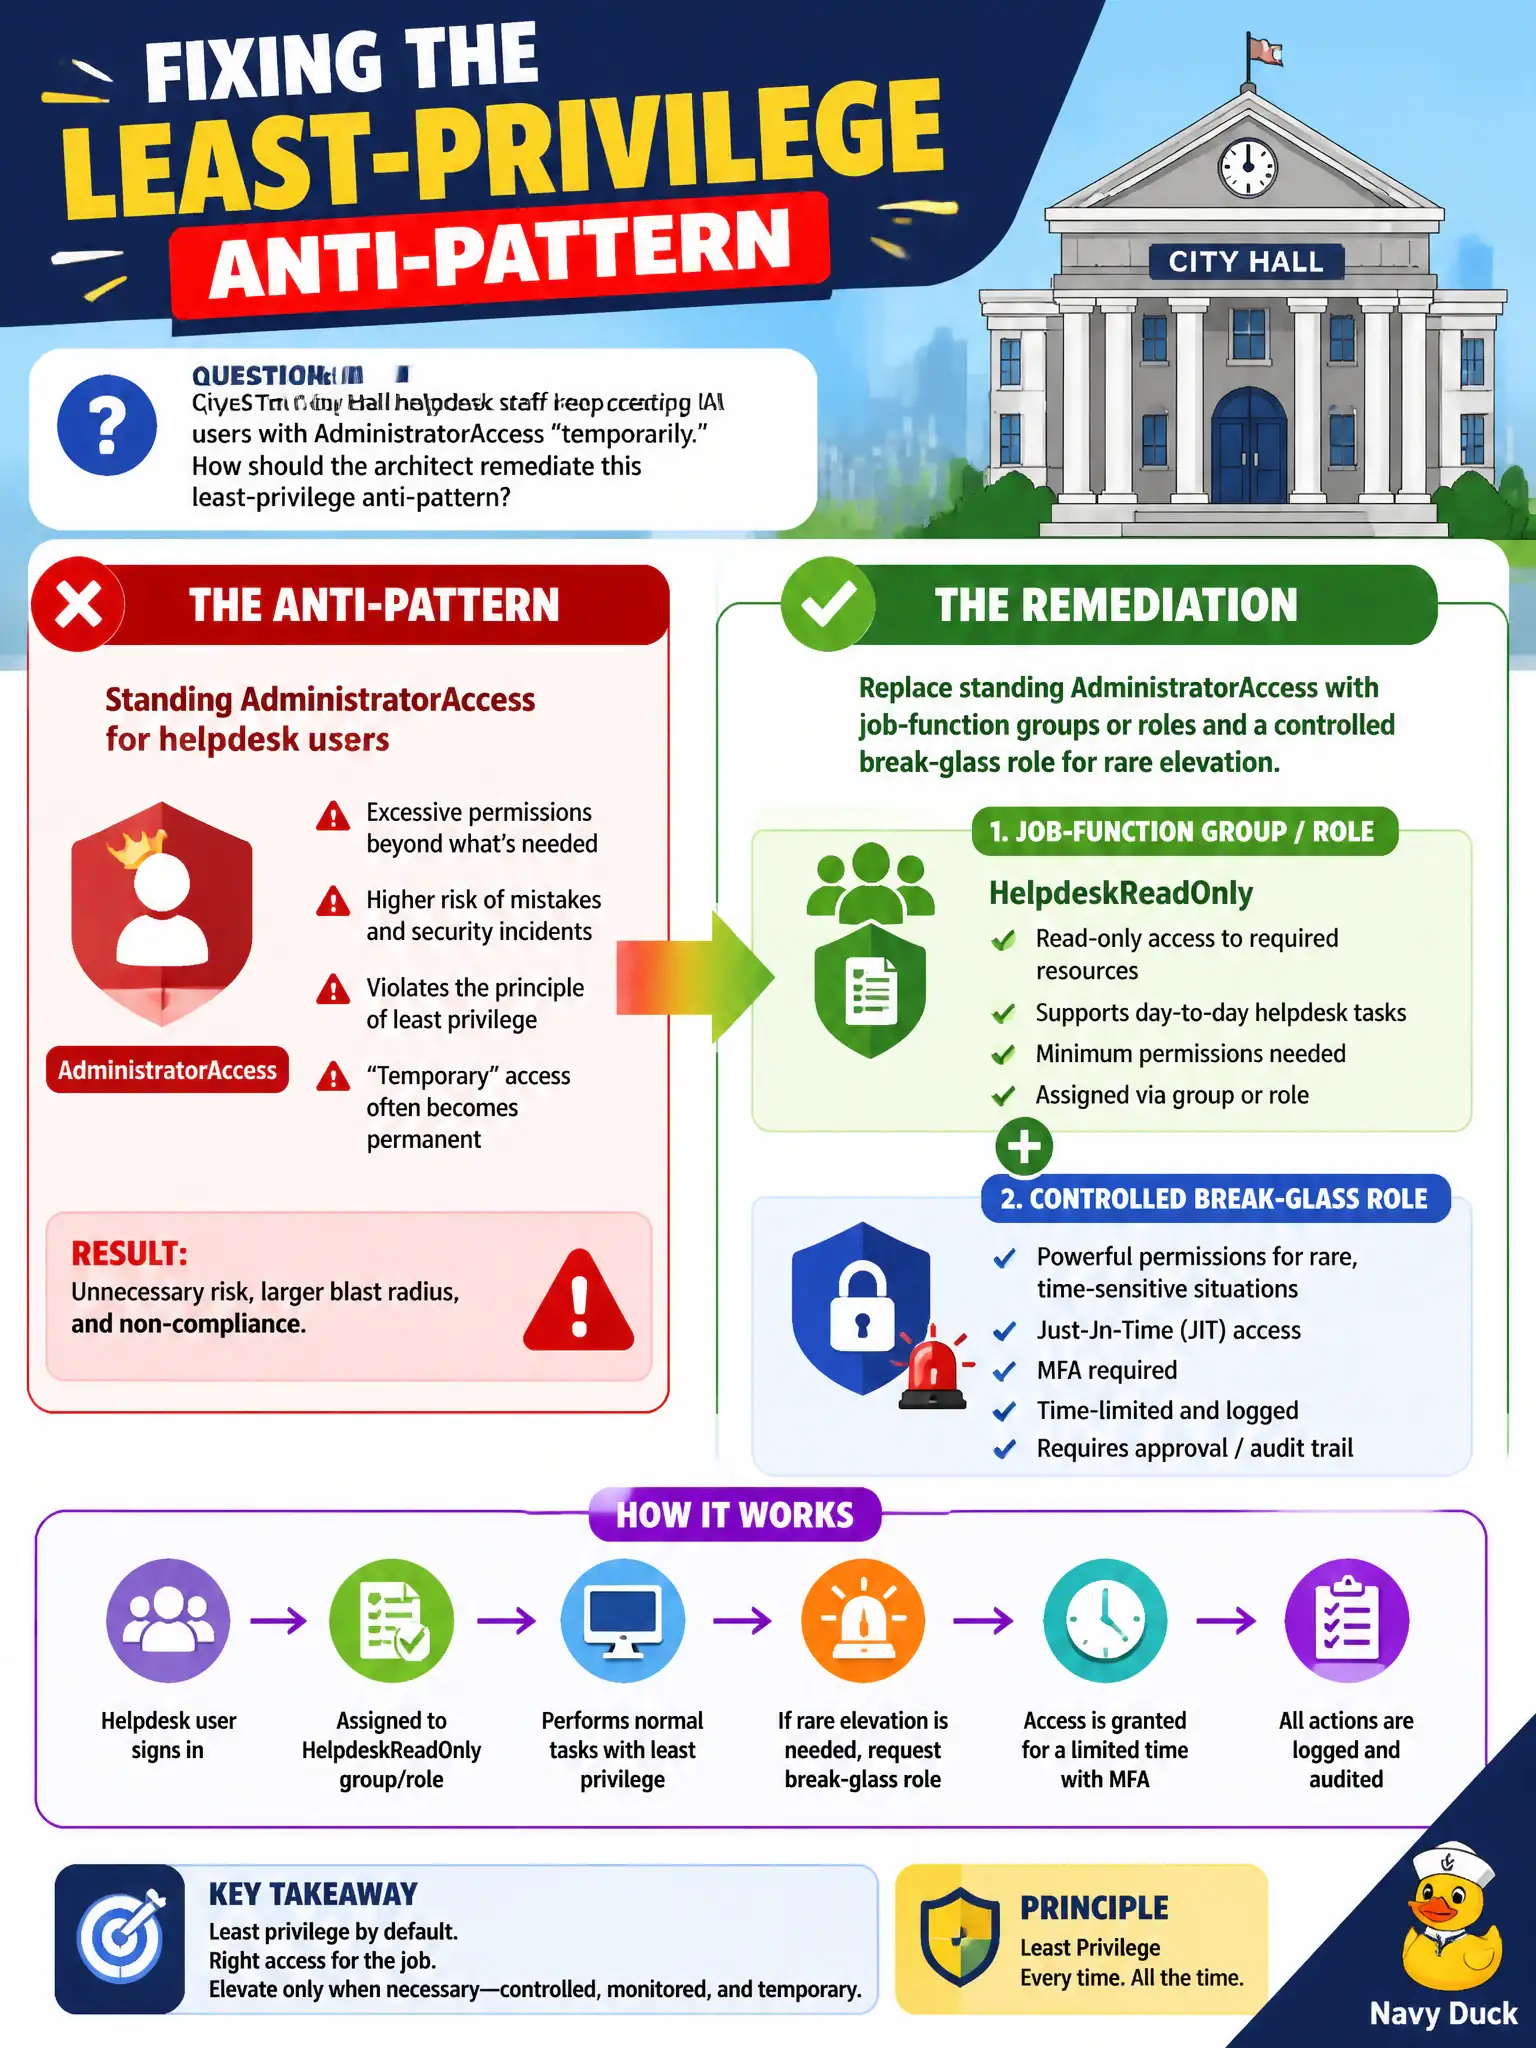
City Hall helpdesk staff keep creating IAM users with AdministratorAccess “temporarily.” How should the architect remediate this least-privilege anti-pattern?
Select an answer to reveal the explanation.
Short Explanation
“Temporary admin” has a way of becoming permanent wallpaper. Give helpdesk a read-mostly role for tickets, and a separate break-glass role with MFA and logging when elevation is truly needed. Standing AdministratorAccess for everyone is how small tickets become big incidents.
Full Explanation
Helpdesk staff who keep creating IAM users with AdministratorAccess "temporarily" need a redesigned least-privilege model: job-function groups or roles such as HelpdeskReadOnly for routine tickets, plus a tightly controlled break-glass role for rare elevation with MFA, short sessions, and mandatory CloudTrail review. Standing AdministratorAccess converts every helpdesk credential into a citywide master key and trains staff to solve every ticket with full admin rights.
Making AdministratorAccess the default for every new IAM user institutionalizes the anti-pattern. Sharing one AdministratorAccess access key among the entire helpdesk removes individual accountability. Removing all IAM policies so work is unauthenticated simply breaks access rather than fixing privilege design.
Exam caveat: permissions boundaries and SCPs can prevent helpdesk delegated admins from attaching AdministratorAccess even if they can create users. Prefer Identity Center permission sets over long-lived IAM users. Operational check: process a sample ticket with HelpdeskReadOnly successfully; attempt an elevated action and confirm denial; use break-glass with MFA only in a drill; search IAM for users with AdministratorAccess and remediate; alert on AttachUserPolicy for that managed policy.