
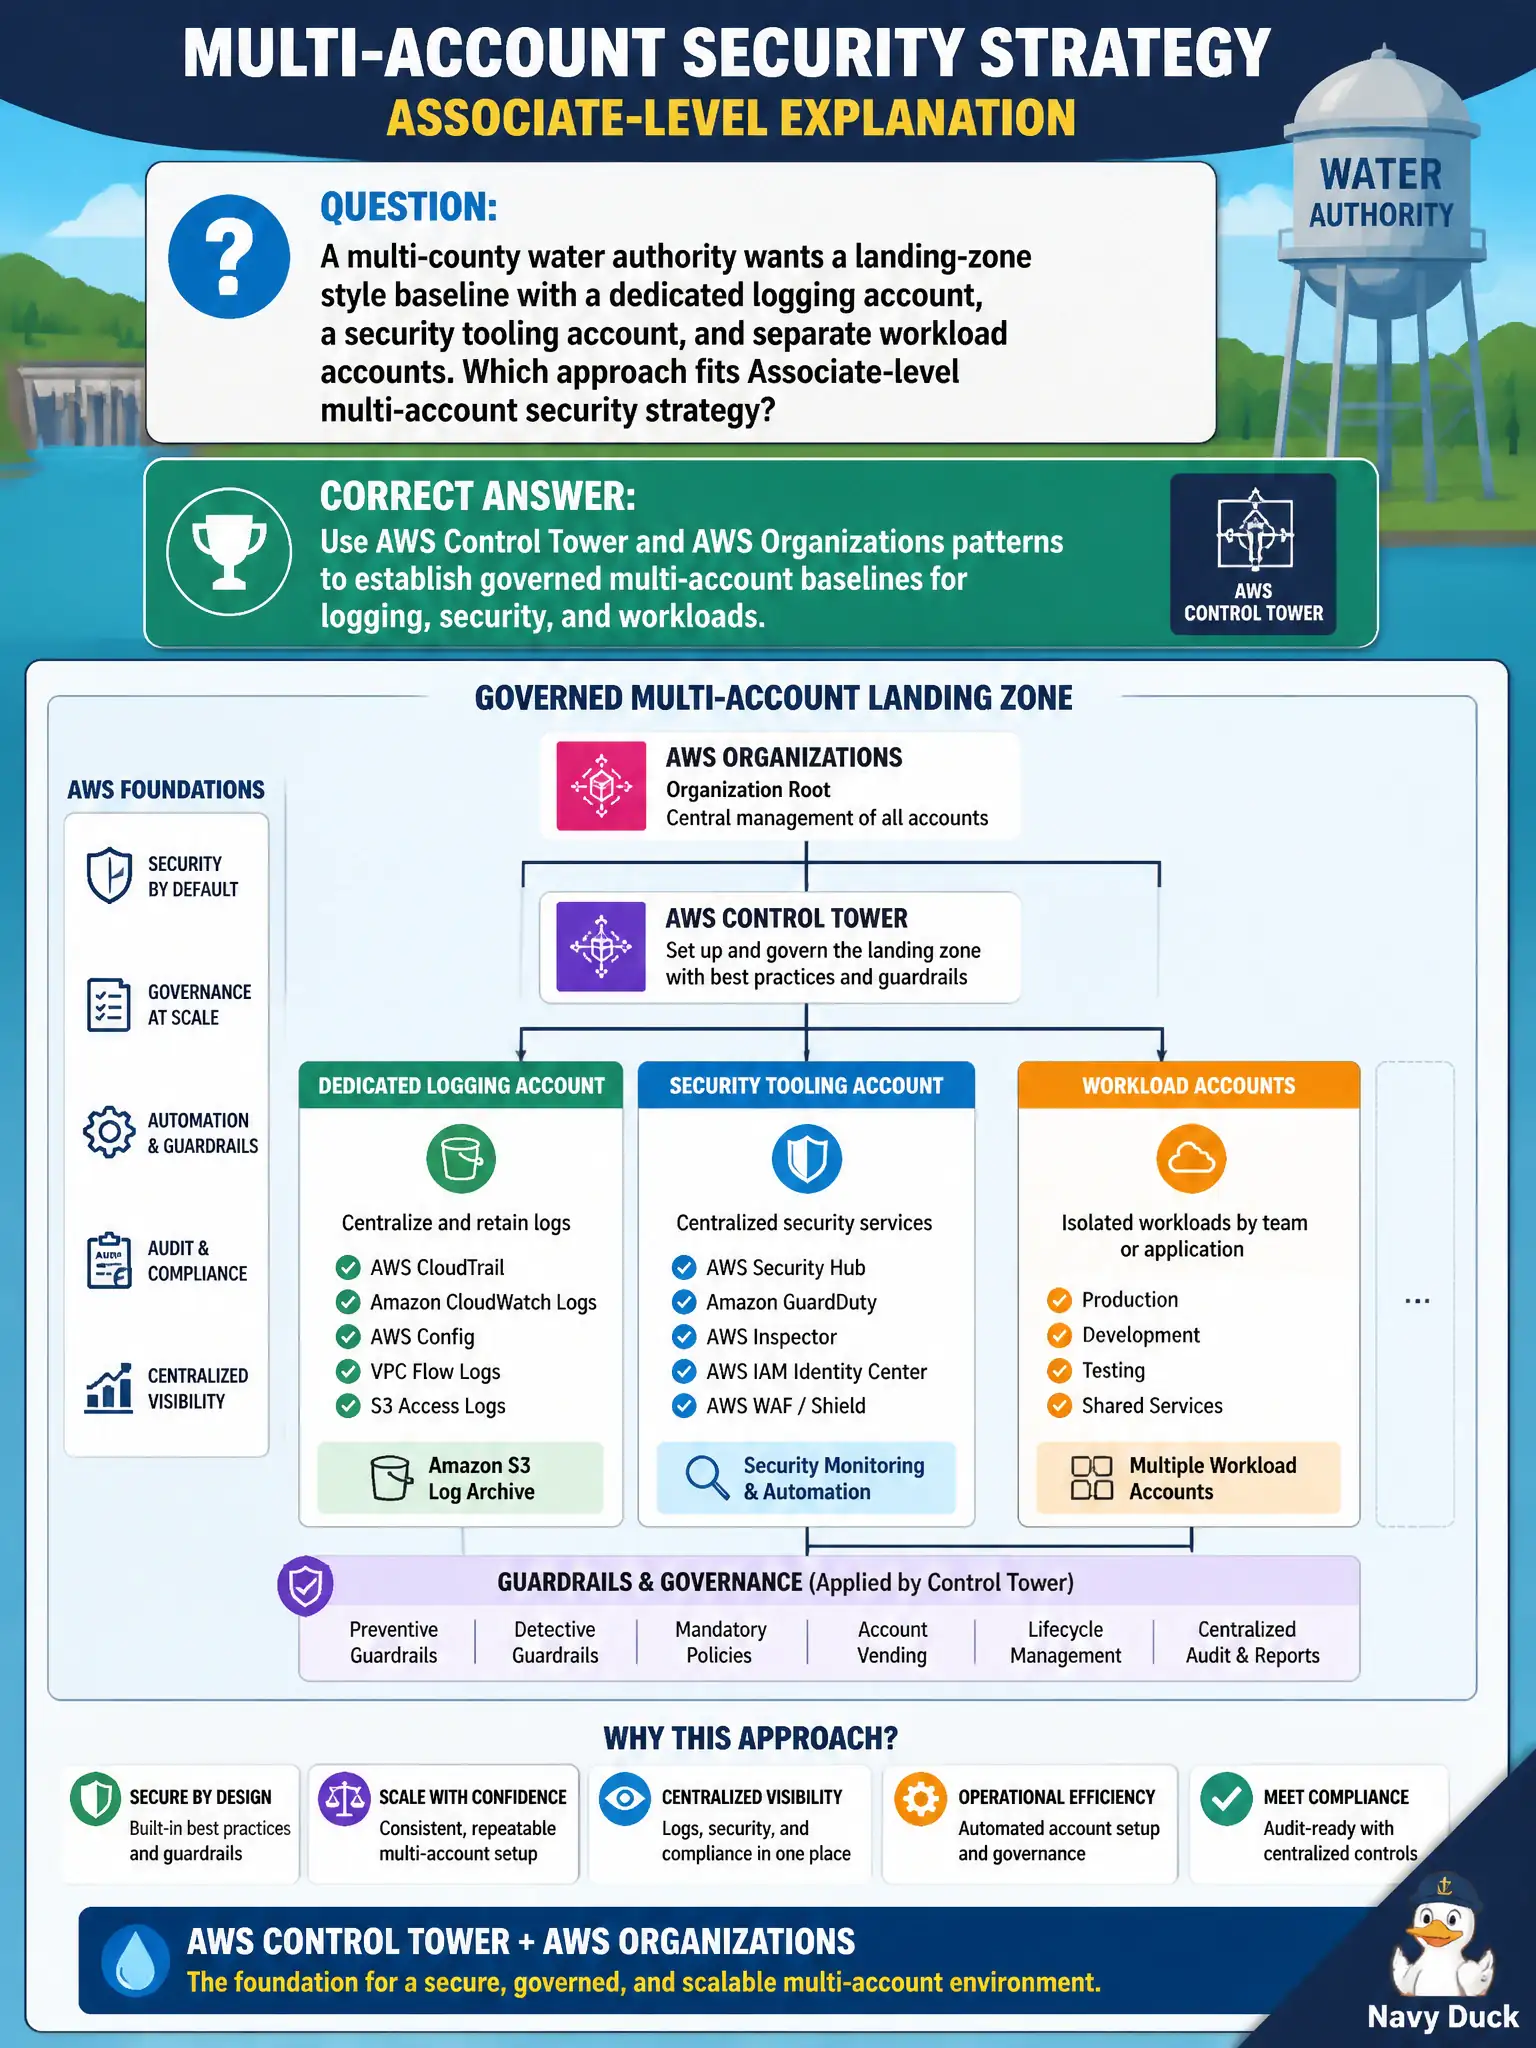
A multi-county water authority wants a landing-zone style baseline with a dedicated logging account, a security tooling account, and separate workload accounts. Which approach fits Associate-level multi-account security strategy?
Select an answer to reveal the explanation.
Short Explanation
Picture a water district campus: one building for cameras (logging), one for security tools, and separate buildings for treatment plants (workloads). Control Tower plus Organizations lays that campus out with guardrails. Stuffing everything into one account or inventing an SAP-sized rewrite misses the Associate target.
Full Explanation
A multi-county water authority that wants a landing-zone style baseline with a dedicated logging account, a security tooling account, and separate workload accounts should follow AWS Organizations multi-account patterns, commonly accelerated with AWS Control Tower. Control Tower establishes a governed multi-account environment: organization structure, mandatory guardrails, a Log Archive account for centralized CloudTrail/Config evidence, an Audit/security tooling account, and provisioned workload accounts for treatment-plant or SCADA-adjacent applications. That campus layout—cameras in one building, security tools in another, plants in their own buildings—matches Associate-level security strategy without inventing a multi-year enterprise program as the only answer.
Placing all logging, security tools, and production apps in one account simplifies billing only at the cost of blast radius: a compromised app role can threaten logs and security tooling. Skipping Organizations and creating unmanaged accounts yields no SCPs, no centralized trail, and no consistent baseline. Insisting on a professional-scale continuous multi-year org transformation as the only acceptable answer overshoots the Associate exam, which targets practical Control Tower/Organizations patterns rather than consulting-program theatrics.
Exam caveat: Control Tower is optional if you manually build Organizations, OUs, SCPs, and a logging account—but the exam often treats Control Tower as the packaged landing-zone answer. Guardrails still need identity design and monitoring. Operational check: confirm separate accounts exist for log archive, security, and at least one workload; verify organization trail delivers to the logging account bucket; attempt a denied action blocked by a preventive guardrail from a workload admin and record AccessDenied.