
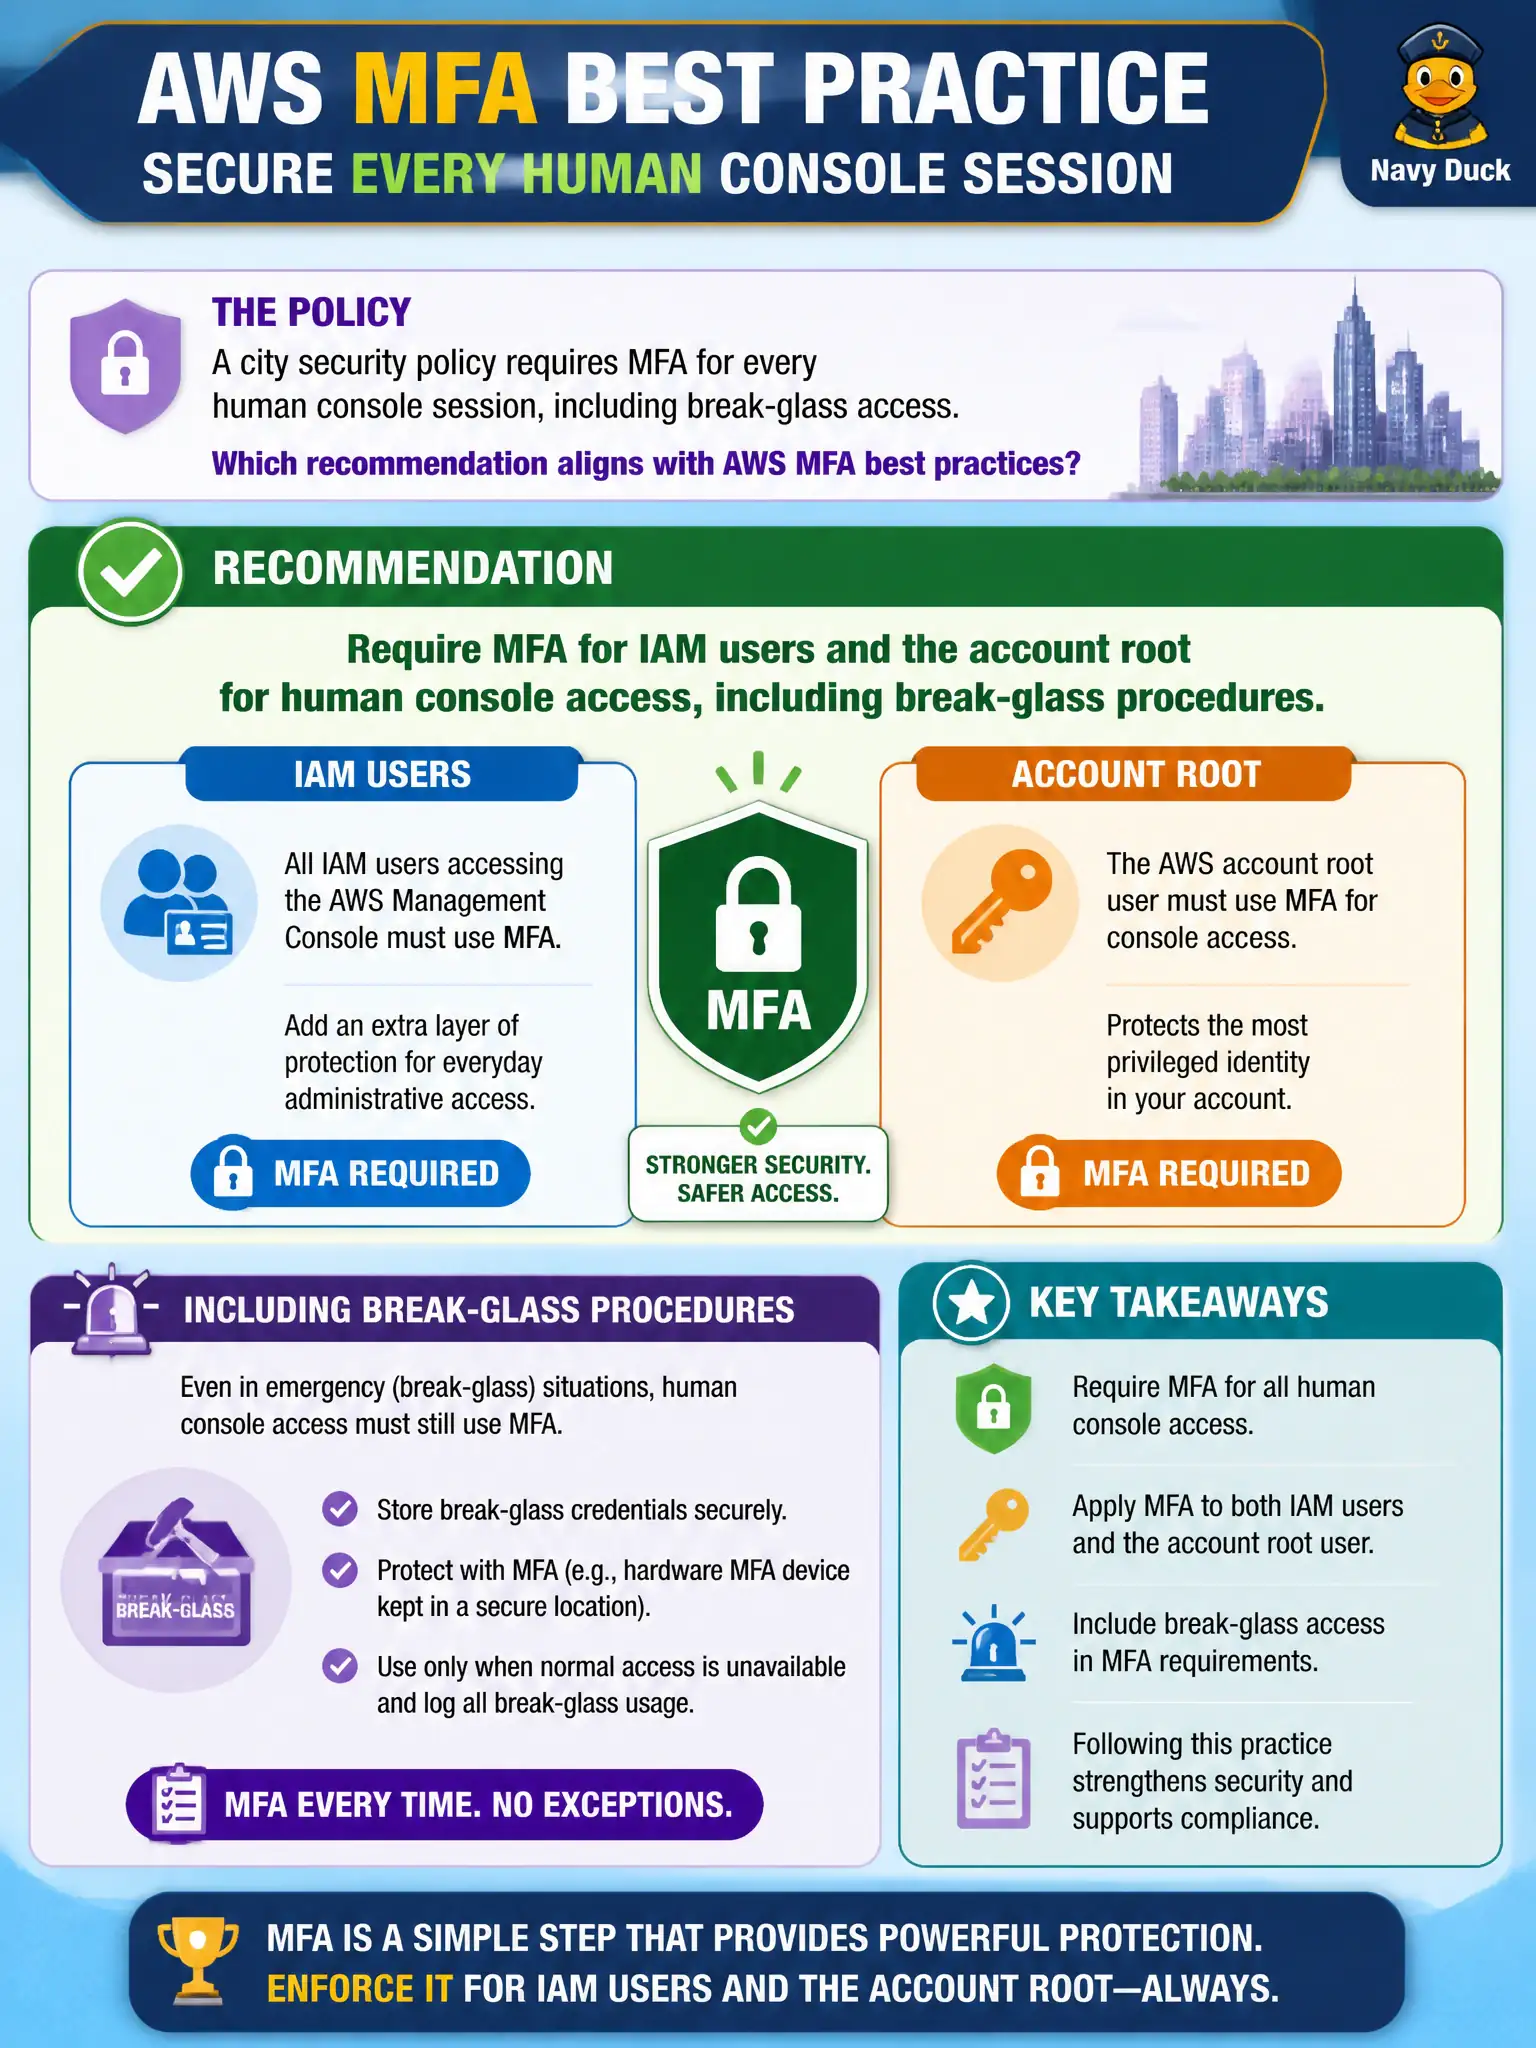
A city security policy requires MFA for every human console session, including break-glass access. Which recommendation aligns with AWS MFA best practices?
Select an answer to reveal the explanation.
Short Explanation
MFA is the second lock on every console door—including the emergency one. Root and IAM humans who open the Management Console should need that second factor; access keys alone are not MFA for console sessions. Skipping MFA on root “just in case” is the opposite of break-glass hygiene.
Full Explanation
Municipal security policy that requires MFA for every human console session—including break-glass—aligns with AWS guidance to protect interactive sign-in with a second factor. IAM users who use the Management Console should have MFA enabled, and the account root user must have MFA as a non-negotiable control. Break-glass procedures still use MFA; emergency access means controlled elevation with strong authentication and heavy logging, not a bypass that leaves root or admin consoles single-factor. Access keys authenticate programmatic API calls and are not a substitute for MFA on console password sign-in.
Treating long-lived IAM access keys as a complete substitute for MFA on console users confuses credential types: keys do not provide console MFA, and standing keys increase risk if laptops are stolen. Enabling MFA only on non-admin users while leaving root without MFA inverts priority—root and admins are the highest-value targets. Disabling console access for everyone and relying solely on unsigned API calls from shared laptops abandons authentication rather than strengthening it and is operationally unusable for city staff who need the console.
Exam caveat: MFA can be enforced with IAM policy conditions (aws:MultiFactorAuthPresent) on sensitive actions, and Identity Center can require MFA via the IdP. Virtual MFA is common; hardware MFA is preferred for root in high-assurance environments. Operational check: attempt console sign-in for root and a privileged IAM/Identity Center user without the second factor and confirm failure; complete MFA and verify access; ensure break-glass runbooks document MFA device custody and CloudTrail review after each use.