
A county records office runs analytics jobs in private VPC subnets that read large case-file objects from Amazon S3 and meter metadata from Amazon DynamoDB. Staff want higher, more predictable throughput and to keep that traffic on the AWS network instead of hairpinning through the internet or a NAT gateway. Which design best meets those goals?
Select an answer to reveal the explanation.
Short Explanation
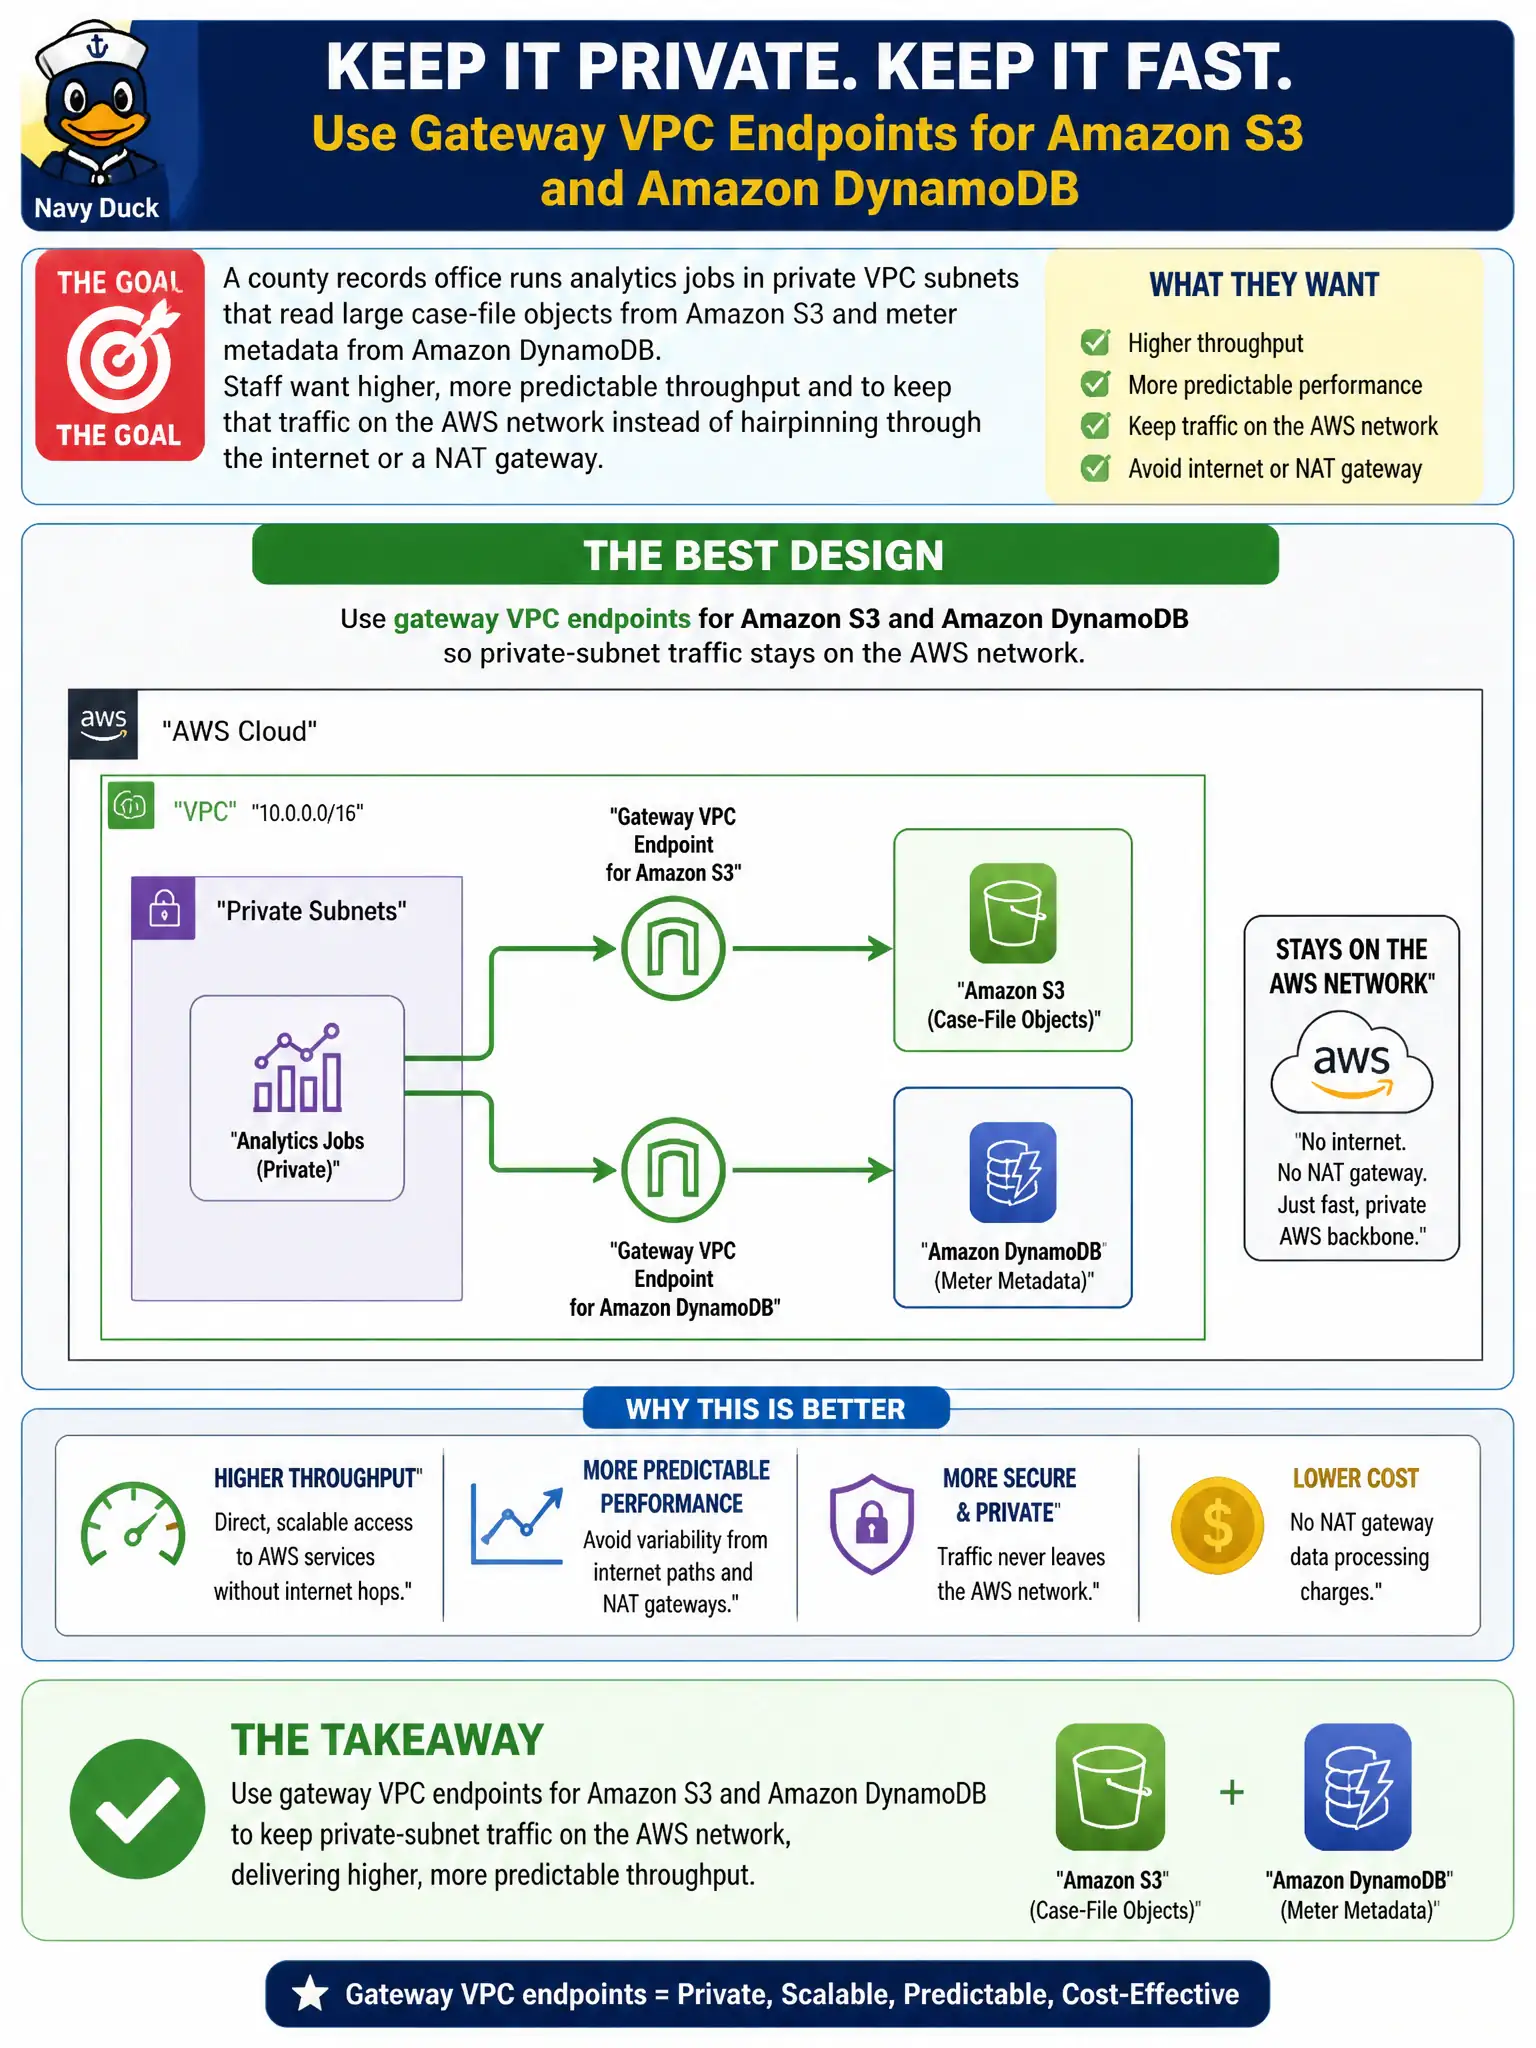
Think of a private on-ramp that never leaves AWS’s road system. Gateway VPC endpoints for S3 and DynamoDB let private-subnet jobs talk to those services without NAT or the public internet. You keep the data path on the AWS network—better for throughput predictability and a cleaner security story for municipal case files.
Full Explanation
Gateway VPC endpoints are the right fit for this county records analytics path because they create private, AWS-backed connectivity from VPC subnets to Amazon S3 and Amazon DynamoDB without forcing traffic through an internet gateway, NAT gateway, or VPN. For large case-file object reads and high-rate DynamoDB metadata lookups, that private path improves throughput predictability and keeps sensitive municipal traffic on the AWS network rather than hairpinning to public service endpoints. Attach an internet gateway to every private subnet and assign public IPs to analytics instances. That design reclassifies the subnets as public and exposes workloads unnecessarily; it also fails the goal of avoiding internet hairpins. Peer the VPC to a transit VPC that only forwards S3 traffic over the public internet. VPC peering does not magically keep S3 private if the forwarding path still uses public internet routes, so the predictability and private-path requirements remain unmet. Place a Network Load Balancer in front of S3 and DynamoDB regional public endpoints. You cannot usefully front those managed regional endpoints with an NLB as if they were your own targets; that pattern misunderstands how those services are reached. Exam caveat: gateway endpoints support S3 and DynamoDB specifically; other AWS APIs generally need interface VPC endpoints (PrivateLink) instead. Operational check: confirm route-table entries for the gateway endpoints, verify IAM and endpoint policies allow the analytics roles, and measure that S3/DynamoDB traffic no longer traverses the NAT gateway in VPC Flow Logs or NAT metrics.