
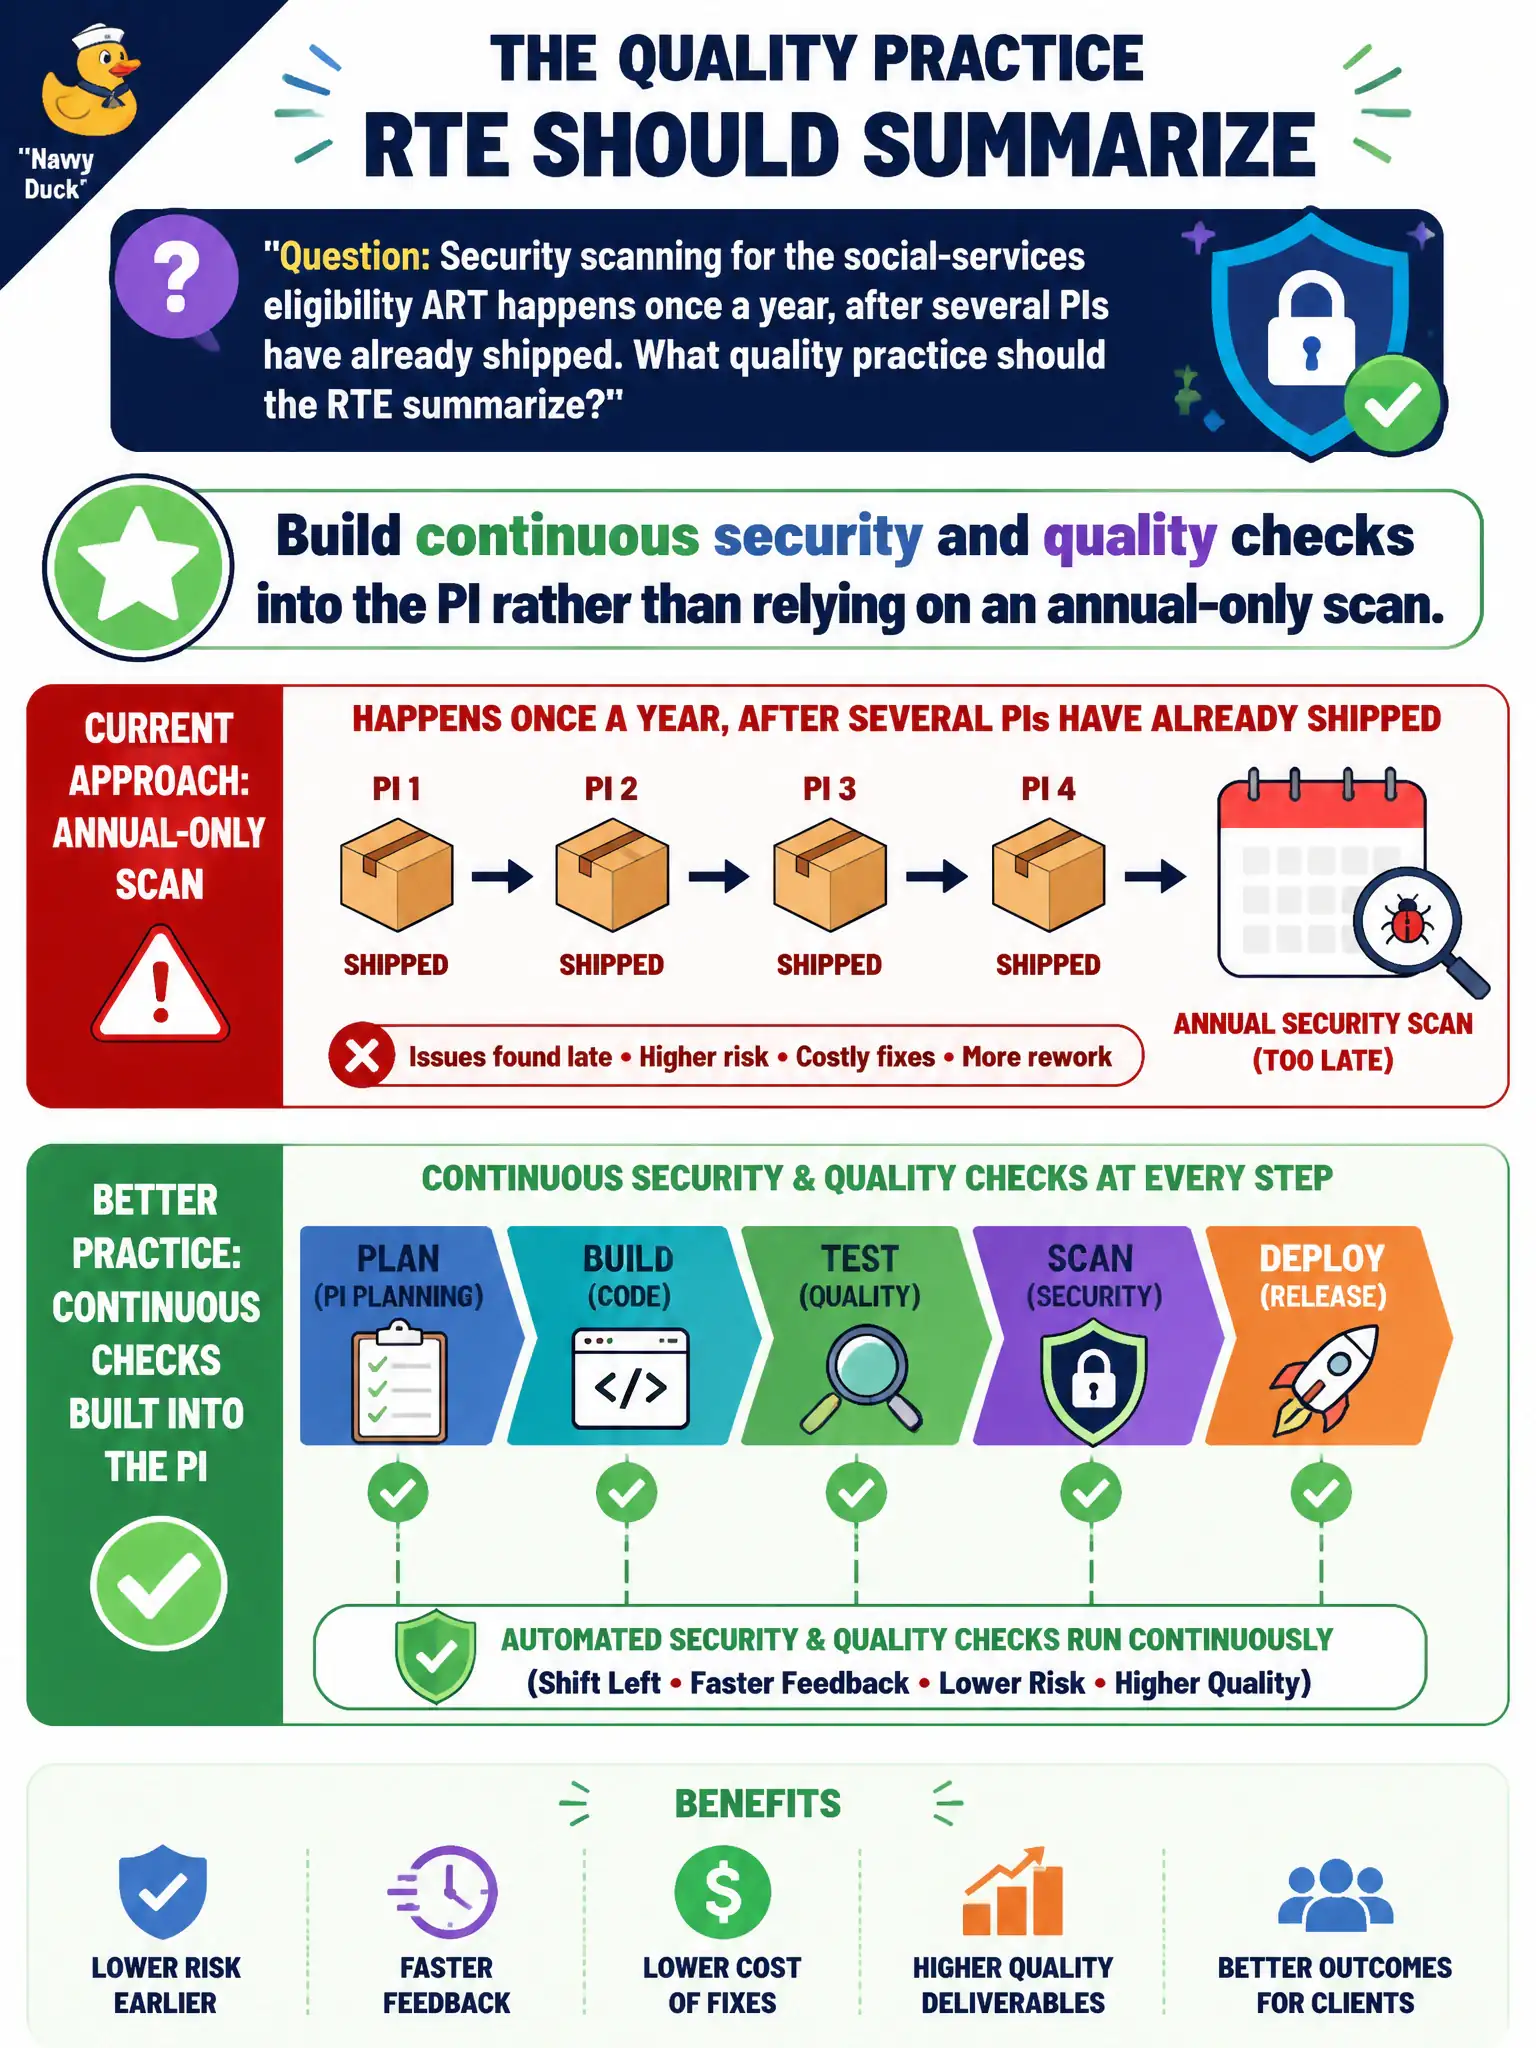
Security scanning for the social-services eligibility ART happens once a year, after several PIs have already shipped. What quality practice should the RTE summarize?
Select an answer to reveal the explanation.
Short Explanation
Checking the eligibility vault once a year is like testing smoke alarms every December and calling it fire safety. Continuous security checks catch the issues while the ART can still fix them. An annual scan is a calendar event, not a quality system.
Full Explanation
Continuous security and quality checks belong in the PI rather than an annual-only scan after several increments have shipped. For a social-services eligibility ART scanning once a year, the RTE should summarize building security into the delivery cadence. Claiming annual scans are enough because eligibility rules change only at budget time ignores continuous code and integration change. Outsourcing every scan to a post-production audit so teams never pause for security discovers issues in production. Moving scanning to a separate security department that never attends ART events recreates handoff delays and blind spots. 911 CAD/RMS integration needs Product Management in Continuous Exploration so dispatcher needs shape the backlog before engineers guess. Exam caveat: deep annual assessments may still complement continuous checks; they do not replace them. Operational check: add security scanning to the eligibility CI path and review critical findings in ART sync before the next System Demo. Schedule discovery sessions with dispatch supervisors and capture hypotheses on the Program Backlog. Hold the civic standard in facilitation notes so the next RTE inherits the same expectation for resident-facing outcomes.