
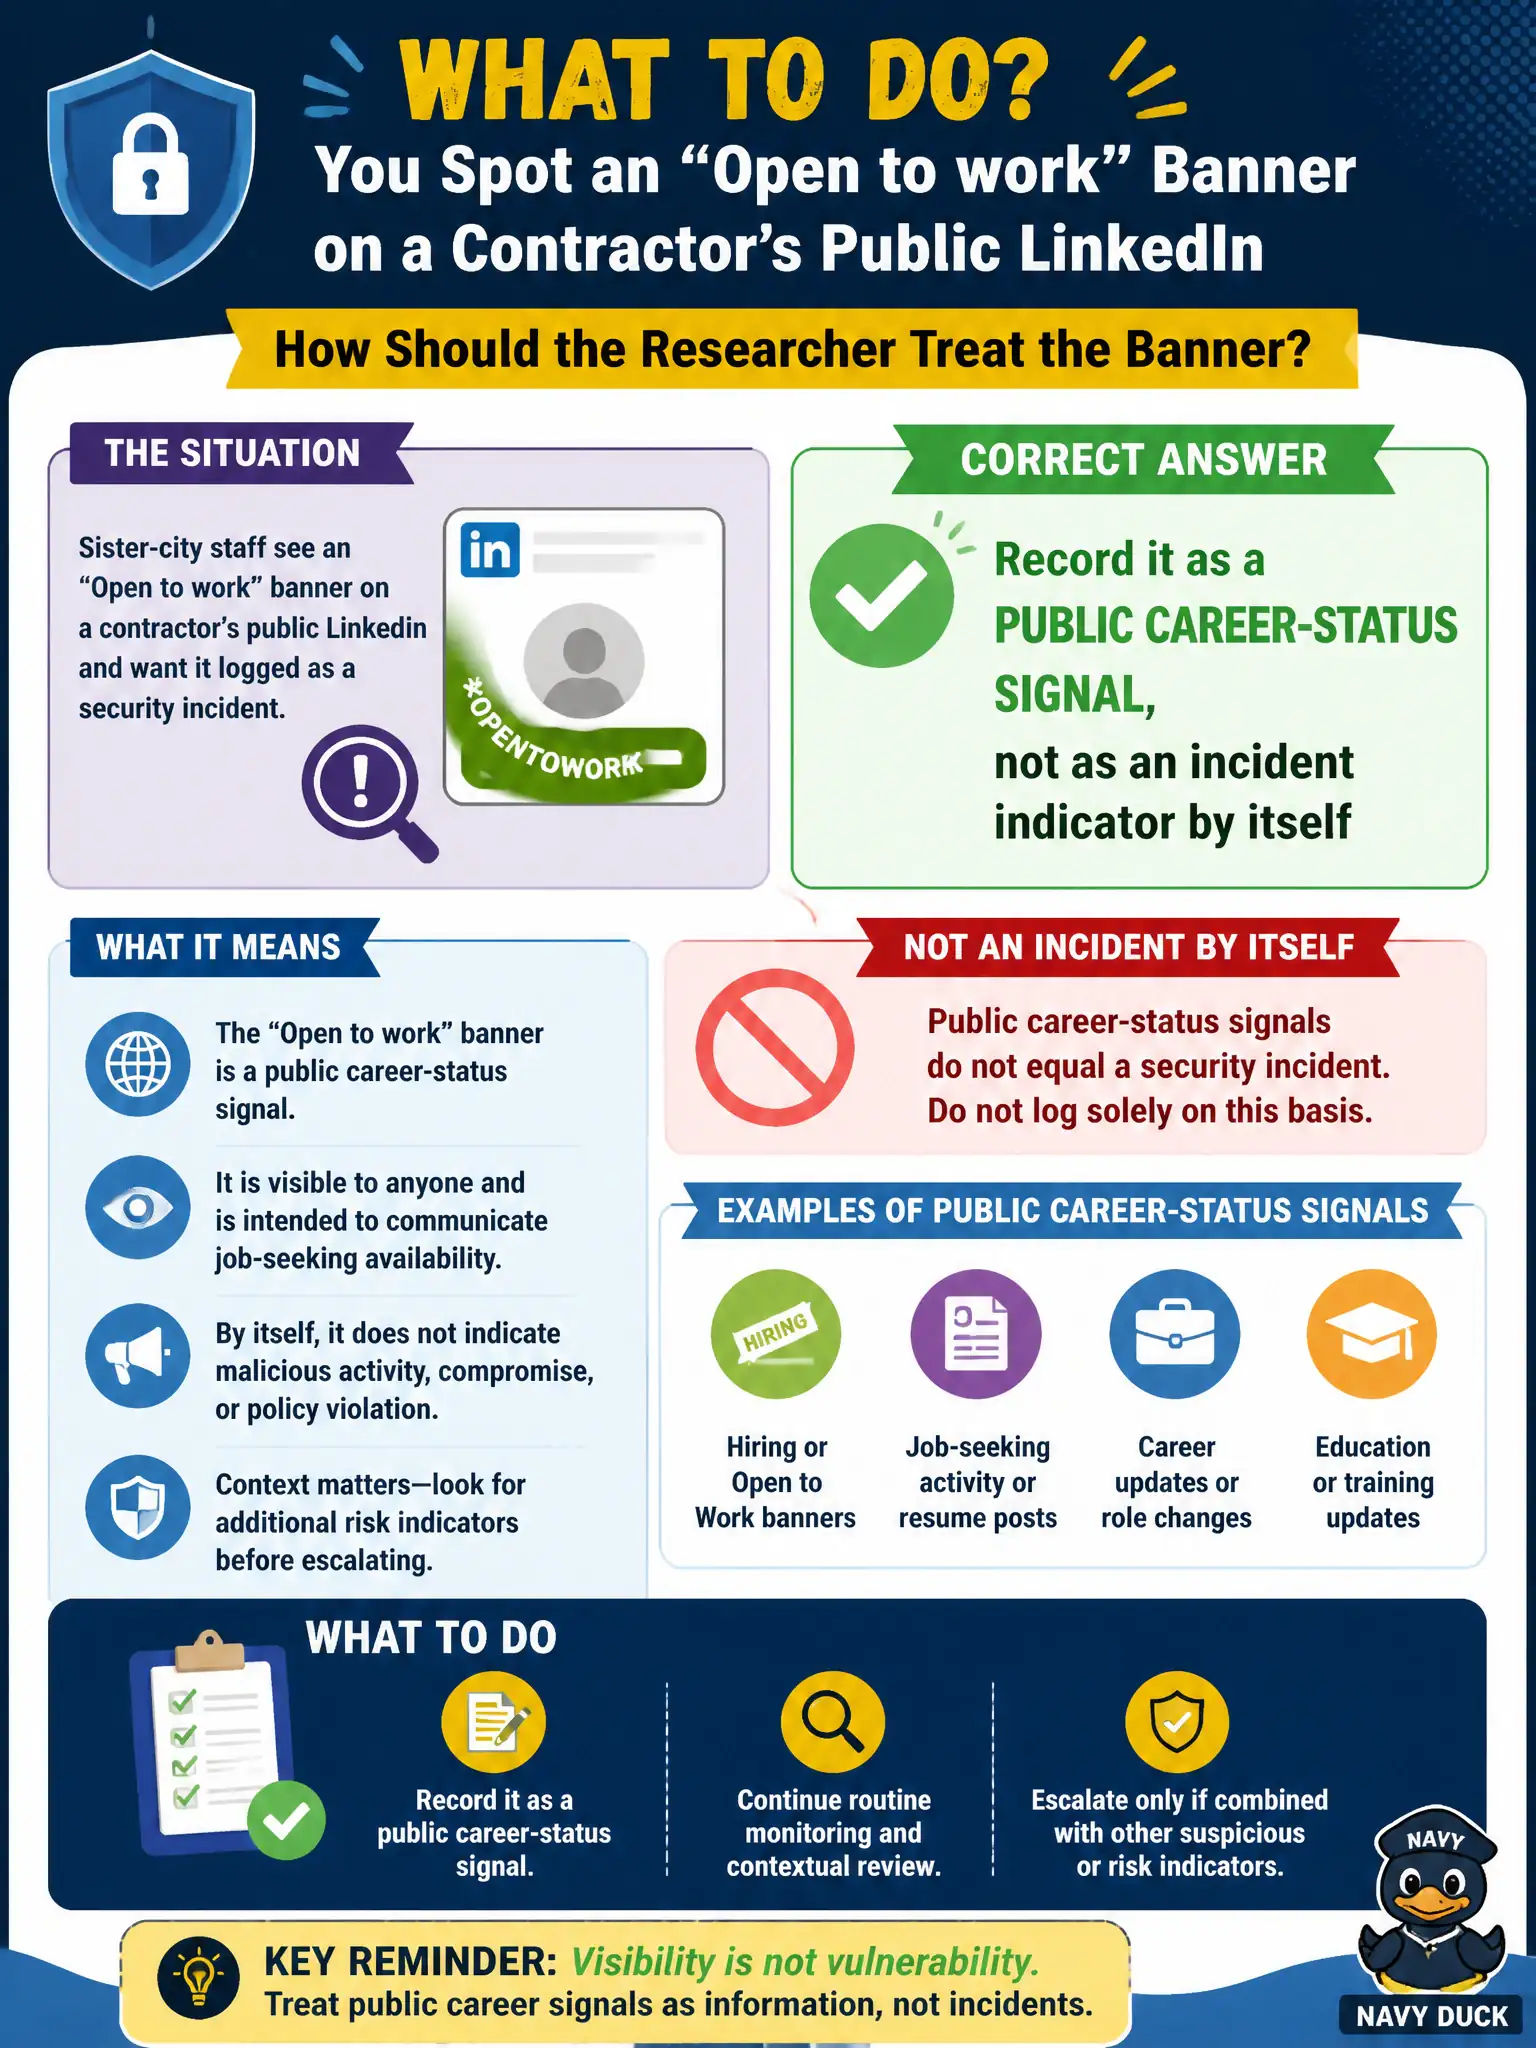
Sister-city staff see an "Open to work" banner on a contractor's public LinkedIn and want it logged as a security incident. How should the researcher treat the banner?
Select an answer to reveal the explanation.
Short Explanation
"Open to work" is a help-wanted sign on a public profile, not a siren. Note it as a career-status signal if it matters to due diligence. It is not a hack of city systems by itself.
Full Explanation
Sister-city staff who see an “Open to work” banner on a contractor’s public LinkedIn should treat it as a public career-status signal, not as an incident indicator by itself. Career UI is collectible when relevant to continuity or key-person risk on a civic contract, but it is not evidence of a cyber breach of city systems and should not open an incident ticket on that basis alone. Opening a cyber incident because the banner “proves a breach” fails by misclassifying a LinkedIn status flag as a security event and by wasting incident-response capacity. Ignoring career-status UI because LinkedIn banners are never collectible fails; public banners are visible artifacts that may matter to contract managers. Demanding the contractor disable the banner as a contract condition before any notes are taken fails by leaping to contractual remediation before the researcher has recorded the observation in context for the program owner. Exam caveat: career signals may inform succession or dependency discussions, but they are not IOC-class evidence for municipal SOC workflows. Operational check: screenshot the banner with date; note any relevance to contractor continuity; keep the finding out of the cyber incident queue unless independent technical indicators appear.